
dismember
 liamg/dismember
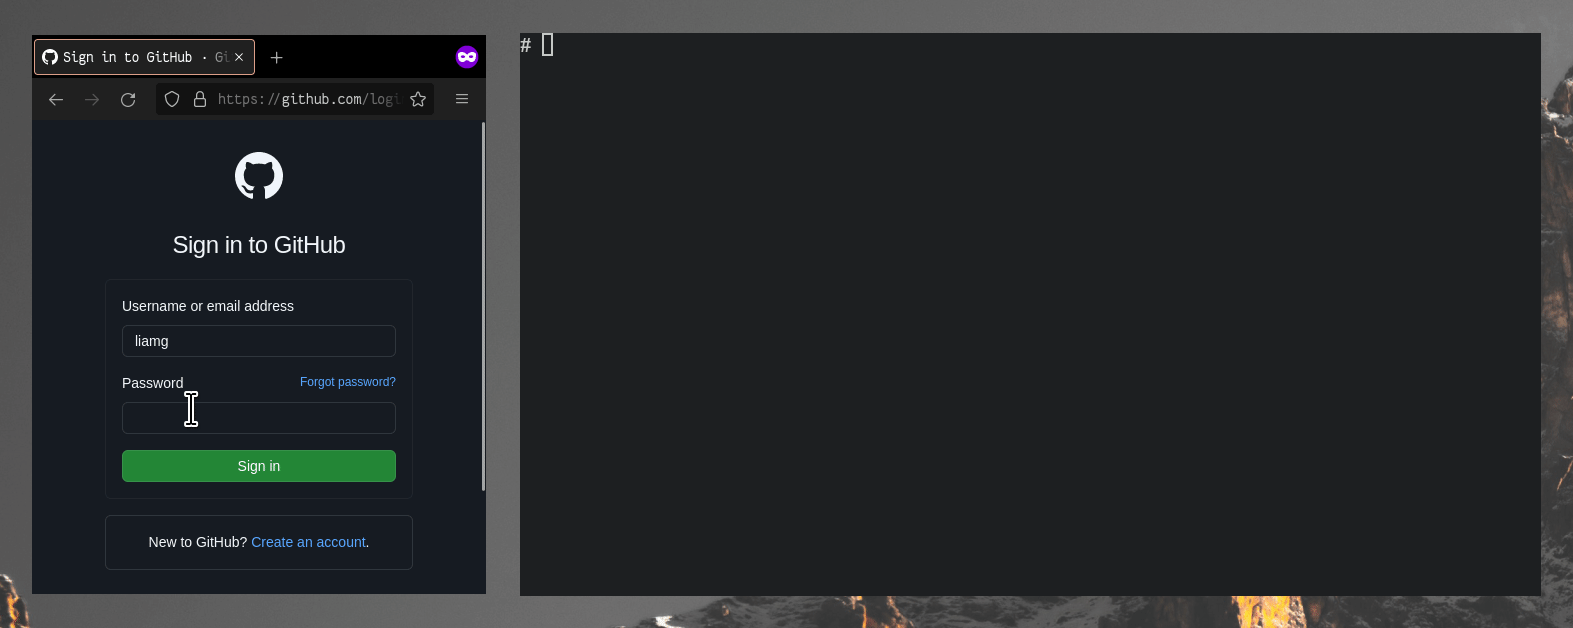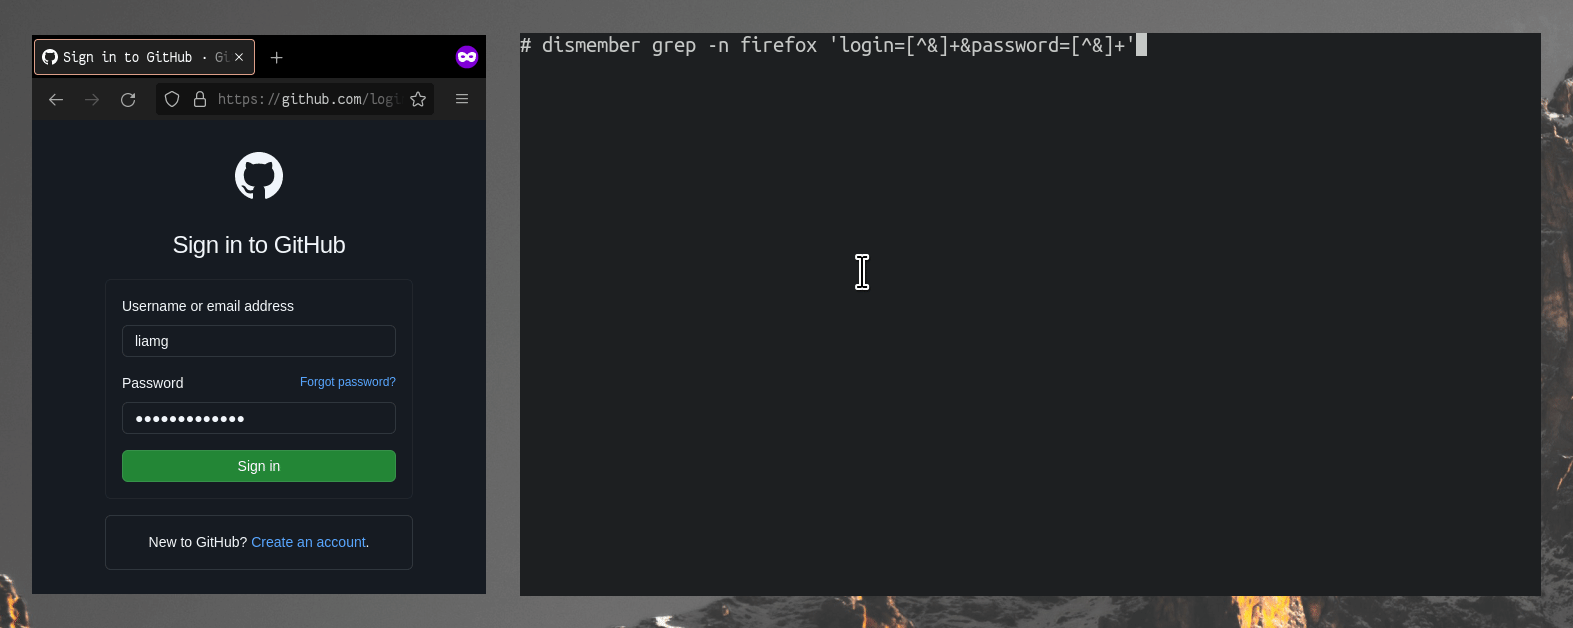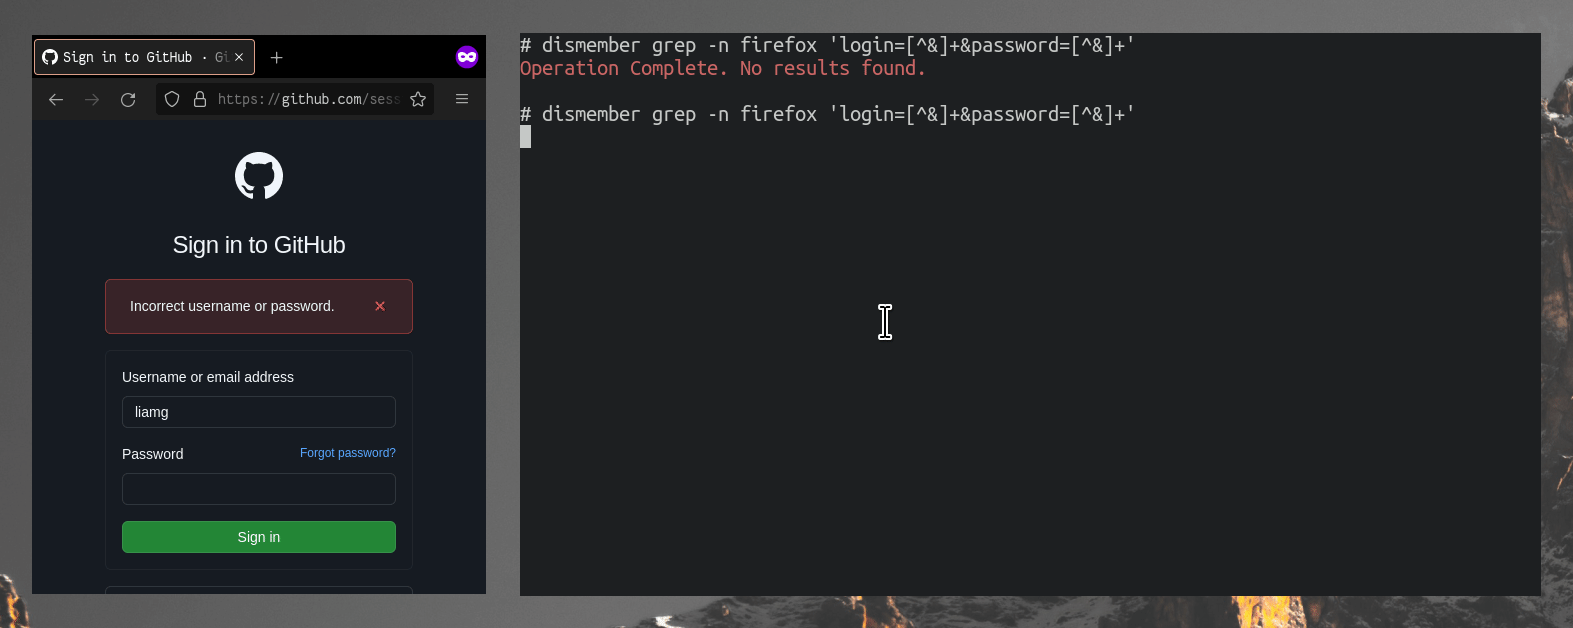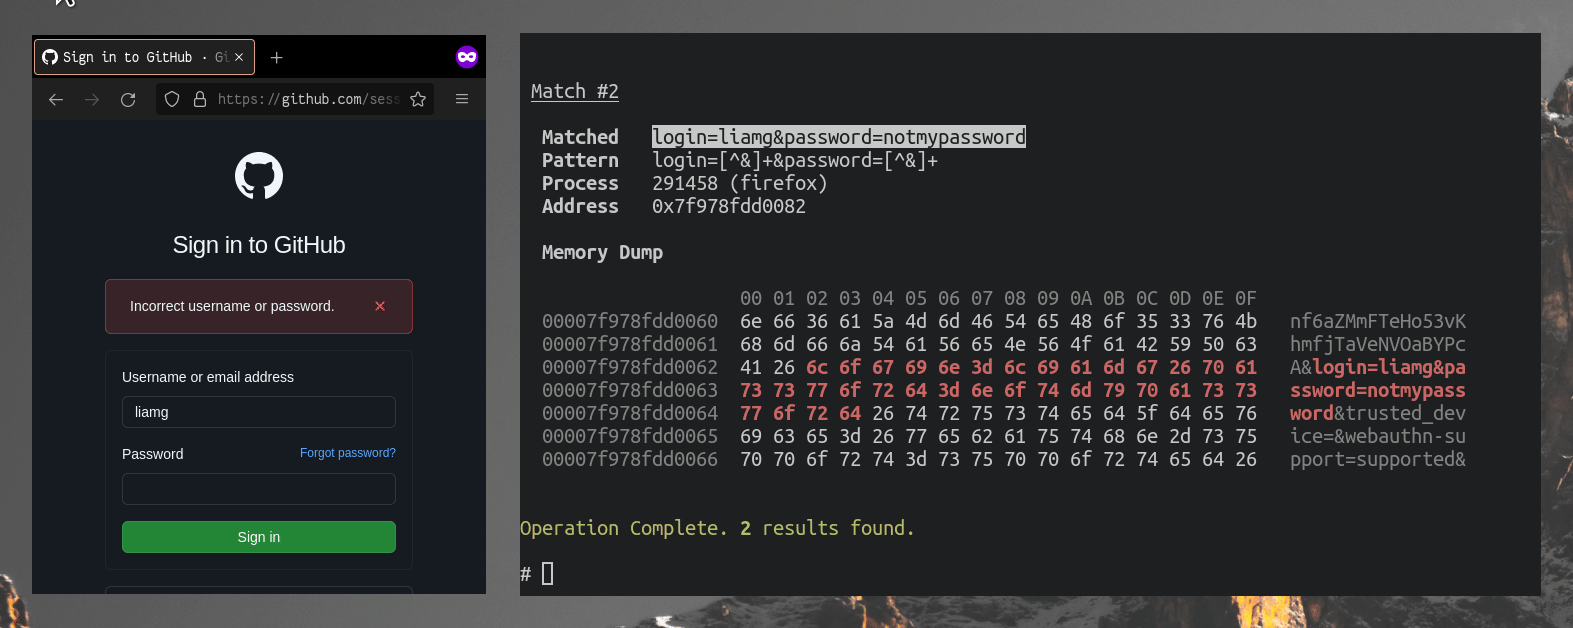
:knife: Scan memory for secrets and more. Maybe eventually a full /proc toolkit.
ctfforensicsinformation-gathering+2
675
liamg/dismember:knife: Scan memory for secrets and more. Maybe eventually a full /proc toolkit.
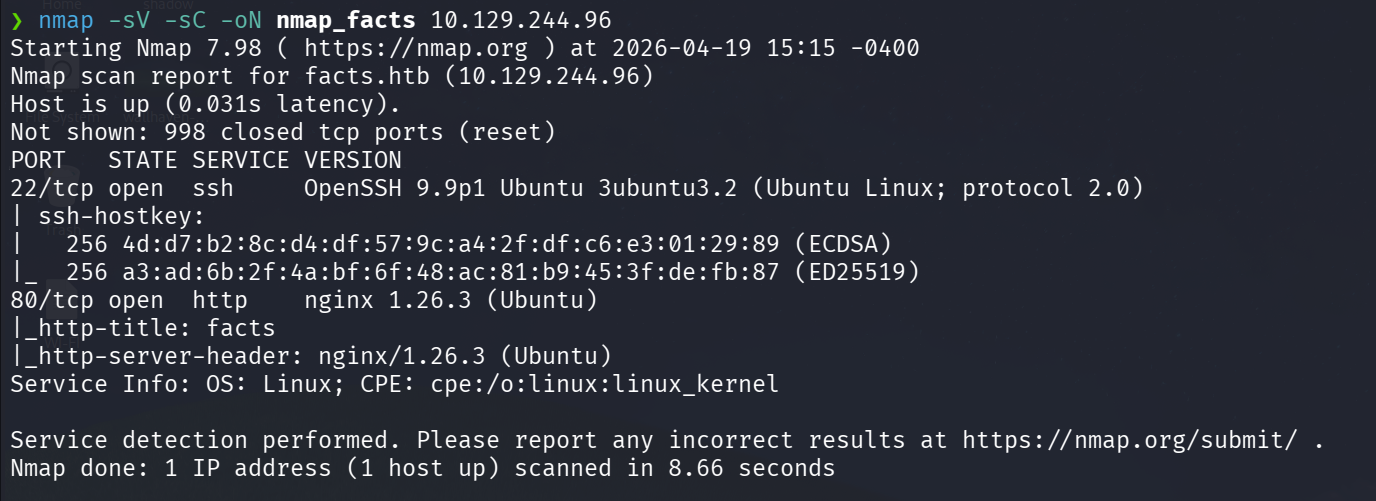 mattiapertusati/htb-facts
HackTheBox — Facts (Easy/Linux) | CVE-2025-2304 + AWS S3 + SSH Key + Facter PrivEsc
 carpedm20/awesome-hacking
A curated list of awesome Hacking tutorials, tools and resources
 frankwxu/digital-forensics-lab
Free hands-on digital forensics labs for students and faculty
 rhinosecuritylabs/cloudgoat
CloudGoat is Rhino Security Labs' "Vulnerable by Design" AWS deployment tool
 sunblaze-ucb/exploitgym
ExploitGym is a large-scale, realistic benchmark built from real-world vulnerabilities designed to evaluate AI agents' ability to develop exploits.
 ruia-ruia/cve-2022-29582-exploit
Exploit for CVE-2022-29582 targeting Google's Kernel CTF
 tianstcht/cve-2023-4427
Exploit for CVE-2023-4427 targeting Chrome 117 V8, using many cross-origin iframes to brute-force ASLR and achieve code execution. Provides…
 thecybergeek/cve-2026-4480-poc
Proof-of-concept exploit for CVE-2026-4480, an unauthenticated remote command execution in Samba's print subsystem via %J injection. Includes reverse…
 elit3pwner/cve-2015-1328-goldeneye
Automated local privilege escalation exploit for CVE-2015-1328 targeting Ubuntu overlayfs, designed for CTF environments with a simple bash…
 germarr93/cybersecurity-pentest-lab
CVE-2004-2687 (Distcc 3.2.1) exploitation, methodology & remediation — Metasploitable2 lab
 dinosn/cve-2026-42945-nginx32-lab
CVE-2026-42945 nginx 32-bit exploit lab ASLR enabled
 bluedragonsecurity/linux-kernel-dirty-pipe-exploitation-logic-bug-
Exploiting CVE-2022-0847 - written by : Antonius (w1sdom)
 ledksv/devarea
HackTheBox DevArea walkthrough chaining CVE-2022-46364 Apache CXF SSRF, CVE-2025-54123 Hoverfly RCE, and SUID bash hijacking for root escalation.
 nanashibx2/bx2-writeups
Cybersecurity writeups, walkthroughs, and technical notes by Nanashi Bx2.
 kentox493/cve-2026-42945_nginxrift
Automates CVE-2026-42945 exploitation in NGINX containers: verifies vulnerable targets, brute-forces heap offsets, executes commands, and opens an…