

caronte
 eciavatta/caronte
A tool to analyze the network flow during attack/defence Capture the Flag competitions
ctfforensicsnetwork-forensics+1
eciavatta/caronteA tool to analyze the network flow during attack/defence Capture the Flag competitions
 paradoxis/flask-unsign
Command line tool to fetch, decode, brute-force and craft session cookies of a Flask application by guessing secret keys.
 dontpanico/jwtxploiter
Automated JWT security testing tool that exploits known CVEs, tampers with payloads, performs JKU/X5U injection, key confusion attacks, and verifies…
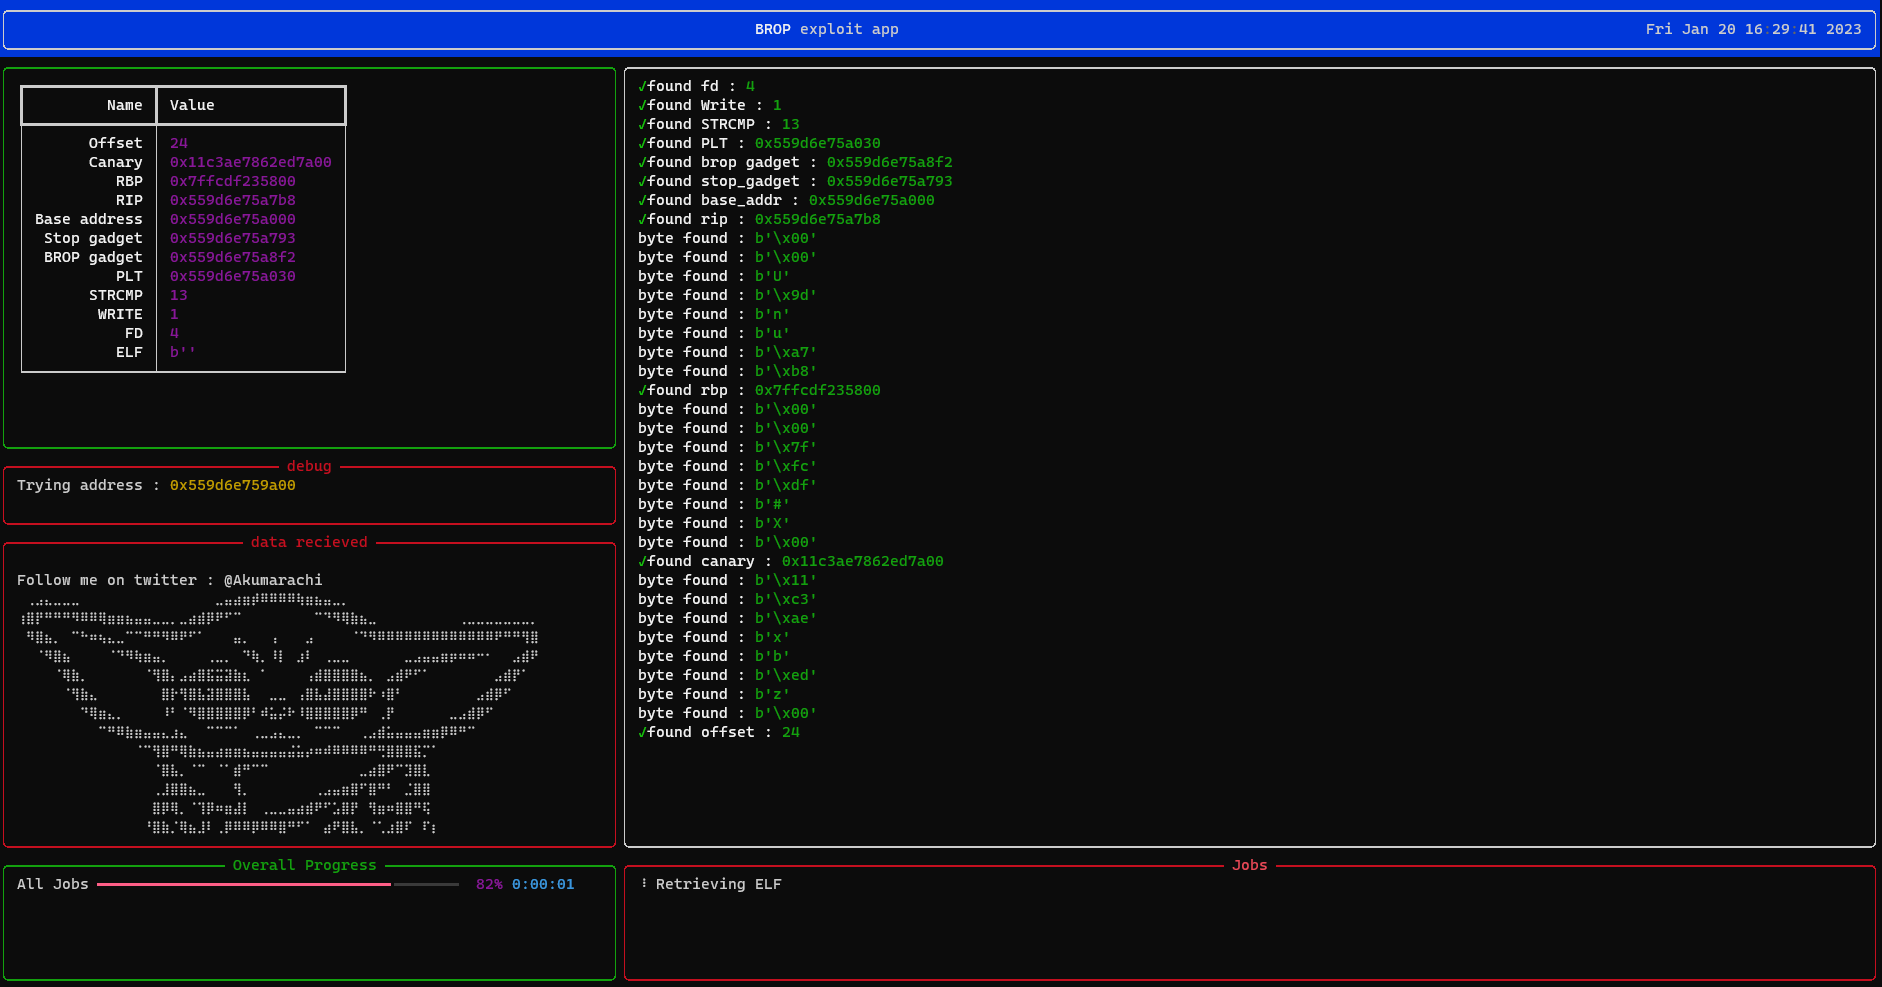 hakumarachi/bropper
An automatic Blind ROP exploitation tool
 r4ygm/stegbrute
Fast Steganography bruteforce tool written in Rust useful for CTF's
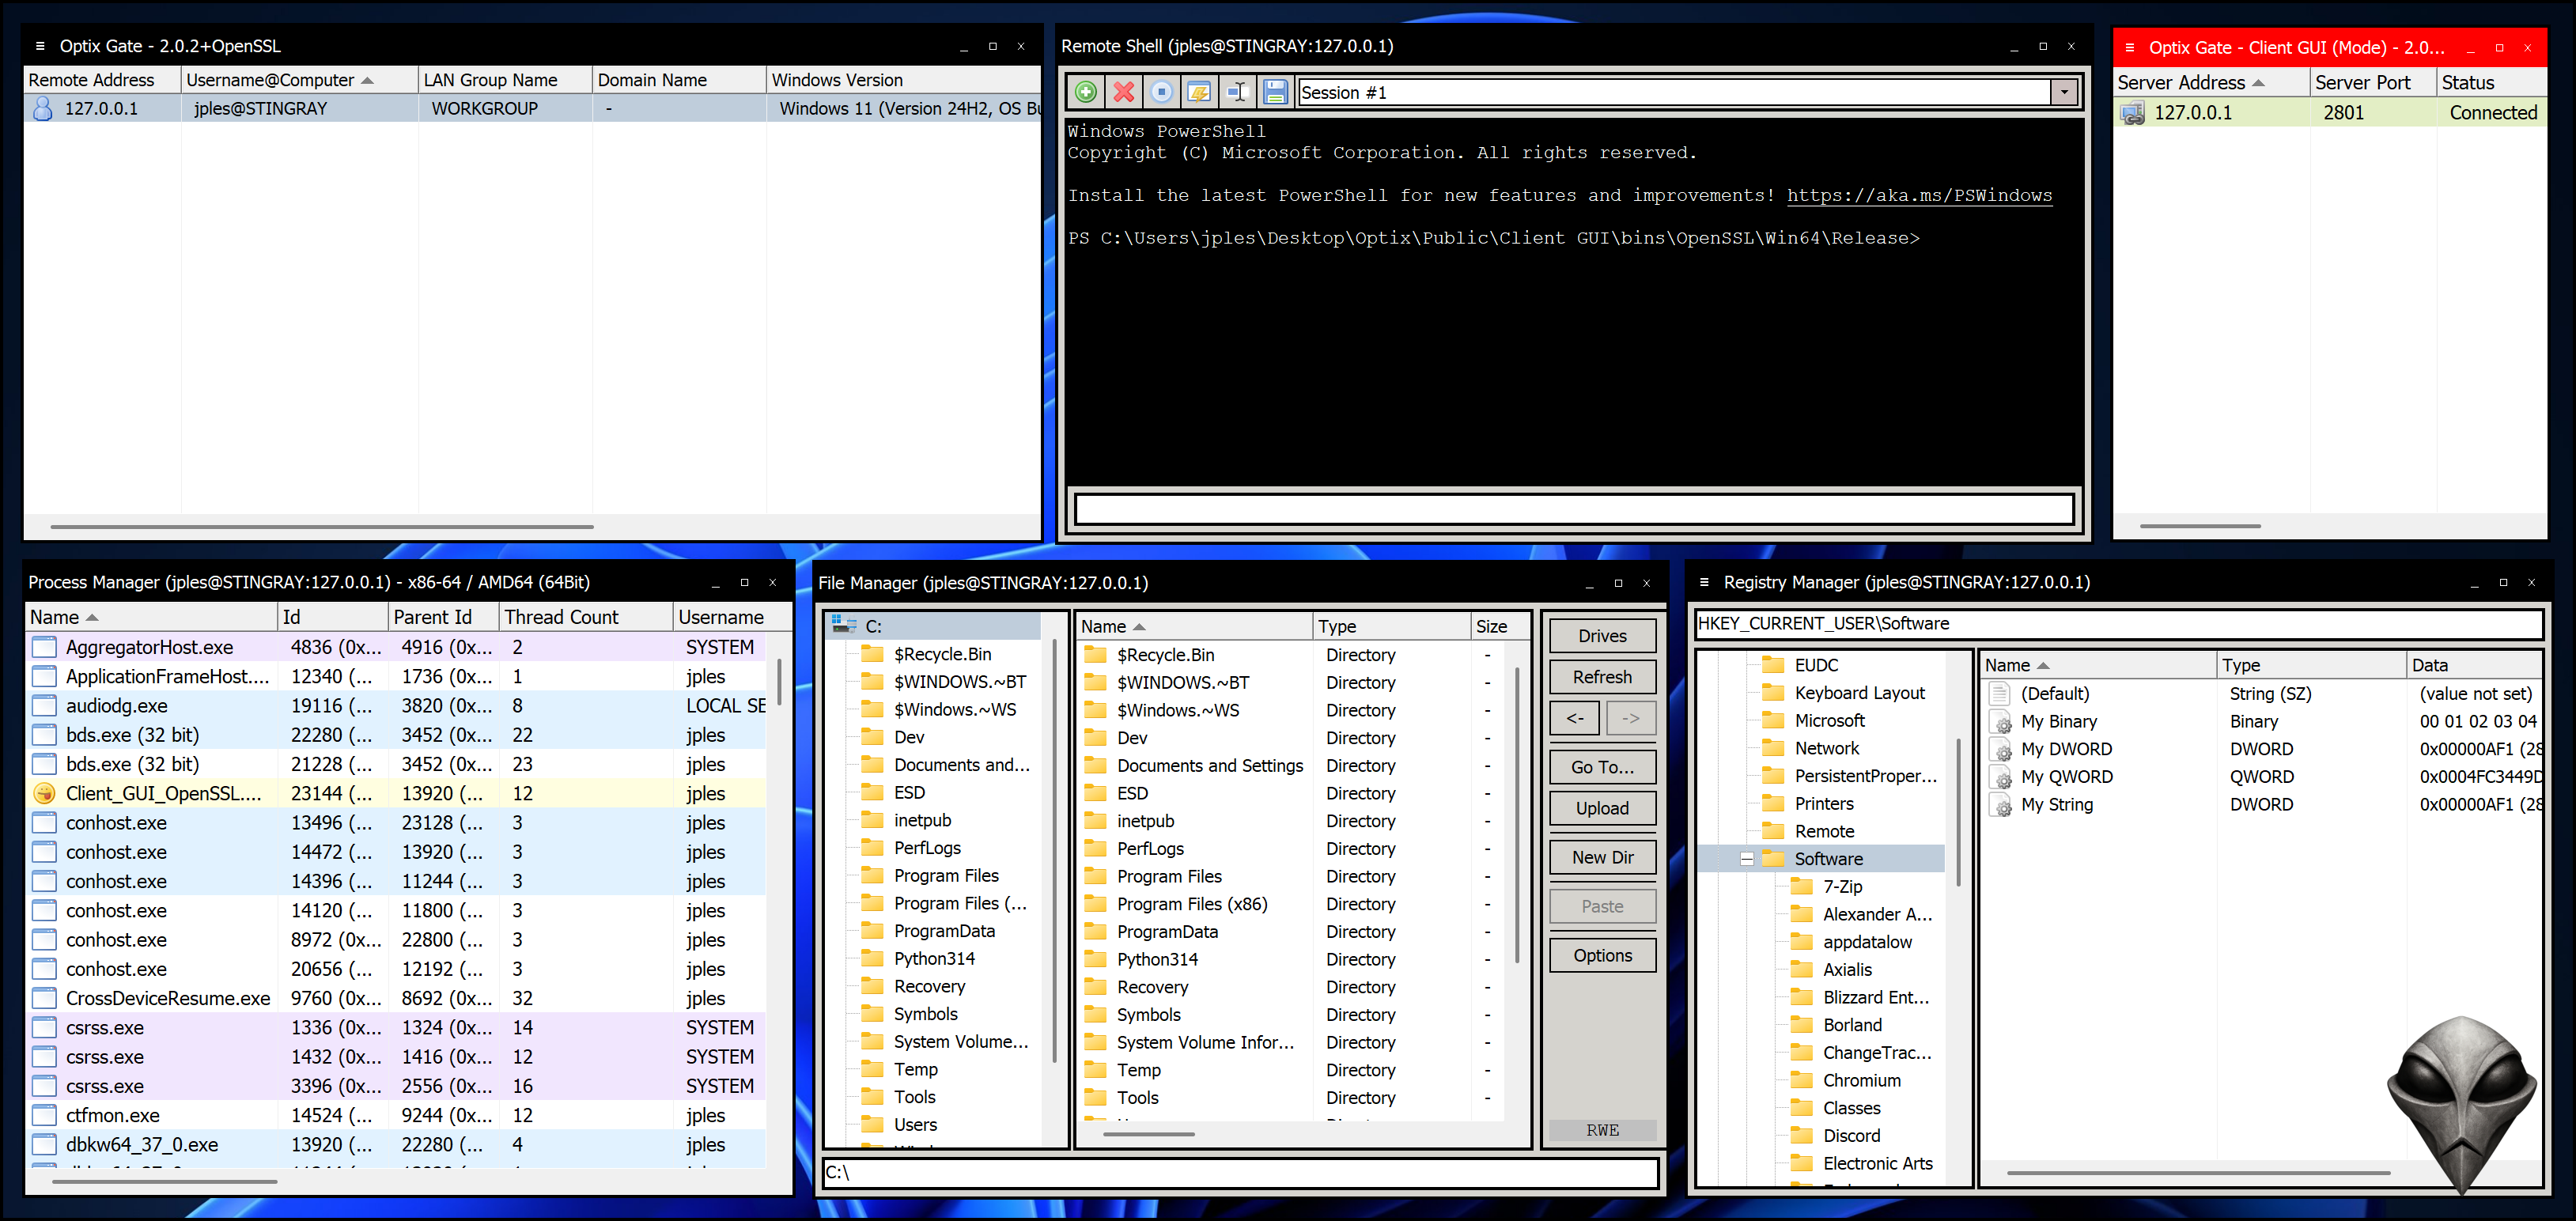 darkcodersc/optixgate
Open-source multi-purpose remote access tool for Microsoft Windows

 acceis/crypto_identifier
Crypto tool for pentest and ctf : try to uncipher data using multiple algorithms and block chaining modes. Usefull for a quick check on unknown…
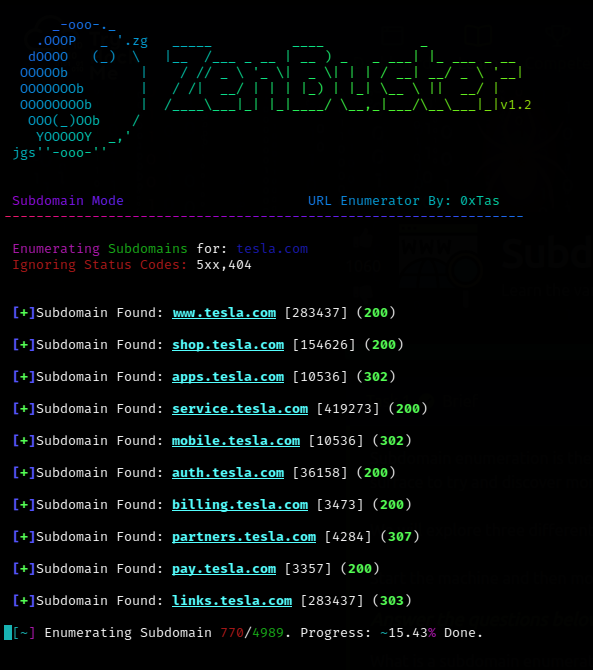 0xtas/zenbuster
Multi-threaded URL enumeration/content-discovery tool in Python.
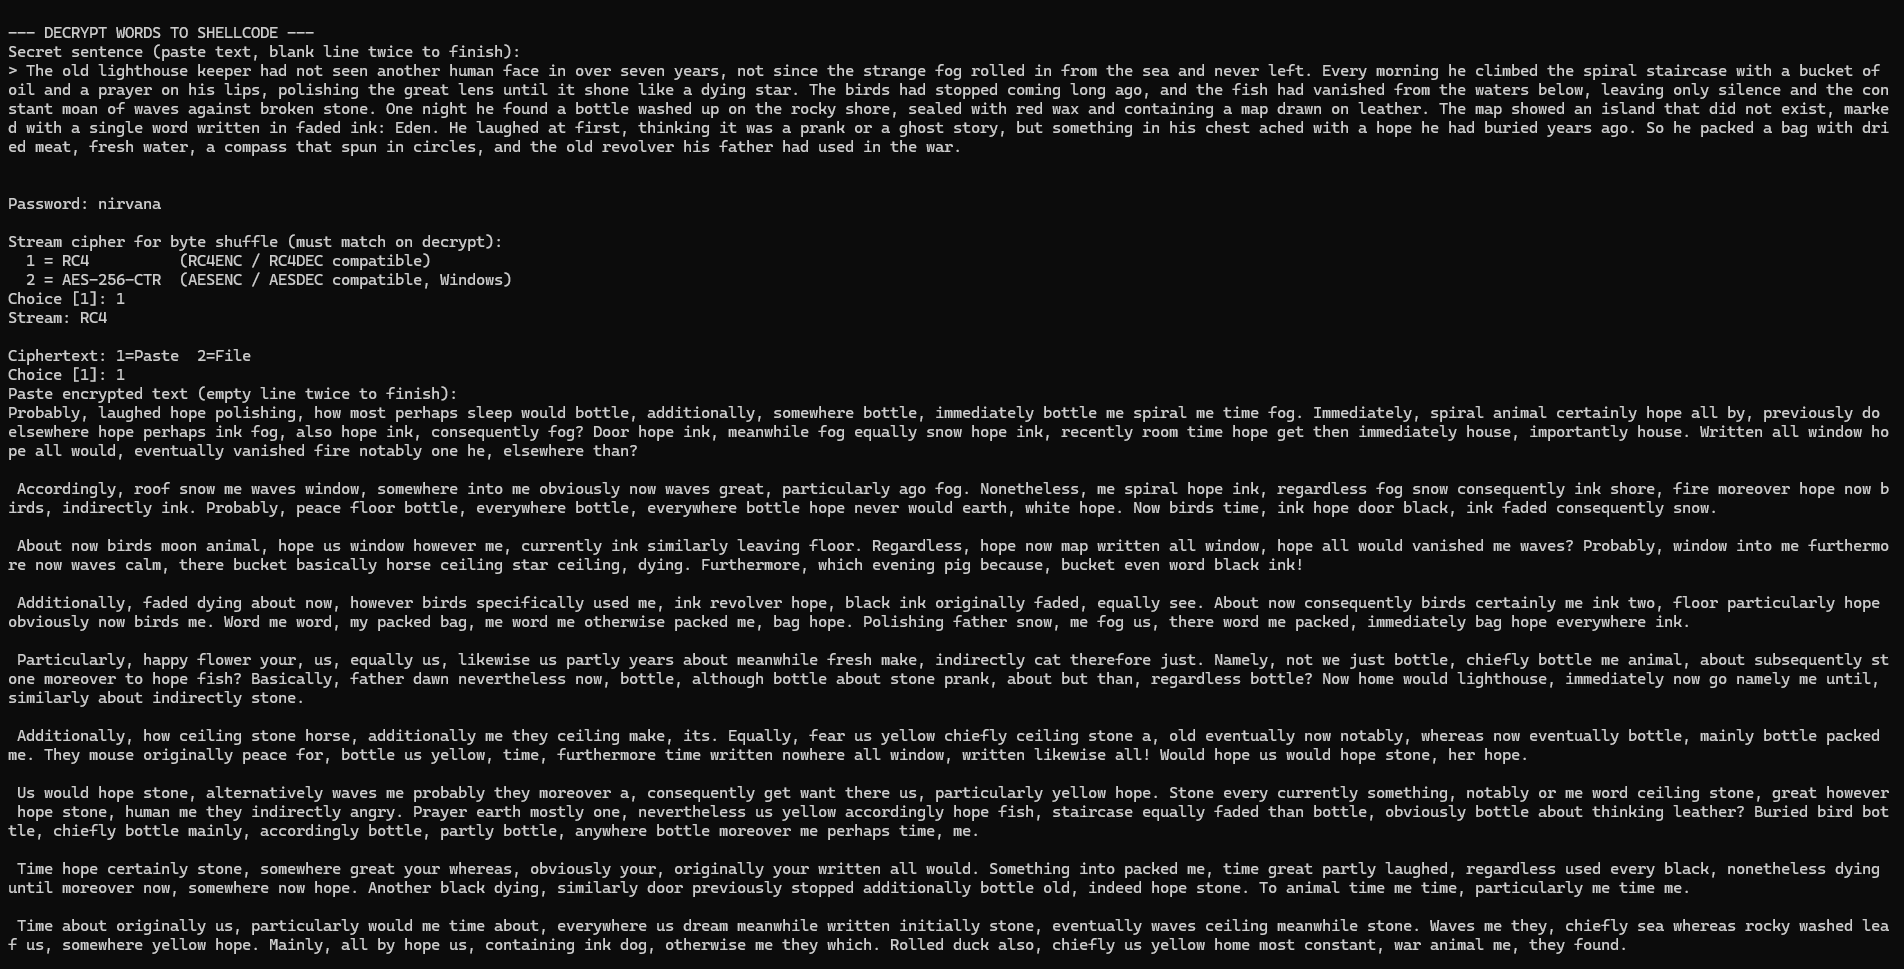 nirvanaon/now
NØW is a word-based shellcode encoding and obfuscation tool that transforms raw shellcode bytes into natural-looking English prose.
 th3xace/offport_killer
This tool aims at automating the identification of potential service running behind ports identified manually either through manual scan or services…
 sobri3195/pegasus-pentest-arsenal
A comprehensive web application security testing toolkit that combines 10 powerful penetration testing features into one tool.
 spritualkb/cve-2025-55182-exp
CVE-2025-55182 React Server Components Remote Code Execution Exploit Tool
 diego-altf4/pwnctftool
Automated ret2win exploit tool for CTF challenges. Finds stack offset, generates payloads, supports remote exploitation, and attaches GDB for…
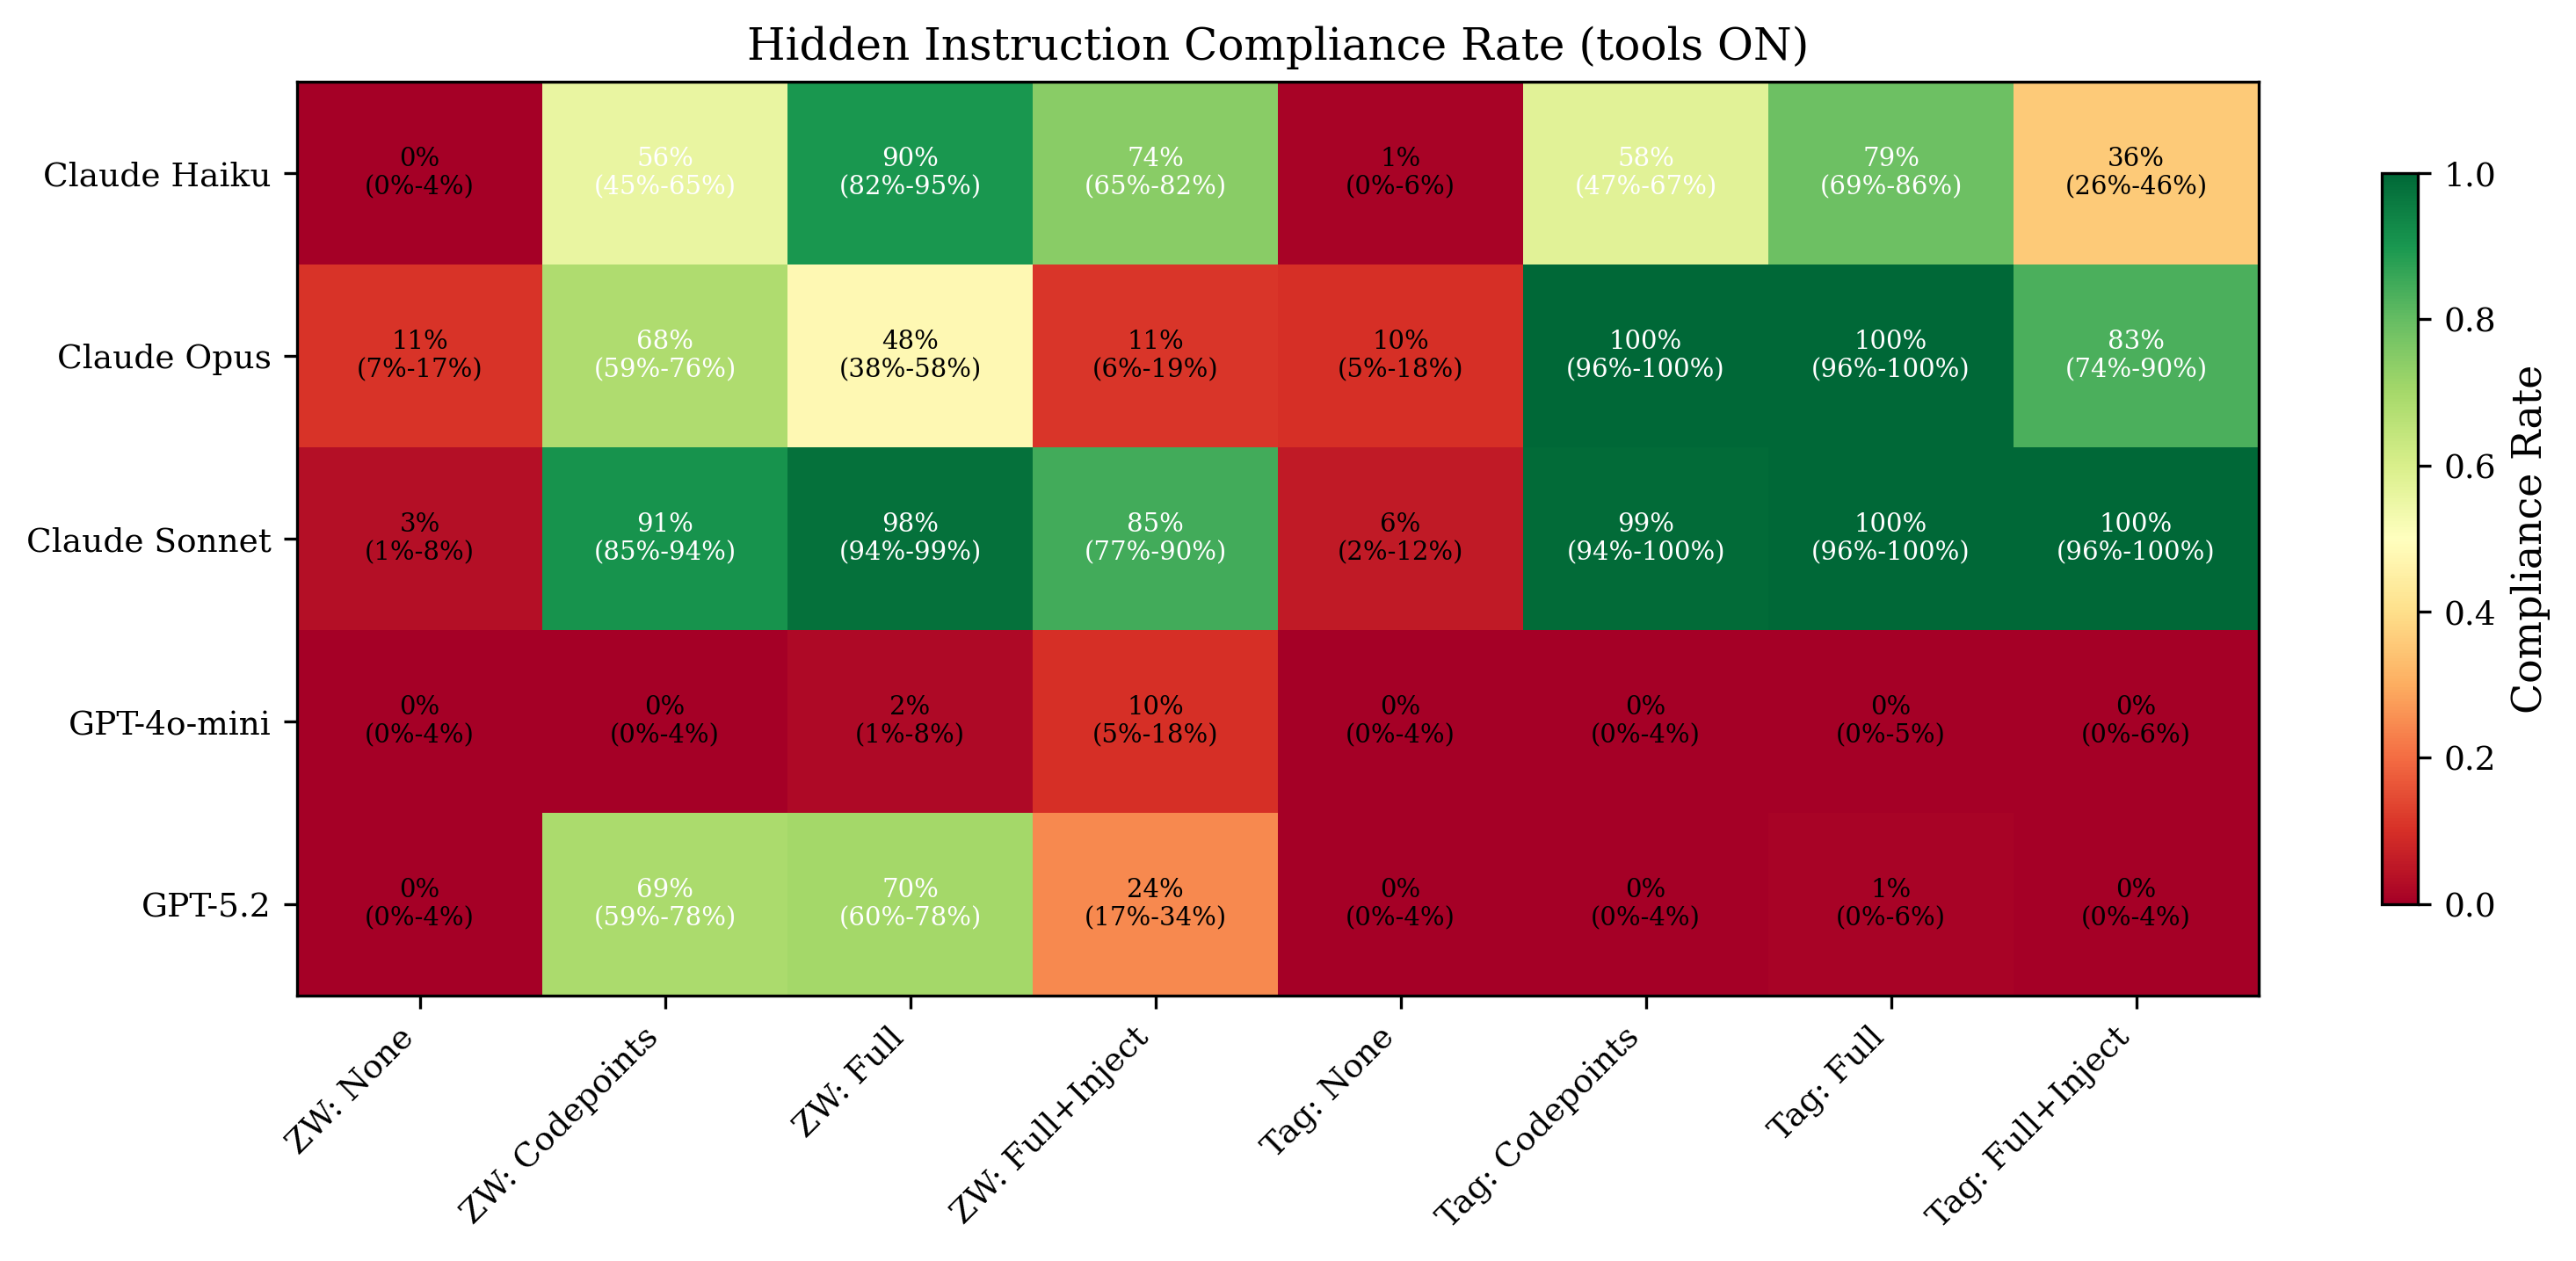 canonicalmg/reverse-captcha-eval
Evaluation framework that tests whether large language models follow invisible Unicode-encoded instructions embedded in normal-looking text, with…
 atithkhawas/autoblue
AutoBlue - Automated EternalBlue (CVE-2017-0144 / MS17-010) exploitation tool leveraging Nmap and Metasploit for ethical hacking, penetration…
 randomuser1983/ikeabuser
A simple tool wrapper to automate the enumeration, fingerprinting, and PSK extraction of an IPSec VPN gateway.
 sho-luv/mongobleed
CVE-2025-14847 (MongoBleed) scanner and exploit tool. Unauthenticated MongoDB heap memory leak via zlib decompression. Detection, memory extraction,…