
cve-2026-80428-ctf
 shivammittal2403/cve-2026-80428-ctf
Containerized educational CTF lab emulating CVE-2026-80428 (CWE-502 deserialization) for safe, isolated student and researcher practice.
container-securityctfdynamic-analysis-sandboxing+5
shivammittal2403/cve-2026-80428-ctfContainerized educational CTF lab emulating CVE-2026-80428 (CWE-502 deserialization) for safe, isolated student and researcher practice.
 cheese-hub/heartbleed
Educational Docker-based lab demonstrating the Heartbleed bug (CVE-2014-0160) with hacker, victim, and server containers for hands-on exploitation…
 d1se0/cve-2024-10924-bypass-mfa-wordpress-lab
Lab environment and exploit script for CVE-2024-10924, demonstrating MFA bypass in WordPress via the Really Simple SSL plugin's skip_onboarding…
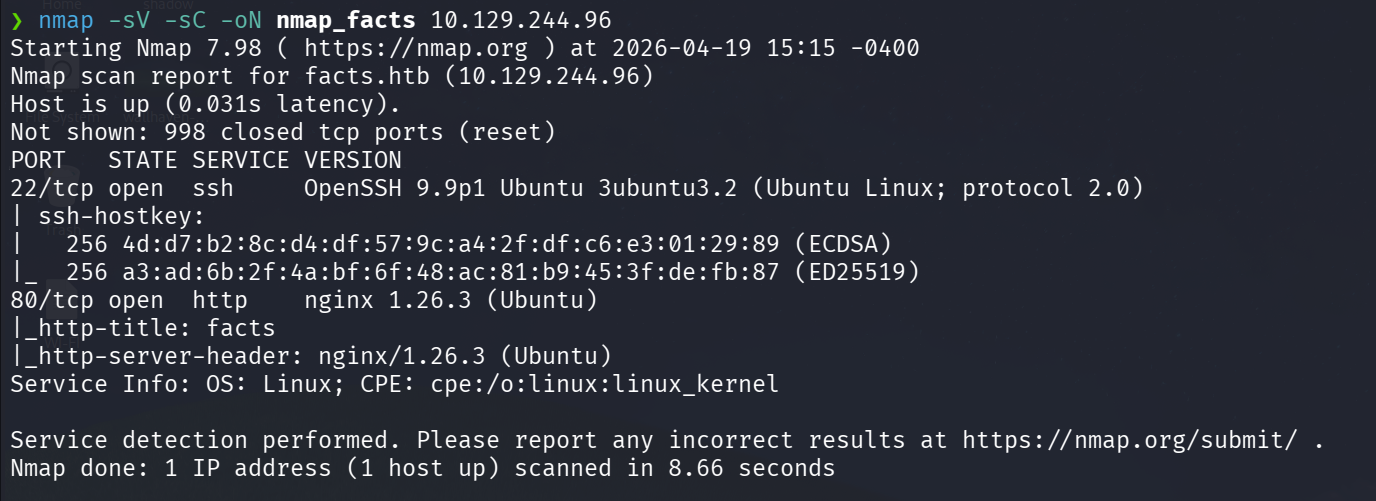 mattiapertusati/htb-facts
HackTheBox — Facts (Easy/Linux) | CVE-2025-2304 + AWS S3 + SSH Key + Facter PrivEsc
 musa-xvi/active-directory-badsuccessor
A TryHackme room covering the CVE-2025-53779 exploitation using windows
 aidilzlkfli/scanning
Analysis of network scan results, service vulnerabilities, OS fingerprinting, and critical Nessus findings including Ghostcat (CVE-2020-1938).
 tr00jan99/pwntilldawn-portal-walkthrough
A detailed penetration testing walkthrough and exploitation report for the 'Portal' machine, focusing on CVE-2011-2523 (vsFTPd 2.3.4 Backdoor) to…
 cyberone-teamares/jquery-cve-2022-31160
jquery XSS Proof of Concept (PoC)
 the-art-of-hacking/h4cker
Curated collection of cybersecurity resources, labs, and training materials covering ethical hacking, penetration testing, exploit development,…
 daffainfo/allaboutbugbounty
All about bug bounty (bypasses, payloads, and etc)
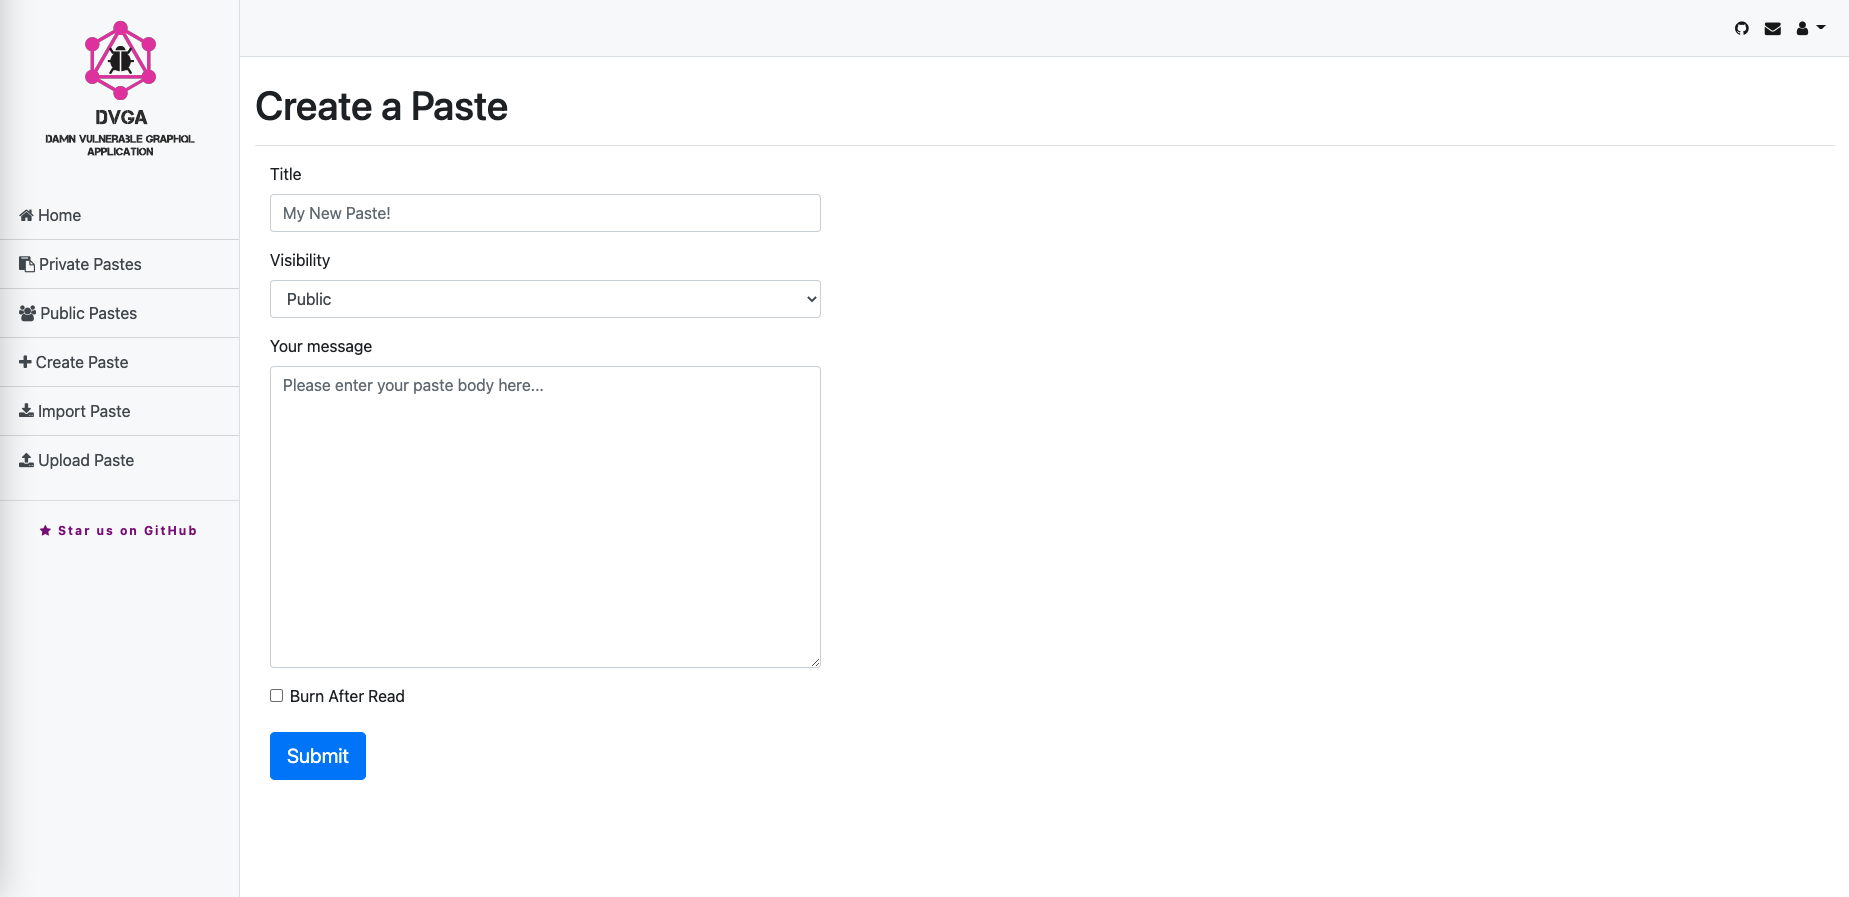 dolevf/damn-vulnerable-graphql-application
Damn Vulnerable GraphQL Application is an intentionally vulnerable GraphQL service implementation designed for learning about and practising GraphQL…
 karollooool/cve-2026-50416-writeup-and-poc
CVE-2026-50416: Windows 11 KASLR bypass
 seanpesce/cve-2024-22243
Example exploitable scenarios for CVE-2024-22243 affecting the Spring framework (open redirect & SSRF).