

Strapi-RCE
 hackhoven/strapi-rce
Exploit script showcasing a mixture of CVE-2019-18818 and CVE-2019-19609 for unauthenticated remote code execution in Strapi CMS.
ctfeducationexploitation+3
hackhoven/strapi-rceExploit script showcasing a mixture of CVE-2019-18818 and CVE-2019-19609 for unauthenticated remote code execution in Strapi CMS.
 foxyproxys/cve-2023-52654
Automated privilege escalation script exploiting misconfigured setuid/sgid binaries, sudo, cron, and LD_PRELOAD on Unix systems. Designed for CTF and…
 behindsecurity/htb-wifinetictwo-exploit
A simple python script to exploit CVE-2021-31630 on HTB WifineticTwo CTF
 ubuntustrike/cve-2017-9805-apache-struts-fuzz-n-sploit
A script to Fuzz and and exploit Apache struts CVE-2017-9805
 flojboj/cve-2024-32002
Educational exploit script for CVE-2024-32002 (Git RCE) with automated setup, designed for CTF environments and security training.
 silasspringer/cve-2018-10933
CTF challenge and exploit script for CVE-2018-10933, a libSSH authentication bypass, with Docker setup and walkthrough.
 rishabh-kumar-cyber-sec/cve-2023-27163-ssrf-to-port-scanning
It is a simple script to automate internal port scanning dueto SSRF in requests-baskets v 1.2.1. this script can also assisst in solving 'SAU'…
 diego-treitos/linux-smart-enumeration
Linux enumeration tool for pentesting and CTFs with verbosity levels
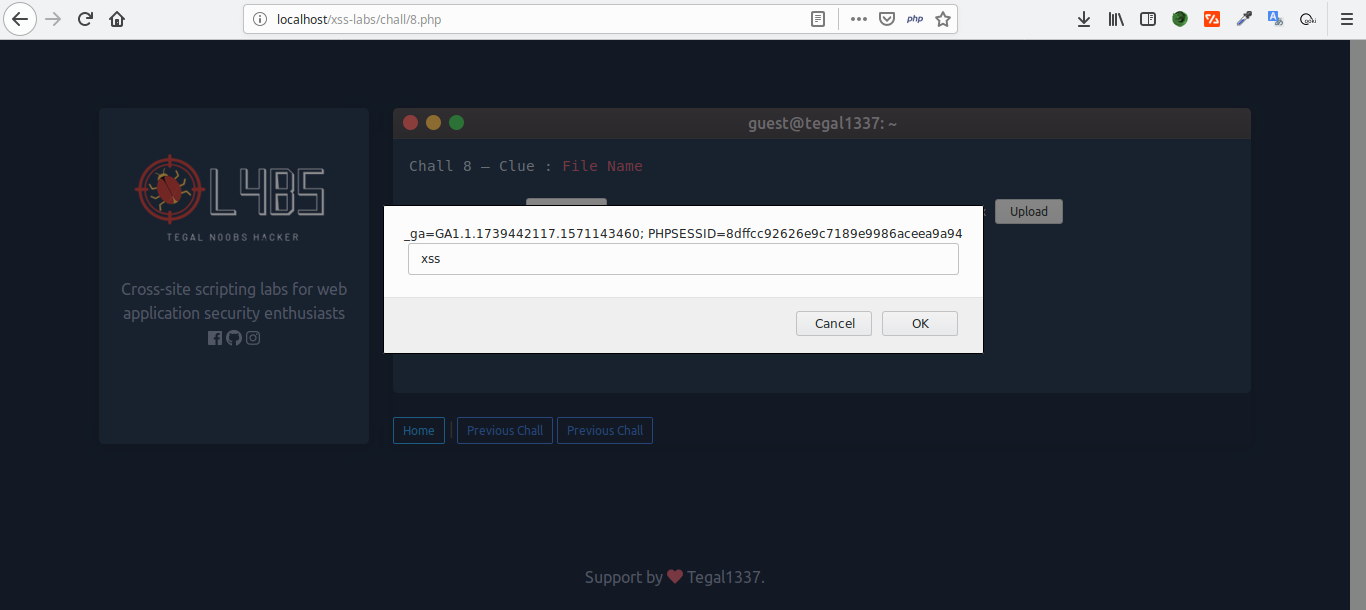 tegal1337/0l4bs
Cross-site scripting labs for web application security enthusiasts
 al1ex/awesome-pentest
Collection of penetration testing tools
 jeanpeyremesmots/osx-password-dumper
A tool to dump users's .plist on a Mac OS system and to convert them into a crackable hash
 hunt3r0x/cve-2021-31630-htb
proof of Concept (PoC) exploit for CVE-2021-31630, targeting the OpenPLC service running on the WifineticTwo box on the Hack The Box platform.
 cpu0x00/cve-2021-3560
ubuntu new PrivEsc race condition vulnerability
 kentox493/cve-2026-42945_nginxrift
Automates CVE-2026-42945 exploitation in NGINX containers: verifies vulnerable targets, brute-forces heap offsets, executes commands, and opens an…
 baptistecontreras/cve-2017-8917-joomla
CVE-2017-8917 SQL injection Vulnerability in Joomla! 3.7.0 exploit
 0xdak/cve-2026-44881_exploit
Single-script exploit for CVE-2026-44881 that chains .git credential leakage, Portainer Git-symlink injection, arbitrary host file read, and SSH…
 rootharpy/cve-2025-5287
Unauthenticated SQL Injection exploit for WordPress Likes and Dislikes Plugin ≤ 1.0.0
 kaleth4/cve-2026-20896
Automated PoC exploit for CVE-2026-20896, a Gitea authentication bypass via directory traversal in the API authorization header, enabling…