
SharkMCP
 weirdmachine64/sharkmcp
A swiss-knife MCP server for analysing PCAP files
ctfdigital-forensicseducation+6
weirdmachine64/sharkmcpA swiss-knife MCP server for analysing PCAP files
 sadfud/exploits
Real world and CTFs exploiting web/binary POCs.
 astrosp/awesome-osint-list
📡 Comprehensive collection of OSINT tools for cybersecurity professionals, researchers, and bug bounty hunters. Topics: information gathering,…
 v33ru/awesome-connected-things-sec
A Curated list of Security Resources for all connected things
 hhhrrrttt222111/ethical-hacking-tools
Complete Listing and Usage of Tools used for Ethical Hacking
 owasp/wrongsecrets-binaries
Source code for the Binaries of OWASP WrongSecrets
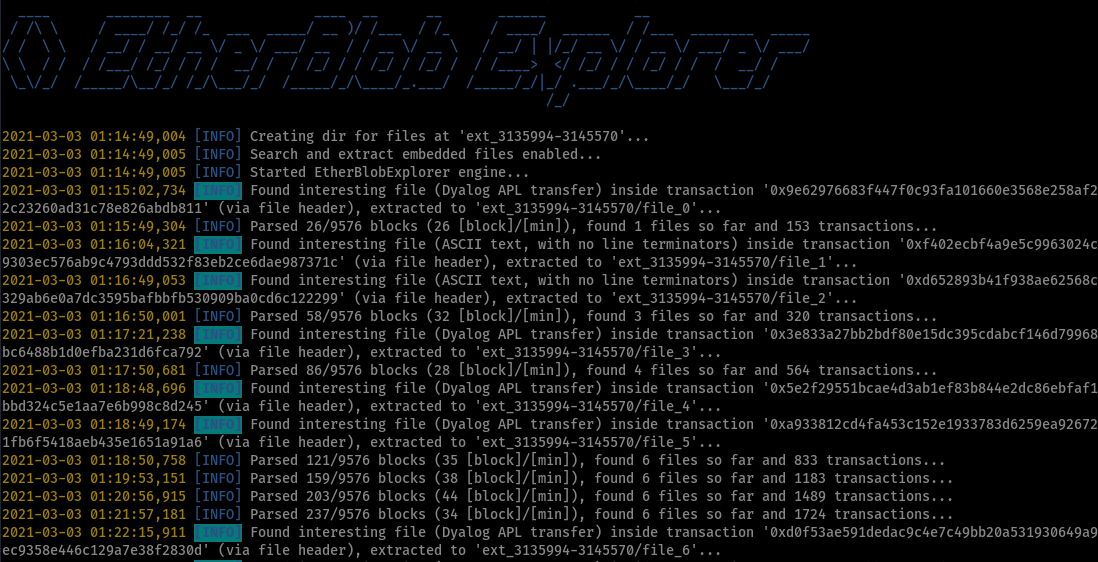 litneet64/etherblob-explorer
Search and extract blob files on the Ethereum Blockchain network
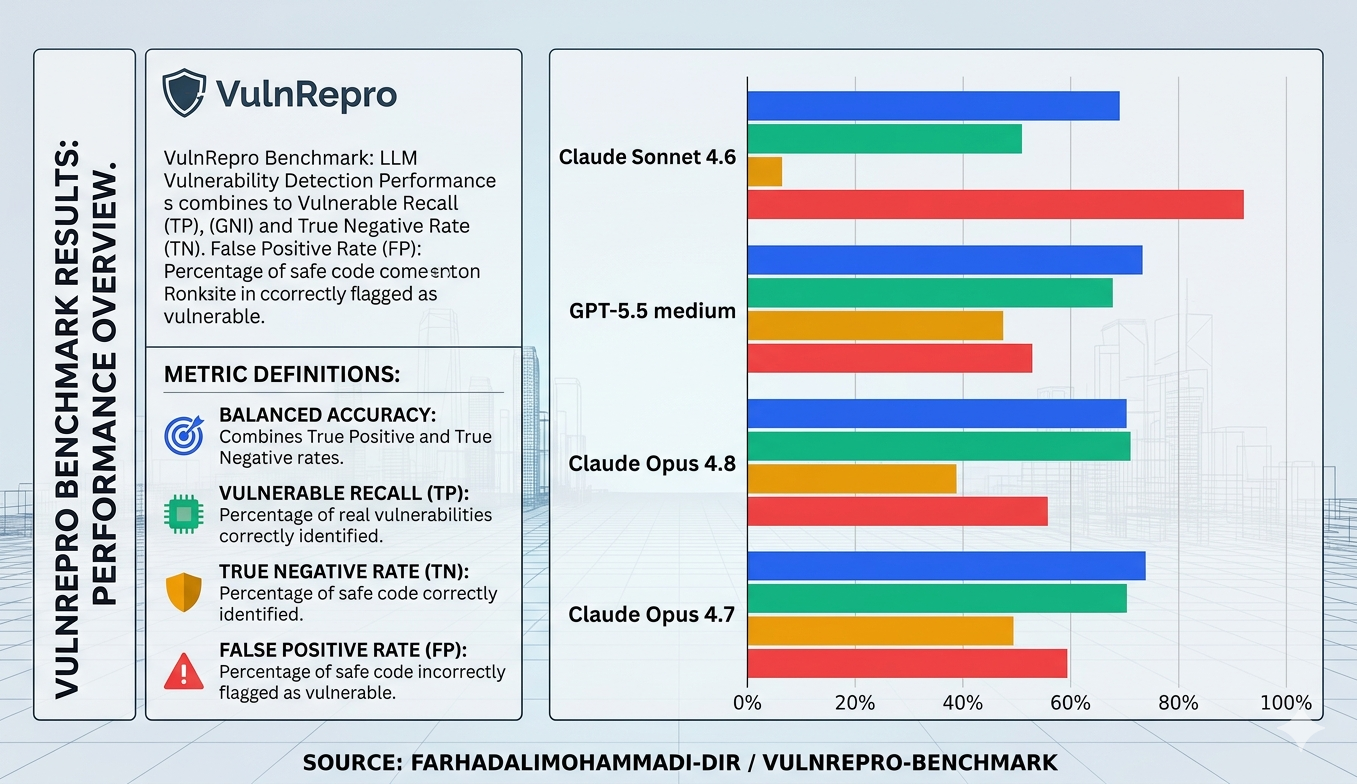 farhadalimohammadi-dir/vulnrepro-benchmark
Benchmark measuring AI models' ability to detect vulnerabilities in source code via real bug bounty cases with balanced recall and false-positive…
 3jee/copy-fail-go
Go port of the CVE-2026-31431 (copy-fail) Linux kernel privilege escalation PoC, with automatic SUID binary enumeration and interactive target…
 autorecon/autorecon
Multi-threaded network reconnaissance tool that automates service enumeration, port scanning, and information gathering for penetration testing and…
 ticarpi/jwt_tool
:snake: A toolkit for testing, tweaking and cracking JSON Web Tokens
 diego-treitos/linux-smart-enumeration
Linux enumeration tool for pentesting and CTFs with verbosity levels
 swisskyrepo/graphqlmap
Security module for php7 and php8 - Killing bugclasses and virtual-patching the rest!
 dolevf/damn-vulnerable-graphql-application
Damn Vulnerable GraphQL Application is an intentionally vulnerable GraphQL service implementation designed for learning about and practising GraphQL…
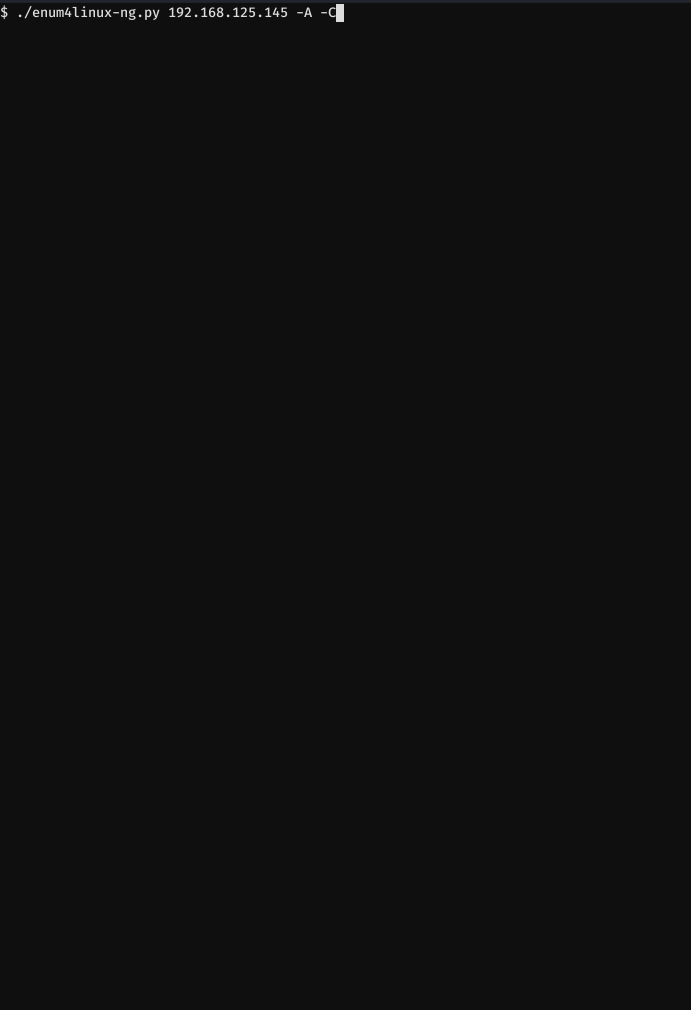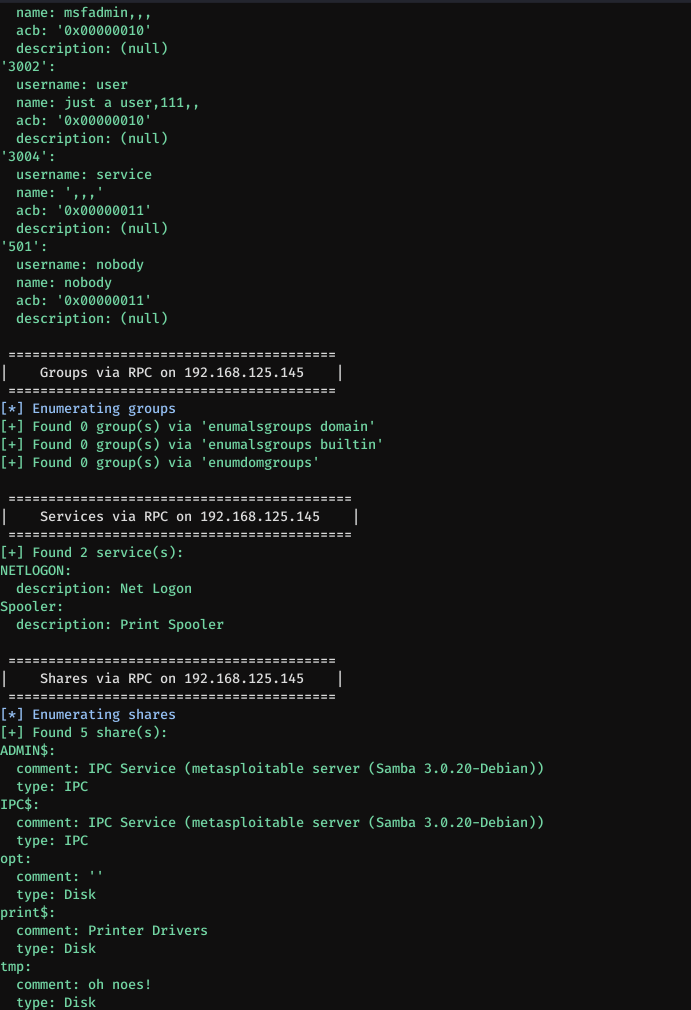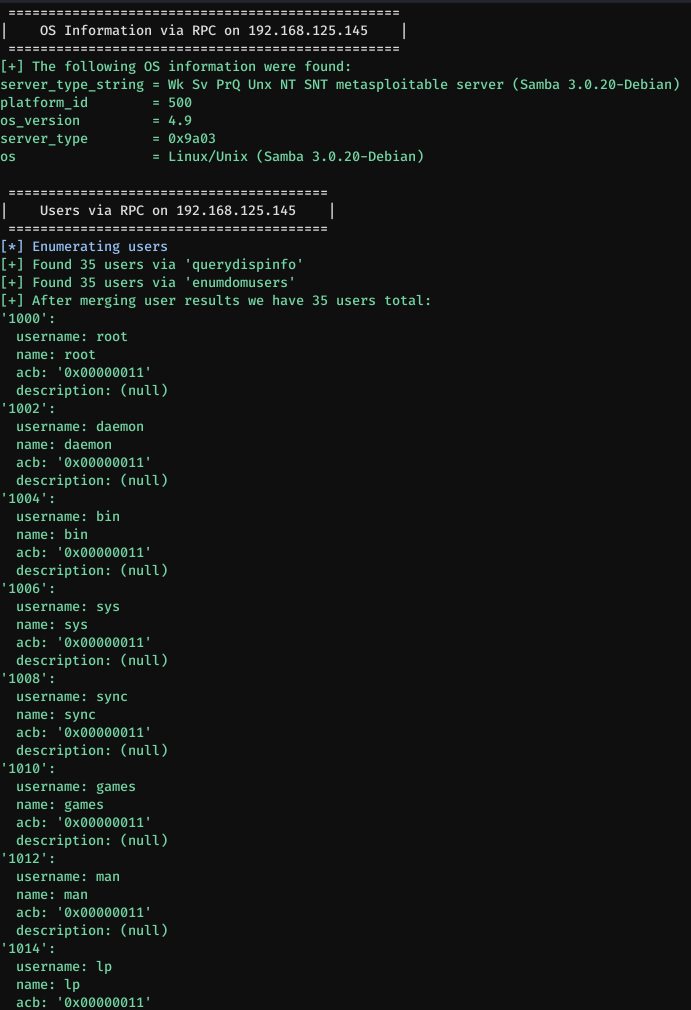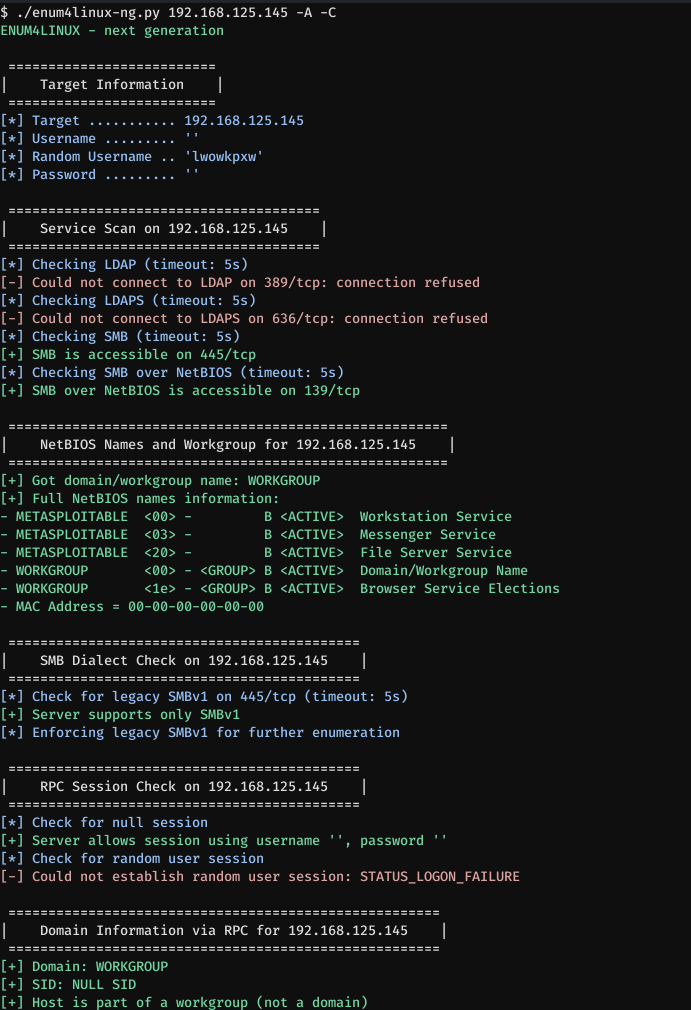 cddmp/enum4linux-ng
A next generation version of enum4linux (a Windows/Samba enumeration tool) with additional features like JSON/YAML export. Aimed for security…
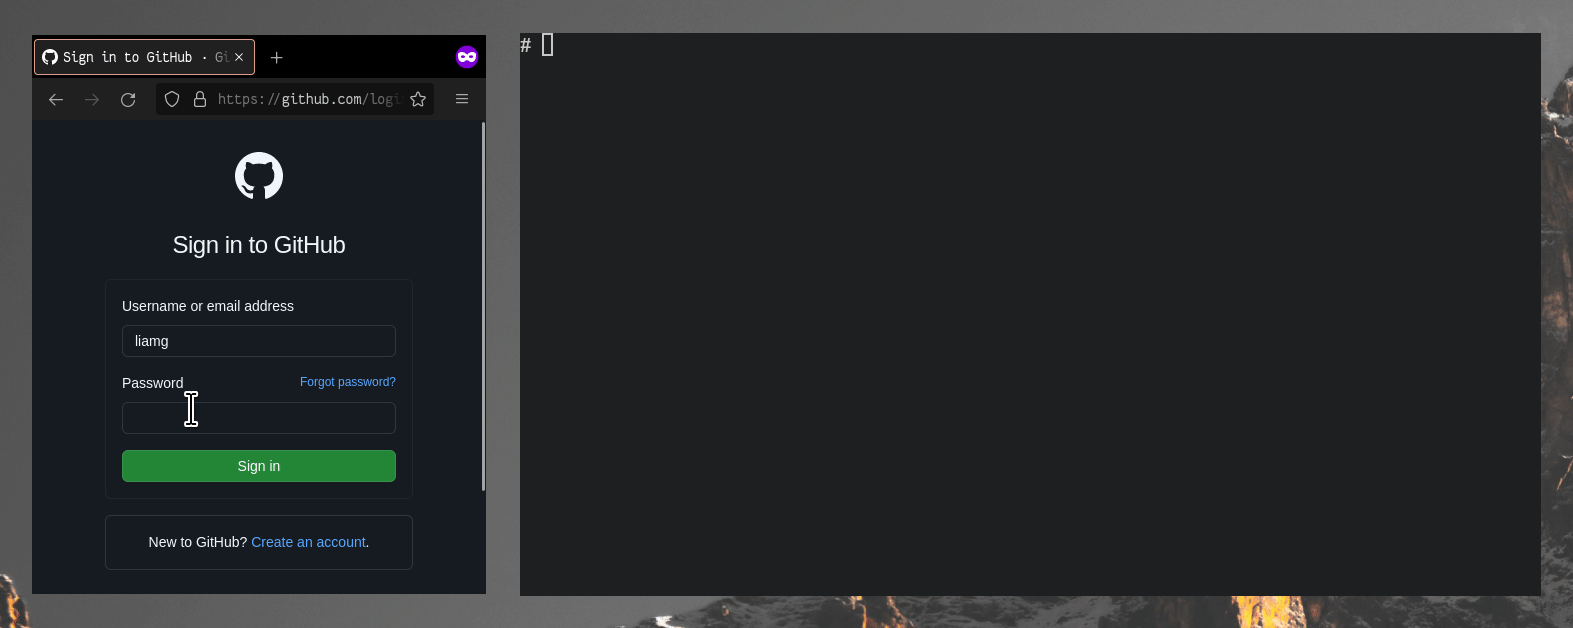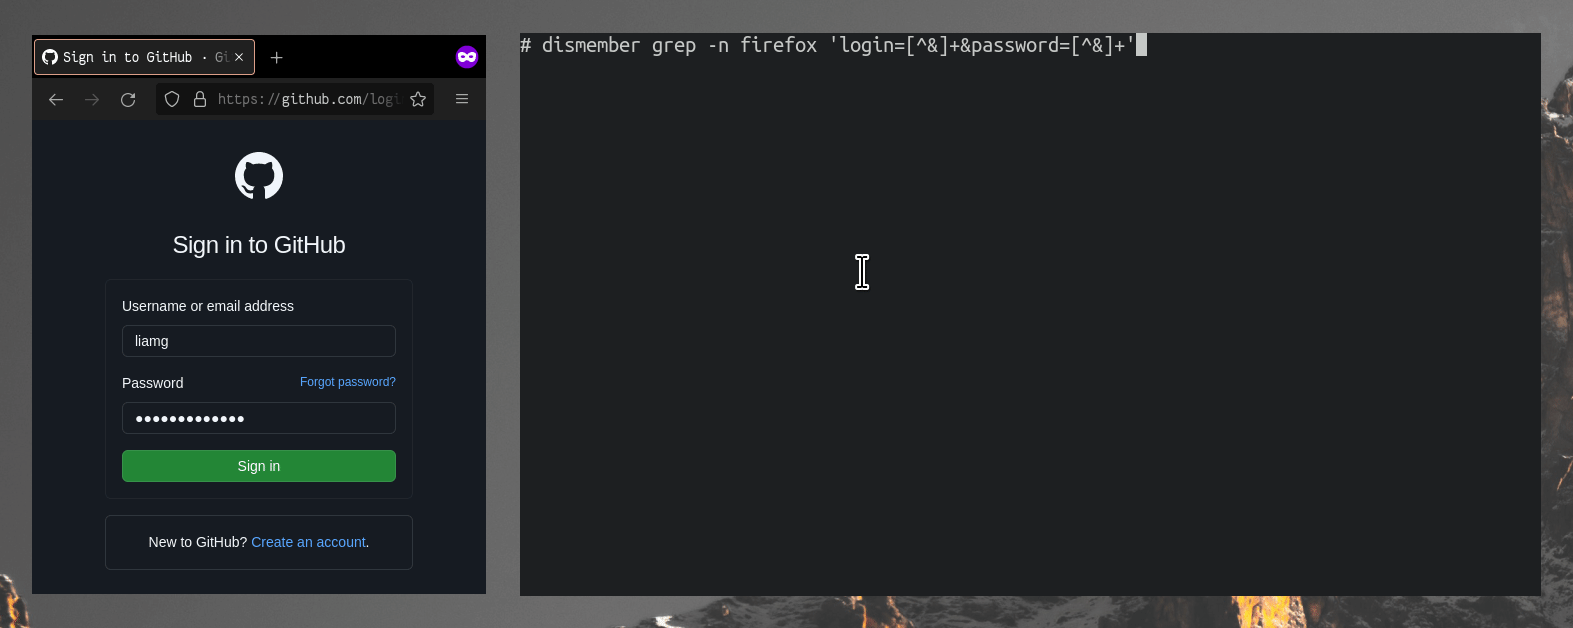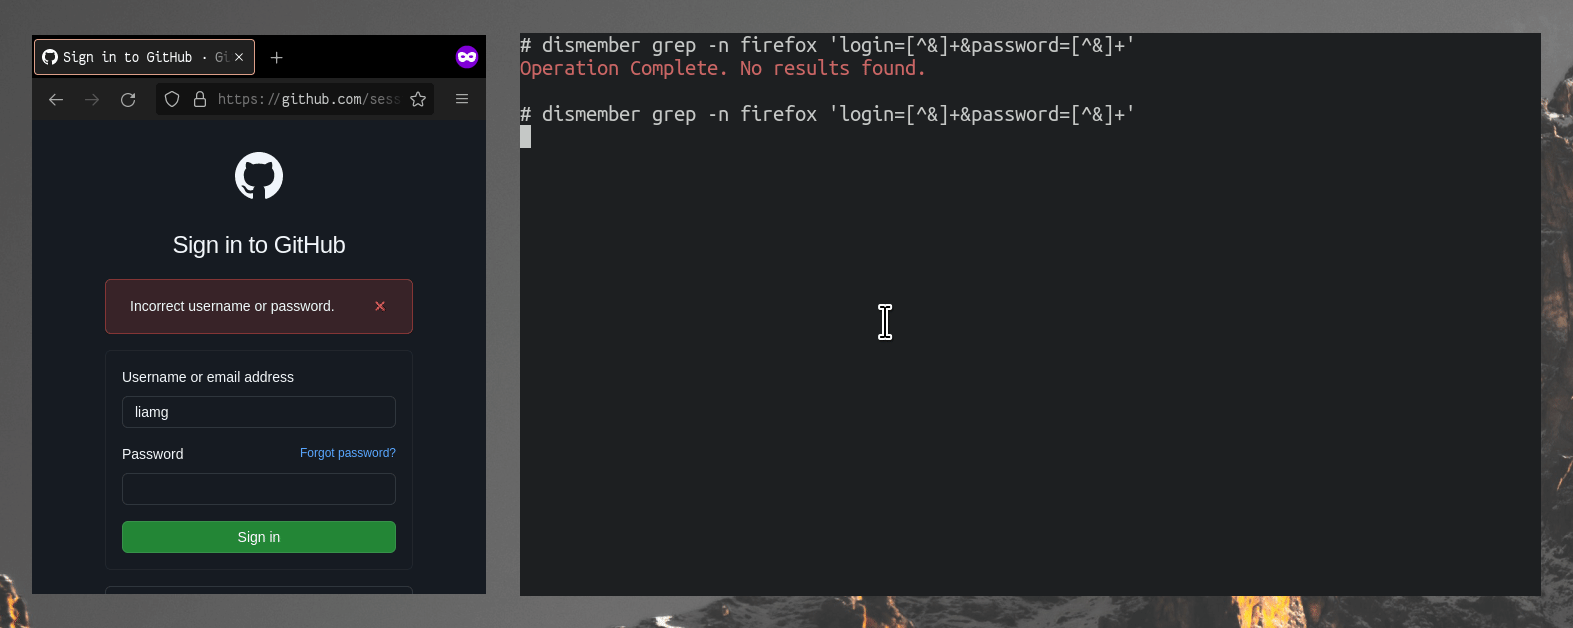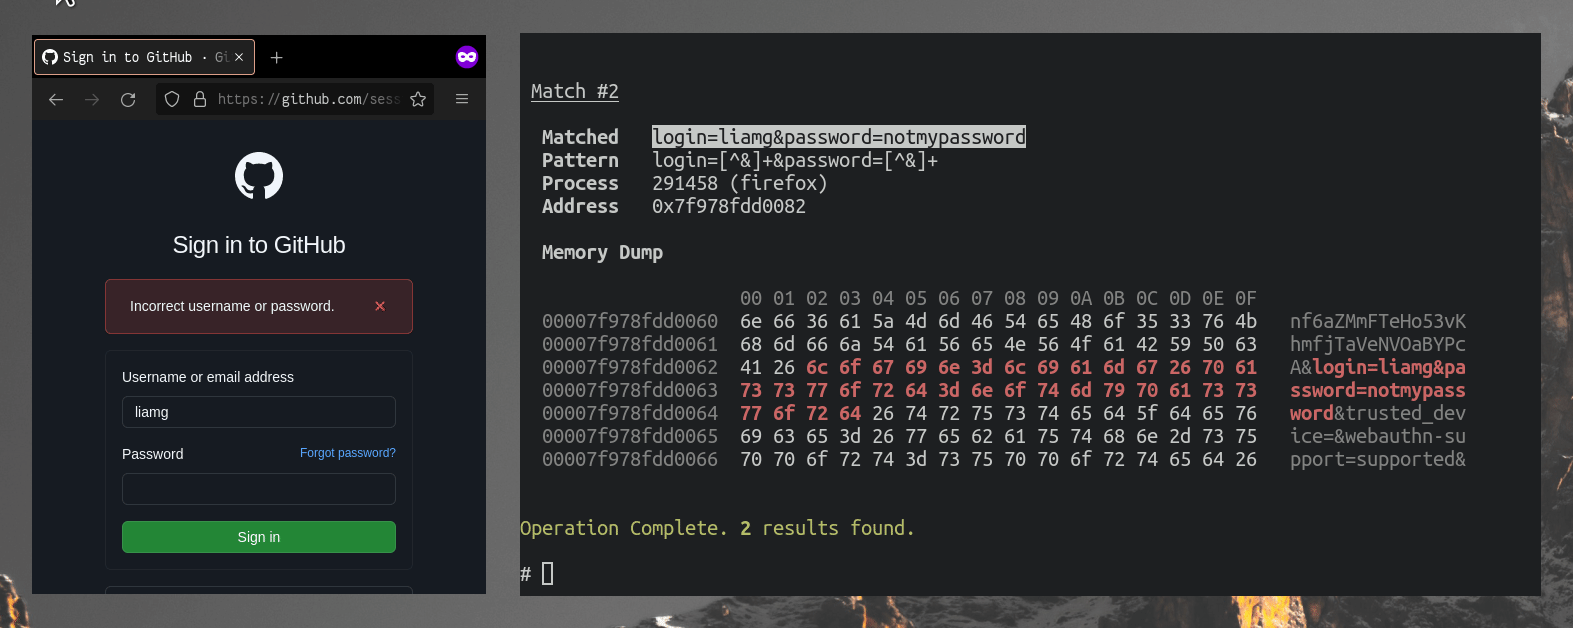 liamg/dismember
:knife: Scan memory for secrets and more. Maybe eventually a full /proc toolkit.
 asaotomo/hx0-hawkeye
一个轻量级浏览器抓包与安全分析扩展,在浏览器侧边栏中即可完成抓包、拦截、修改、重放、规则检测与AI辅助分析的完整工作流。(A lightweight browser extension for traffic capture and security analysis, enabling…
 th3xace/offport_killer
This tool aims at automating the identification of potential service running behind ports identified manually either through manual scan or services…