
CVE-2026-8206-Lab
 rootdirective-sec/cve-2026-8206-lab
Local Docker lab demonstrating CVE-2026-8206 unauthenticated account takeover in Kirki WordPress plugin. Compares vulnerable 6.0.6 vs patched 6.0.7…
ctfeducationexploitation+3
rootdirective-sec/cve-2026-8206-labLocal Docker lab demonstrating CVE-2026-8206 unauthenticated account takeover in Kirki WordPress plugin. Compares vulnerable 6.0.6 vs patched 6.0.7…
 segunakinsoyinu/cve-2024-42009-roundcube-xss
Stored XSS exploit for Roundcube Webmail ≤1.6.6 (CVE-2024-42009) with zero-click email exfiltration via CSS animation event handlers. Includes SMTP…
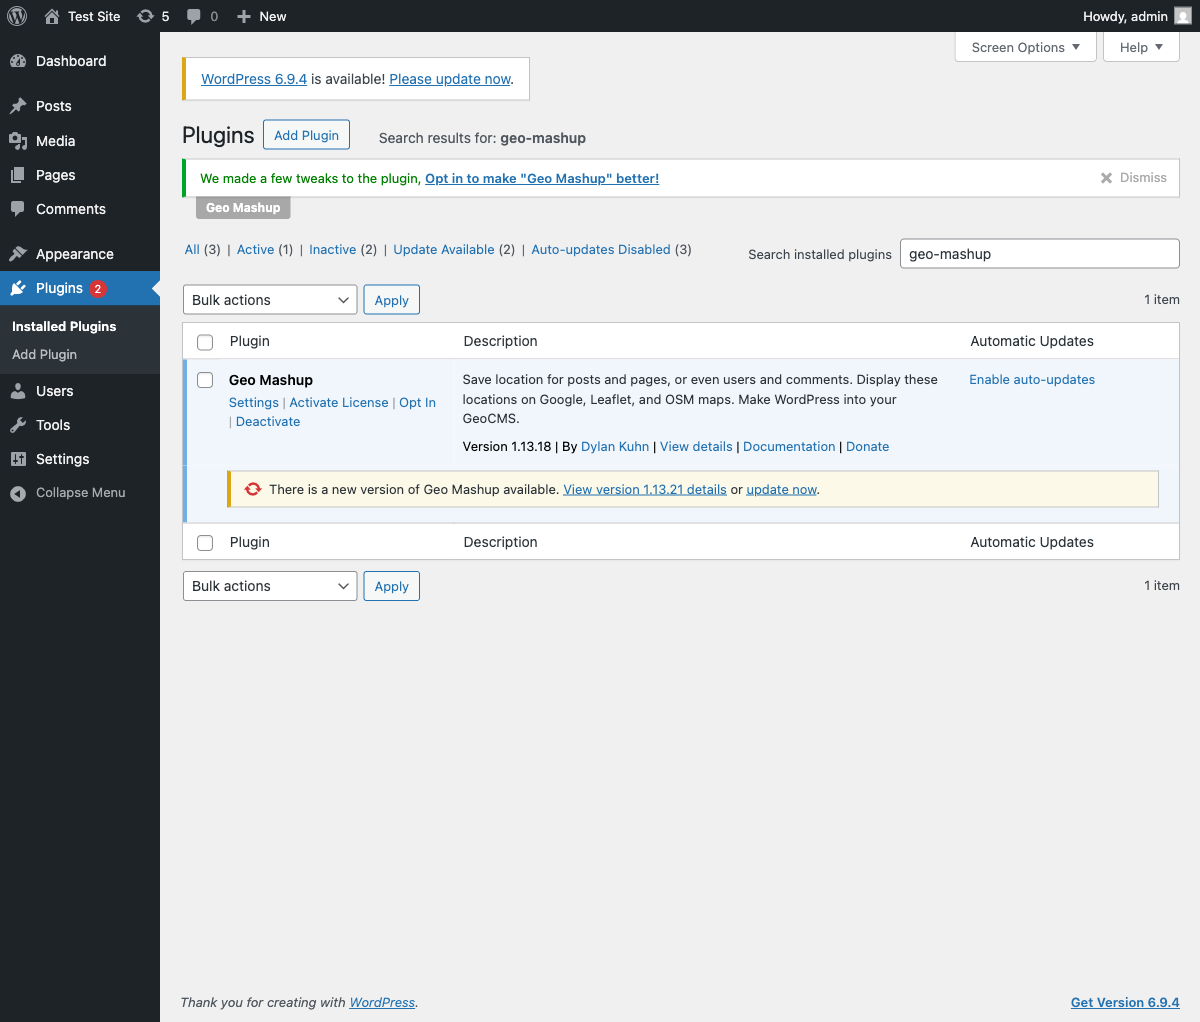 ydking0911/cve-2026-4060-poc
Proof-of-concept for CVE-2026-4060: unauthenticated time-based blind SQL injection in Geo Mashup WordPress plugin via ORDER BY clause. Includes…
 ash1996x/cve-2025-50154-aggressor-script
Cobalt Strike Aggressor script that weaponizes LNK and Library-MS files to trigger SMB NTLMv2 hash disclosure, including CVE-2025-24054 bypass, for…
 rootdirective-sec/cve-2025-11262-lab
Docker lab for reproducing CVE-2025-11262, an unauthenticated stored blind XSS in Link Whisper Free WordPress plugin. Includes vulnerable and patched…
 rootdirective-sec/cve-2026-33626-lab
Docker Compose lab reproducing CVE-2026-33626 SSRF in LMDeploy's vision-language image loader. Compares vulnerable (0.12.0) and patched (0.12.3)…
 mhamzakhattak/cve-2025-29927
CTF-style proof-of-concept demonstrating CVE-2025-29927 Next.js middleware authorization bypass. Includes vulnerable Docker app and exploit script to…
 maradonam18/-cve-2025-59528-poc
A simple python script to exploit CVE-2025-59528, this an Authenticated RCE vulnerability in Flowise application, a popular AI tool. That is also…
 trax69/cve-2025-55182-poc
Proof of Concept for CVE-2025-55182 ("React2Shell"). A fully dockerized environment demonstrating Remote Code Execution (RCE) via insecure…
 ahmedf000/cve-2025-49132_htb_season10
Unauthenticated RCE exploit for CVE-2025-49132 in Pterodactyl Panel via path traversal, PEAR command injection, and PHP code execution. Includes HTB…

 jithinodattu/cve-2007-4559-lab
Self-contained Docker lab demonstrating CVE-2007-4559 (TarSlip) directory traversal via Python's tarfile module. Includes vulnerable and fixed APIs,…
 stellardriftlabs/cve-2018-8097-poc
POC for CVE-2018-8097 This script exploits CVE-2018-8097 and can retrieve files and contents using a blind RCE method.
 maikneysm/autopwn-titanic.htb
This is an automated exploitation script for the Hack The Box machine *Titanic*. It extracts Gitea user hashes via LFI, assists in cracking them, and…
 n0m4d22/poc-cve-2015-10141-xdebug
Proof-of-Concept exploit script for Xdebug 2.5.5 and earlier versions (CVE-2015-10141).
 nou-man/cve-2022-46169
Proof of concept / CTF script for exploiting CVE-2022-46169 in Cacti, versions >=1.2.22
 n1et/cve-2021-4034
Shell script that exploits CVE-2021-4034 (PwnKit) for local privilege escalation, intended for CTF use.
 henryisnotavailable/dompdf-exploit-rce
An exploit script for CVE-2022-28368 designed to make exploitation less annoying, made for a HTB machine