

x64dbg
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
ai-assisted-reversingbinary-analysisbinary-exploitation+7
50.1k2 days ago
x64dbg/x64dbgAn open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
 karollooool/cve-2026-50416-writeup-and-poc
CVE-2026-50416: Windows 11 KASLR bypass
 kentox493/cve-2026-42945_nginxrift
Automates CVE-2026-42945 exploitation in NGINX containers: verifies vulnerable targets, brute-forces heap offsets, executes commands, and opens an…
 fernandocassiodev/cve-2015-1328
Step-by-step walkthrough for exploiting CVE-2015-1328 (OverlayFS) to escalate privileges from a low-privileged user to root on Ubuntu 14.04. Includes…
 ixzodiak/cve-2025-8110
Gogs service Exploit and get the root user
 hunt-benito/ash-authentication-oauth2-oidc-account-takeover-cve-2026-49757-email-based-user-matching
Proof-of-concept exploit for CVE-2026-49757 demonstrating OAuth2/OIDC account takeover via email-based user matching in AshAuthentication, with…
 0xcyberstan/cve-2026-46215-poc
Exploit for CVE-2026-46215, a Linux kernel DRM GEM use-after-free local privilege escalation. Uses racing, slab spraying, and Dirty Pipe-style file…
 hann1bl3l3ct3r/cve-2026-6145
User Registration & Membership <= 5.1.5 - Unauthenticated Missing Authorization to Admin Approval Bypass via 'action' Parameter
 rippsec/cve-2025-49113-roundcube-rce
CVE-2025-49113 – Roundcube ≤1.6.10 post-auth RCE via PHP object deserialization (HackTheBox CTF)
 th3xace/sudo_killer
A tool designed to exploit a privilege escalation vulnerability in the sudo program on Unix-like systems. It takes advantage of a specific…
 mafiosohack/offensive-lab-2
Penetration test walkthrough on a vulnerable Ubuntu VM. Exploited the ProFTPD 1.3.3c backdoor (CVE-2010-4221) to gain root access and capture the…
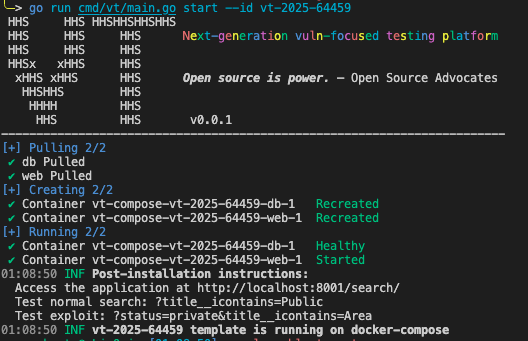 omarkurt/django-connector-cve-2025-64459-testbed
A self-contained testbed for Django CVE-2025-64459. Demonstrates QuerySet.filter() parameter injection via dictionary expansion using Docker.
 0xdtc/crushftp-auth-bypass-cve-2025-31161
Exploit for CrushFTP CVE-2025-31161 auth bypass: detects vulnerable targets, enumerates users, and creates unauthorized admin accounts through…
 carlosrpastrana/cve-2011-2553
Bash exploit for CVE-2011-2553 enabling remote code execution and privilege escalation on vulnerable FTP services via a special character in the USER…
 eyodav/cve-2025-34157
A stored XSS in the project delete flow allows execution of attacker-controlled JavaScript in an administrator’s browser when the admin attempts to…
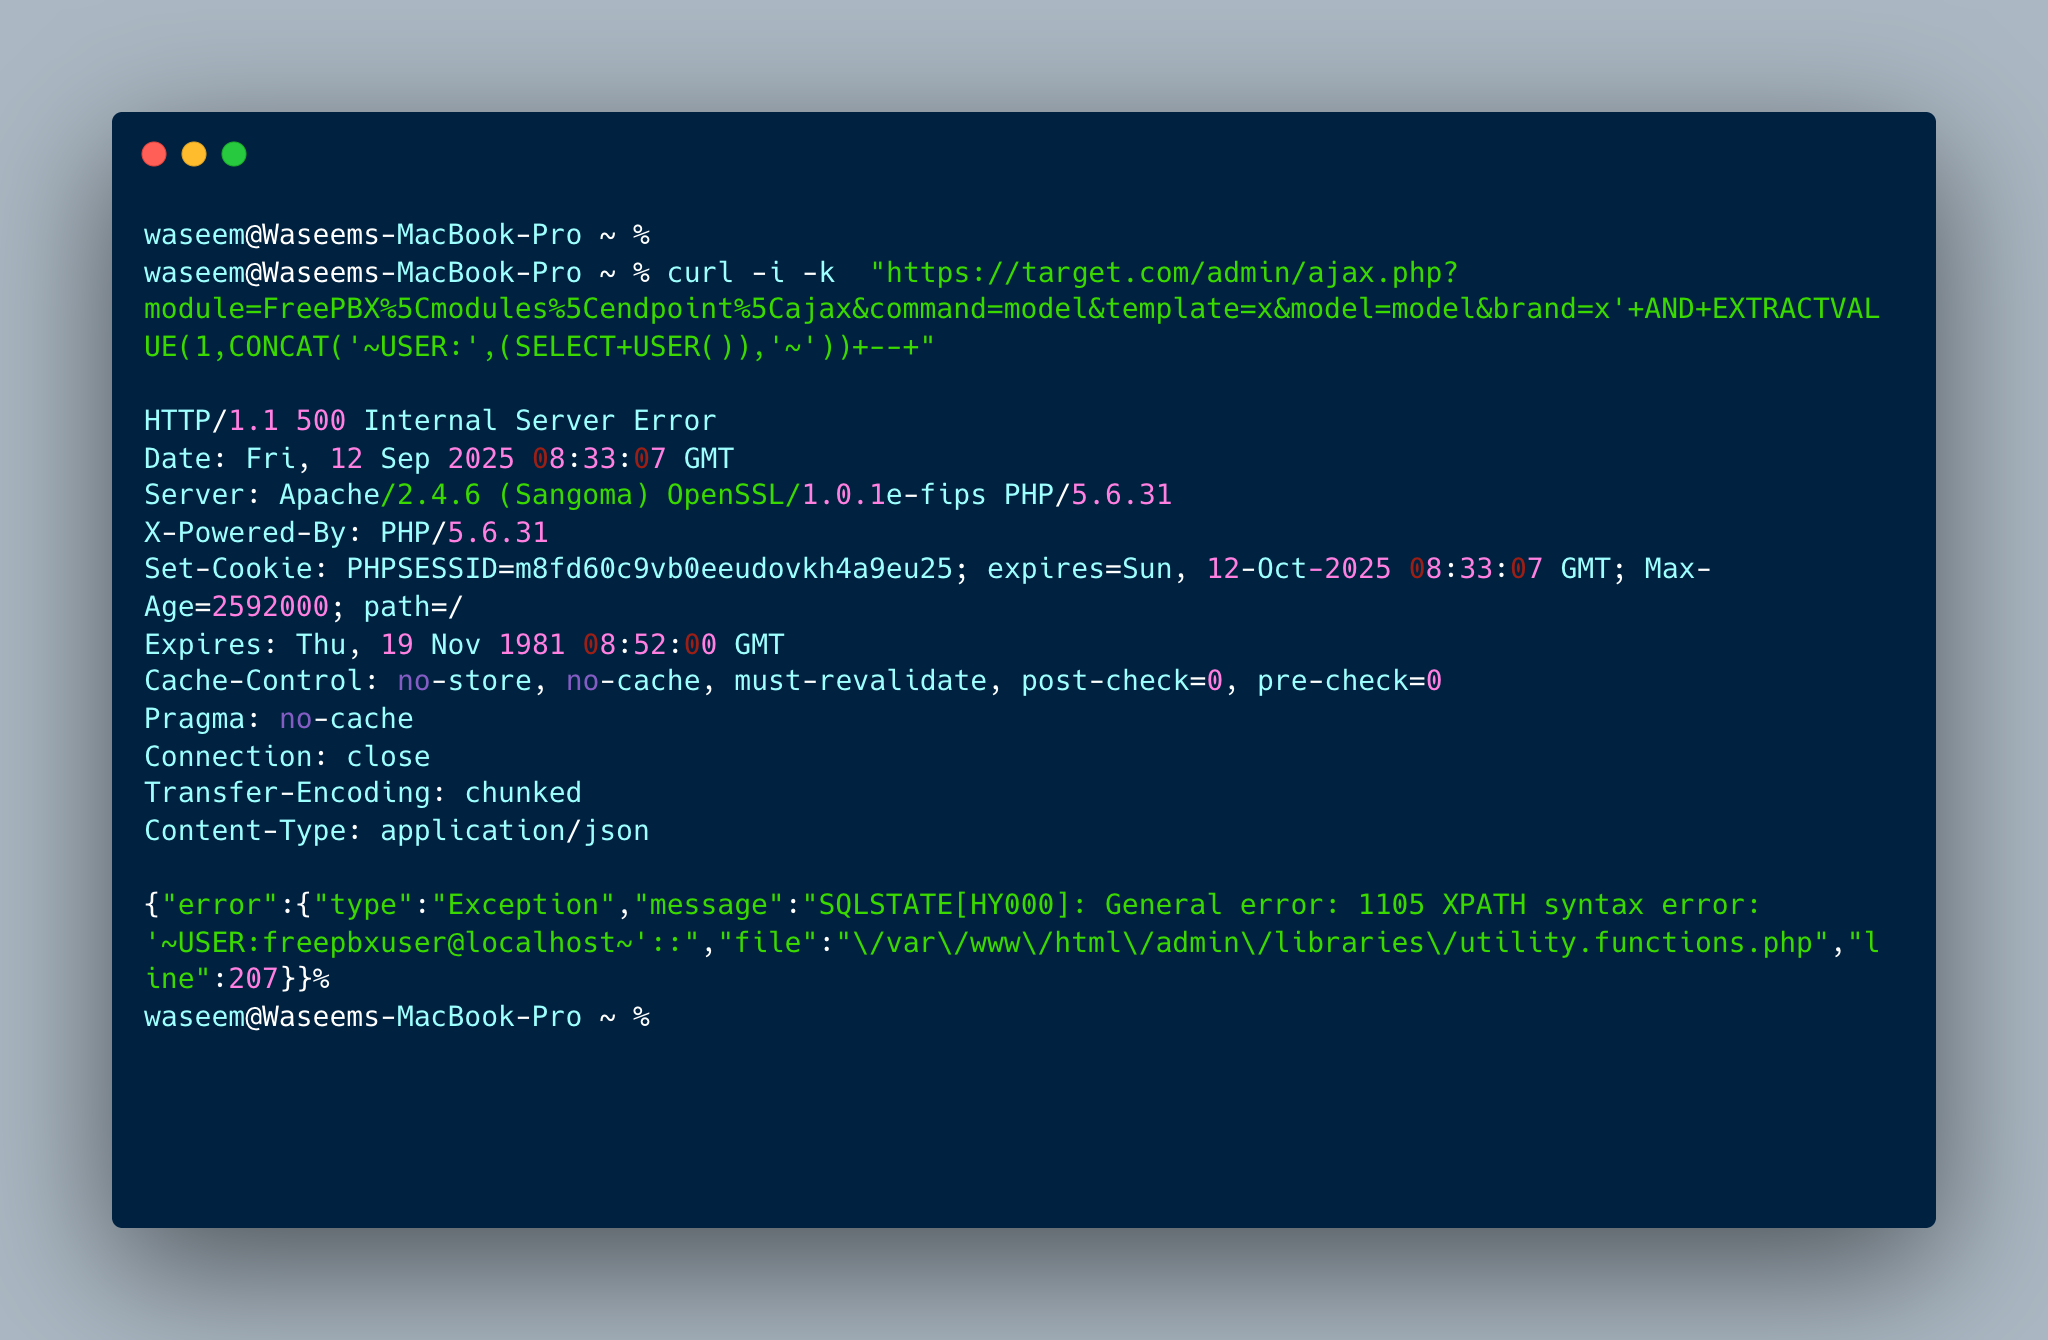 muhammadwaseem29/sql-injection-and-rce_cve-2025-57819
FreePBX versions 15, 16, and 17 contain a Remote Code Execution (RCE) vulnerability caused by insufficient sanitization of user-supplied data in…
 imbios/lab-cve-2016-15042
CVE-2016-15042 lab: Dockerized WordPress PoC for unauthenticated file upload in Frontend File Manager <4.0 and N‑Media Post Front‑end Form <1.1
 sabbu143s/cve_2020_35848
CVE-2020-35848 impacts Cockpit-CMS v1.7 due to unsafe handling of user inputs in authentication mechanisms, leading to remote code execution. This…