
Labtainers
 mfthomps/labtainers
Labtainers: A Docker-based cyber lab framework
binary-exploitationcryptographyctf+9
mfthomps/labtainersLabtainers: A Docker-based cyber lab framework
 hacktricks-wiki/hacktricks
Welcome to the page where you will find each trick/technique/whatever I have learnt in CTFs, real life apps, and reading researches and news.
 gchq/cyberchef
The Cyber Swiss Army Knife - a web app for encryption, encoding, compression and data analysis
 goshs-labs/goshs
Feature-rich single-binary file server for red teamers and developers. HTTP/S · WebDAV · FTP/SFTP · SMB · LDAP/S · NTLM hash capture · DNS/SMTP…

 mitsu-bis/security-portfolio
Security portfolio of original responsible-disclosure findings, CTF and lab write-ups, methodology notes, and purpose-built pentest tooling covering…
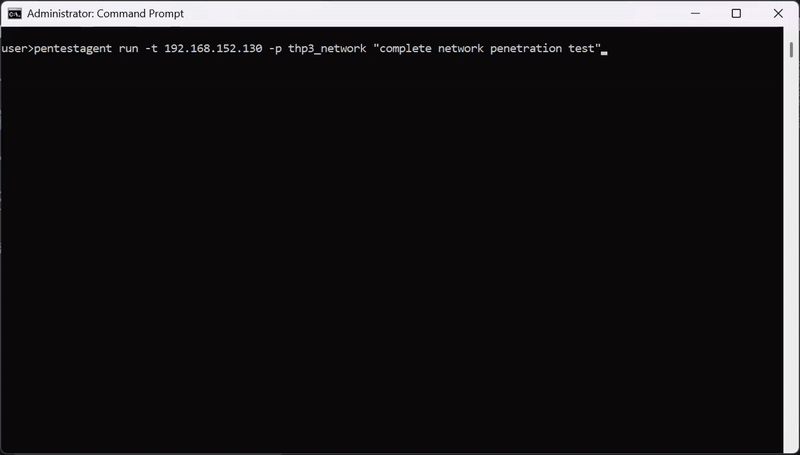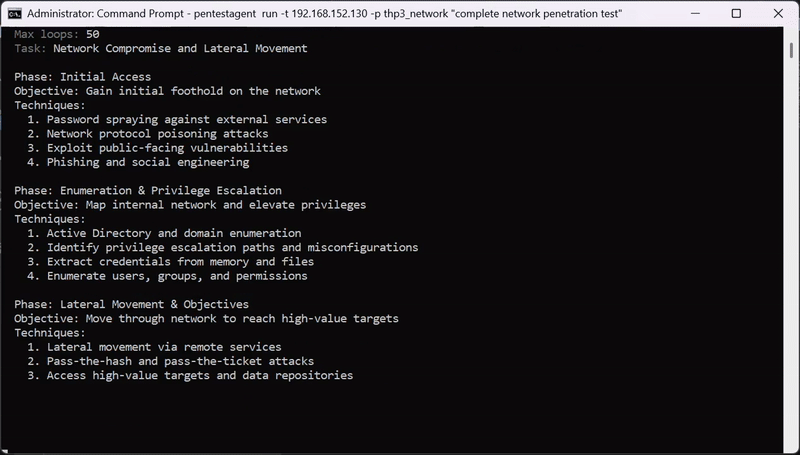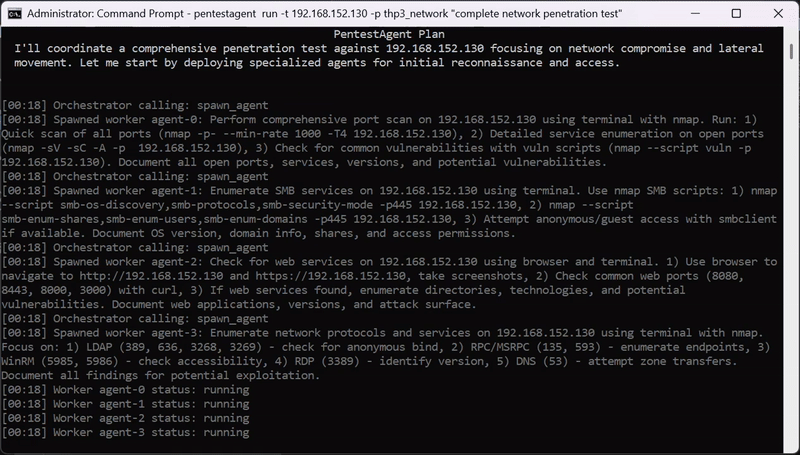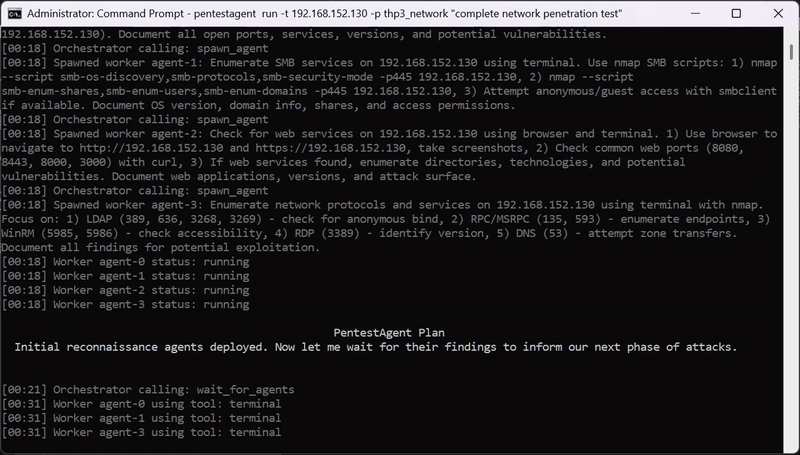 gh05tcrew/pentestagent
AI agent framework for black-box security testing with autonomous multi-agent orchestration, built-in pentesting tools, and MCP integration for bug…
 leaningtech/webvm
Client-side Linux virtual machine running in the browser via WebAssembly, with Tailscale networking, Dockerfile-based custom images, and CTF…
 bst04/cybersources
A curated list of cybersecurity tools and resources.
 dedsec1121fk/dedsec
Educational Android (Termux) toolkit for learning penetration testing, OSINT, social engineering, and network security through hands-on scripts,…
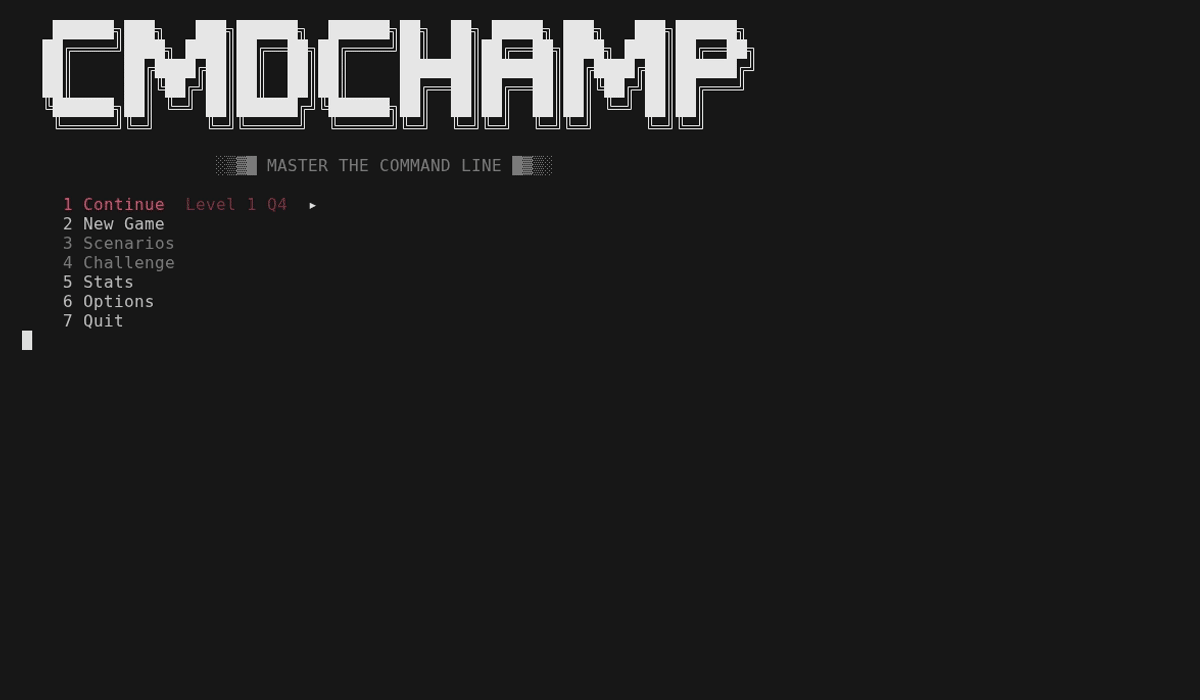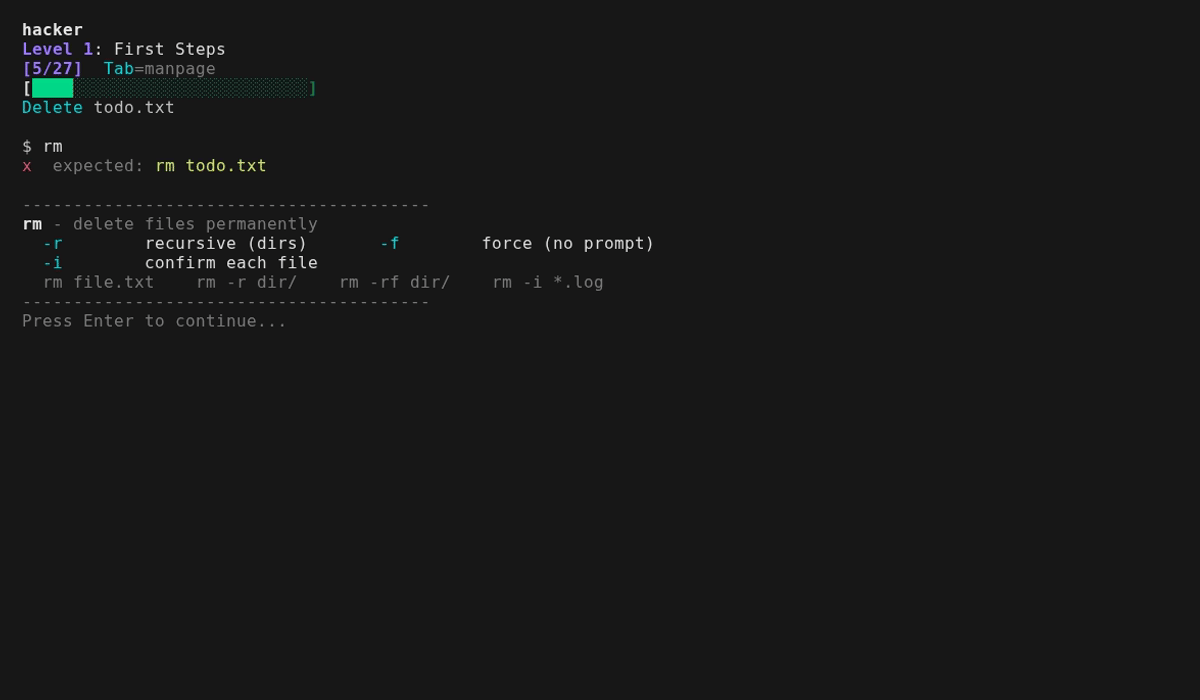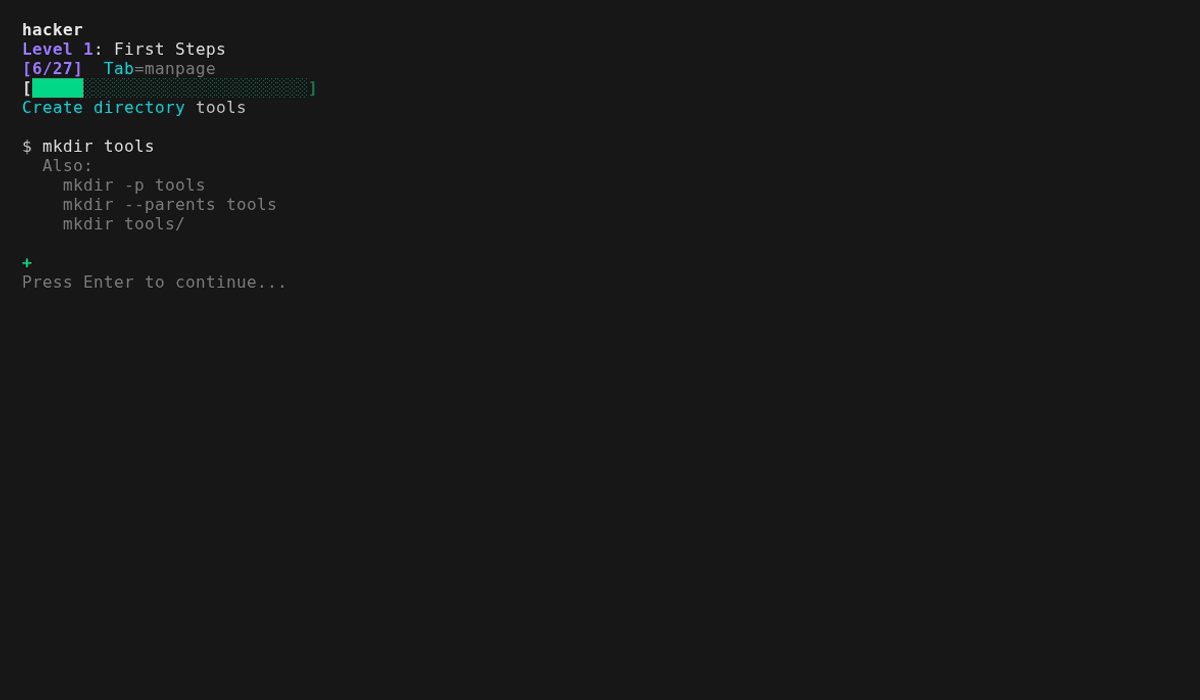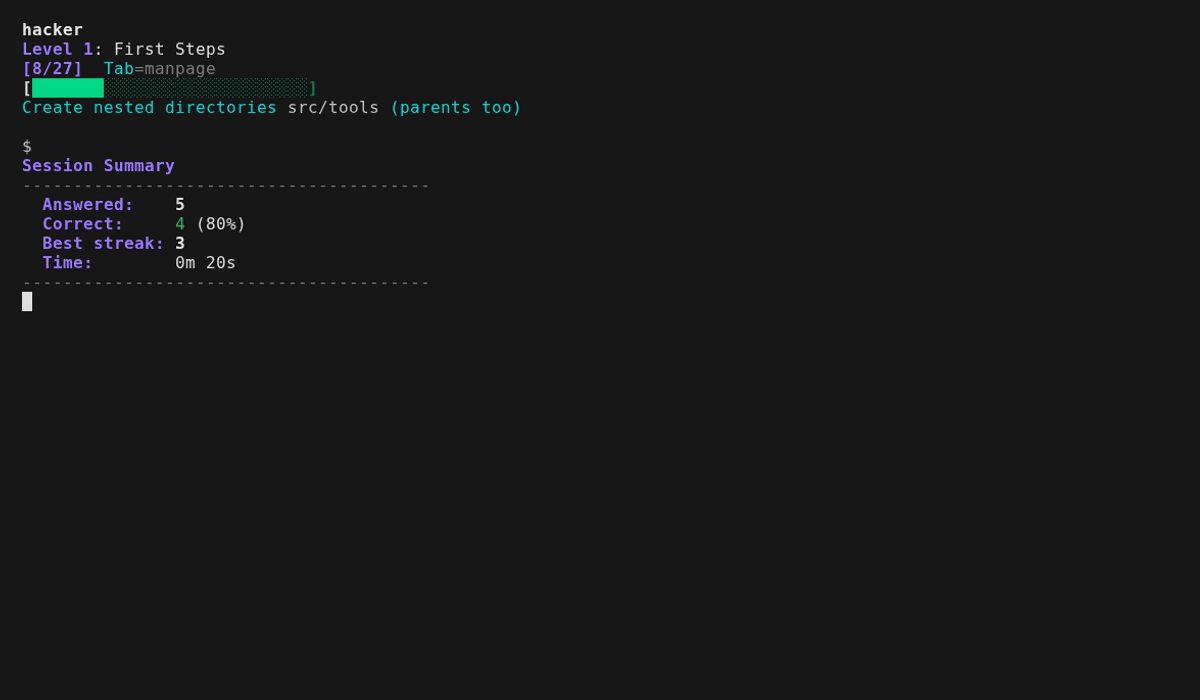 mellen9999/cmdchamp
bash CLI trainer — 30 levels from ls to privilege escalation
 m14r41/pentestingeverything
Complete Solution for VAPT/AppSec and Pentesting Guide: Web | Mobile | API | Thick Client | Source Code Review | DevSecOps | Wireless | Network…
 fankh/vulnerability-poc
CVE proof-of-concept labs, exploit scripts, and detection/prevention rules (Nginx, Apache, Snort, YARA) for high-severity CVEs. Authorized security…
 astrosp/awesome-osint-list
📡 Comprehensive collection of OSINT tools for cybersecurity professionals, researchers, and bug bounty hunters. Topics: information gathering,…
 cmpnn-romain/cve-2024-27198_lab
Lab for the CVE-2024-27198
 zales2004/sunset-noontide-pentesting
Description Professional penetration testing assessment of the Sunset: Noontide VulnHub machine, covering reconnaissance, service enumeration,…
 germarr93/cybersecurity-pentest-lab
CVE-2004-2687 (Distcc 3.2.1) exploitation, methodology & remediation — Metasploitable2 lab
 quincyomoruyi6-lang/blue-writeup-cve-2017-0144
Conducted a complete security assessment of an unpatched Windows 7 target ("Blue") to demonstrate the impact of legacy service vulnerabilities in an…