
CVE-2026-48908
 bayu06802/cve-2026-48908
Proof-of-concept exploit for CVE-2026-48908, an unauthenticated RCE in Joomla SP Page Builder via arbitrary file upload, with adaptive payload…
ctfeducationexploitation+4
bayu06802/cve-2026-48908Proof-of-concept exploit for CVE-2026-48908, an unauthenticated RCE in Joomla SP Page Builder via arbitrary file upload, with adaptive payload…
 r3fr4kt/popcorn-tjnull-oscp-
Popcorn HTB write-up covering advanced directory fuzzing, file upload bypass via magic numbers/extension spoofing using Burp Suite, and privilege…
 rootdirective-sec/cve-2026-5718-lab
Local Docker lab demonstrating CVE-2026-5718 arbitrary file upload in a WordPress plugin, with vulnerable and patched services for side-by-side…
 rootdirective-sec/cve-2026-3844-lab
Local Docker lab for reproducing CVE-2026-3844, an unauthenticated arbitrary file upload to RCE in the WordPress Breeze Cache plugin. Compares…
 speatx/chamilolms-cve-2023-4220
CVE-2023-4220 — Unauthenticated file upload RCE in Chamilo LMS ≤ 1.11.24. OSCP-style and auto exploit.
 echosecure/vuln-chain-lab
PoC Docker lab: chaining file upload bypass + stored XSS to create admin accounts. Educational resource for pen testers.
 mkirahmet/cve-2023-50164-htb-strutted
Proof-of-concept for CVE-2023-50164 (Apache Struts 2), originally by jakabakos and adapted for the HTB Strutted lab environment. For educational use…
 imbios/lab-cve-2016-15042
CVE-2016-15042 lab: Dockerized WordPress PoC for unauthenticated file upload in Frontend File Manager <4.0 and N‑Media Post Front‑end Form <1.1

 ldb33/cve-2023-24249-poc
Proof-of-concept exploit for CVE-2023-24249, an arbitrary file upload vulnerability in laravel-admin, enabling web shell deployment for penetration…
 pixel-defaultbr/cve-2023-50164
Educational exploit for CVE-2023-50164 (Apache Struts 2) demonstrating path traversal and remote code execution via malicious file upload, designed…
 lgenagul/cve-2023-4220-proof-of-concept
Chamilo LMS Unauthenticated Big Upload File that allows remote code execution
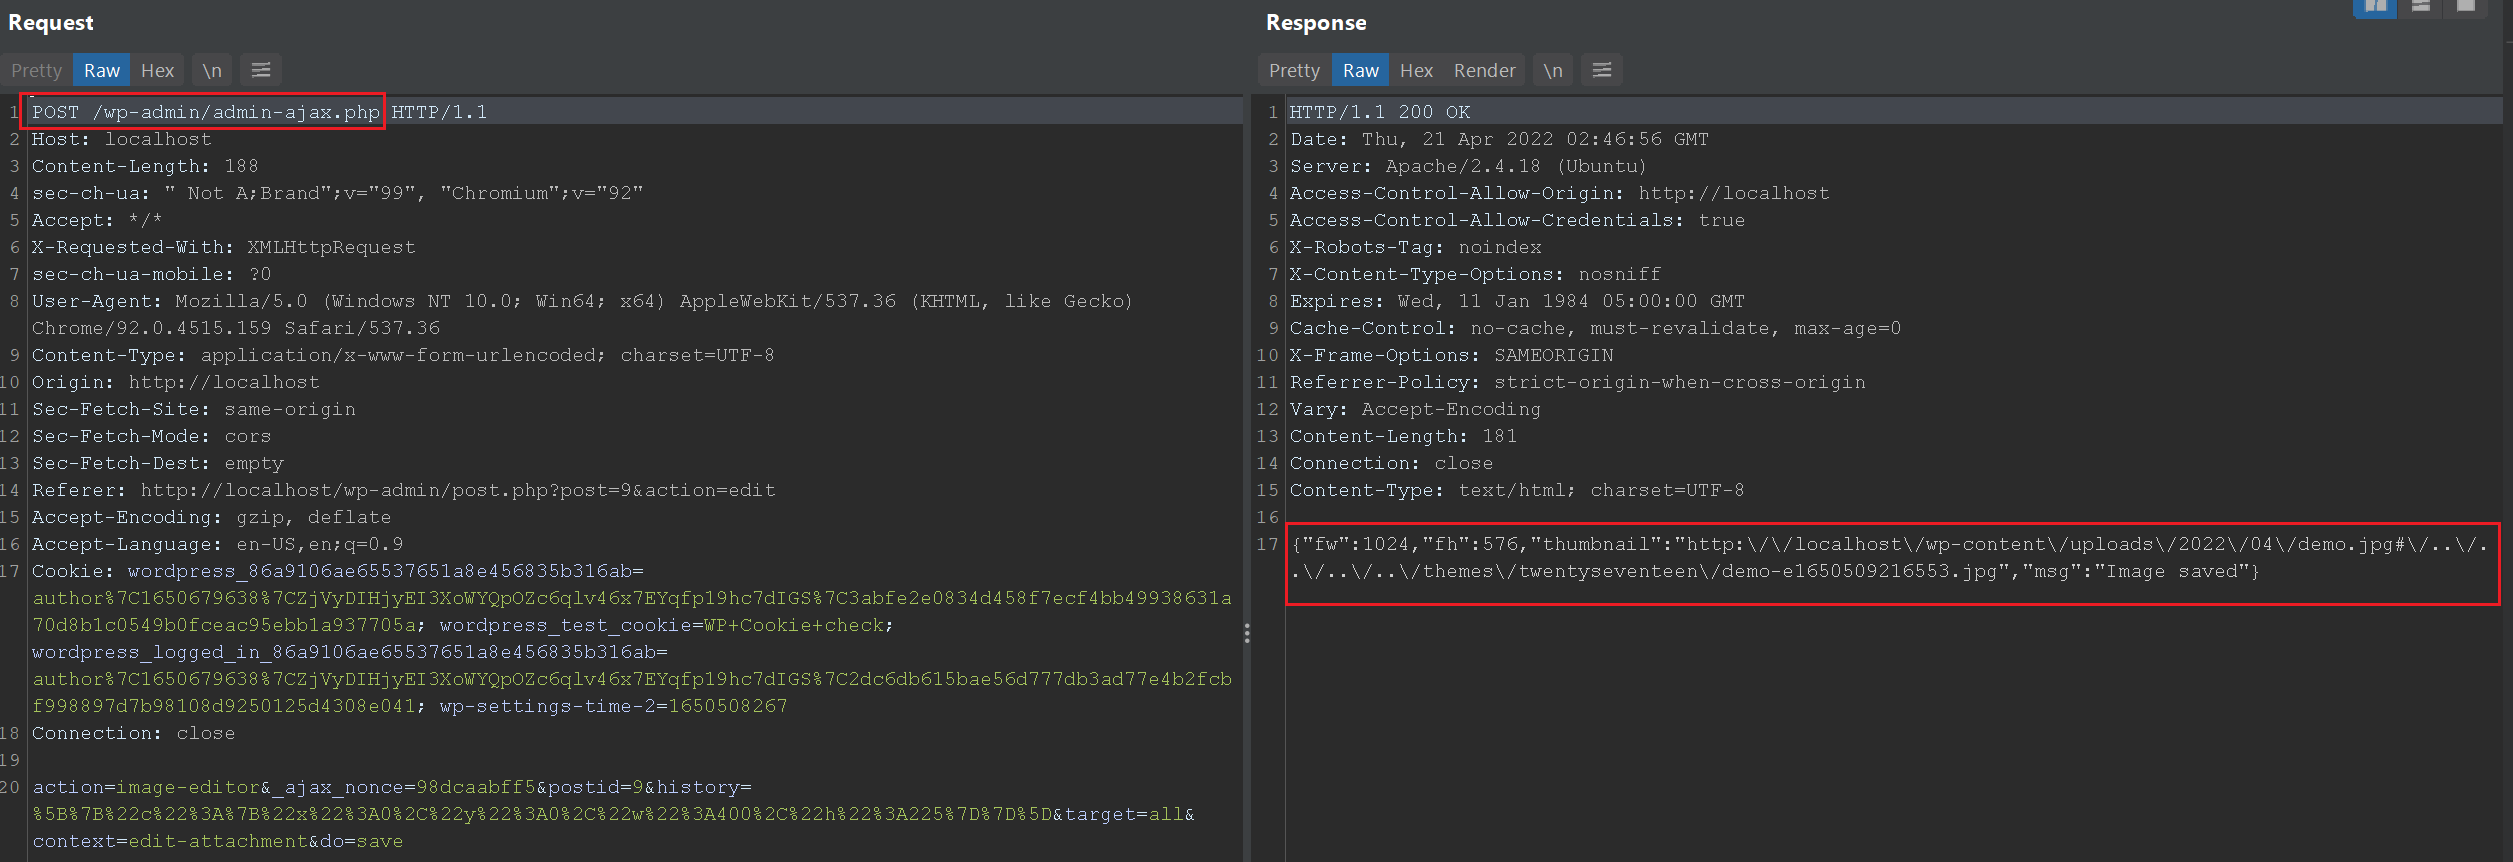 tuannq2299/cve-2019-8942
Detailed technical analysis and proof-of-concept exploit for WordPress RCE vulnerabilities CVE-2019-8942 and CVE-2019-8943, demonstrating LFI-to-RCE…
 tegal1337/0l4bs
Cross-site scripting labs for web application security enthusiasts