
screenpipe
 screenpipe/screenpipe
YC (S26) | Open Computer History | Record your screen continuously locally and provide context to your agents (Claude, Codex, Openclaw, Hermes,…
ctfcurated-resourceseducation+8
21.8k
screenpipe/screenpipeYC (S26) | Open Computer History | Record your screen continuously locally and provide context to your agents (Claude, Codex, Openclaw, Hermes,…

 alzeaty1/security-writeups
CTF writeups and teaching scripts for web security, bug bounty techniques, and network forensics, with blank-value versions for active practice.
 recurse-labs/recurse
Agentic reverse engineering IDE with a pure-Rust multi-architecture disassembler, native decompiler, debugger, and LLM agent for binary analysis and…
 dhotrey/awesome-cybersec
A collection of awesome platforms, blogs, documents, books, resources and cool stuff about security
 pduggusa/dugganusa-ietf
DugganUSA threat-intelligence contributions to the IETF Hackathon — real-world agentic-attack benchmark vectors, CVE-2026-33697 attestation analysis,…
 mobetasec/cve-2024-1813-poc
PoC exploit for CVE-2024-1813: PHP object injection in Simple Job Board WordPress plugin, achieving unauthenticated RCE via gadget chain. Includes…
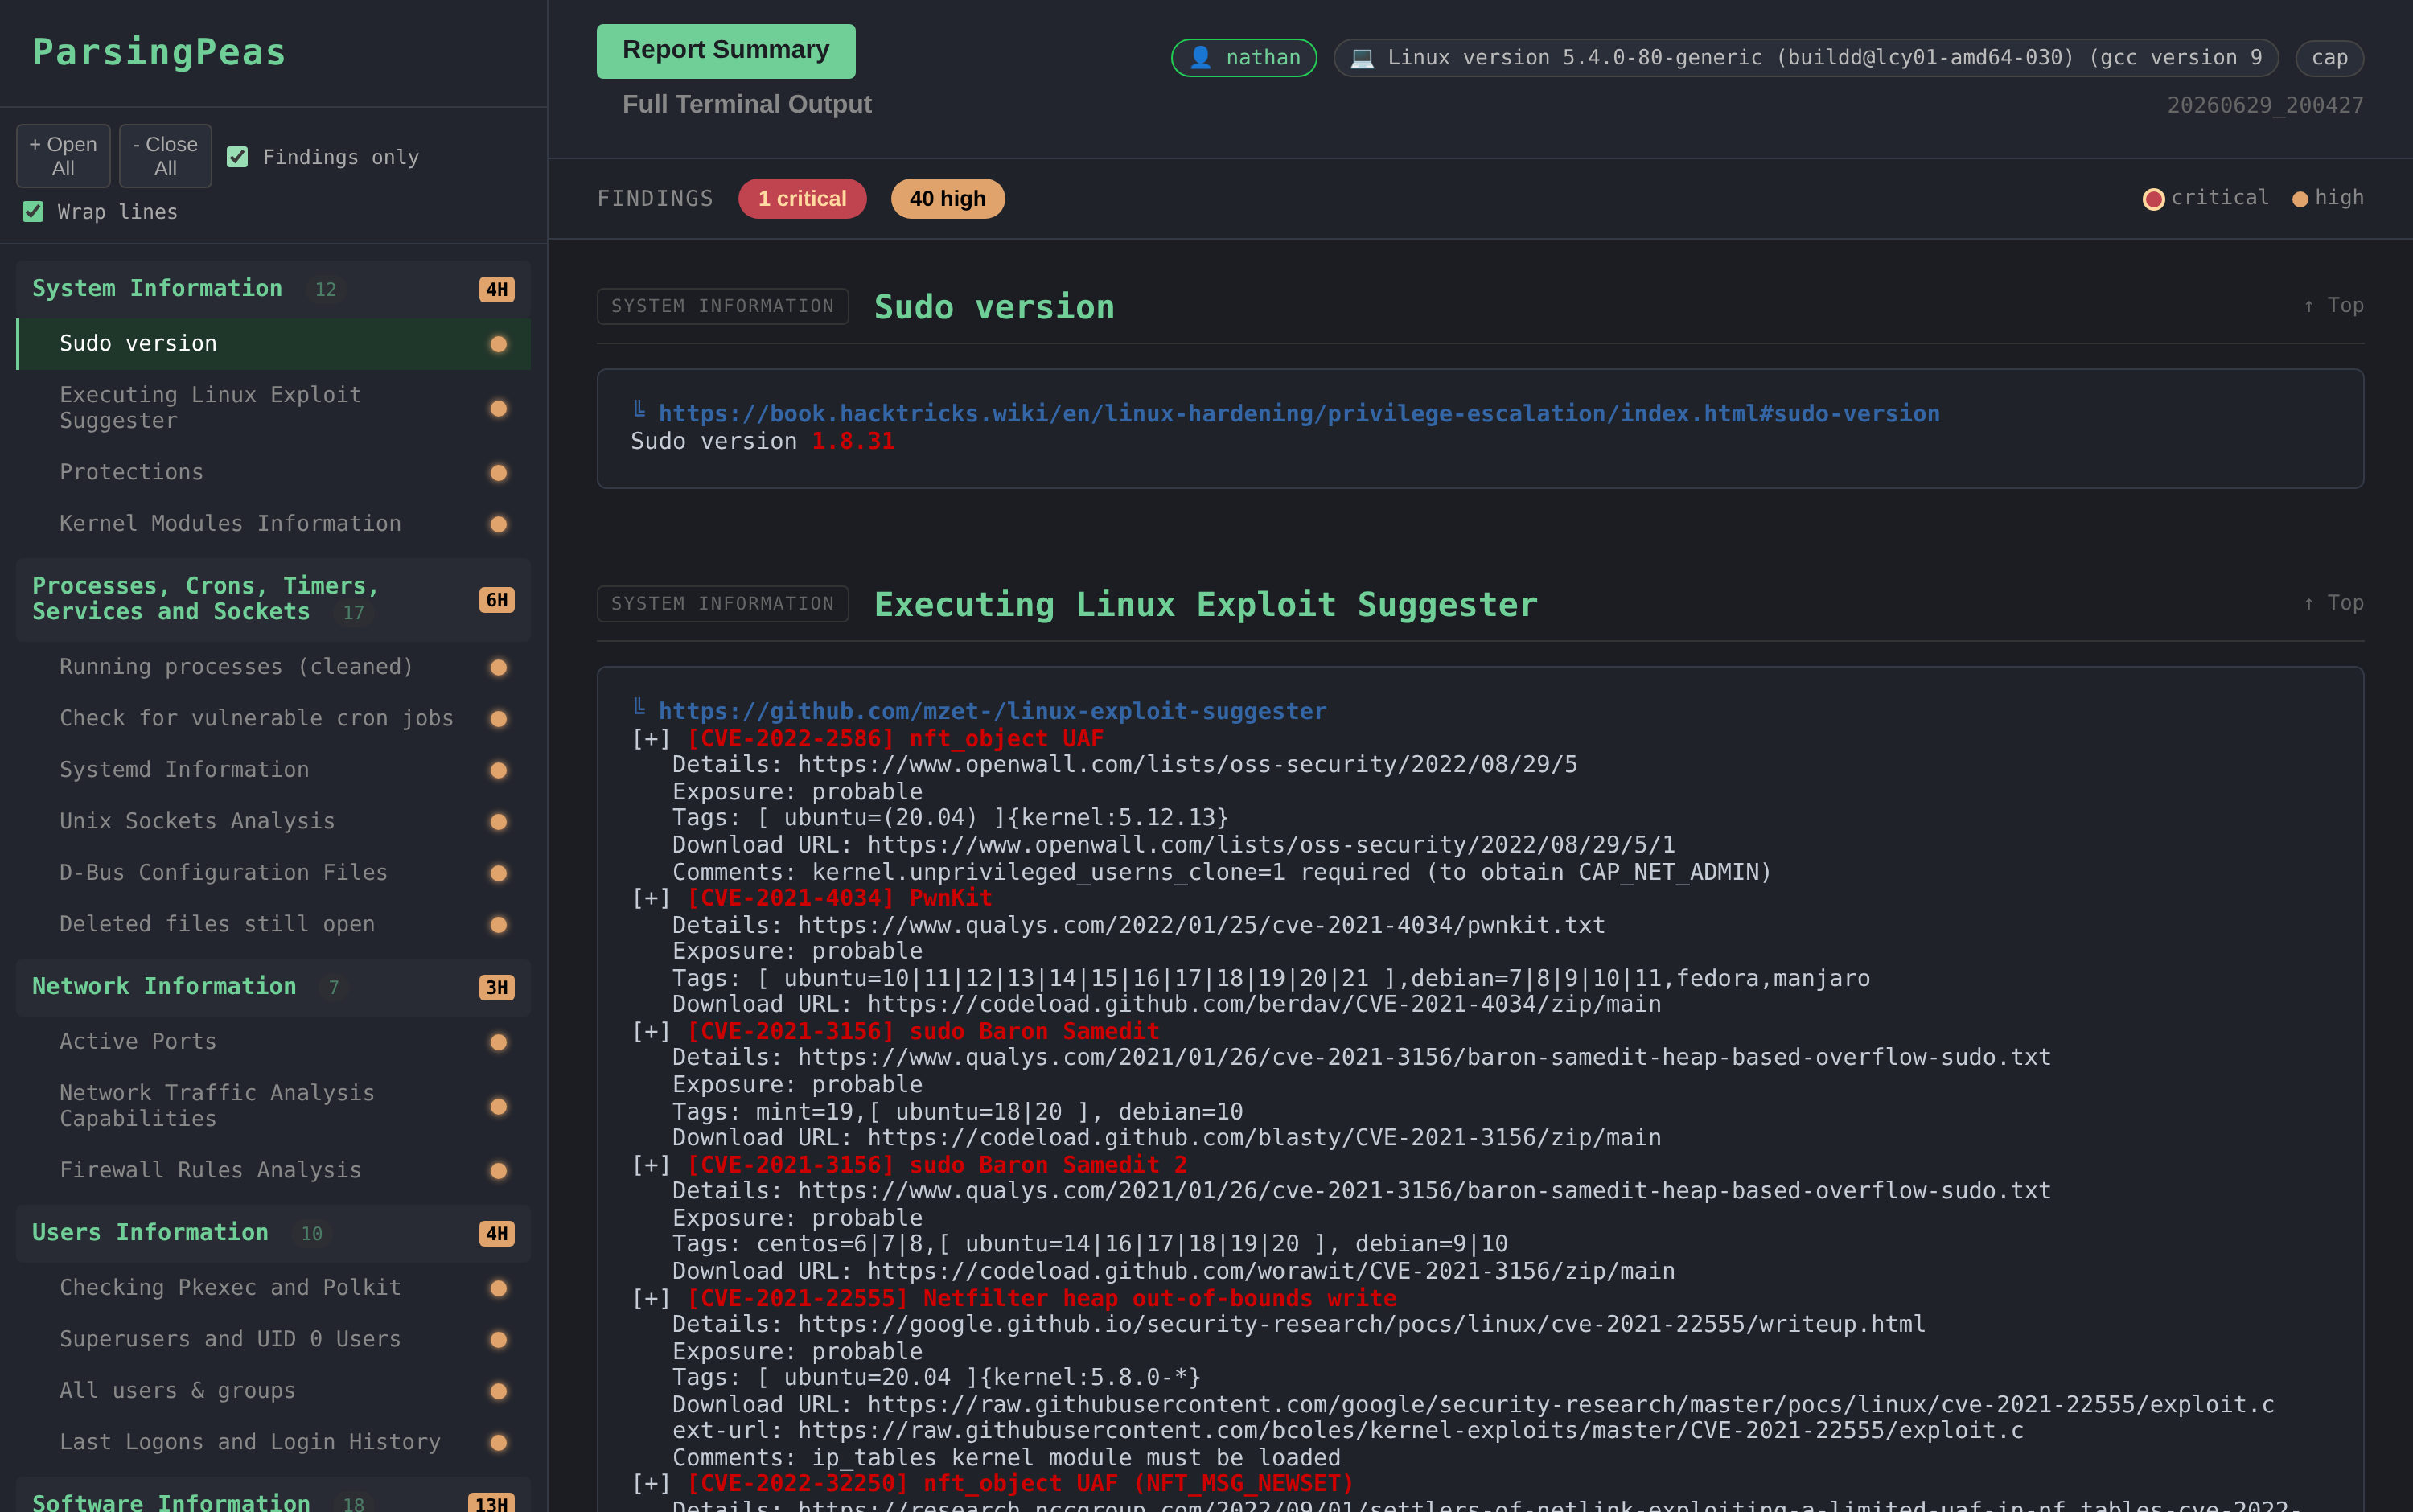 yuvalmil/parsingpeas
HTML parser for PEAS output with additional features
 ronin-rb/ronin
Ronin is a Free and Open Source Ruby Toolkit for Security Research and Development. Ronin also allows for the rapid development and distribution of…
 jvdsn/crypto-attacks
Python implementations of cryptographic attacks and utilities.
 z3yr0xx/cve-2025-64459
CTF challenge demonstrating Django ORM filter injection (CVE-2025-64459) with auth bypass and product filter bypass exploits, including deployment…
 mgueye3/log4shell
This repository contains my work for a cybersecurity assignment where I exploited the real-world Log4Shell (CVE-2021-44228) vulnerability inside a…
 dr4xp/pwnkit-helper
For CTF's and Safe Environments.... CVE-2021-4034 Local PrivEsc.
 imbios/lab-cve-2016-15042
CVE-2016-15042 lab: Dockerized WordPress PoC for unauthenticated file upload in Frontend File Manager <4.0 and N‑Media Post Front‑end Form <1.1
 sofianehamlaoui/pentest-bookmarkz
A collection of useful links for Pentesters
 owasp/owaspbugbounty
This is a container of web applications that work with OWASP Bug Bounty for Projects
 pouriam23/next.js-middleware-bypass-cve-2025-29927-
CTF challenge to learn and practice exploiting the Next.js middleware bypass vulnerability (CVE-2025-29927) by finding a flag in an admin page.
 pouriam23/vulnerability-in-remix-react-router-cve-2025-31137-
CTF challenge replicating CVE-2025-31137 in Remix/React Router Express. Learn to exploit a server-side vulnerability to find the admin flag.