
boha
 oritwoen/boha
Crypto bounties, puzzles and challenges data library
cryptographyctfcurated-resources+2
oritwoen/bohaCrypto bounties, puzzles and challenges data library
 hacktricks-wiki/hacktricks
Welcome to the page where you will find each trick/technique/whatever I have learnt in CTFs, real life apps, and reading researches and news.
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 tencent/ai-infra-guard
A full-stack AI Red Teaming platform securing AI ecosystems via Agent Scan, Skills Scan, MCP scan, AI Infra scan and LLM jailbreak evaluation.
 koadt/oss-oopssec-store
Security training for the apps you actually ship. Open your browser and start hacking.
 devploit/awesome-ctf-resources
A list of Capture The Flag (CTF) frameworks, libraries, resources and software for started/experienced CTF players 🚩
 owasp/wrongsecrets
Vulnerable app with examples showing how to not use secrets
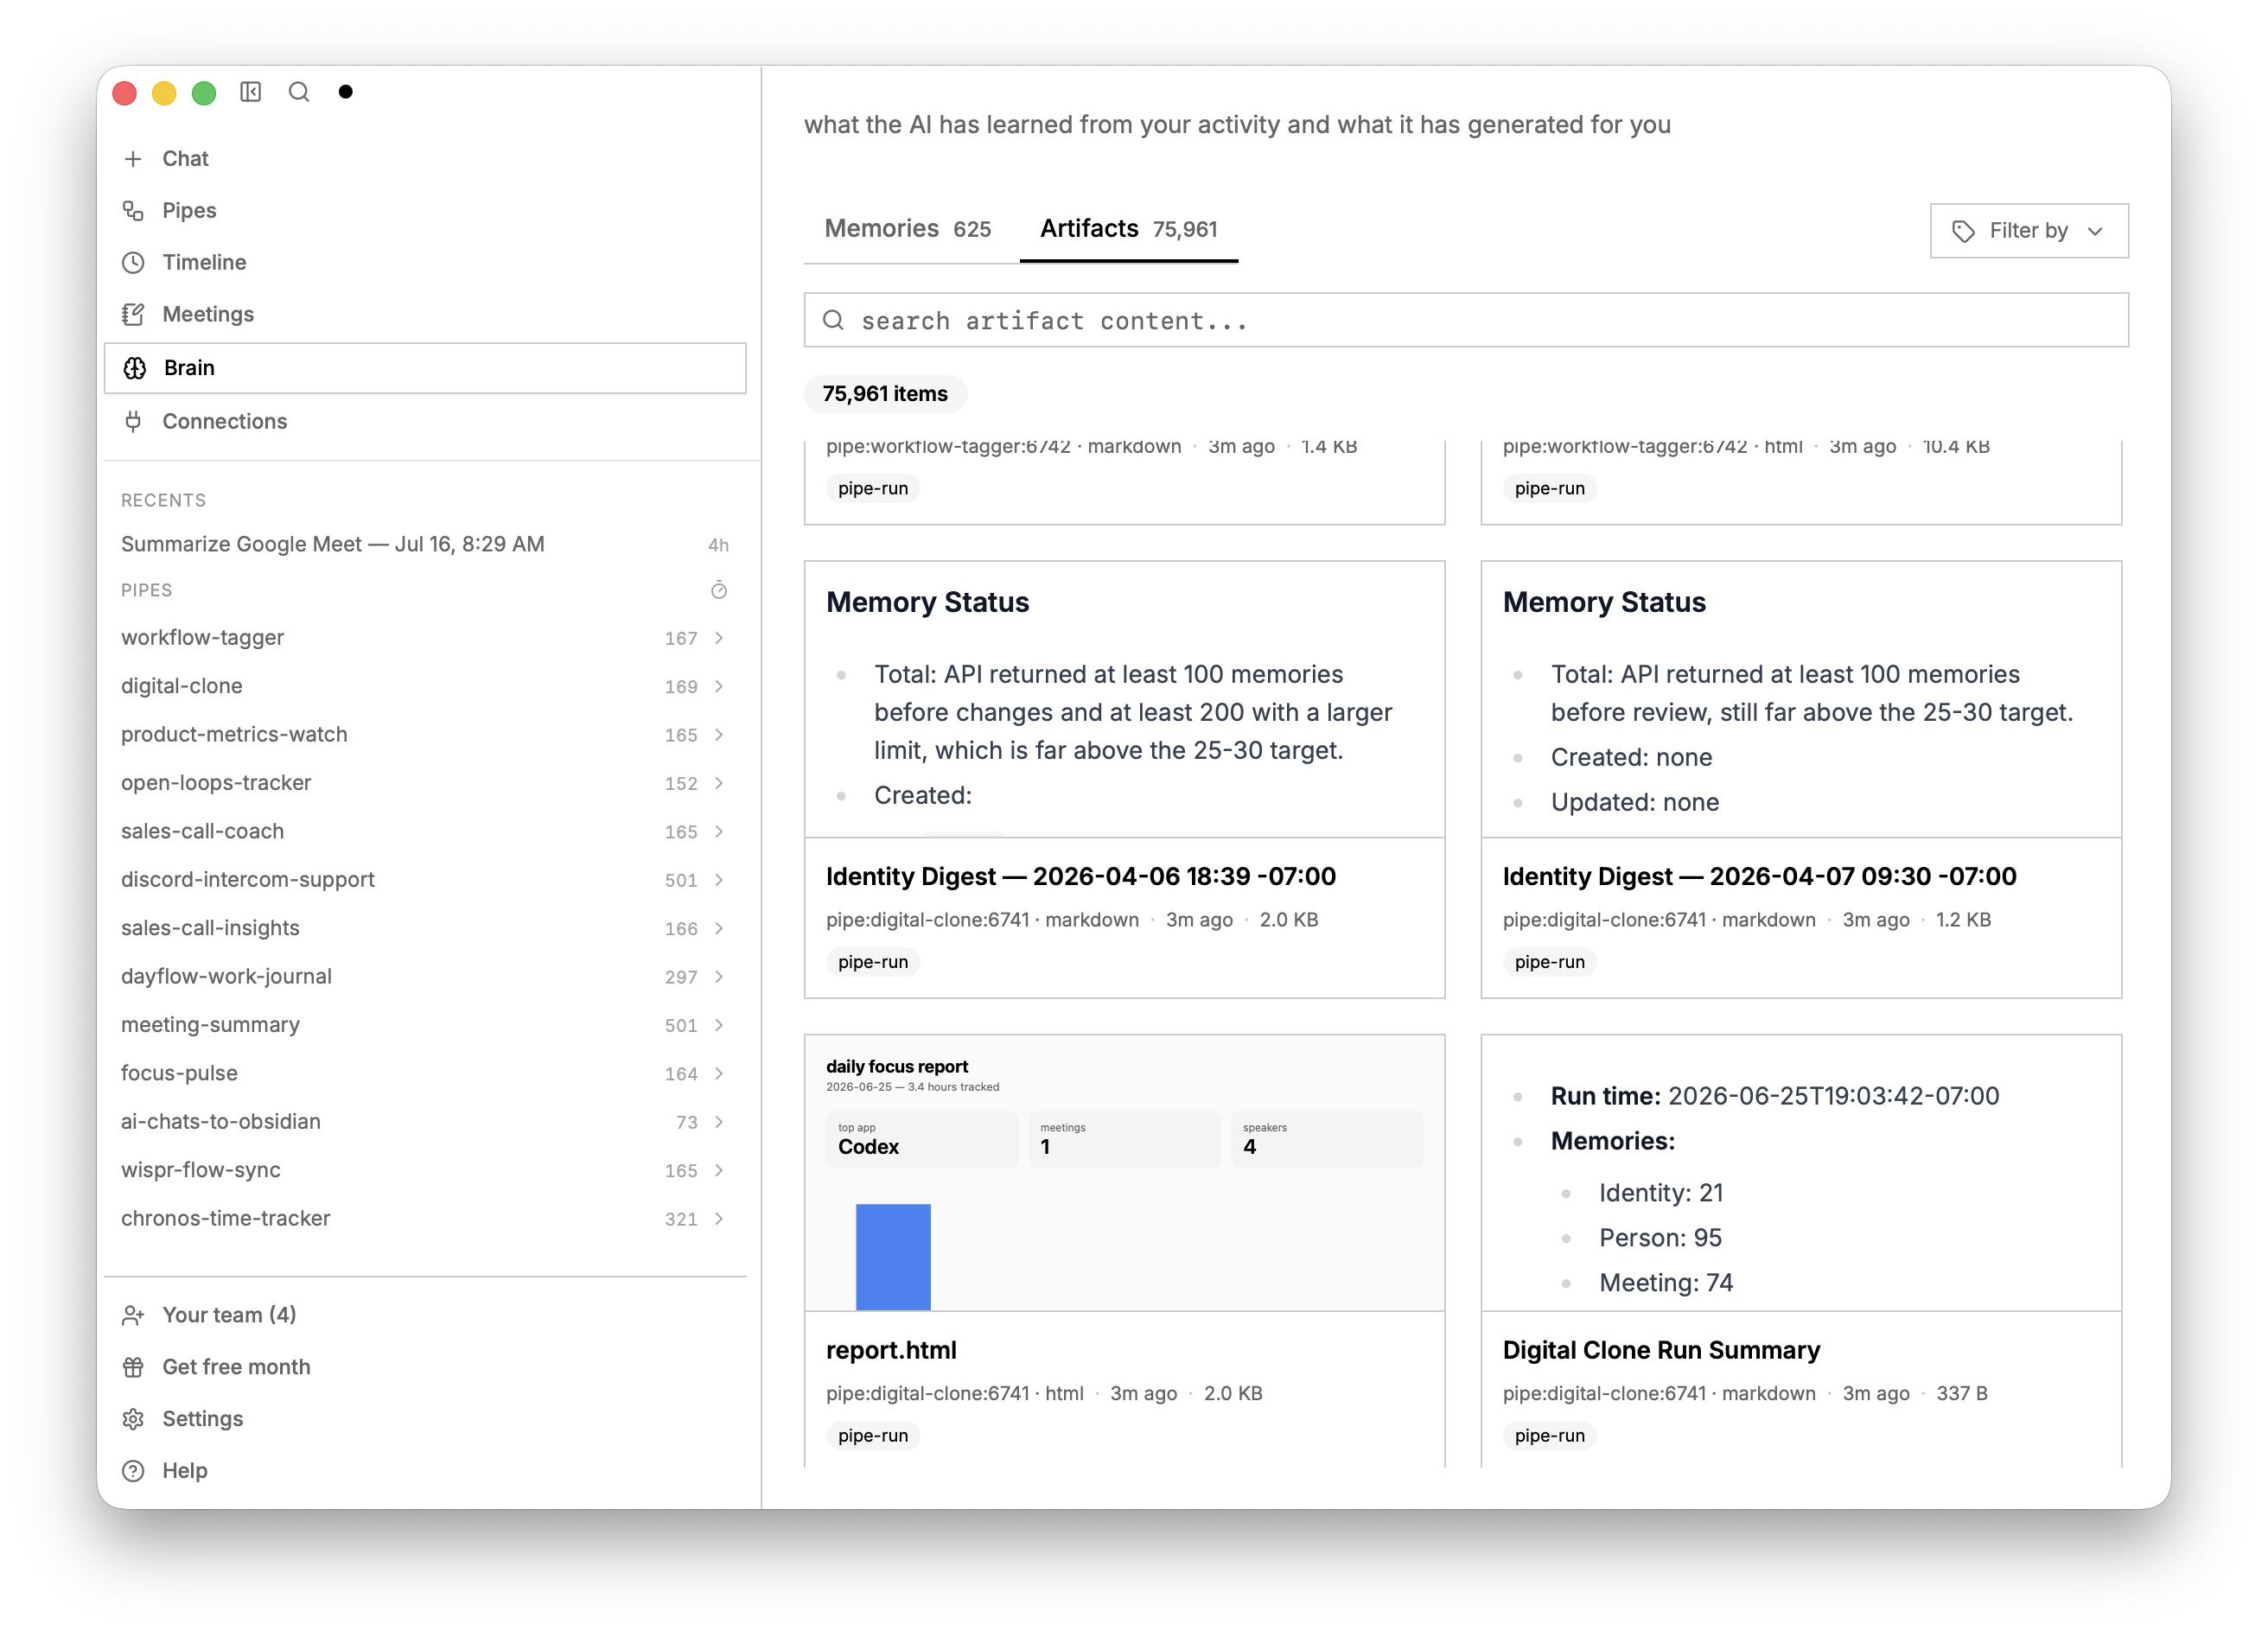 screenpipe/screenpipe
YC (S26) | Open Computer History | Record your screen continuously locally and provide context to your agents (Claude, Codex, Openclaw, Hermes,…
 frankwxu/digital-forensics-lab
Free hands-on digital forensics labs for students and faculty
 purpleailab/decepticon
Autonomous Hacking Agent for Red Team
 pnwcomputers/ultimate-cybersecurity-master-guide
This repository provides a centralized resource for operational cyber defense and offense, compiling Theory, Tools, Operating Procedures, and…
 portbuster1337/lpe-toolkit
Multi-architecture Linux privilege escalation toolkit with 29 pre-built and runtime-compilable exploits. Auto-detects kernel version, filters patched…
 1833ravikumar-max/cve-2021-41773-apache-path-traversal-lab
Docker-based cybersecurity lab for studying and reproducing CVE-2021-41773 in an isolated environment.
 abdelhakimgafernetworksec/enigm-writeup
Comprehensive penetration testing write-up and exploit details for Hack The Box - Enigma machine, covering local enumeration, OliveTin CVE-2026-27626…
 rsactftool/rsactftool
RSA attack tool (mainly for ctf) - retrieve private key from weak public key and/or uncipher data
 danielmiessler/seclists
Curated collection of wordlists for security assessments, including usernames, passwords, URLs, fuzzing payloads, and sensitive data patterns for…