

php2shell-lab
 tani2shell/php2shell-lab
Black-box pentest lab for the PHP2Shell engine memory-corruption family (CVE-2026-109618 / CVE-2026-109619, CVSS 9.8/9.2). Dual-flag verified attack…
binary-exploitationcontainer-securityctf+7
4
tani2shell/php2shell-labBlack-box pentest lab for the PHP2Shell engine memory-corruption family (CVE-2026-109618 / CVE-2026-109619, CVSS 9.8/9.2). Dual-flag verified attack…
 taniungou/php2shell-lab
Black-box pentest lab for the PHP2Shell engine memory-corruption family (CVE-2026-109618 / CVE-2026-109619, CVSS 9.8/9.2). Dual-flag verified attack…
 hackerking24/cve-2026-29782-openstamanager-rce
Proof-of-concept exploit for CVE-2026-29782, chaining SQL injection and PHP object injection to achieve remote code execution in OpenSTAManager.…
 khwajasaad267-coder/cve-2024-4577-lab
Docker-based CTF lab demonstrating CVE-2024-4577 PHP-CGI argument injection leading to RCE. Includes vulnerable PHP 5.4.1 CGI, exploit scripts, and…
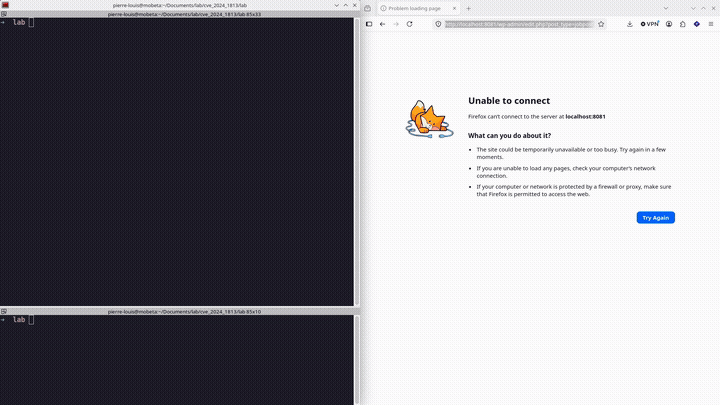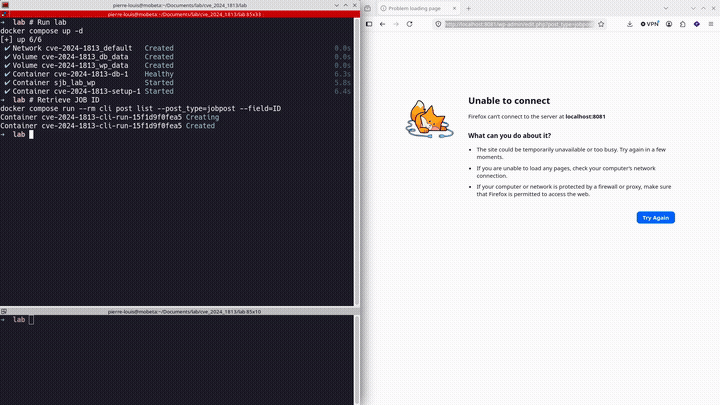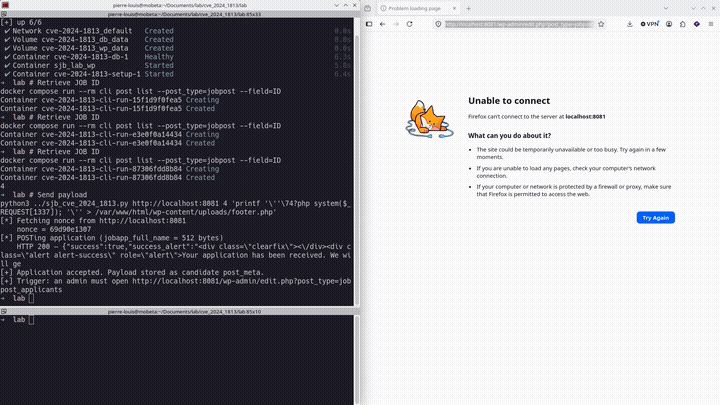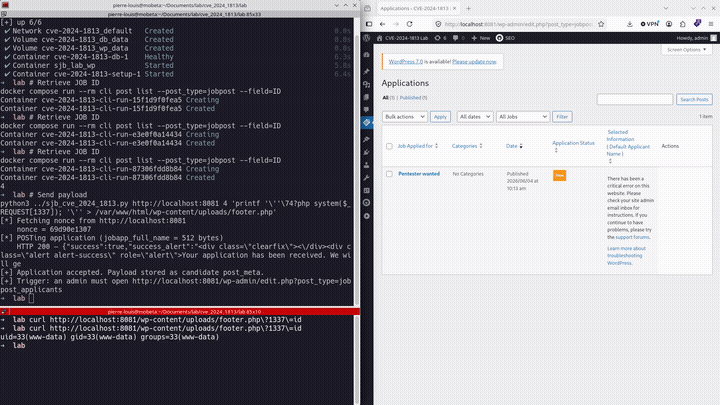 mobetasec/cve-2024-1813-poc
PoC exploit for CVE-2024-1813: PHP object injection in Simple Job Board WordPress plugin, achieving unauthenticated RCE via gadget chain. Includes…
 ayham-megdadi/zero-day-legacy
A vulnerable Boot-to-Root CTF lab machine simulating a hospital environment. Features a realistic 17-step attack chain including SQL Injection, XSS,…
 xmyronn/cve-2026-11518-xss
Proof-of-concept for unauthenticated stored XSS in SourceCodester Inventory System, demonstrating admin session hijacking via crafted registration…
 rcribelar-nucleus/my-cool-demo-php-code
PHP RCE CVE-2024-2961 Nucleus Hackathon Demo
 jwsly12/cve-2025-66034-htb-ctf
Exploit for VariaType HTB machine leveraging XML injection in fontTools to achieve RCE via PHP reverse shell payload in .designspace metadata.
 ahmedf000/cve-2025-49132_htb_season10
Unauthenticated RCE exploit for CVE-2025-49132 in Pterodactyl Panel via path traversal, PEAR command injection, and PHP code execution. Includes HTB…
 19melek19/themisfits-cve-2024-8465-sqli
Intentionally vulnerable PHP web app demonstrating SQL injection authentication bypass and unauthorized data disclosure modeled after CVE-2024-8465…
 a1ex-var1amov/ctf-cve-2019-11043
Intentionally vulnerable PHP app with Nginx/PHP-FPM setup for reproducing CVE-2019-11043, including Docker and Kubernetes deployment,…
 a1ex-var1amov/ctf-cve-2024-4577
CTF challenge demonstrating CVE-2024-4577 PHP CGI argument injection, with vulnerable app, attack scripts, and Kubernetes/Docker deployment for…
 5kr1pt/roundcube_cve-2025-49113
Explicação + Lab no THM
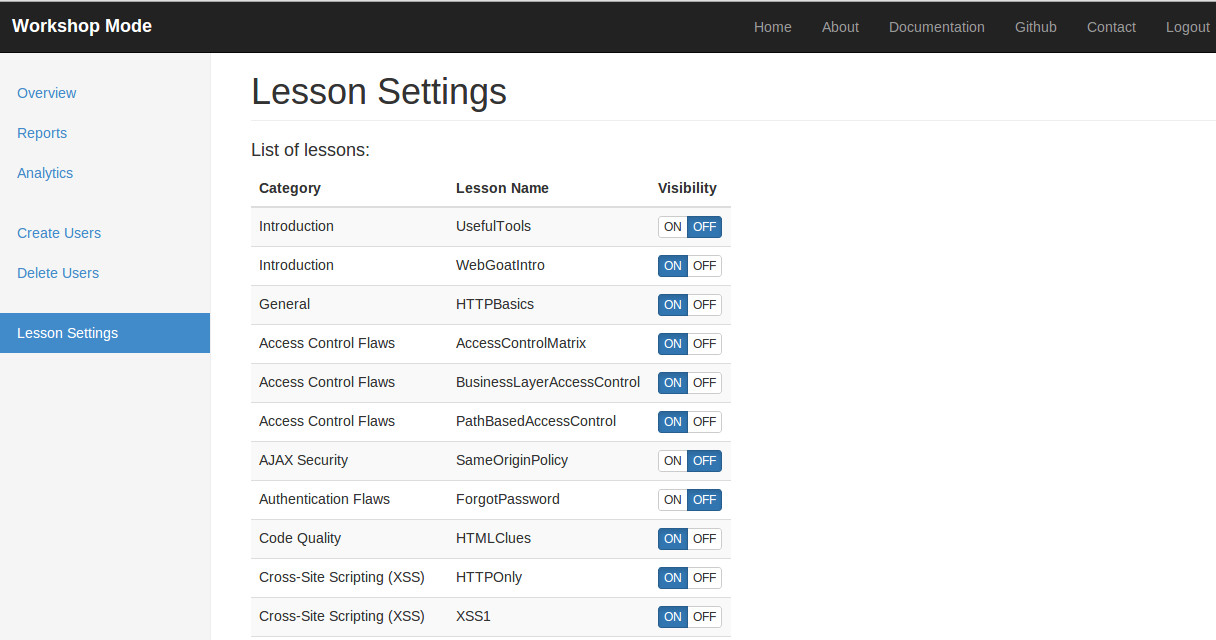 owasp/owaspwebgoatphp
A deliberately vulnerable web application for learning web application security.
 1h3ll/cve-2025-50365_csrf_delete_category-phpgurukul-cve
PoC for CVE-2025-50365: a CSRF flaw in PHPGurukul Maid Hiring Management System allowing deletion of hiring categories via a crafted admin request.
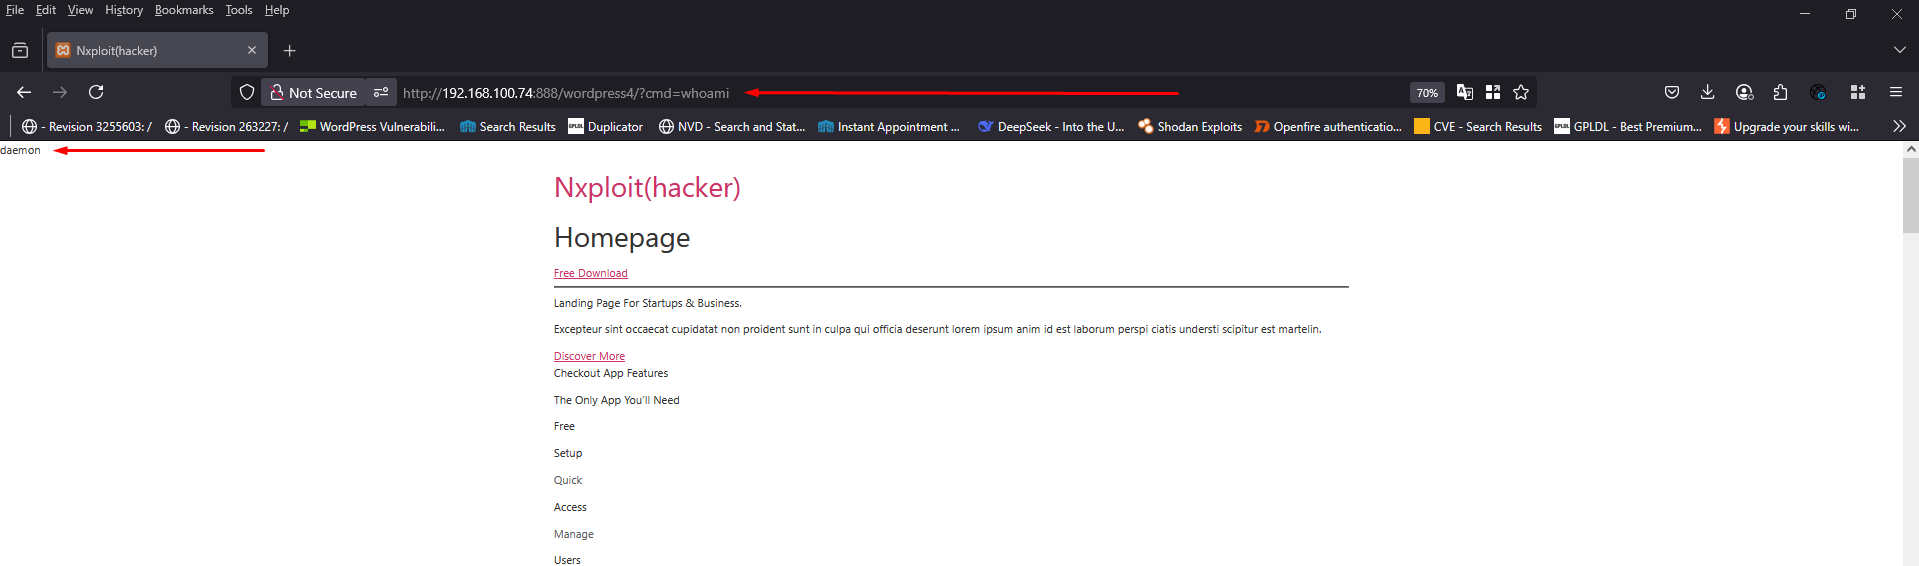 nxploited/cve-2025-39601
WordPress Custom CSS, JS & PHP plugin <= 2.4.1 - CSRF to RCE vulnerability
 ahmedmansour93/event-id-268-rule-name-soc292-possible-php-injection-detected-cve-2024-4577-
🚨 New Incident Report Completed! 🚨 Just wrapped up "Event ID 268: SOC292 - Possible PHP Injection Detected (CVE-2024-4577)" on LetsDefend.io. This…