

secdim-assurance-drift-challenge
 franklincg/secdim-assurance-drift-challenge
SecDim Challenge Builder repro inspired by CVE-2026-88861: AAL1 MFA bypass at privileged credential boundary
api-securityauthentication-authorizationctf+5
franklincg/secdim-assurance-drift-challengeSecDim Challenge Builder repro inspired by CVE-2026-88861: AAL1 MFA bypass at privileged credential boundary
 alardiians/gitea-cve-2026-28699
Lab + writeup for CVE-2026-28699: Gitea OAuth2 scope enforcement bypass via HTTP Basic auth
 vanhari/cve-2026-39987
Proof-of-concept exploit for an authentication bypass in marimo's terminal WebSocket endpoint, enabling unauthenticated command execution in versions…
 kaleth4/cve-2026-20896
Automated PoC exploit for CVE-2026-20896, a Gitea authentication bypass via directory traversal in the API authorization header, enabling…
 hunt-benito/ash-authentication-oauth2-oidc-account-takeover-cve-2026-49757-email-based-user-matching
Proof-of-concept exploit for CVE-2026-49757 demonstrating OAuth2/OIDC account takeover via email-based user matching in AshAuthentication, with…
 ez4rd1x1/cve-2026-8181
Proof-of-concept exploit for CVE-2026-8181, an authentication bypass in the Burst Statistics WordPress plugin. Demonstrates remote, unauthenticated…
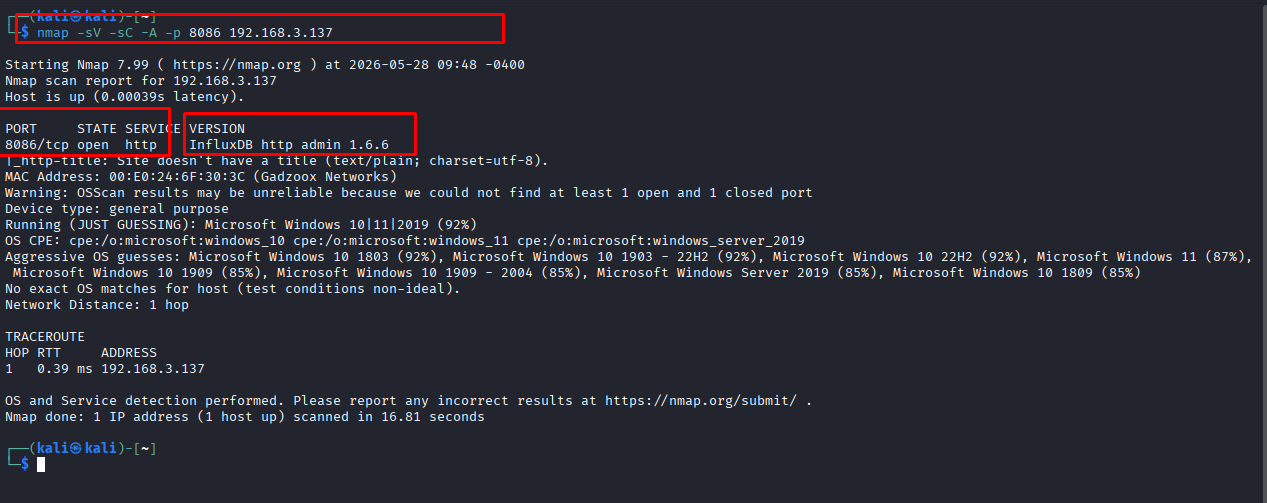 dungsocool/cve-2019-20933
Step-by-step lab writeup demonstrating CVE-2019-20933 InfluxDB authentication bypass via forged JWT tokens, including exploitation,…
 trivulzianus/tarantubench
The full repo of all the labs available as part of the benchmark
 bishopfox/otto-support
An implementation of a vulnerable MCP server using mcp-go
 toddkk02/cve-2025-29927
Proof-of-concept exploit for CVE-2025-29927, demonstrating authentication bypass in Next.js middleware via the x-middleware-subrequest header, with…
 0xdtc/crushftp-auth-bypass-cve-2025-31161
Exploit for CrushFTP CVE-2025-31161 auth bypass: detects vulnerable targets, enumerates users, and creates unauthorized admin accounts through…
 yafiah-darwesh/cs50-cyber-paloalto-oauth
CS50 Cybersecurity final project — Palo Alto OAuth token breach (CVE-2024-3400)
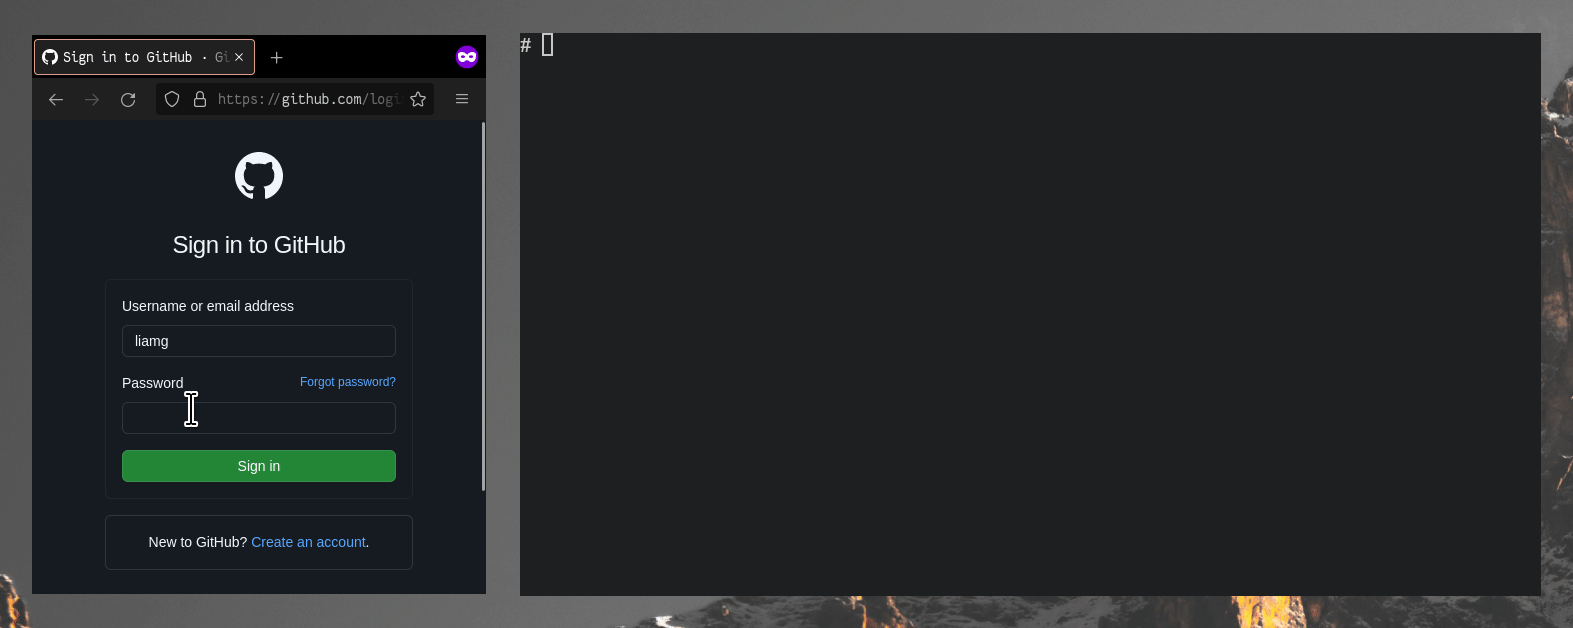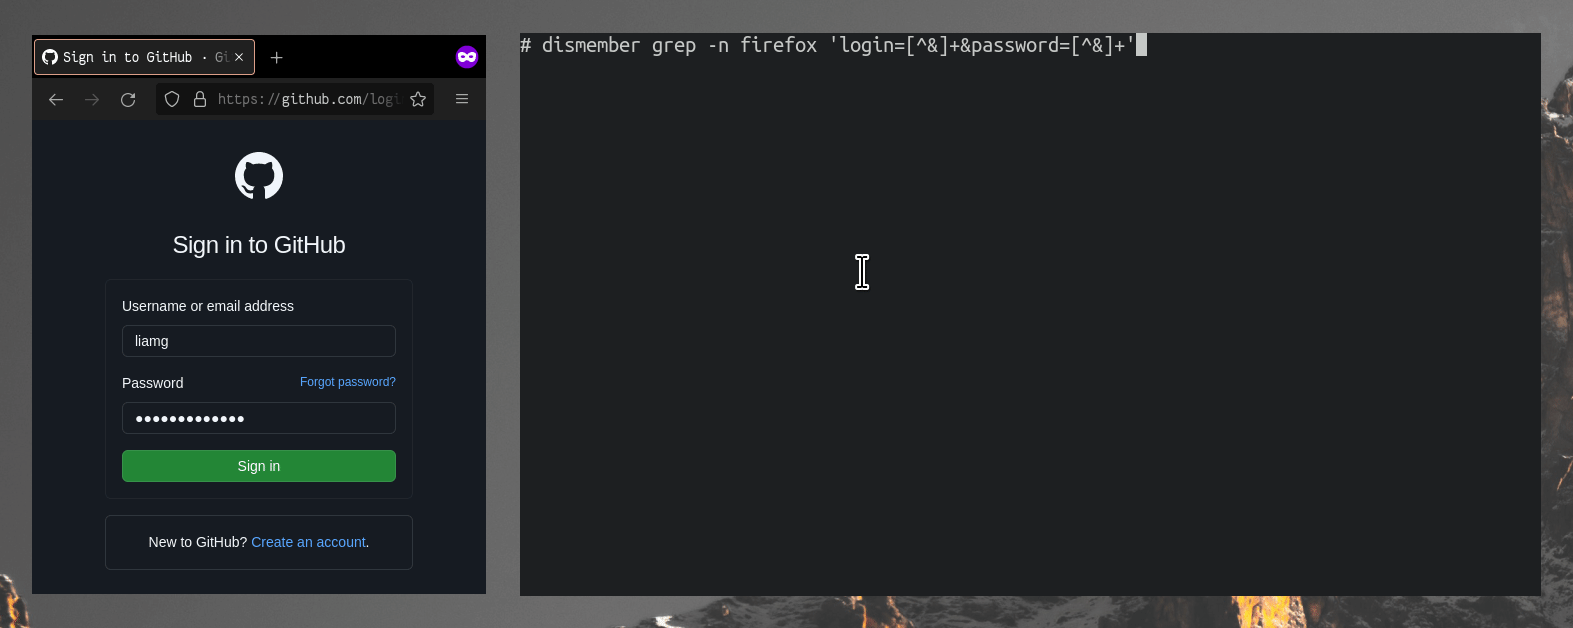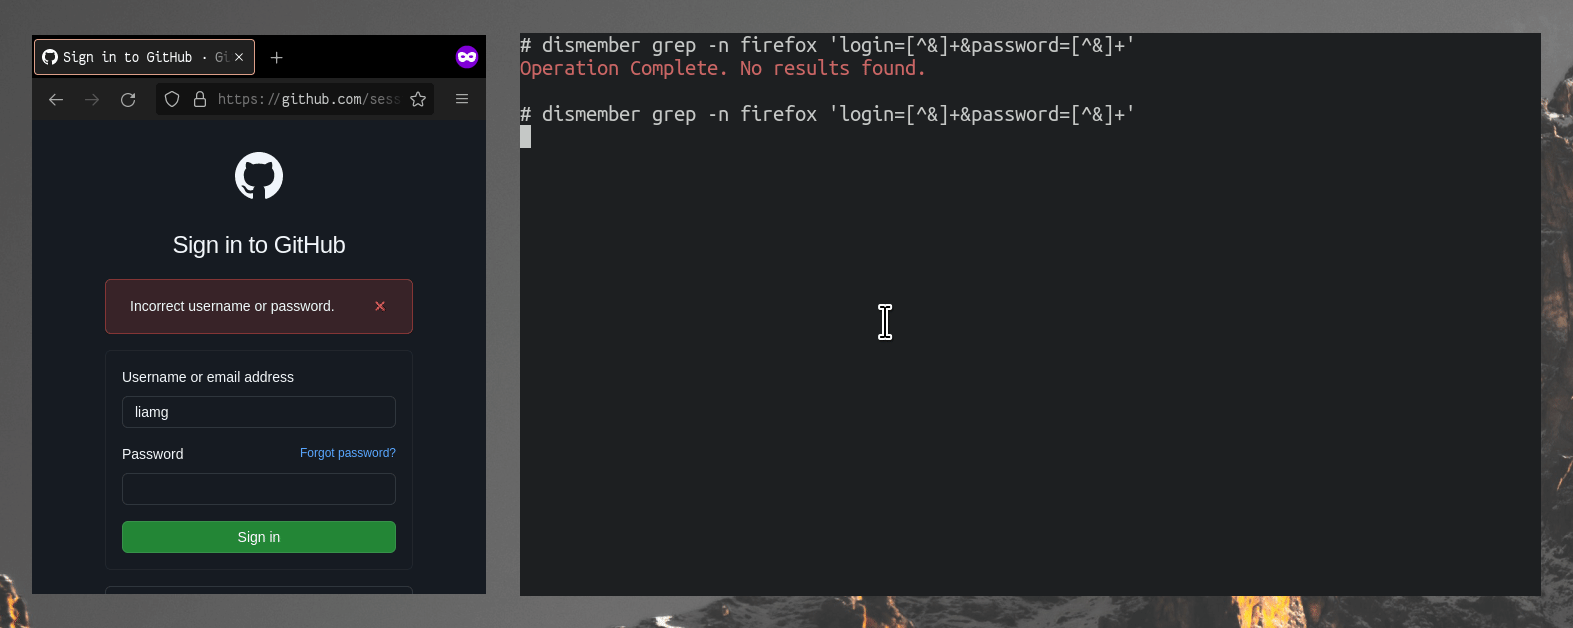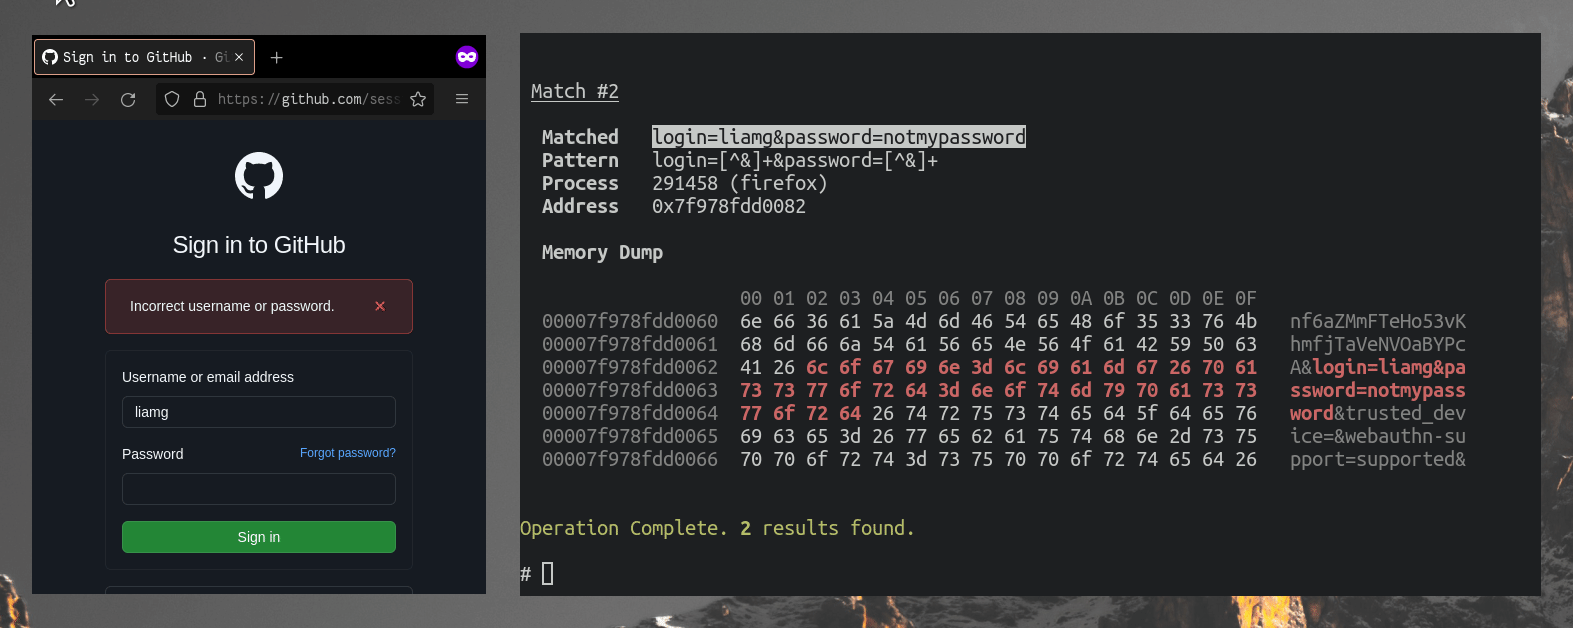 liamg/dismember
:knife: Scan memory for secrets and more. Maybe eventually a full /proc toolkit.