
SGLang-0.5.9-RCE
 stuub/sglang-0.5.9-rce
Proof of Concept exploitation of CVE-2026-5760 - RCE in SGLang 0.5.9 via malicious GGUF
code-analysisctfeducation+5
56 months ago
stuub/sglang-0.5.9-rceProof of Concept exploitation of CVE-2026-5760 - RCE in SGLang 0.5.9 via malicious GGUF
 rippsec/cve-2025-24893-xwiki-ssti-rce
CVE-2025-24893 – XWiki SSTI unauthenticated RCE exploit (HackTheBox CTF)
 charles2gan/gda-android-reversing-tool
the fastest and most powerful android decompiler(native tool working without Java VM) for the APK, DEX, ODEX, OAT, JAR, AAR, and CLASS file. which…
 thefizzyfish/cve-2025-4138_tarfile_filter_bypass
CVE-2025-4138 - Python Arbitrary file write outside extraction directory
 useru1k/php-8.1.0-dev-exploit
Exploit for the PHP 8.1.0-dev backdoor vulnerability (CVE-2021-21707)
 davidaroca27/cve-2024-23346-exploit
This is a exploit for the known Remote Code Execution (RCE) vulnerability in the `pymatgen` (CVE-2024-23346) Python library by uploading a malicious…
 maikneysm/autopwn-titanic.htb
This is an automated exploitation script for the Hack The Box machine *Titanic*. It extracts Gitea user hashes via LFI, assists in cracking them, and…
 ldb33/cve-2023-24249-poc
Proof-of-concept exploit for CVE-2023-24249, an arbitrary file upload vulnerability in laravel-admin, enabling web shell deployment for penetration…
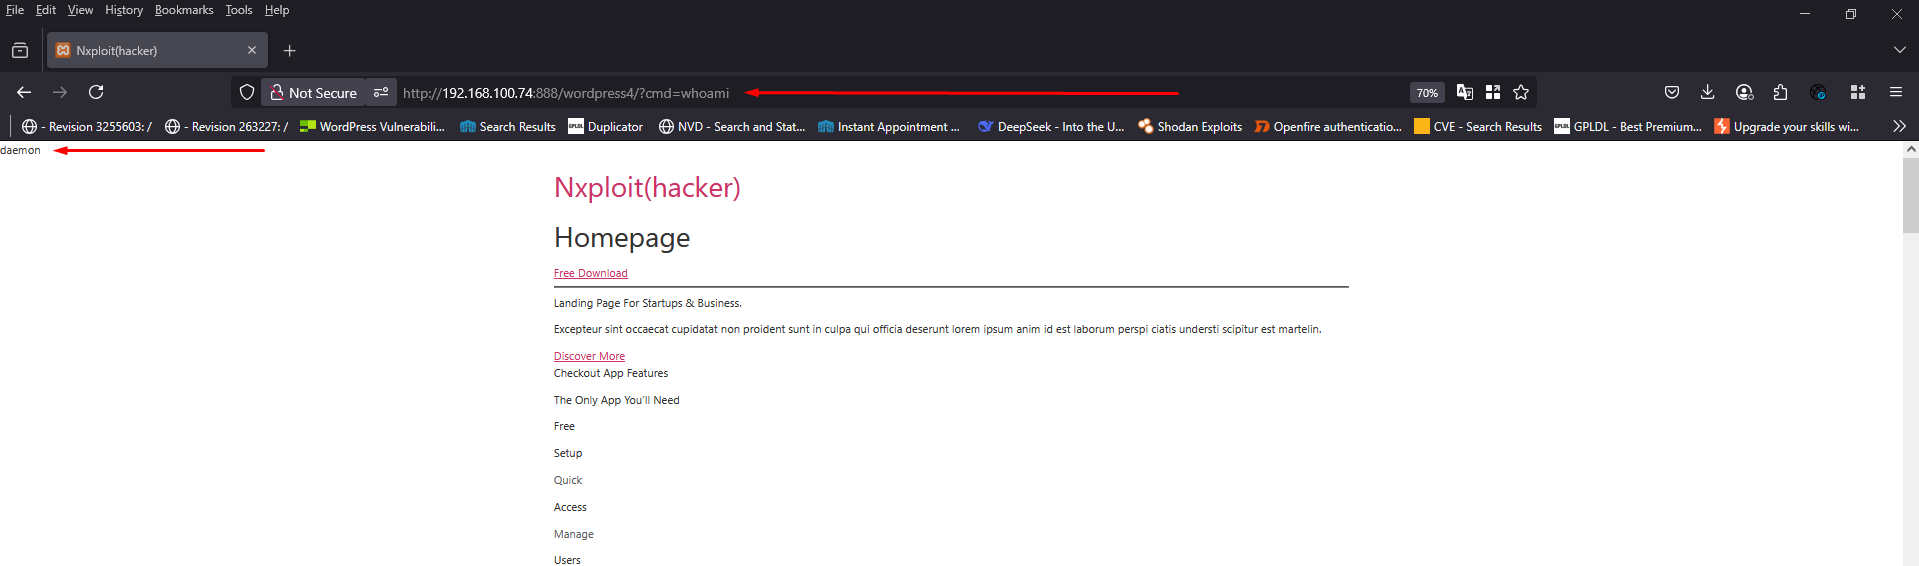 nxploited/cve-2025-39601
WordPress Custom CSS, JS & PHP plugin <= 2.4.1 - CSRF to RCE vulnerability
 pixel-defaultbr/cve-2023-50164
Educational exploit for CVE-2023-50164 (Apache Struts 2) demonstrating path traversal and remote code execution via malicious file upload, designed…
 youssefdds/cve-2024-23724
Proof-of-concept exploit for CVE-2024-23724 in Ghost CMS, demonstrating privilege escalation via malicious SVG profile image upload.
 j3r1ch0123/cve-2024-24590
Created this exploit for the Hack The Box machine, Blurry.
 lgenagul/cve-2023-4220-proof-of-concept
Chamilo LMS Unauthenticated Big Upload File that allows remote code execution
 l41kaa/cve-2023-33733-exploit-poc
Python exploit script for CVE-2023-33733 targeting web applications. Automates authentication, session extraction, and reverse shell delivery for…
 wytchwulf/cve-2015-1397-magento-shoplift
Exploit scripts for CVE-2015-1397 in Magento CMS, including a pre-auth exploit to gain admin credentials and a post-auth RCE module for reverse shell…
 user0x1337/cve-2023-30547
PoC to CVE-2023-30547 (Library vm2)
 battleofthebots/dejavu
Challenge based on CVE-2021-22204 where users send a malicious file to a web application to gain RCE
 otrf/security-datasets
Re-play Security Events