

Labtainers
 mfthomps/labtainers
Labtainers: A Docker-based cyber lab framework
binary-exploitationcryptographyctf+9
mfthomps/labtainersLabtainers: A Docker-based cyber lab framework
 infoslack/awesome-web-hacking
Curated list of web application security resources including books, tools, cheat sheets, labs, and courses for learning penetration testing and…
 ph4l4nx/ctf-s-tools
Repository to index useful tools for CTF's
 hhhrrrttt222111/ethical-hacking-tools
Complete Listing and Usage of Tools used for Ethical Hacking
 bst04/cybersources
A curated list of cybersecurity tools and resources.
 bcoles/kasld
KASLD derandomizes the Linux kernel's virtual and physical memory layout from a local process, using whatever its vantage — privilege, configuration,…
 abraxas/gatex
FortinetHunter (@YogSoth0) binary cracking application. Part of CTF for FortinetHunter. ELF door: a stripped Nuitka onefile, an XOR-scrambled…
 qinglove777/cve-2024-2961-xxe-exploit
CVE-2024-2961 (CNEXT) PHP file-read to RCE exploit adapted to an XXE/CTF channel
 io12/pwninit
Automates setup of binary exploitation challenges by patching ELF binaries, fetching matching linkers, unstripping libc, and generating pwntools…
 motechstore/cve-2025-27591-poc
# CVE-2025-27591 PoC — Below Local Privilege Escalation This repository contains a Proof of Concept (PoC) demonstrating the local privilege…
 nephila016/cve-2025-55319-poc
PoC for CVE-2025-55319
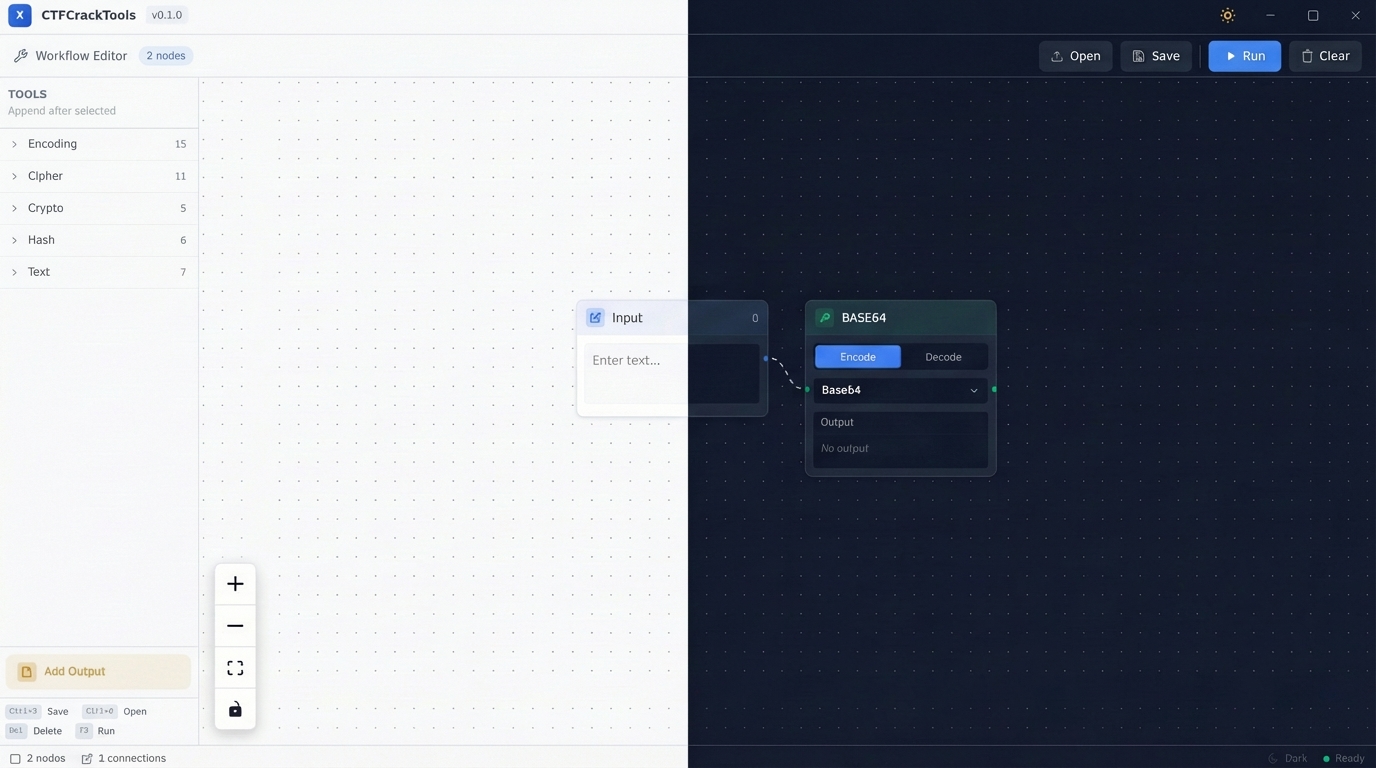 0chencc/ctfcracktools
The next-generation CTF Swiss Army Knife powered by Rust & Tauri. Features a visual node-based workflow and local AI intelligence for extreme…
 3jee/copy-fail-go
Go port of the CVE-2026-31431 (copy-fail) Linux kernel privilege escalation PoC, with automatic SUID binary enumeration and interactive target…
 kaxm23/rust-cve-2025-55182-scanner
powerfull rust cve-2025-55182-scanner used for ctf & ethical purpose only
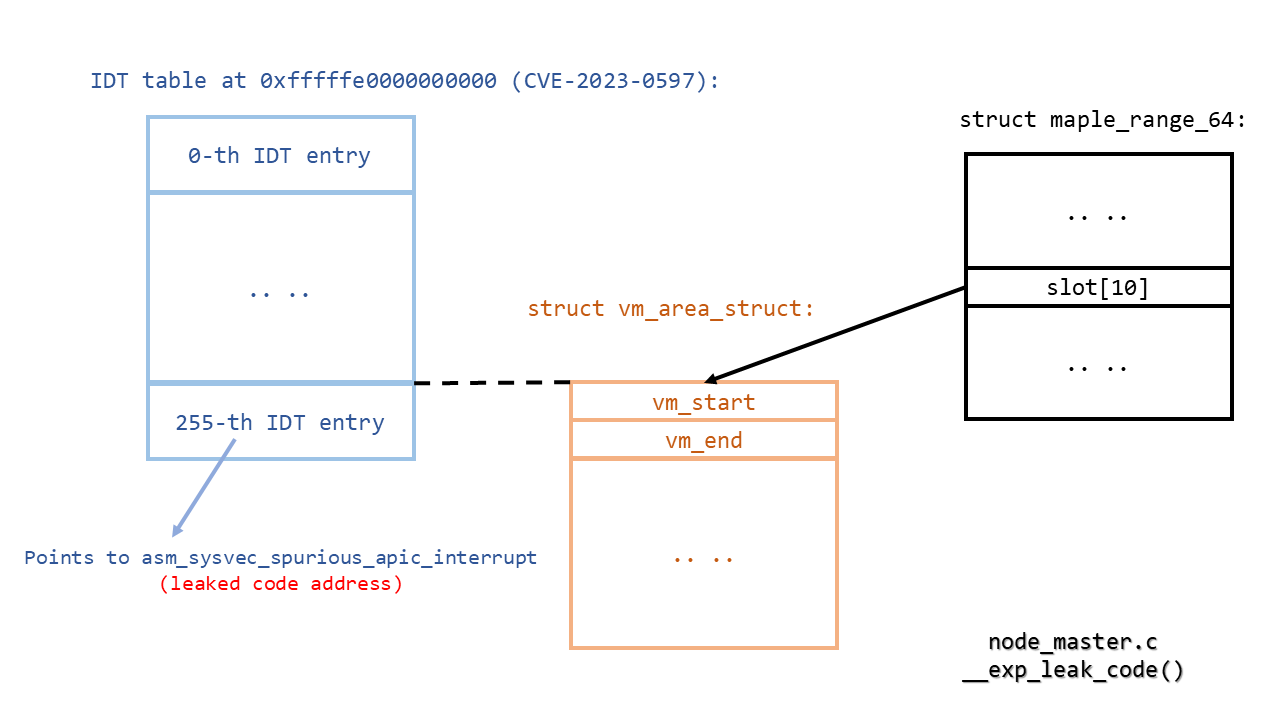 lrh2000/stackrot
CVE-2023-3269: Linux kernel privilege escalation vulnerability
 thefizzyfish/cve-2025-4138_tarfile_filter_bypass
CVE-2025-4138 - Python Arbitrary file write outside extraction directory
 dr4xp/pwnkit-helper
For CTF's and Safe Environments.... CVE-2021-4034 Local PrivEsc.
 j3r1ch0123/cve-2025-32462
Exploit for CVE-2025-32462 enabling privilege escalation by bypassing sudo host restrictions on Linux systems with affected sudo versions and…