
juice-shop
 juice-shop/juice-shop
Intentionally vulnerable web application covering OWASP Top 10 vulnerabilities for security training, CTF competitions, and penetration testing…
ctfeducationlabs-practice+3
13.9k
juice-shop/juice-shopIntentionally vulnerable web application covering OWASP Top 10 vulnerabilities for security training, CTF competitions, and penetration testing…
 soham23/firefox-rce-nssmil
Educational standalone JavaScript implementation of the public exploit for CVE-2016-9079 (Firefox Use-After-Free), adapted from the original…
 anxs3c/twomillion-machine-writeup
From deobfuscating code.js to root, CVE-2023-0386
 koadt/poc-cve-2025-29927
This repository contains a proof of concept (POC) and an exploit script for CVE-2025-29927, a critical vulnerability in Next.js that allows attackers…
 koadt/poc-cve-2025-55182
This repository contains a POC of CVE-2025-55182, a critical (CVSS score 10.0) pre-authentication remote code execution vulnerability affecting React…
 amusedx/cve-2026-22686
CTF challenge focused on sandbox escape via source code review of a JavaScript execution environment, designed for hands-on vulnerability analysis…
 eyodav/cve-2025-34157
A stored XSS in the project delete flow allows execution of attacker-controlled JavaScript in an administrator’s browser when the admin attempts to…
 binneko/cve-2025-46041
Proof-of-concept for a stored XSS vulnerability in Anchor CMS v0.12.7, demonstrating arbitrary JavaScript execution via the page description field.
 naveen-005/next.js-middleware-bypass-vulnerability-cve-2025-29927
A basic proof of concept of the CVE-2025-29927 vulnerability that allows to bypass the middleware scripts.
 terjanq/tiny-xss-payloads
A collection of tiny XSS Payloads that can be used in different contexts. https://tinyxss.terjanq.me
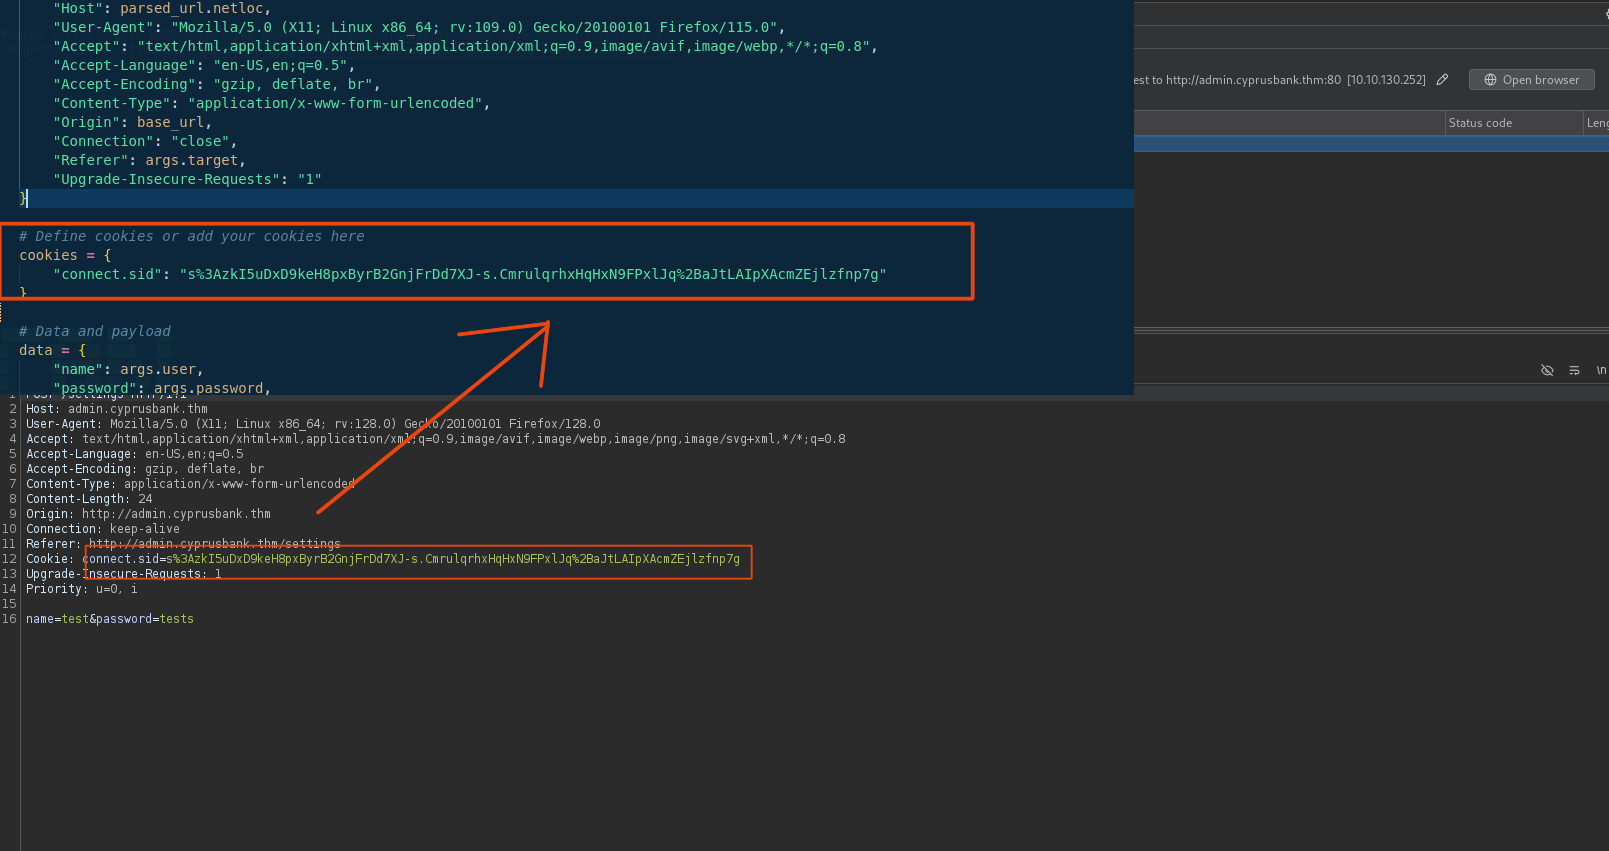 l0n3m4n/cve-2022-29078
Serverside Template Injection (SSTI) RCE - THM challenge "whiterose"
 mbrandner-group/juiceshopgl
Intentionally vulnerable web application for security training, CTF competitions, and testing security tools. Covers OWASP Top Ten vulnerabilities…