h4cker
 the-art-of-hacking/h4cker
Curated collection of cybersecurity resources, labs, and training materials covering ethical hacking, penetration testing, exploit development,…
ai-securityctfcurated-resources+8
29.5k
the-art-of-hacking/h4ckerCurated collection of cybersecurity resources, labs, and training materials covering ethical hacking, penetration testing, exploit development,…
 qazbnm456/awesome-web-security
🐶 A curated list of Web Security materials and resources.
 ledksv/wingdata
HackTheBox Wingdata walkthrough covering WingFTP CVE-2025-47812 command injection for initial access and tar path traversal sudo privilege escalation…
 r3fr4kt/devvortex
HackTheBox Devvortex walkthrough covering subdomain fuzzing, Joomla API enumeration, template-based web shell, bcrypt hash cracking, and Apport-CLI…
 fknmega/aether
AI-driven OSINT and security research agent that builds a live knowledge graph from public data, with bundled recon tools and offensive-security…
 porcumarcooo/tryhackme-blue-ms17-010
Walkthrough, threat analysis, and remediation guide for CVE-2017-0144 (EternalBlue).
 elder-plinius/t3mp3st
autonomous red teaming platform; multi-agent offensive-security meta-harness
 s0ld13rr/pentestcode
Autonomous AI penetration testing agent that orchestrates multi-agent recon, exploitation, post-exploitation, and reporting with persistent…

 wattocyber/offensive-one-liners
110 offensive-security one-liners for authorized testing and CTFs, grouped by category and kill-chain step.
 jgalego/hiddensteps
HiddenSteps — a local-first personal workflow intelligence platform
 pannagkumaar/pentest-lab
Modern cyber range with 50 hands-on challenges across web, API, cloud, AI, and blue-team security tracks. Features guided attack chains, transparent…
 parbatzone/reconvault
🔍 Recon notes organizer for bug bounty hunters and CTF players — subdomains, ports, endpoints, vulns, all in one place.
 inertfluid/cve-2026-54316-lab
Reproduction lab for CVE-2026-54316 (Claude Code WebFetch huggingface.co bare-hostname permission bypass / exfiltration)
 ledksv/monitorsfour
HackTheBox MonitorsFour walkthrough covering credential leak, CVE-2025-24367 Cacti RCE, and CVE-2025-9074 Docker Desktop API container escape to root.
 r3fr4kt/popcorn-tjnull-oscp-
Popcorn HTB write-up covering advanced directory fuzzing, file upload bypass via magic numbers/extension spoofing using Burp Suite, and privilege…
 musa-xvi/active-directory-badsuccessor
A TryHackme room covering the CVE-2025-53779 exploitation using windows
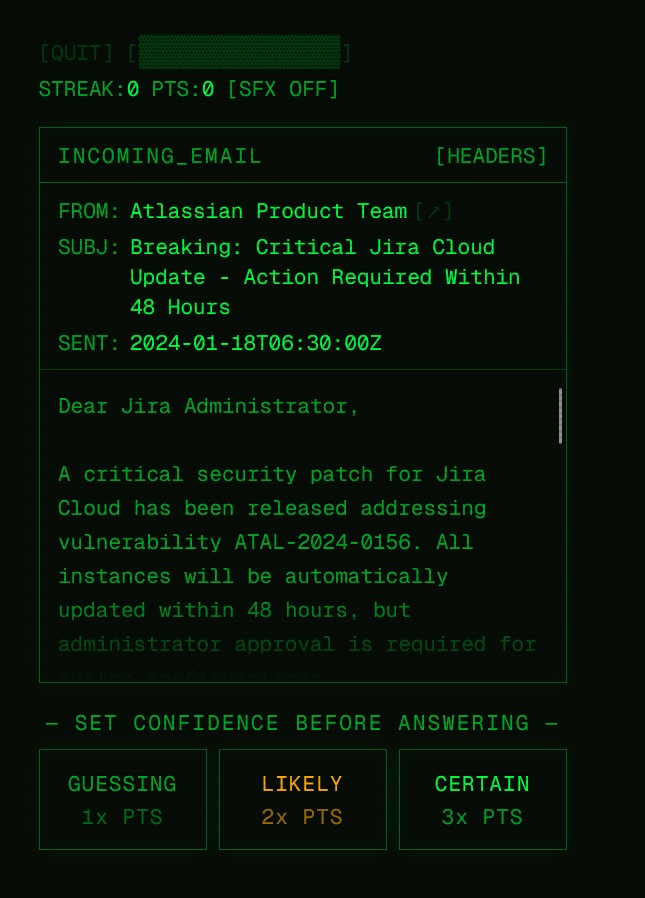 scottalt/ai-email-threat-research
A cybersecurity research game measuring how humans detect AI-generated phishing emails. Built as a retro terminal experience.