

CyberSecurity-Pentest-Lab
 germarr93/cybersecurity-pentest-lab
CVE-2004-2687 (Distcc 3.2.1) exploitation, methodology & remediation — Metasploitable2 lab
ctfeducationexploitation+6
1
germarr93/cybersecurity-pentest-labCVE-2004-2687 (Distcc 3.2.1) exploitation, methodology & remediation — Metasploitable2 lab
 abraxas/gatex
FortinetHunter (@YogSoth0) binary cracking application. Part of CTF for FortinetHunter. ELF door: a stripped Nuitka onefile, an XOR-scrambled…
 gonzabot/kernel-exploit-dirtycow
Lab — Privilege Escalation via Dirty Cow CVE-2016-5195 | 4Geeks Academy
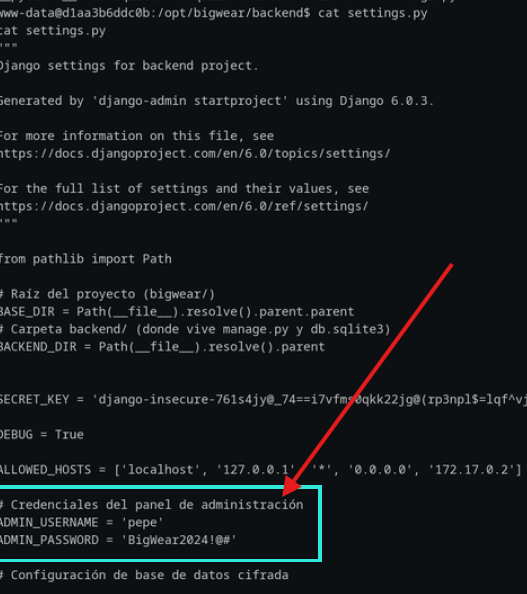 salimelh94/web-penetration-test
Exploiting WordPress vulnerabilities (CVE-2025-34077), authentication bypass via cookie injection, and privilege escalation to root. Part of my…
 0xtensho/cve-2025-49132-poc
Proof-of-concept exploit for CVE-2025-49132, abusing a file inclusion vulnerability in Pterodactyl to achieve remote code execution via pearcmd.php.
 illera88/ponce
IDA 2016 plugin contest winner! Symbolic Execution just one-click away!
 owasp/mas-crackmes
The MAS Crackmes aka. UnCrackable Apps, a collection of mobile reverse engineering challenges part of the OWASP MAS project.
 natteesetobol/cve-2018-15133-lavel-expliot
"Lavel Exploit CVE-2018-15133 is a powerful exploit that allows attackers to gain unauthorized access to vulnerable systems. This exploit was…
 synacktiv/toy-wasm-symbexp
A toy symbolic execution engine, supporting the blog article ...
 m1ghtym0/browser-pwn
An updated collection of resources targeting browser-exploitation.
 danielazulayy/ctf-2021
CTF for HDE 64 students at See Security College. Exploit a JWT (web part) & CVE-2021-3156 (LPE part).