
CVE-2025-29927-PoC
 ritinify/cve-2025-29927-poc
Proof-of-concept exploit for CVE-2025-29927, a Next.js middleware authorization bypass. Includes a vulnerable target lab and Python script to verify…
ctfeducationexploitation+3
ritinify/cve-2025-29927-pocProof-of-concept exploit for CVE-2025-29927, a Next.js middleware authorization bypass. Includes a vulnerable target lab and Python script to verify…
 r4y-br/cve-2022-22963
Python automation script that reproduces CVE-2022-22963, a critical SpEL injection in Spring Cloud Function, enabling reverse shell in authorized lab…
 cves-labs/cve-2026-21877
Dockerized vulnerable lab environment with a Python-based network monitor and dedicated exploit script, enabling hands-on exploitation, privilege…
 hunt-benito/llama-factory-webui-rce-cve-2026-58116-trust-remote-code-model-path-injection
Proof-of-concept exploit for CVE-2026-58116 demonstrating remote code execution in LLaMA-Factory WebUI via trust_remote_code model path injection.…
 jithinodattu/cve-2007-4559-lab
Self-contained Docker lab demonstrating CVE-2007-4559 (TarSlip) directory traversal via Python's tarfile module. Includes vulnerable and fixed APIs,…
 tombstoneghost/htb-sau-exploit-chain
Automated exploit chain for HTB Sau — CVE-2023-27163 (SSRF) + Maltrail Unauthenticated RCE → Reverse Shell
 maradonam18/-cve-2025-59528-poc
A simple python script to exploit CVE-2025-59528, this an Authenticated RCE vulnerability in Flowise application, a popular AI tool. That is also…
 liquid-sec/variatype.htb-cve-2025-66034
Python exploit script for CVE-2025-66034 in the HackTheBox Variatype machine, delivering command execution and reverse shell payloads for initial…
 azureadtrent/cve-2025-4517-poc
Privilege Escalation script for CVE-2025-4517
 trax69/cve-2025-55182-poc
Proof of Concept for CVE-2025-55182 ("React2Shell"). A fully dockerized environment demonstrating Remote Code Execution (RCE) via insecure…
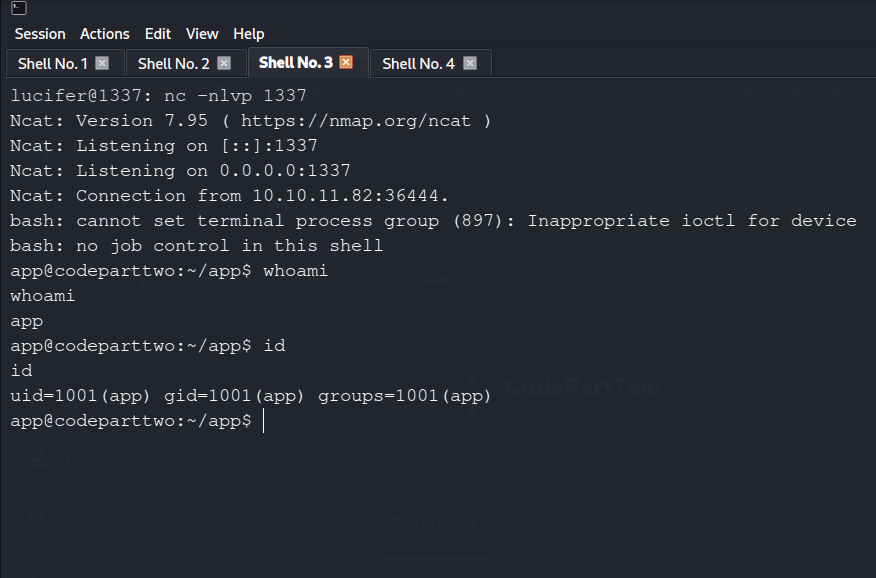 l1337xi/cve-2024-28397-exploit-automation
A Python automation script for exploiting the **js2py Sandbox Escape** vulnerability (CVE-2024-28397). This tool automates the payload generation and…
 n0m4d22/poc-cve-2015-10141-xdebug
Proof-of-Concept exploit script for Xdebug 2.5.5 and earlier versions (CVE-2015-10141).

 rootharpy/cve-2025-5287
Unauthenticated SQL Injection exploit for WordPress Likes and Dislikes Plugin ≤ 1.0.0
 elusivehacker/cve-2019-7214
For CTF use only (the CVE-2019-7214 also resolves the host from /etc/hosts)

 l41kaa/cve-2023-33733-exploit-poc
Python exploit script for CVE-2023-33733 targeting web applications. Automates authentication, session extraction, and reverse shell delivery for…
 foxyproxys/cve-2023-52654
Automated privilege escalation script exploiting misconfigured setuid/sgid binaries, sudo, cron, and LD_PRELOAD on Unix systems. Designed for CTF and…