

x64dbg
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
ai-assisted-reversingbinary-analysisbinary-exploitation+7
49.6k9h 59m ago
x64dbg/x64dbgAn open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 0xor0ne/awesome-list
Cybersecurity oriented awesome list
 frankwxu/digital-forensics-lab
Free hands-on digital forensics labs for students and faculty
 mytechnotalent/reverse-engineering
A FREE comprehensive reverse engineering tutorial covering x86, x64, 32-bit/64-bit ARM, 8-bit AVR and 32-bit RISC-V architectures.
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 owasp/wrongsecrets-binaries
Source code for the Binaries of OWASP WrongSecrets
 angr/angr
A powerful and user-friendly binary analysis platform!
 devploit/awesome-ctf-resources
A list of Capture The Flag (CTF) frameworks, libraries, resources and software for started/experienced CTF players 🚩
 1833ravikumar-max/cve-2021-41773-apache-path-traversal-lab
Docker-based cybersecurity lab for studying and reproducing CVE-2021-41773 in an isolated environment.
 the-art-of-hacking/h4cker
Curated collection of cybersecurity resources, labs, and training materials covering ethical hacking, penetration testing, exploit development,…
 recurse-labs/recurse
Agentic reverse engineering IDE with a pure-Rust multi-architecture disassembler, native decompiler, debugger, and LLM agent for binary analysis and…
 zhaoxuya520/reverse-skill
AI-powered skill router pack for reverse engineering, penetration testing, and security research. Routes AI agents to correct methodologies and…
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
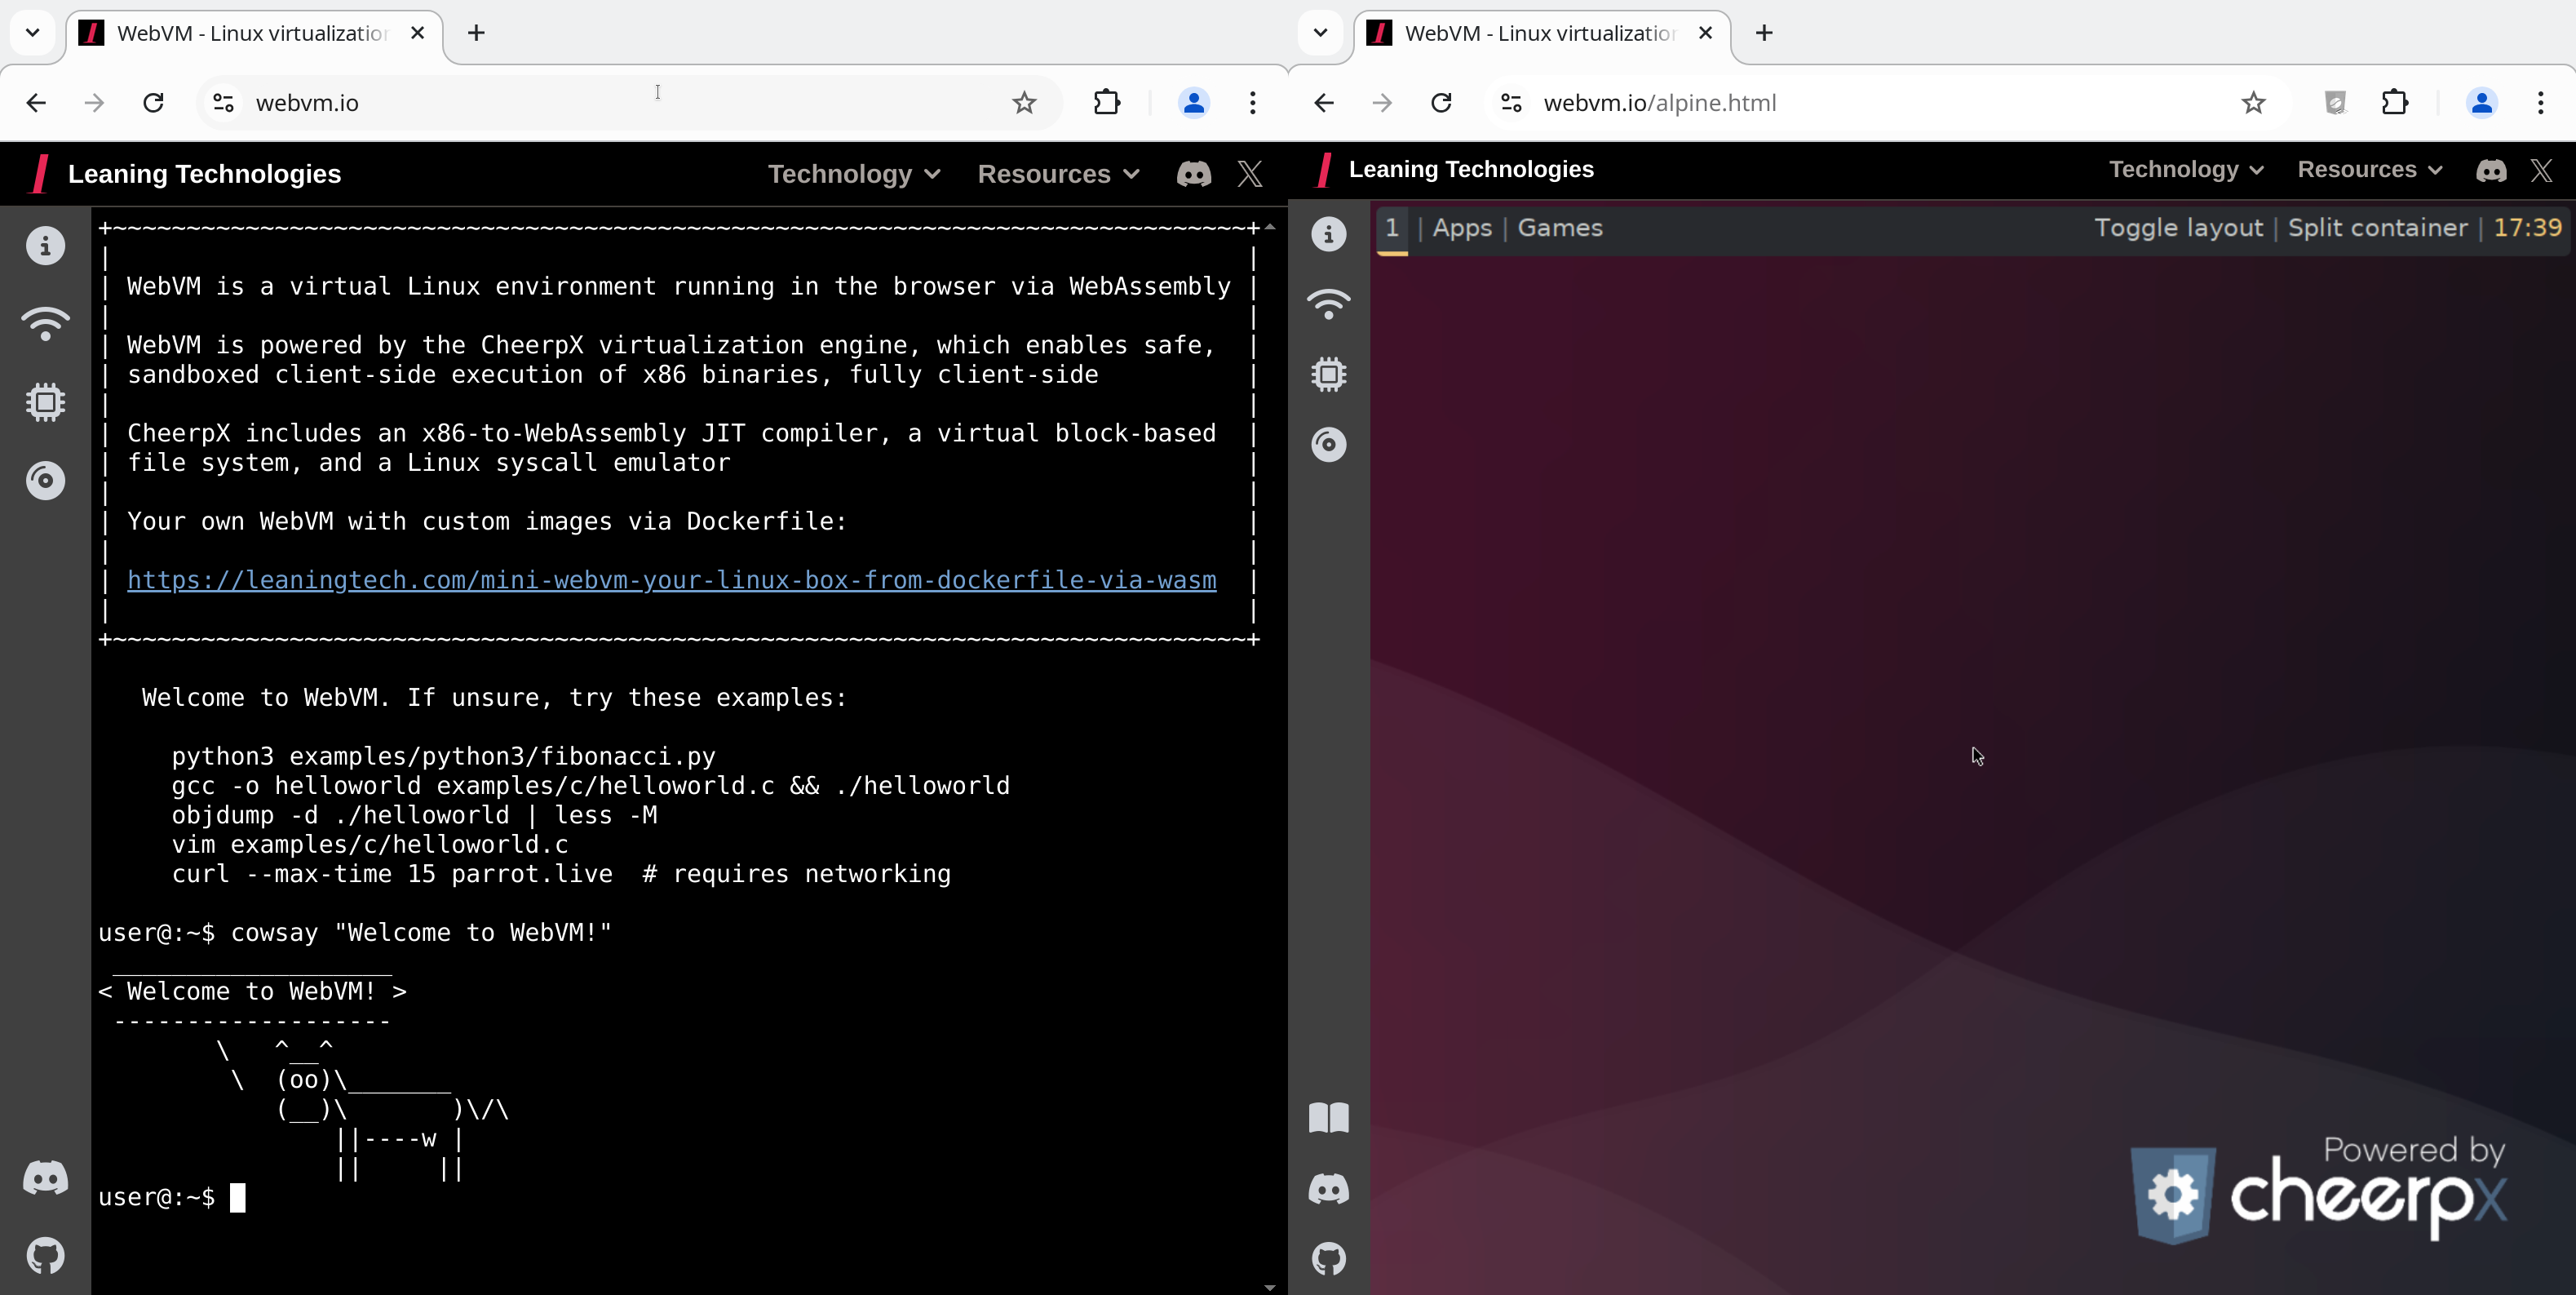 leaningtech/webvm
Client-side Linux virtual machine running in the browser via WebAssembly, with Tailscale networking, Dockerfile-based custom images, and CTF…
 bst04/cybersources
A curated list of cybersecurity tools and resources.