
atomicvulns
 doretox/atomicvulns
Atomic web vulnerability labs. One OWASP flaw per app — minimal Flask + Docker, intentionally broken for hands-on study with Burp Suite.
ctfeducationlabs-practice+5
8
doretox/atomicvulnsAtomic web vulnerability labs. One OWASP flaw per app — minimal Flask + Docker, intentionally broken for hands-on study with Burp Suite.
 vatsal200600/stegolab
All-in-one Image Steganography Toolkit for CTFs & Forensics

 wattocyber/offensive-one-liners
110 offensive-security one-liners for authorized testing and CTFs, grouped by category and kill-chain step.
 agampreet-singh/redroot
RedRoot is a Python-based, CLI-driven offensive security framework that brings essential red teaming tools into one unified terminal environment.…

 ecu-10525611-xander/cve-2022-37706
All Credit to MaherAzzouzi (https://github.com/MaherAzzouzi/CVE-2022-37706-LPE-exploit). This is a copy of the exploit for CTFs
 drhaitham/cve-2014-6271-shellshock-
A complete, modern demonstration lab for CVE-2014-6271 (Shellshock), including architecture, exploitation steps, Burp Suite usage, reverse shells,…
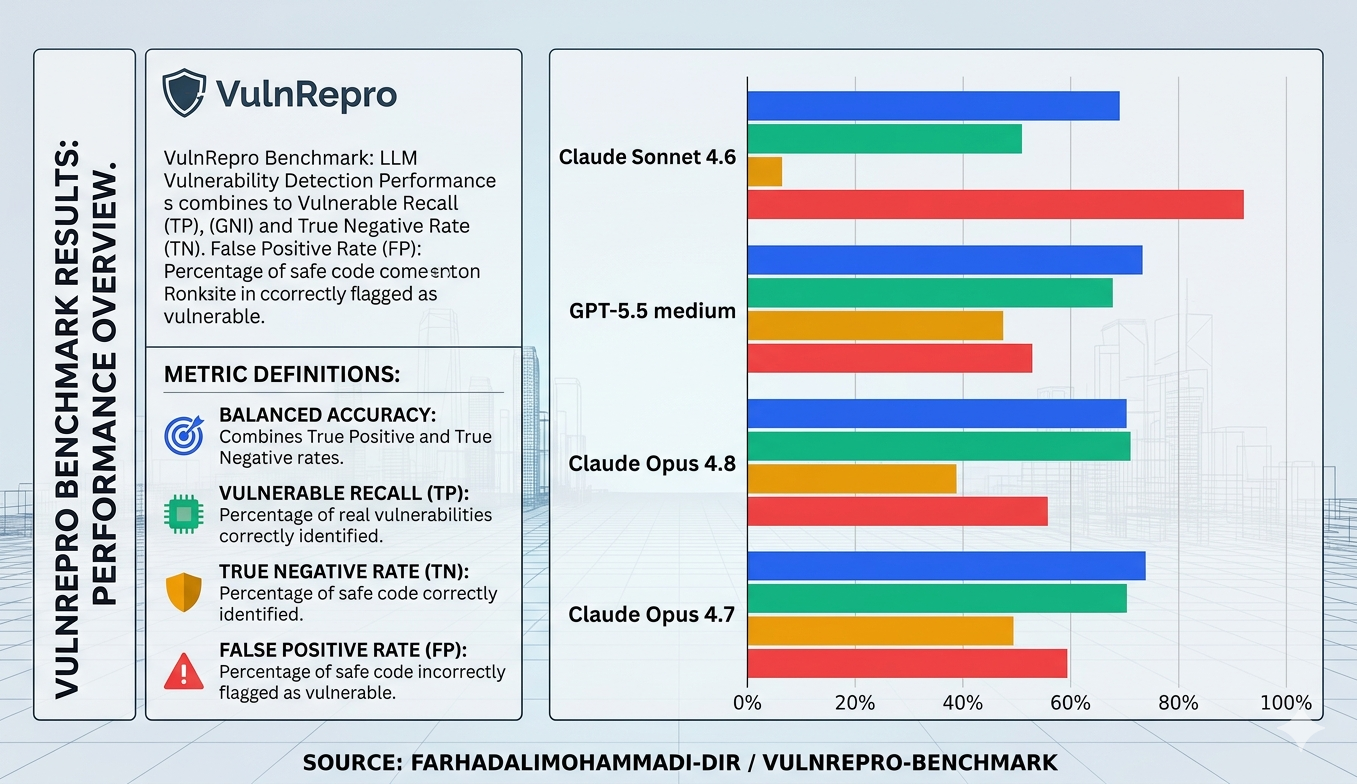 farhadalimohammadi-dir/vulnrepro-benchmark
Benchmark measuring AI models' ability to detect vulnerabilities in source code via real bug bounty cases with balanced recall and false-positive…
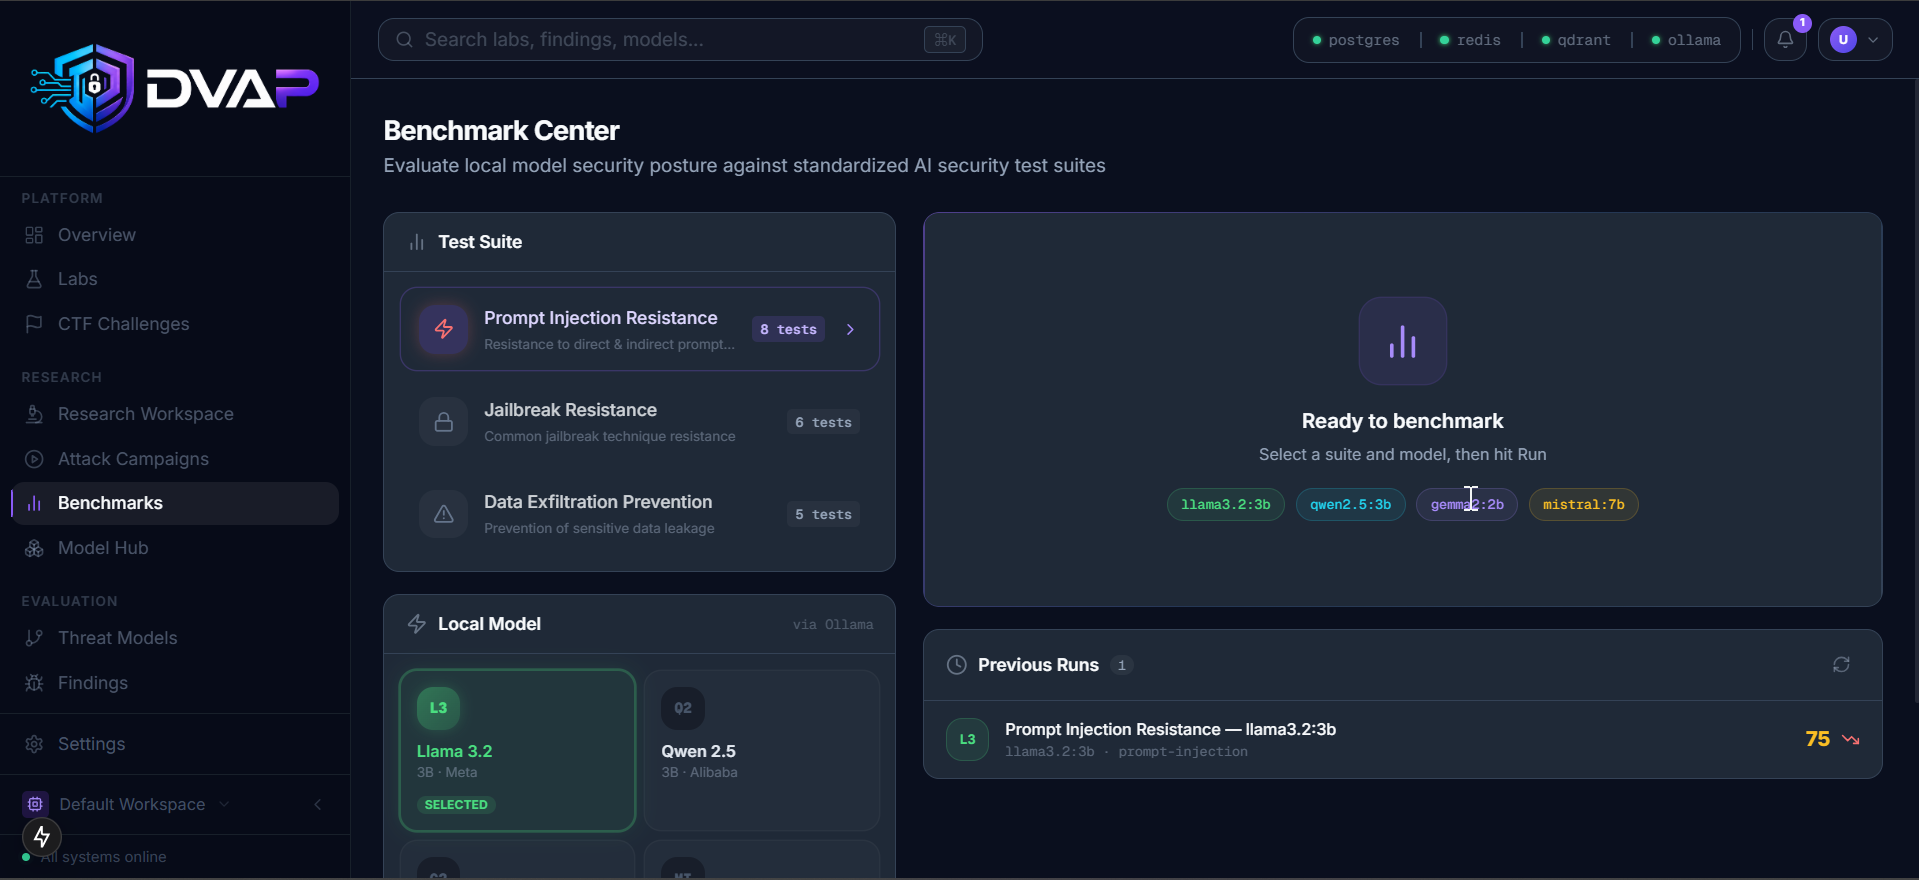 sonuoffsec/dvap
An OWASP-aligned intentionally vulnerable platform for learning and testing AI, LLM, RAG, MCP, and Agentic AI security.
 bluedragonsecurity/linux-kernel-dirty-pipe-exploitation-logic-bug-
Exploiting CVE-2022-0847 - written by : Antonius (w1sdom)
 themursalin/htb-mailing-a-complete-walkthrough
If you've been grinding through HackTheBox machines, Mailing is one of those boxes that genuinely teaches you something. It's rated Easy, runs on…
 apexpredator-infosec/forti_shield
A combined POC for CVE-2021-31955, CVE-2015-4077, and CVE-2015-5736
 adityabhatt3010/react2shell-cve-2025-55182
React2Shell CVE-2025-55182: unauthenticated unsafe deserialization in React Server Components leading to reliable remote code execution via the…
 oritwoen/boha
Crypto bounties, puzzles and challenges data library
 cinnamon1212/modified-cve-2020-10915-msfmodule
THIS IS NOT AN ORIGINAL EXPLOIT. THIS IS AN AUDITED VERSION FOR A THM BOX
 parbatzone/reconvault
🔍 Recon notes organizer for bug bounty hunters and CTF players — subdomains, ports, endpoints, vulns, all in one place.
 danielmiessler/seclists
Curated collection of wordlists for security assessments, including usernames, passwords, URLs, fuzzing payloads, and sensitive data patterns for…
 lockedbyte/cryptovenom
Cryptovenom: The Cryptography Swiss Army Knife