
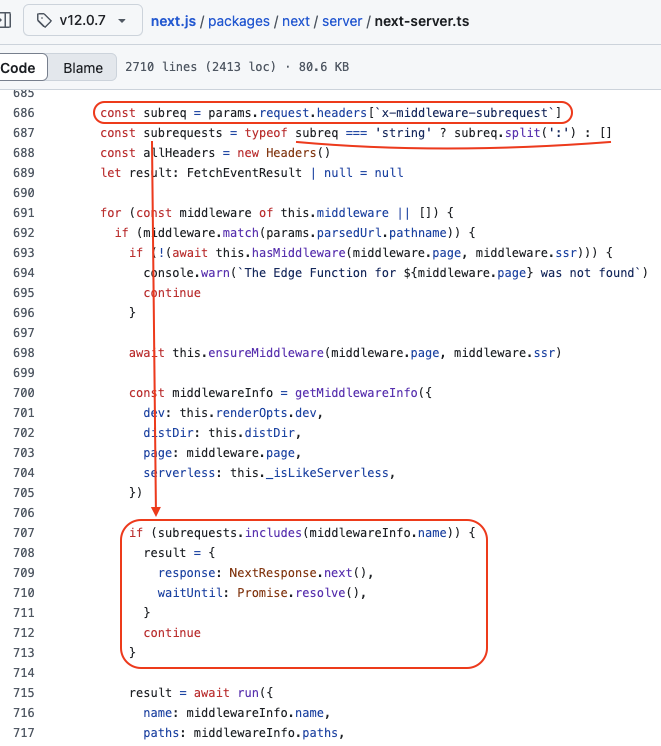
 gokul-krishnan-v-r/cve-2025-29927
Next.js and the corrupt middleware...TRY TO HACK IT..!
 prprhyt/poc_tls1_3_cve-2020-13777
Proof-of-concept for CVE-2020-13777 (GnuTLS TLS 1.3 reconnect vulnerability). Parses pcap files to demonstrate the flaw for educational and technical…
 eyodav/cve-2025-34157
A stored XSS in the project delete flow allows execution of attacker-controlled JavaScript in an administrator’s browser when the admin attempts to…
 pasan2002/cve-2019-9053---cms-made-simple-sql-injection-exploit-modified-
This is a modified version of the time-based SQL injection exploit for CMS Made Simple <= 2.2.9. The exploit was originally created by Daniele Scanu…
 keymandll/cve-2022-29622
Hack this service to prove CVE-2022–29622 is valid
 j3r1ch0123/cve-2024-24590
Created this exploit for the Hack The Box machine, Blurry.
 adindrabkin/llama_facts
Web application vulnerable to Python3 Flask SSTI (CVE-2019-8341)
 0xgh057r3c0n/cve-2025-6934
CVE-2025-6934 is a critical vulnerability in the WordPress Opal Estate Pro plugin (<= 1.7.5) that allows unauthenticated attackers to create new…
 sn0wbaall/cve-2024-23334-poc
Automated proof-of-concept exploit for CVE-2024-23334, a path traversal vulnerability in aiohttp, enabling remote directory traversal and…
 19melek19/themisfits-cve-2024-8465-sqli
Intentionally vulnerable PHP web app demonstrating SQL injection authentication bypass and unauthorized data disclosure modeled after CVE-2024-8465…
 zardus/ctf-tools
Some setup scripts for security research tools.