
CVE-2026
 horkimhab/cve-2026
Educational collection of CVE proof-of-concept resources and vulnerability research material for authorized lab testing, defensive study, and secure…
ctfcurated-resourceseducation+4
horkimhab/cve-2026Educational collection of CVE proof-of-concept resources and vulnerability research material for authorized lab testing, defensive study, and secure…
 horkimhab/cve-2026-74469
Proof-of-concept and educational research repository for CVE-2026-74469 (DiagSpill), providing vulnerability analysis material for authorized lab…
 shivammittal2403/cve-2026-80428-ctf
Containerized educational CTF lab emulating CVE-2026-80428 (CWE-502 deserialization) for safe, isolated student and researcher practice.
 iknowjason/awesome-cloudsec-labs
Awesome free cloud native security learning labs. Includes CTF, self-hosted workshops, guided vulnerability labs, and research labs.
 sadfud/exploits
Real world and CTFs exploiting web/binary POCs.
 owasp/vulnerable-container-hub
VULCONHUB provides access to files to build your own hands-on vulnerable container image to learn and practice security
 yusufdalbudak/cve-2026-42945
Dockerized lab for training on NGINX rewrite vulnerability (CVE-2026-42945) with vulnerable and patched instances, benign test scripts, and…
 mooowu/cve-2025-55182-poc
Lab environment and PoC exploit for CVE-2025-55182 (React2Shell), a critical RCE vulnerability in React Server Components. Includes vulnerable app,…
 d1se0/cve-2024-10924-bypass-mfa-wordpress-lab
Lab environment and exploit script for CVE-2024-10924, demonstrating MFA bypass in WordPress via the Really Simple SSL plugin's skip_onboarding…
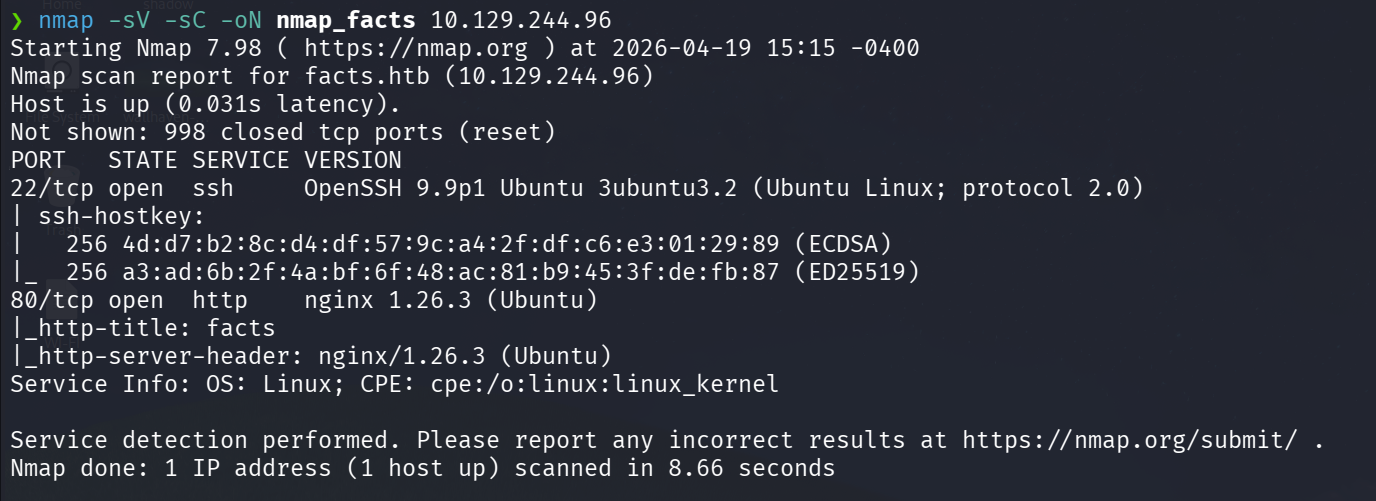 mattiapertusati/htb-facts
HackTheBox — Facts (Easy/Linux) | CVE-2025-2304 + AWS S3 + SSH Key + Facter PrivEsc
 wired0ut/cve-2012-6422
An exploitation for the /dev/exynos-mem vulnerability introduced in earlier samsung phones.
 0x4m4/hexstrike-ai
MCP server enabling AI agents to autonomously execute 150+ cybersecurity tools for automated penetration testing, vulnerability discovery, bug bounty…
 infoslack/awesome-web-hacking
Curated list of web application security resources including books, tools, cheat sheets, labs, and courses for learning penetration testing and…
 tencent/ai-infra-guard
A full-stack AI Red Teaming platform securing AI ecosystems via Agent Scan, Skills Scan, MCP scan, AI Infra scan and LLM jailbreak evaluation.
 reddelexc/hackerone-reports
Curated collection of top HackerOne bug bounty reports organized by vulnerability type and program, with scripts to fetch, deduplicate, and rank…
 shaniidev/bug-reaper
Web2 bug bounty Agent Skill — evidence-based, no AI slop. Covers 18 vulnerability classes across HackerOne, Bugcrowd, Intigriti, and YesWeHack.
 maikneysm/autopwn-titanic.htb
This is an automated exploitation script for the Hack The Box machine *Titanic*. It extracts Gitea user hashes via LFI, assists in cracking them, and…
 cybertechajju/cve-2025-57819
Nuclei-based toolkit for detecting and validating the FreePBX authentication bypass vulnerability (CVE-2025-57819) with detection and exploit PoC…