
CVE-2026-38526
 harry178945/cve-2026-38526
Python PoC exploiting CVE-2026-38526 in Krayin CRM <= 2.2.x: authenticated PHP webshell upload via /admin/tinymce/upload leading to remote code…
ctfexploitationpayload-development+5
harry178945/cve-2026-38526Python PoC exploiting CVE-2026-38526 in Krayin CRM <= 2.2.x: authenticated PHP webshell upload via /admin/tinymce/upload leading to remote code…
 mrdark-ops/cve-2026-38526
Python PoC exploiting CVE-2026-38526 in Krayin CRM <= 2.2.x: authenticates, uploads a PHP webshell via /admin/tinymce/upload, and executes commands…
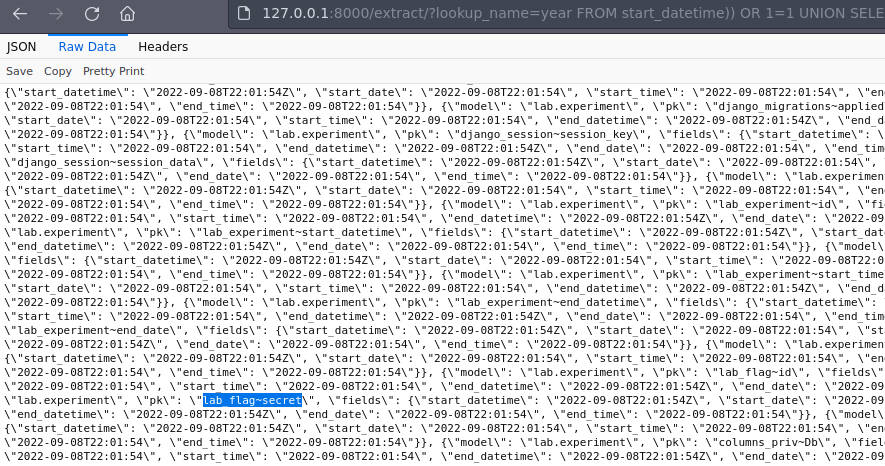 lnwza0x0a/ctf_django_cve-2022-34265
Docker-based CTF challenge demonstrating SQL injection in Django's Trunc() and Extract() database functions (CVE-2022-34265) with UNION-based payload…
 useru1k/php-8.1.0-dev-exploit
Exploit for the PHP 8.1.0-dev backdoor vulnerability (CVE-2021-21707)
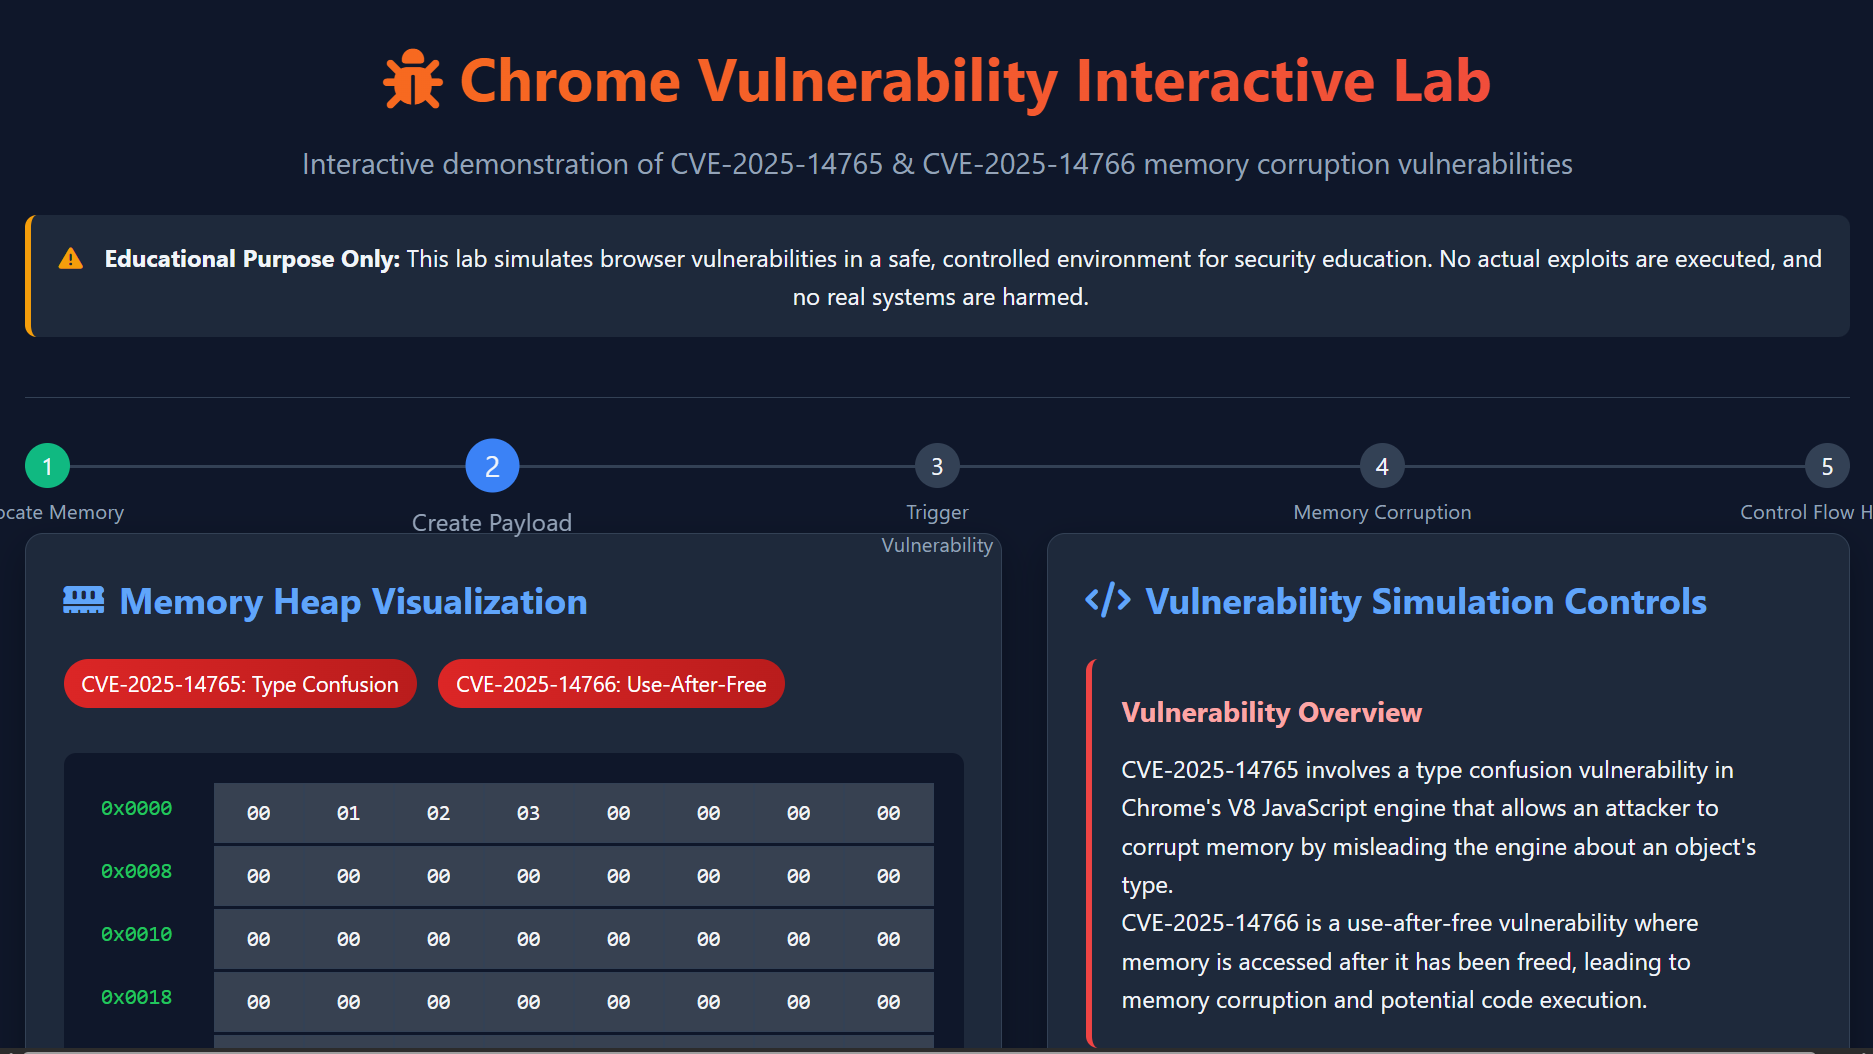 infosecantara/cve-2025-14765-and-cve-2025-14766
Interactive browser-based lab simulating Chrome memory corruption vulnerabilities (CVE-2025-14765/14766) for safe security training, featuring…
 mafiosohack/offensive-lab-2
Penetration test walkthrough on a vulnerable Ubuntu VM. Exploited the ProFTPD 1.3.3c backdoor (CVE-2010-4221) to gain root access and capture the…
 j4ck3lsyn-gen2/n8n-cve-2025-68613-tryhackme
The minor methodology for room: https://tryhackme.com/room/n8ncve202568613
 hunt-benito/llama-factory-webui-rce-cve-2026-58116-trust-remote-code-model-path-injection
Proof-of-concept exploit for CVE-2026-58116 demonstrating remote code execution in LLaMA-Factory WebUI via trust_remote_code model path injection.…
 thefizzyfish/cve-2025-4138_tarfile_filter_bypass
CVE-2025-4138 - Python Arbitrary file write outside extraction directory
 rippsec/cve-2025-24893-xwiki-ssti-rce
CVE-2025-24893 – XWiki SSTI unauthenticated RCE exploit (HackTheBox CTF)
 okymi-x/cve-2024-34070
Proof-of-concept exploit for CVE-2024-34070, a stored XSS in Froxlor. Detects vulnerable instances, extracts version, and injects payload to create…
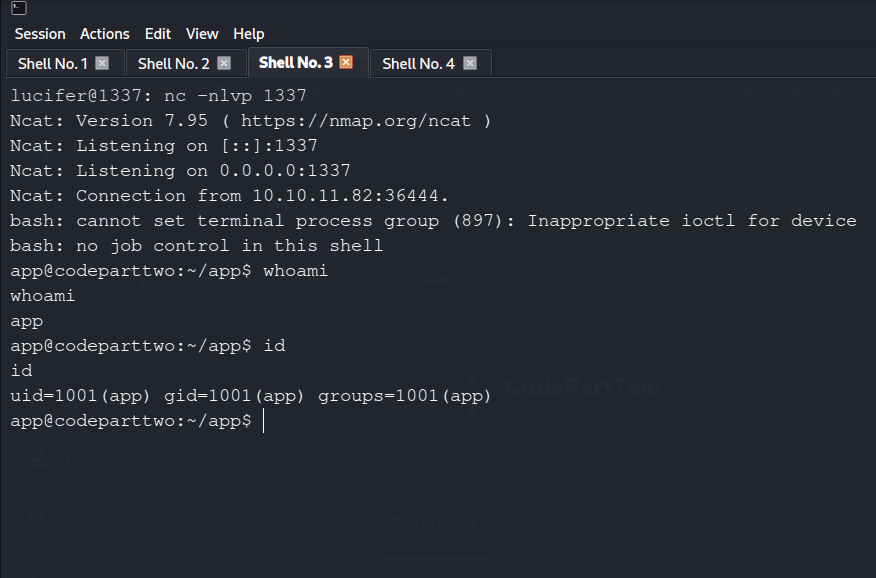 l1337xi/cve-2024-28397-exploit-automation
A Python automation script for exploiting the **js2py Sandbox Escape** vulnerability (CVE-2024-28397). This tool automates the payload generation and…
 davidaroca27/cve-2024-23346-exploit
This is a exploit for the known Remote Code Execution (RCE) vulnerability in the `pymatgen` (CVE-2024-23346) Python library by uploading a malicious…
 lgenagul/cve-2023-4220-proof-of-concept
Chamilo LMS Unauthenticated Big Upload File that allows remote code execution
 l41kaa/cve-2023-33733-exploit-poc
Python exploit script for CVE-2023-33733 targeting web applications. Automates authentication, session extraction, and reverse shell delivery for…
 user0x1337/cve-2023-30547
PoC to CVE-2023-30547 (Library vm2)
 ldb33/cve-2023-24249-poc
Proof-of-concept exploit for CVE-2023-24249, an arbitrary file upload vulnerability in laravel-admin, enabling web shell deployment for penetration…