

owasp-ctf
 owasp/owasp-ctf
Self-hosted CTF control plane for security-learning events: team registration, live leaderboard, and patch-to-score, quiz, jeopardy, and AI challenge…
container-securityctfdevsecops+7
11
owasp/owasp-ctfSelf-hosted CTF control plane for security-learning events: team registration, live leaderboard, and patch-to-score, quiz, jeopardy, and AI challenge…
 fknmega/aether
AI-driven OSINT and security research agent that builds a live knowledge graph from public data, with bundled recon tools and offensive-security…
 the-viper-one/pentest-everything
A collection of CTF write-ups, pentesting topics, guides and notes. Notes compiled from multiple sources and my own lab research. Topics also support…
 spiralbl0ck/blacklotus-z2a-challenge
BlackLotus-Z2A-Challenge, Nothing to see here 4 now , please move along
 josh-blythe/bordair-detector
Two-stage prompt-injection and jailbreak detector: regex gates plus a quantised DeBERTa-v3 ONNX classifier, with image, document, and audio support.…
 ctf-o-matic/capture-the-flag
Helper scripts to remaster Linux Live CD images for the purpose of creating ready to use security wargames with pre-installed vulnerabilities to…
 cyprianatsyor/toolshell-cve-2025-53770-sharepoint-exploit-lab-letsdefend
Step-by-step walkthrough of exploiting CVE-2025-53770 (ToolShell) in a LetsDefend lab, covering RCE, web shell deployment, and incident response…
 reddelexc/hackerone-reports
Curated collection of top HackerOne bug bounty reports organized by vulnerability type and program, with scripts to fetch, deduplicate, and rank…

 cthhhhhh/crushftp-ssti-lfi-proof-of-concept
Proof-of-concept for CVE-2024-4040 (CrushFTP SSTI -> unauthenticated LFI) in a controlled CS443 lab environment - for educational/authorised use only.
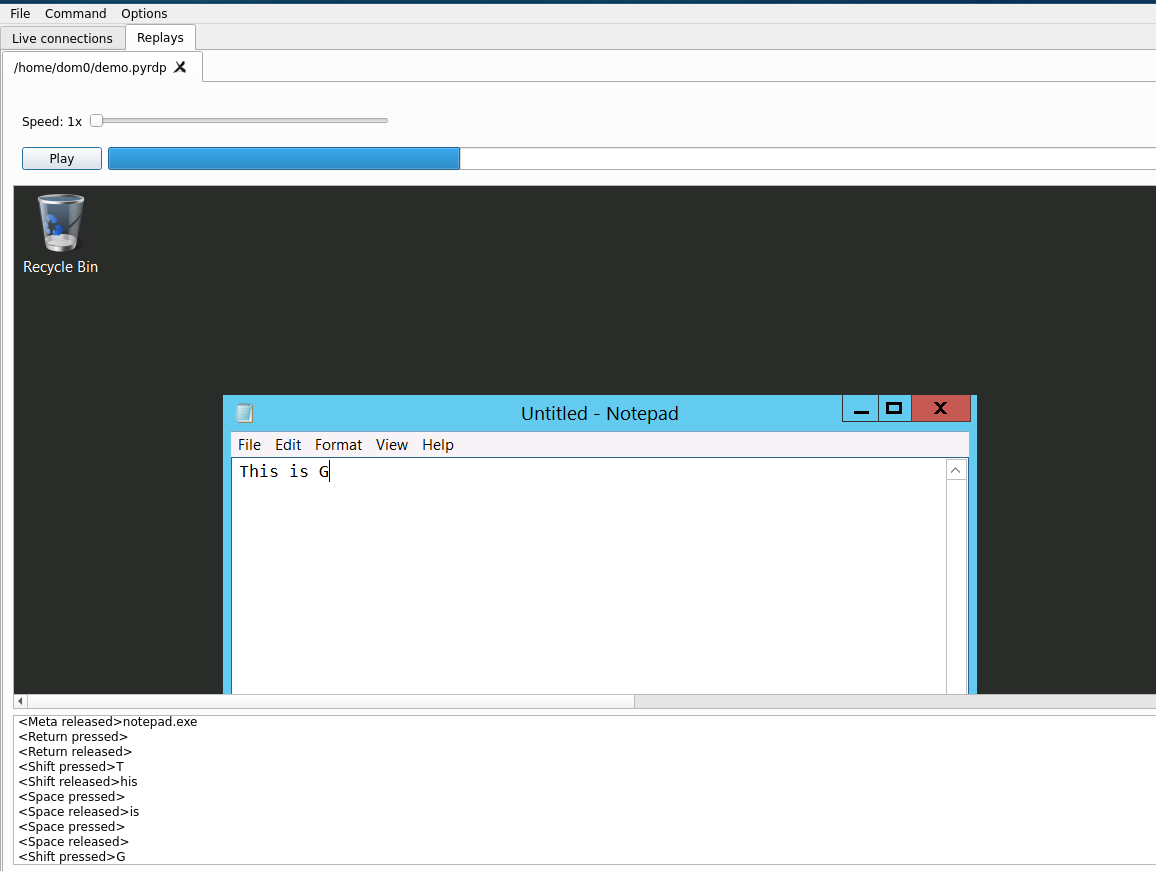 gosecure/pyrdp
RDP monster-in-the-middle (mitm) and library for Python with the ability to watch connections live or after the fact
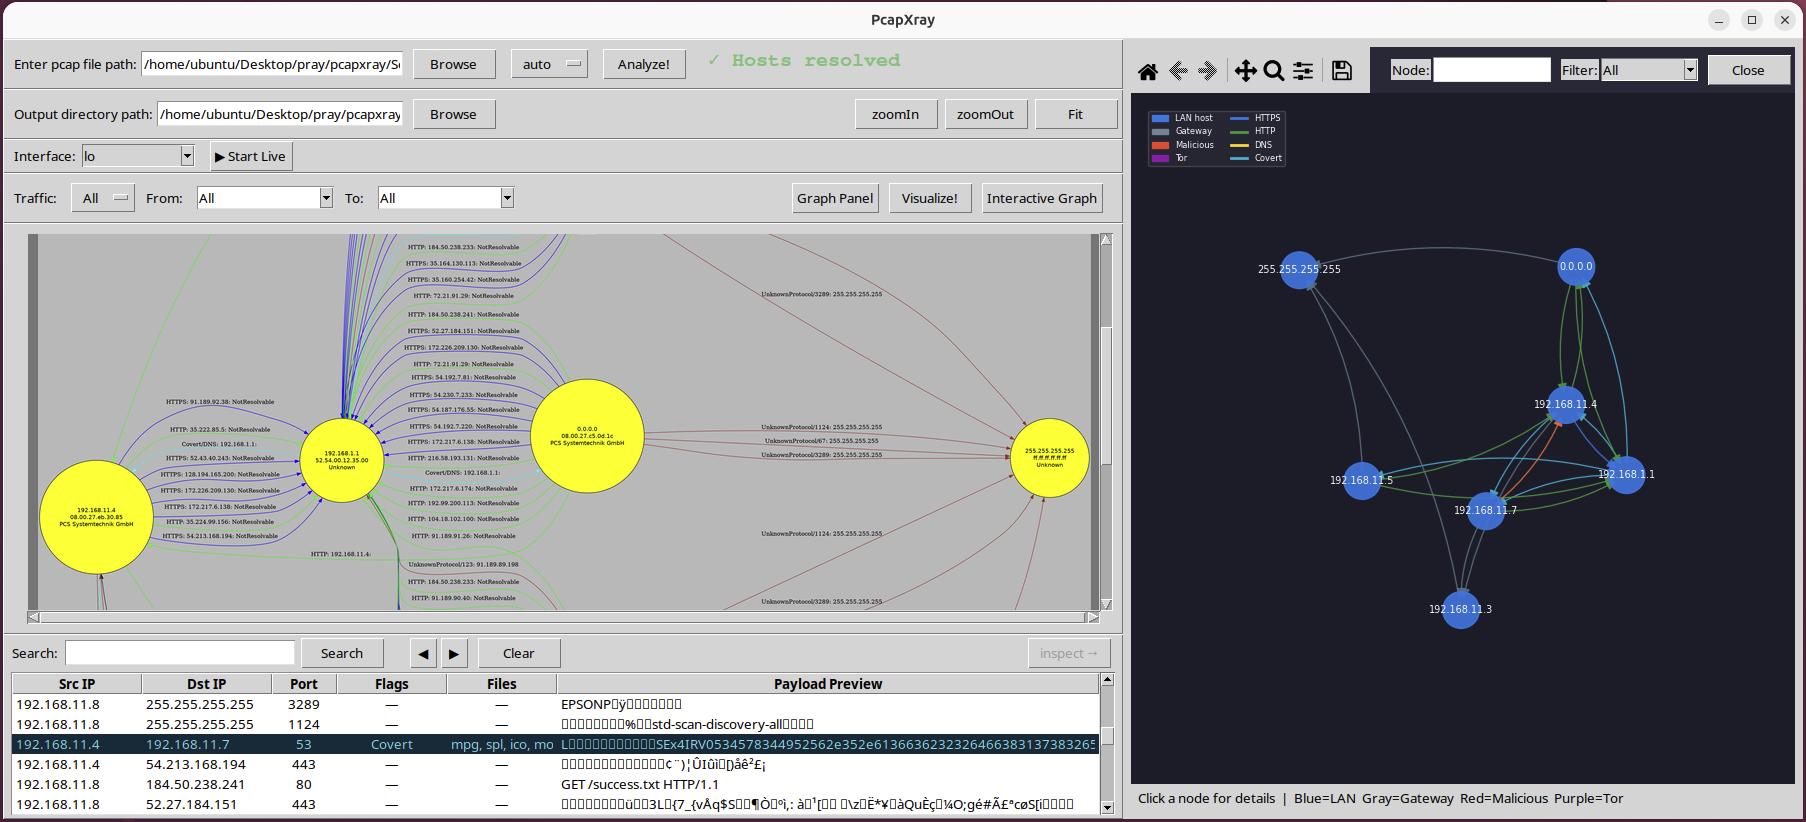 srixivas/pcapxray
❄️ PcapXray - A Network Forensics Tool - To visualize a Packet Capture offline as a Network Diagram including device identification, highlight…