
awesome-osint-arsenal
 rawfilejson/awesome-osint-arsenal
OSINT & recon toolkit // 100+ tools, one-command installer, SOCMINT, GEOINT, network recon, dark web, forensics & more.
ctfcurated-resourcesdigital-forensics+8
1.7k
rawfilejson/awesome-osint-arsenalOSINT & recon toolkit // 100+ tools, one-command installer, SOCMINT, GEOINT, network recon, dark web, forensics & more.
 danielmiessler/seclists
Curated collection of wordlists for security assessments, including usernames, passwords, URLs, fuzzing payloads, and sensitive data patterns for…
 hamed233/cybersecurity-mastery-roadmap
A comprehensive, step-by-step guide to mastering cybersecurity from beginner to expert level with curated resources, tools, and career guidance
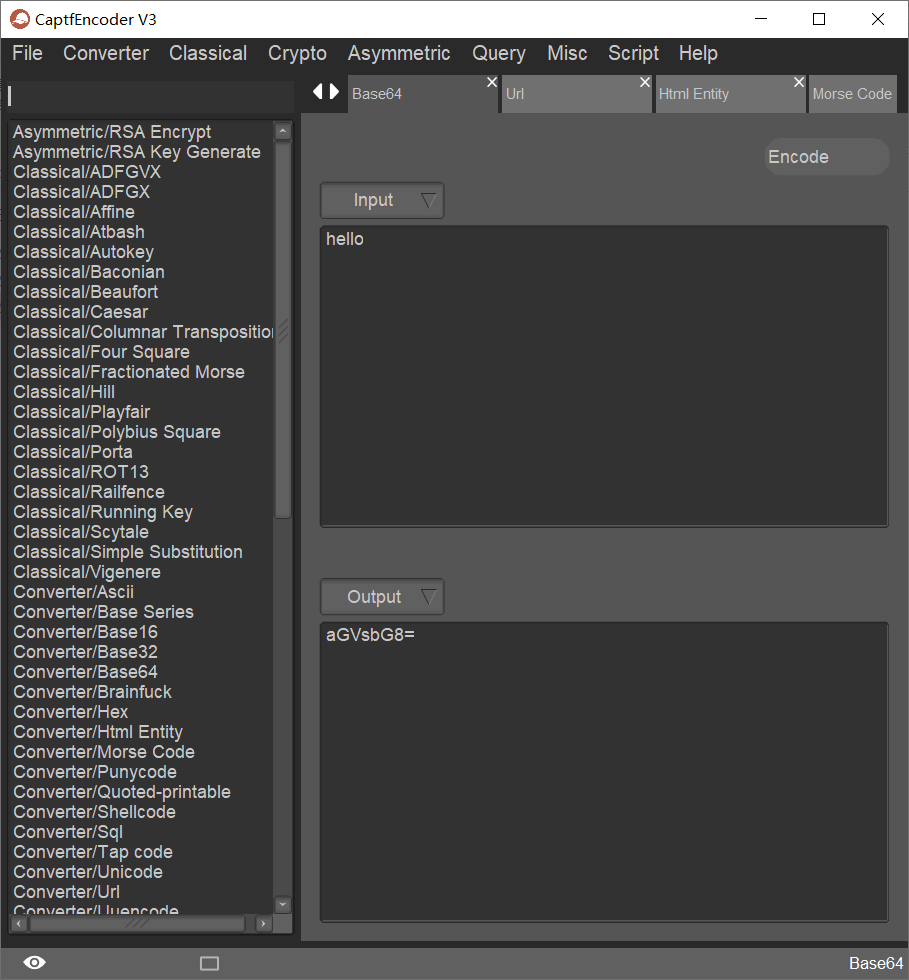 guyoung/captfencoder
Cross-platform security toolkit for encoding, classical and modern cryptography, hash computation, and online reconnaissance queries, designed for…
 six2dez/pentest-book
Curated penetration testing wiki with daily-updated techniques, scripts, and checklists for reconnaissance, web, cloud, mobile, and…
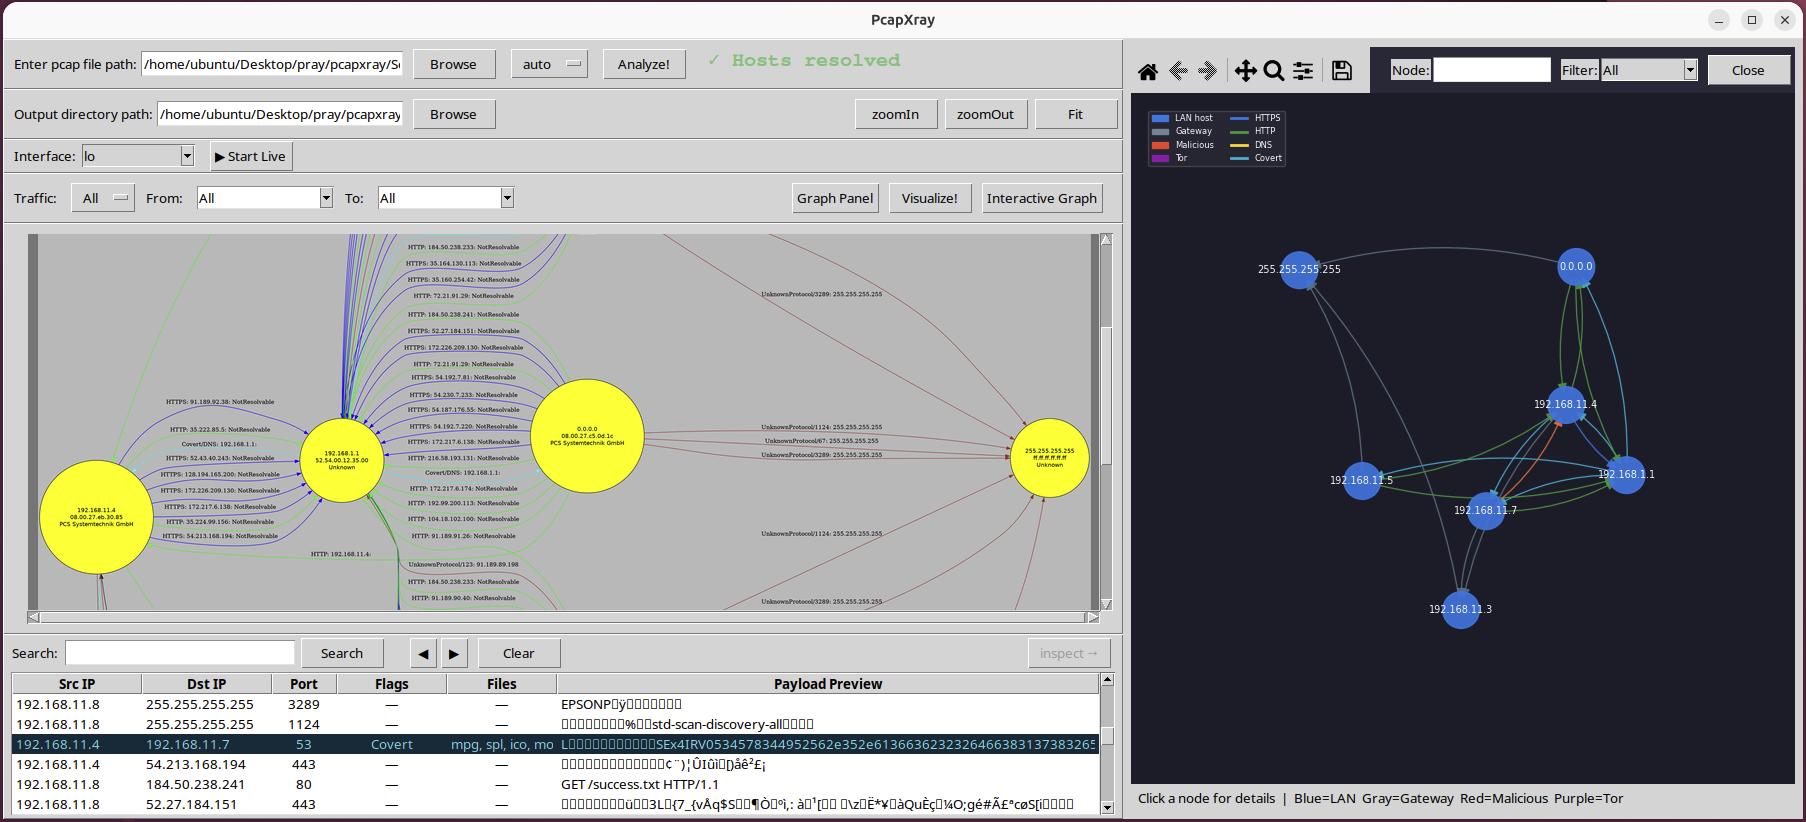 srixivas/pcapxray
❄️ PcapXray - A Network Forensics Tool - To visualize a Packet Capture offline as a Network Diagram including device identification, highlight…
 autorecon/autorecon
Multi-threaded network reconnaissance tool that automates service enumeration, port scanning, and information gathering for penetration testing and…
 daffainfo/allaboutbugbounty
All about bug bounty (bypasses, payloads, and etc)
 ronin-rb/ronin
Ronin is a Free and Open Source Ruby Toolkit for Security Research and Development. Ronin also allows for the rapid development and distribution of…
 rogerzeferino/cve-2019-17558-apache-solr-rce
CTF write-up documenting CVE-2019-17558 exploitation in Apache Solr, covering reconnaissance, Metasploit limitations, manual Velocity template…
 shiva108/waes
CPH:SEC WAES: Web Auto Enum & Scanner - Auto enums website(s) and dumps files as result
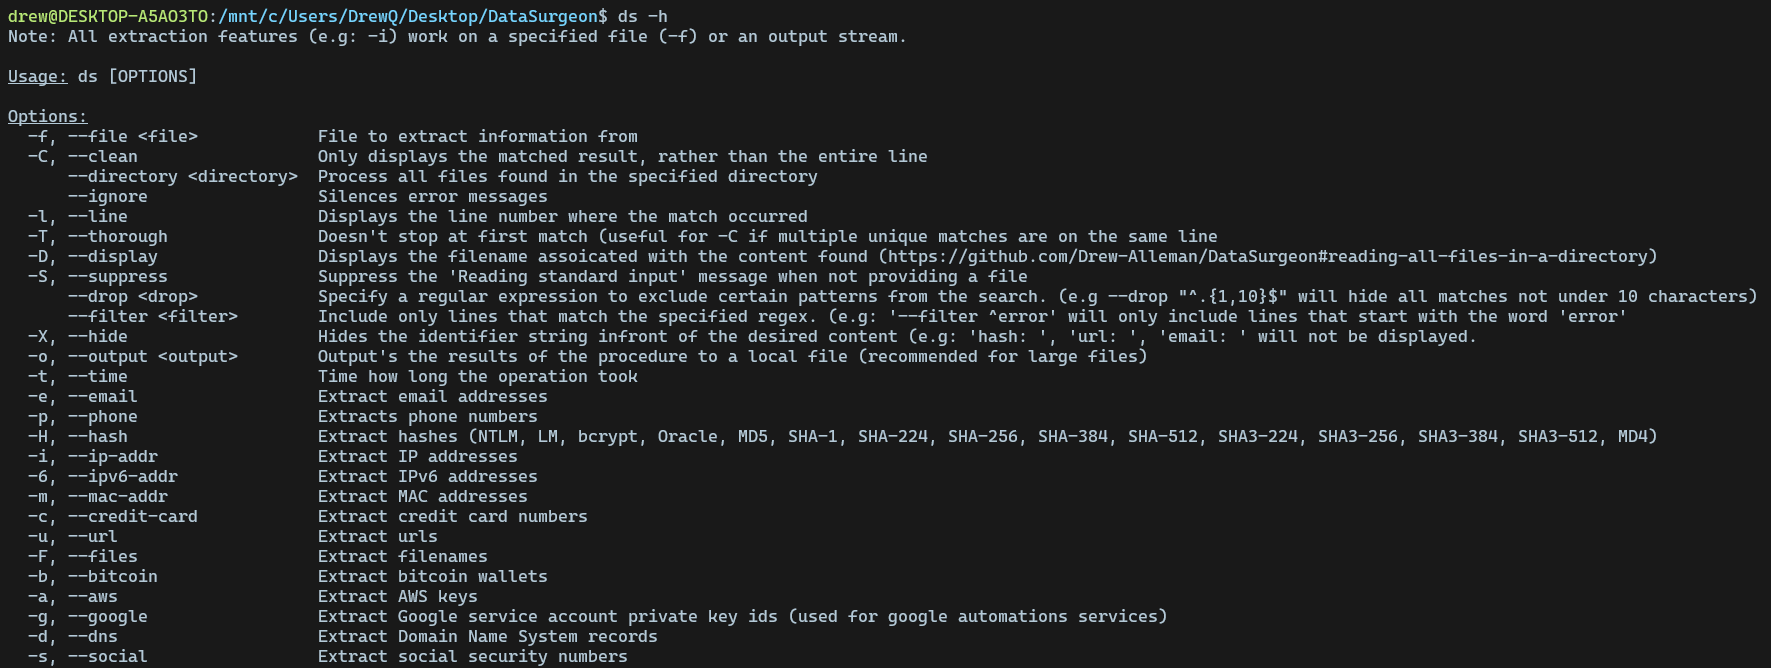 drew-alleman/datasurgeon
Quickly Extracts IP's, Email Addresses, Hashes, Files, Credit Cards, Social Security Numbers and a lot More From Text
 devploit/debughunter
Chrome extension that passively finds debug parameters, sensitive headers and exposed paths (.env, .git, actuator) while you browse. Built for bug…
 knowledge-wisdom-understanding/recon
Enumerate a target Based off of Nmap Results
 zales2004/sunset-noontide-pentesting
Description Professional penetration testing assessment of the Sunset: Noontide VulnHub machine, covering reconnaissance, service enumeration,…
 paulameg/simplectf-thm-walkthrough
First CTF successfully completed! This repo documents my walkthrough of TryHackMe's Simple CTF. It covers network reconnaissance (Nmap), web…
 vanshuk-bhagat/apache-http-server-vulnerabilities-cve-2021-41773-and-cve-2021-42013
In this project, I documented a detailed penetration testing process targeting Apache HTTP Server vulnerabilities, specifically CVE-2021-41773 and…