
Scanning
 aidilzlkfli/scanning
Analysis of network scan results, service vulnerabilities, OS fingerprinting, and critical Nessus findings including Ghostcat (CVE-2020-1938).
ctfeducationexploitation+6
aidilzlkfli/scanningAnalysis of network scan results, service vulnerabilities, OS fingerprinting, and critical Nessus findings including Ghostcat (CVE-2020-1938).
 infoslack/awesome-web-hacking
Curated list of web application security resources including books, tools, cheat sheets, labs, and courses for learning penetration testing and…
 webpwnized/mutillidae
OWASP Mutillidae II is a free, open-source, deliberately vulnerable web application providing a target for web-security training. This is an…
 mmoobbeeiidat-design/hack-the-box-enigma-findings-report
HTB_Enigma Security Assessment – Full pentest completed, chaining NFS disclosure, IMAPS password reuse, and OS Command Injection in OpenSTAManager…
 mmoobbeeiidat-design/hack-the-box-nexus-findings-report
HTB_Nexus Penetration Test Report – Comprehensive security assessment documenting credential leakage from Gitea, CVE-2026-38526 exploitation in…
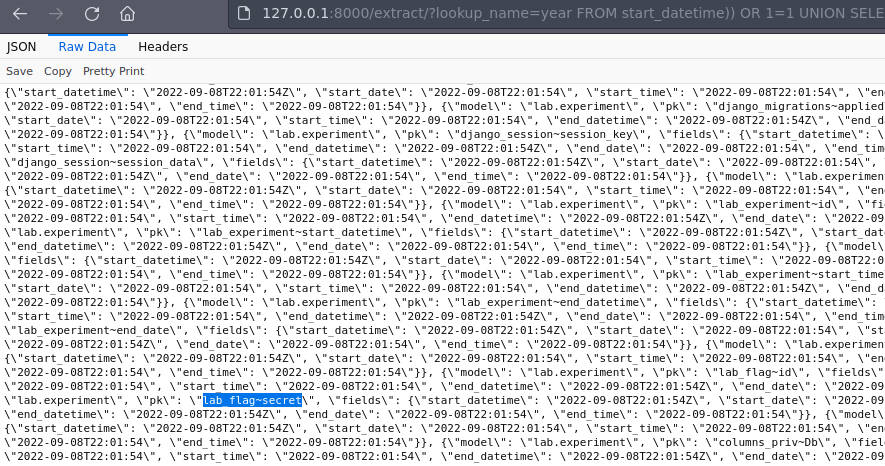 lnwza0x0a/ctf_django_cve-2022-34265
Docker-based CTF challenge demonstrating SQL injection in Django's Trunc() and Extract() database functions (CVE-2022-34265) with UNION-based payload…
 quincyomoruyi6-lang/blue-writeup-cve-2017-0144
Conducted a complete security assessment of an unpatched Windows 7 target ("Blue") to demonstrate the impact of legacy service vulnerabilities in an…
 eljoamy/mongobleed-exploit
MongoBleed (CVE-2025-14847) Lab & PoC : A complete educational environment to reproduce the critical unauthenticated memory leak in MongoDB. Includes…
 zales2004/sunset-noontide-pentesting
Description Professional penetration testing assessment of the Sunset: Noontide VulnHub machine, covering reconnaissance, service enumeration,…
 netw0rk7/cve-2012-2122-home-lab
CVE-2012-2122 MySQL Authentication Bypass Home Lab
 tempuss/ctf_cve-2020-7471
CTF challenge exploiting CVE-2020-7471, a Django SQL injection vulnerability in PostgreSQL StringAgg, with Docker setup and exploit scripts.
 cedric-martz/ethernalblue_report
This is a security assessment report regarding the EthernalBlue vulnerability (CVE-2017-0143).
 gokul-krishnan-v-r/cve-2024-53900
Mongo Vulnub Lab...Try to Hack IT.....!
 chathura123git/ethical-hacking-cve-2011-2523
Ethical Hacking Assessment | Practical vulnerability testing of vsftpd 2.3.4 backdoor (CVE-2011-2523) on Metasploitable2 using Kali Linux & Metasploit
 sho-luv/mongobleed
CVE-2025-14847 (MongoBleed) scanner and exploit tool. Unauthenticated MongoDB heap memory leak via zlib decompression. Detection, memory extraction,…
 nisaruj/nosqli-flintcms
Blind noSQL injection case study lab based on CVE-2018-3783
 andreaf17/poc-cve-2024-44349
Proof-of-concept exploit for CVE-2024-44349, an SQL injection in Anteeo WMS v4.7.x, enabling database dumping and arbitrary SQL query execution.