
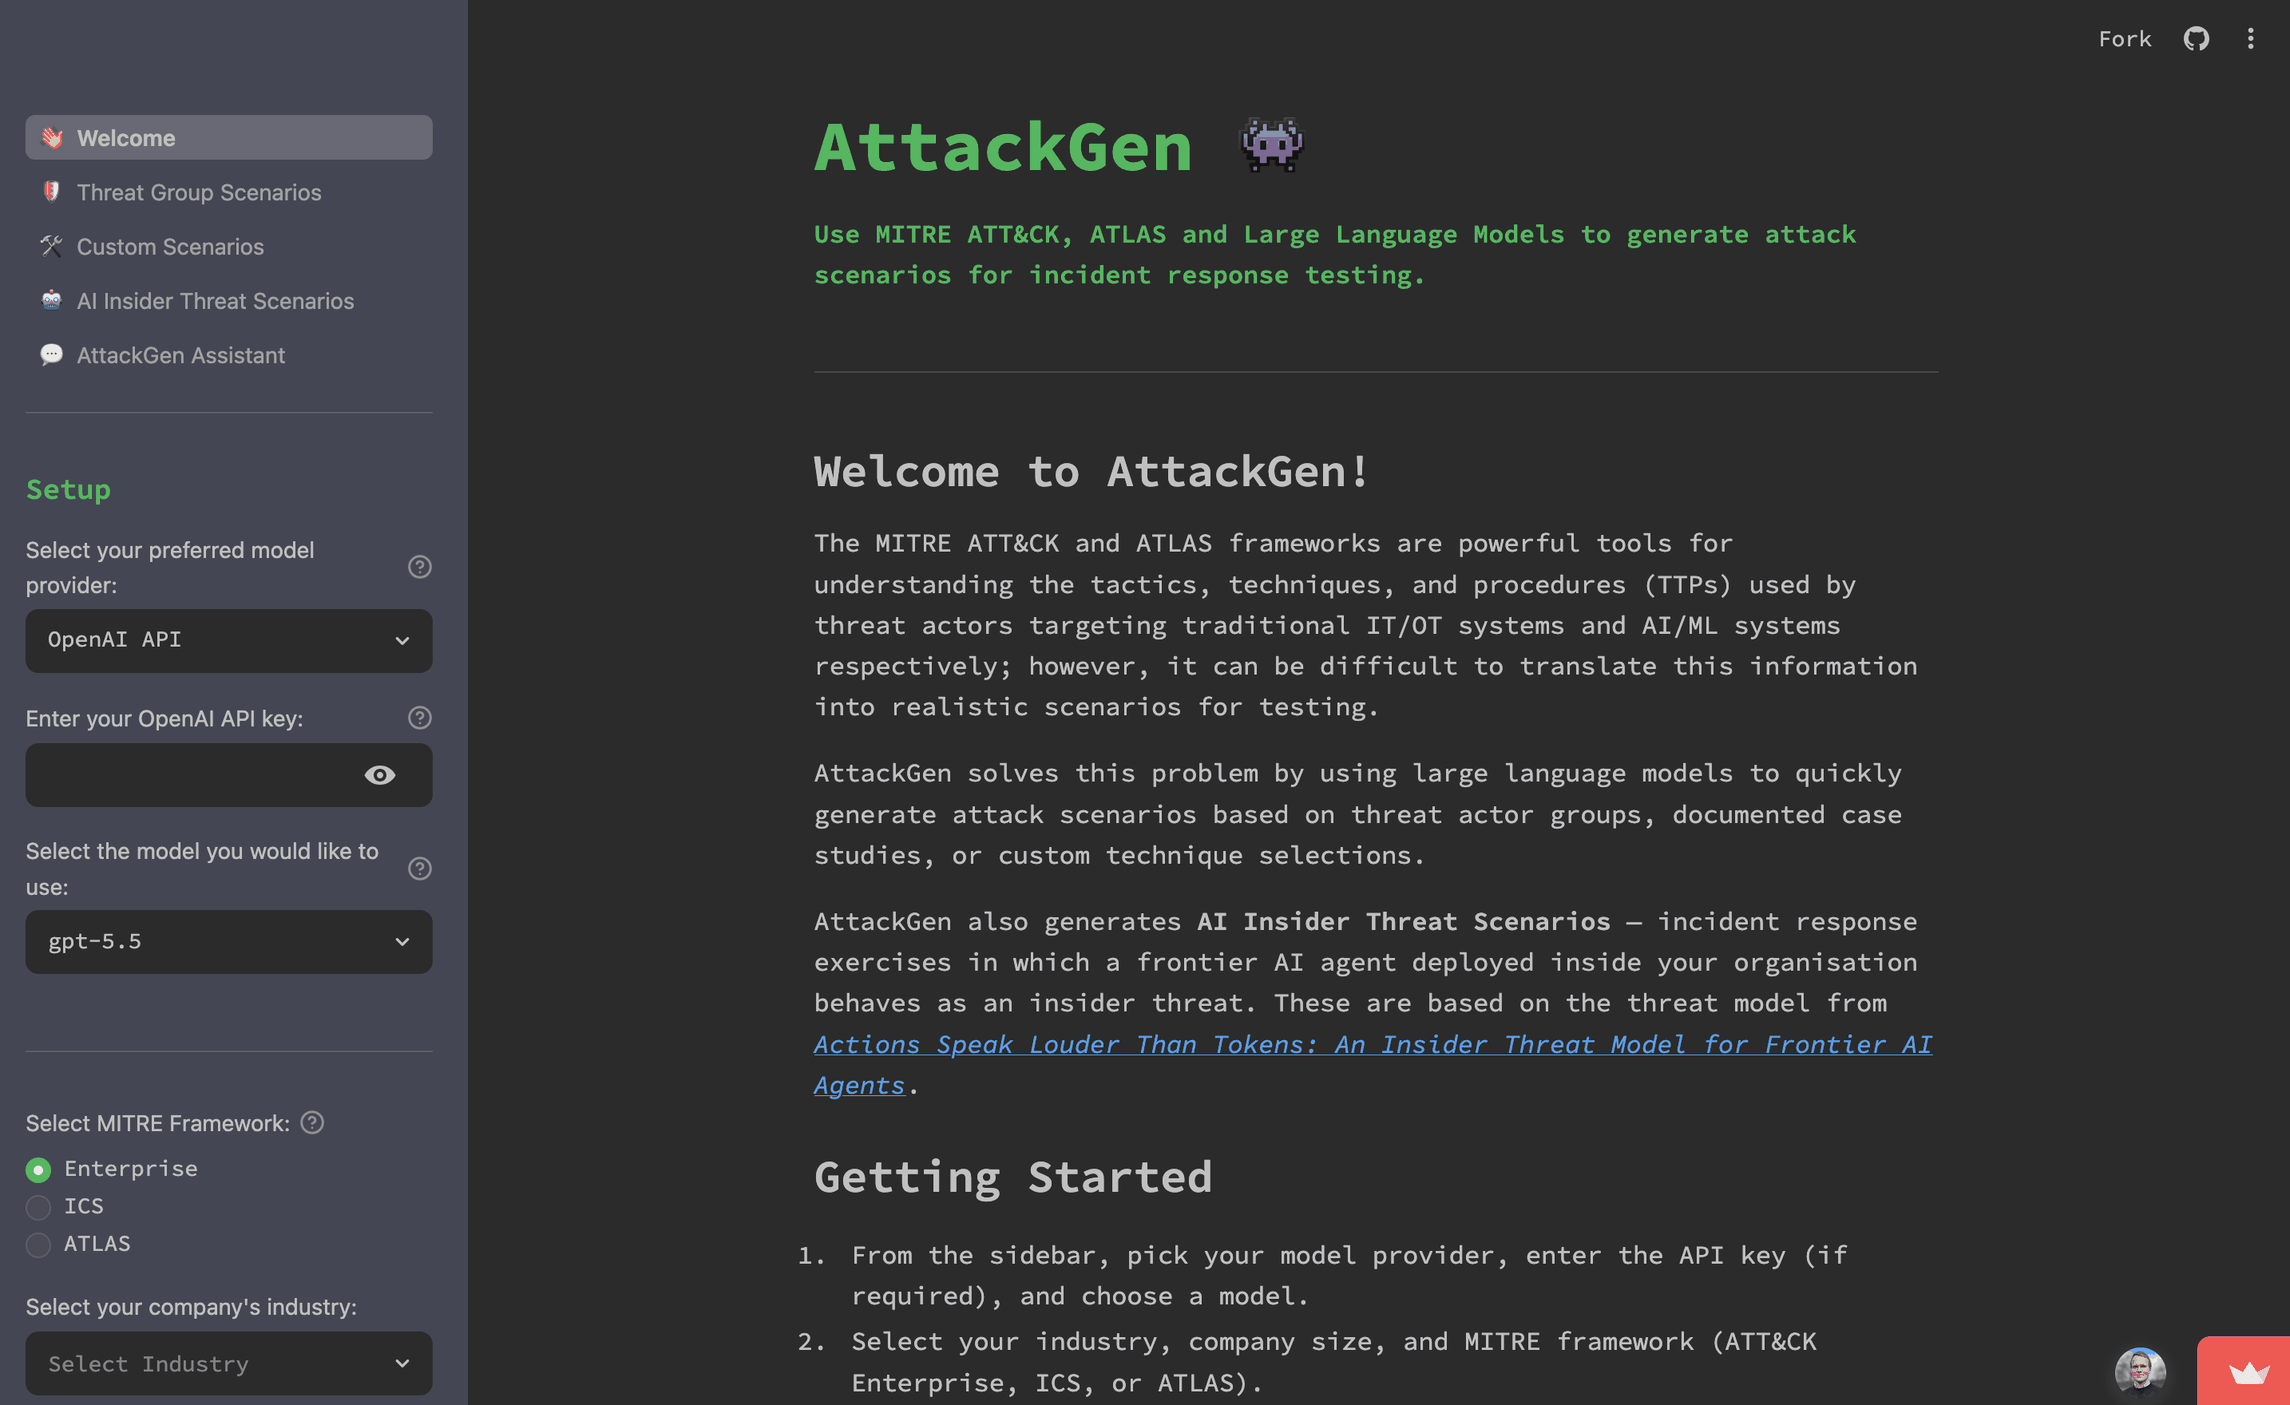
attackgen
 mrwadams/attackgen
AttackGen is a cybersecurity incident response testing tool that leverages the power of large language models and the comprehensive MITRE ATT&CK…
ai-securityctfeducation+5
1.2k
mrwadams/attackgenAttackGen is a cybersecurity incident response testing tool that leverages the power of large language models and the comprehensive MITRE ATT&CK…
 mfthomps/labtainers
Labtainers: A Docker-based cyber lab framework
 eurogig/jankybank
Simple Java Front and Back end with bad log4j version featuring CVE-2021-44228
 agampreet-singh/redroot
RedRoot is a Python-based, CLI-driven offensive security framework that brings essential red teaming tools into one unified terminal environment.…
 b3nac/injuredandroid
A vulnerable Android application that shows simple examples of vulnerabilities in a ctf style.
 sorcerio/code-roulette
Code Roulette is a terminal interface based (TUI), online multiplayer, Russian Roulette game where the loser executes the winner's Python payload…
 hanmin0512/cve-2014-6271_pwnable
Hands-on lab demonstrating the Shellshock (CVE-2014-6271) Bash vulnerability with privilege escalation via environment variable injection, based on…
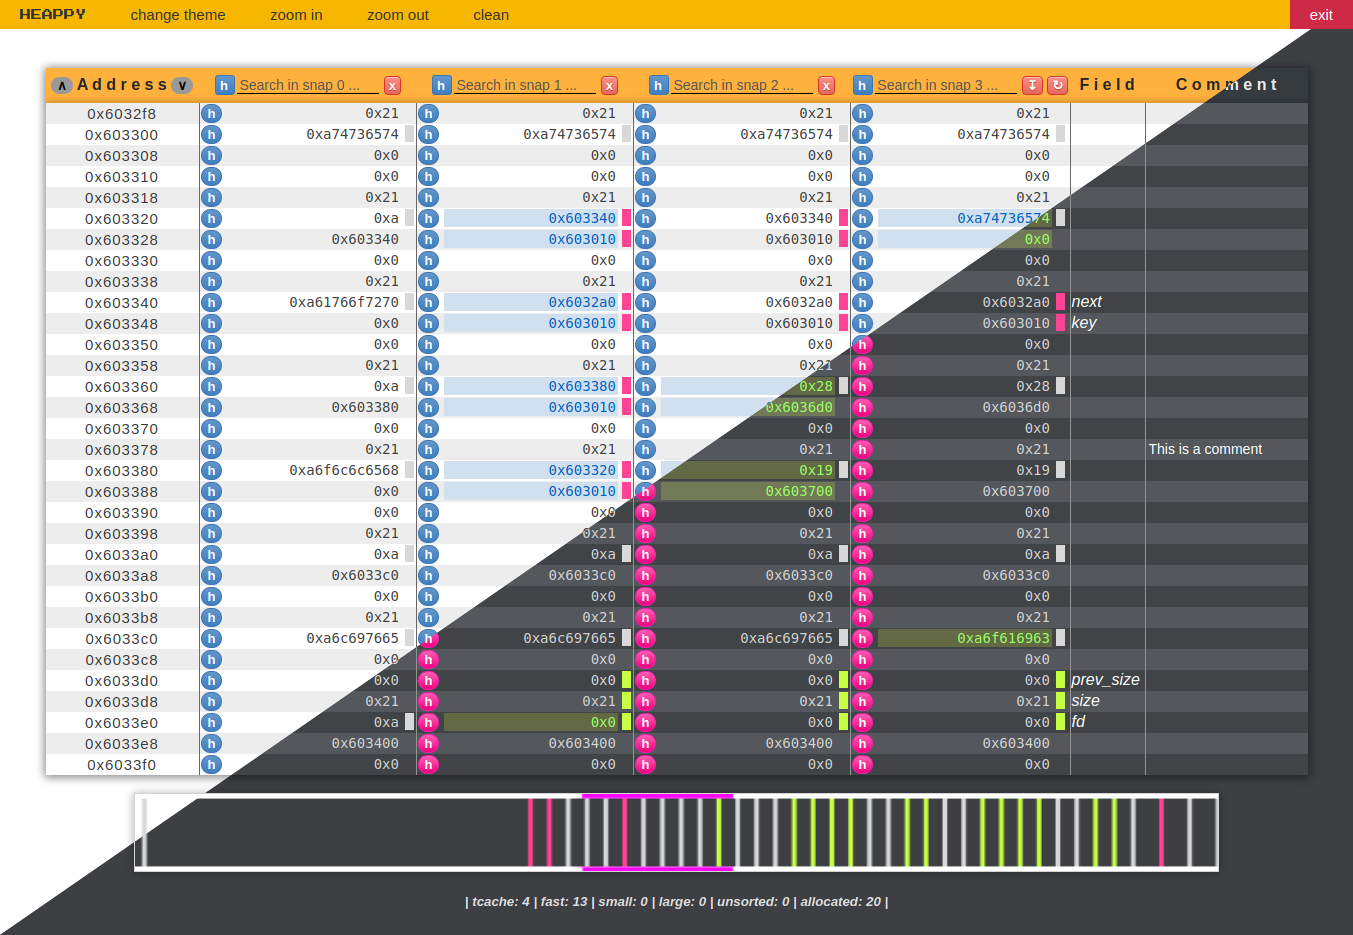 gand3lf/heappy
A happy heap editor to support your exploitation process :slightly_smiling_face:
 shiva108/waes
CPH:SEC WAES: Web Auto Enum & Scanner - Auto enums website(s) and dumps files as result
 inferiorak/cve-2025-55182-react2shell-async-scanner
Async RCE scanner for CVE-2025-55182 / CVE-2025-66478 — prototype-pollution → code execution via React Server Actions.
 gh0stuncle/cve-2018-16763_fuel_cms_exploit
A fuel CMS exploit based on Python for RCE mentioned in CVE-2018-16763.
 knowledge-wisdom-understanding/recon
Enumerate a target Based off of Nmap Results
 silocityit/cve-2021-4034-playground
A hands-on binary exploitation challenge based on CVE-2021-4034, designed for practicing privilege escalation techniques in a controlled environment.
 baktistr/cve-2025-59532-poc
A Docker-based research environment for analyzing CVE-2025-59532, a path traversal vulnerability in OpenAI Codex CLI that allows arbitrary file write…
 flojboj/cve-2021-31630
POC Exploit for CVE-2021-31630 written in Python3 and using C reverse shell with non-blocking mode
 bohemian-miser/cve-2025-65018_exploit_challenge
CTF challenge exploiting a heap overflow in libpng's png_image_finish_read to overwrite a function pointer and spawn a shell, with build scripts and…
 gokul-krishnan-v-r/cve-2024-53900
Mongo Vulnub Lab...Try to Hack IT.....!