
ClaimJumper
 fevra-dev/claimjumper
Professional JWT security testing toolkit. Analyze, crack, forge, and exploit JSON Web Tokens with 15+ vulnerability checks, 100k secret wordlist,…
authenticationcryptographyexploitation+6
1
fevra-dev/claimjumperProfessional JWT security testing toolkit. Analyze, crack, forge, and exploit JSON Web Tokens with 15+ vulnerability checks, 100k secret wordlist,…
 shopify/ssllabs.rb
Ruby client for the Qualys SSL Labs API enabling automated SSL/TLS server assessment, vulnerability detection (e.g., BEAST), and security grade…
 infoslack/awesome-web-hacking
Curated list of web application security resources including books, tools, cheat sheets, labs, and courses for learning penetration testing and…
 aymanelsherif/oracle-oam-authentication-bypas-exploit
Exploit for Oracle Access Manager padding oracle vulnerability (CVE-2018-2879)
 salgio/ewelink-qr-code
This repo describes a vulnerability affecting the QR code based pairing process of the eWeLink IoT devices (CVE-2020-12702).
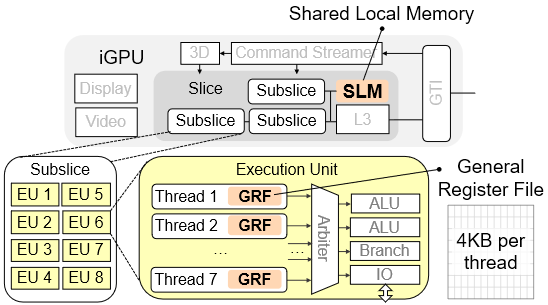 he-wenjian/igpu-leak
[CVE-2019-14615] iGPU Leak: An Information Leakage Vulnerability on Intel Integrated GPU
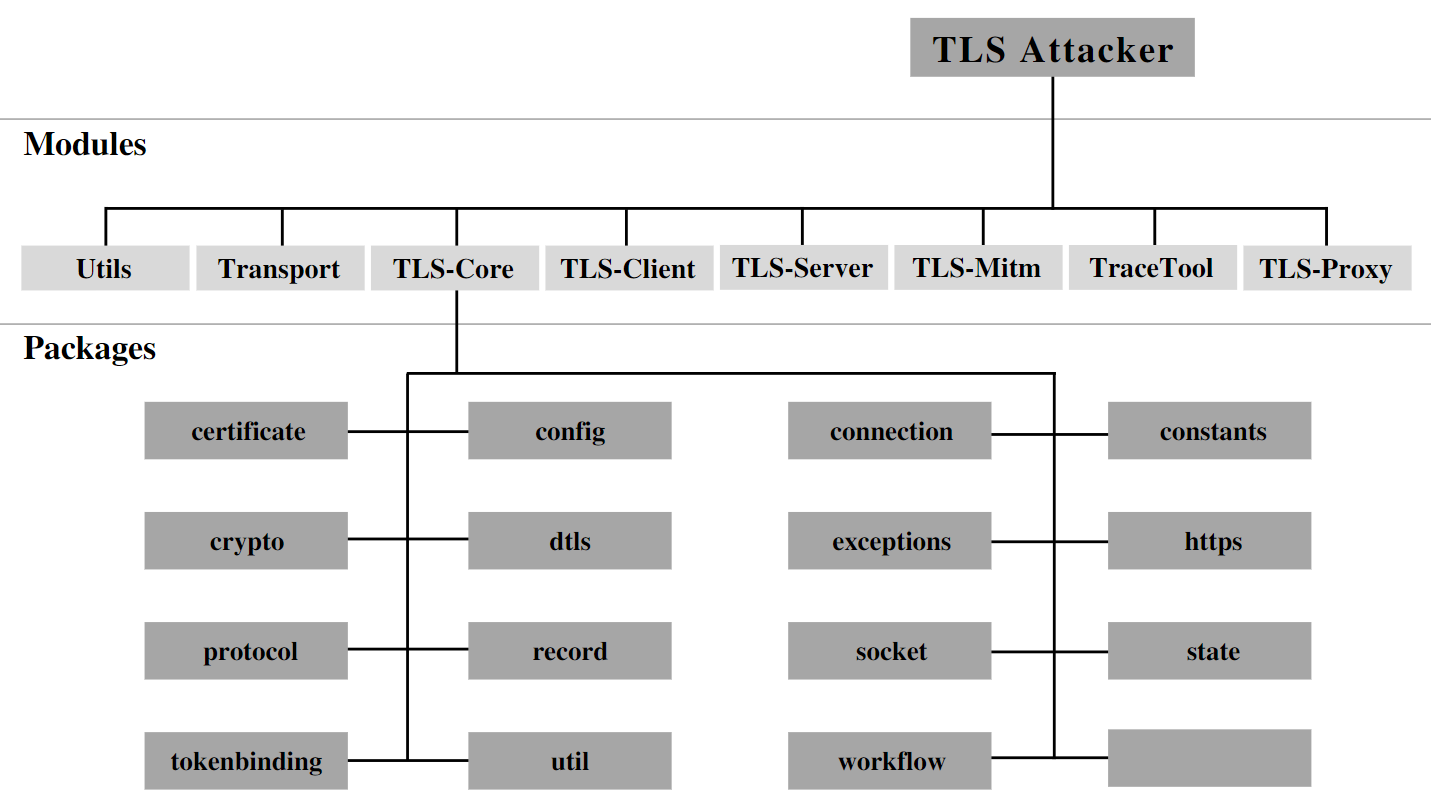 tls-attacker/tls-attacker
Java-based framework for systematic fuzzing and analysis of TLS libraries. Enables arbitrary protocol message crafting, modification, and testing of…
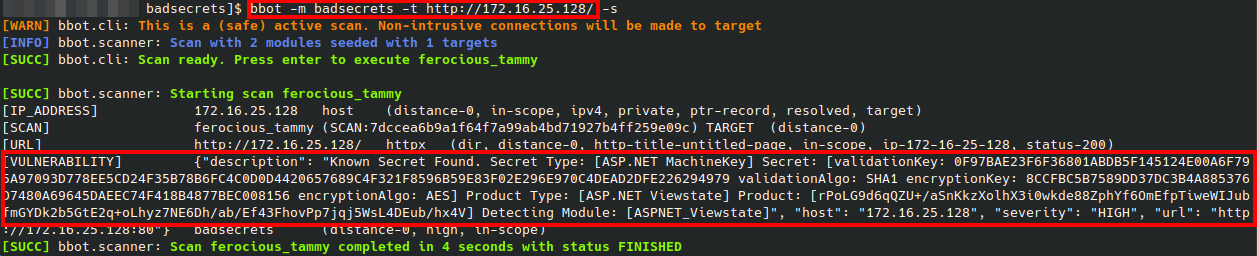 blacklanternsecurity/badsecrets
A library for detecting known secrets across many web frameworks
 iangcarroll/cookiemonster
Decodes and unsigns vulnerable session cookies from Django, Flask, Laravel, Express, and JWT frameworks. Supports HMAC-based decoders, base64…
 jas502n/shiro-721
RememberMe Padding Oracle Vulnerability RCE
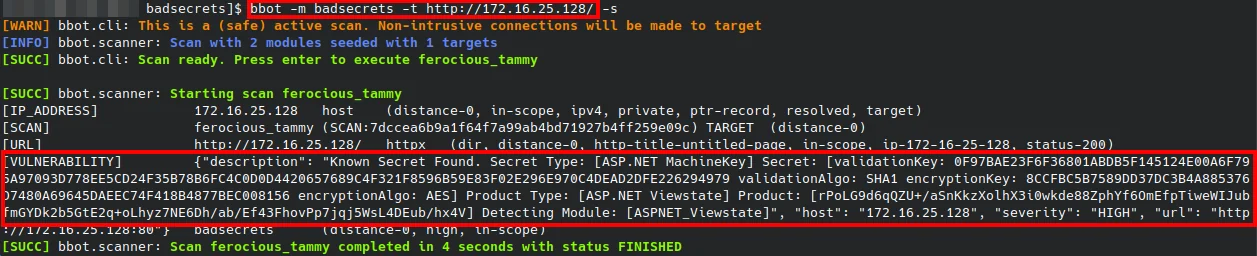 irsdl/crapsecrets
A library for detecting known secrets across many web frameworks
 secretnonempty/cve-2014-0224
Go-based MITM exploit demo for OpenSSL CVE-2014-0224 (CCS Injection) targeting RC4-SHA cipher, with server/client proxy setup for testing TLS…
 alex-seymour/cve-2020-10560-key-recovery
Proof-of-concept exploit that recovers the site_key for OSSN 5.3 and above, exploiting CVE-2020-10560 arbitrary file read vulnerability.
 gogo2464/cve-2024-5124
Exploit for CVE-2024-5124 targeting ChuanhuChatGPT via TLS timing side-channel attack. Uses tlsfuzzer to perform character-by-character credential…
 crims-on/cve-2021-21239
A script to exploit a vulnerability in xmlsec1 where xmlsec ignores loaded public keys
 voorivex/pentest-guide
Penetration tests guide based on OWASP including test cases, resources and examples.
 strozfriedberg/padbuster
Automated script for performing Padding Oracle attacks
 blacklanternsecurity/dp_cryptomg
Another tool for exploiting CVE-2017-9248, a cryptographic weakness in Telerik UI for ASP.NET AJAX dialog handler.