
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
11 results
cookiemonster preview

cookiemonster

GitHubiangcarroll/cookiemonster

Decodes and unsigns vulnerable session cookies from Django, Flask, Laravel, Express, and JWT frameworks. Supports HMAC-based decoders, base64…
cryptographypenetration-testingvulnerability-analysis+1
997
1 year ago
crackerjack preview

crackerjack

GitHubsadreck/crackerjack

Web-based GUI for Hashcat that simplifies password cracking with session management, mask generation, wordlist support, and multi-user access.

cryptographyhash-analysispassword-cracking+3
641 year ago
CovenantDecryptor preview

CovenantDecryptor

GitHubnaacbin/covenantdecryptor

Decrypts Covenant C2 communications by extracting RSA private keys from minidumps, recovering AES session keys, and converting network captures to…
command-and-controlcryptographydigital-forensics+4
372 years ago
Loracrack preview

Loracrack

GitHubapplied-risk/loracrack

LoRaWAN session cracker - A PoC for exploiting weak or shared Application Keys
cryptographyexploitationhardware-iot-security+3
204 years ago
CVE-2026-61500 preview

CVE-2026-61500

GitHubaramosf/cve-2026-61500

Python PoC and Docker lab for CVE-2026-61500: recovers Rejetto HFS V8 PRNG state to forge an admin session cookie and achieve RCE via server_code.
cryptographyeducationexploitation+7
12 days ago
CVE-2026-2005 preview

CVE-2026-2005

GitHubm3str3/cve-2026-2005

Proof-of-concept exploit for CVE-2026-2005, a heap buffer overflow in PostgreSQL pgcrypto's pgp_pub_decrypt, demonstrating oversized PGP session key…

binary-exploitationcryptographydatabase-security+2
7 months ago
apache__shiro_CVE-2023-34478_1-11-0 preview

apache__shiro_CVE-2023-34478_1-11-0

GitHubshoucheng3/apache__shiro_cve-2023-34478_1-11-0

Java security framework providing authentication, authorization, cryptography, and session management APIs to secure any application from mobile to…
authentication-authorizationcryptographyweb-security
1 year ago
details-for-CVE-2022-46505 preview

details-for-CVE-2022-46505

GitHubsmalltown123/details-for-cve-2022-46505

MatrixSSL session resume bug
binary-analysiscryptographyeducation+2
3 years ago
bleeding-heart preview

bleeding-heart

GitHubpierceoneill/bleeding-heart

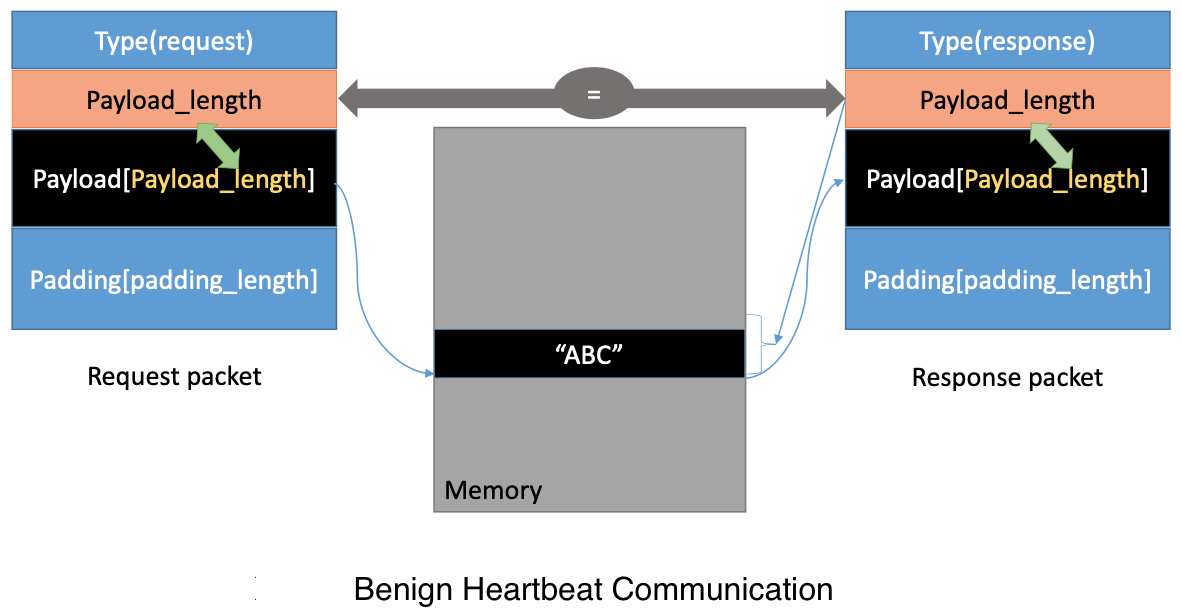
The Heartbleed bug `CVE-2014-0160` is a severe implementation flaw in the OpenSSL library, which enables attackers to steal data from the memory of…
cryptographyeducationexploitation+3
5 years ago
tetsuo-pulse preview

tetsuo-pulse

GitHub7etsuo/tetsuo-pulse

Tetsuo Socket Library

api-securitycryptographydns-analysis+6
707 months ago
DeadDialect preview

DeadDialect

GitHubengrbilal992/deaddialect

A session-unique RISC-V ISA — every boot speaks a different dialect. Old binaries become invalid. Malware cannot persist.

binary-analysiscryptographydefensive-tools+7
65 months ago