ephemera
 qarait/ephemera
Zero-Trust SSH CA
authentication-authorizationcloud-infrastructure-securityconfiguration-auditing+6
qarait/ephemeraZero-Trust SSH CA
 c0r0n3r/dheater
Proof-of-concept denial-of-service tool that exploits the DHEat attack (CVE-2002-20001) by enforcing Diffie-Hellman key exchange against TLS and SSH…
 dheatattack/dheater
Proof-of-concept denial-of-service tool that enforces Diffie-Hellman ephemeral key exchange over TLS and SSH to saturate server CPU, implementing…
 kabiri-labs/sshfinder
Parallel SSH service discovery and security auditor that scans any port, validates SSH banners, and audits authentication methods, weak cryptography,…
 coroner/cryptolyzer
Multi-protocol cryptographic analyzer auditing TLS, SSL, SSH, IKE, DNSSEC, and HTTP security headers. Detects 400+ cipher suites, generates JA3/HASSH…
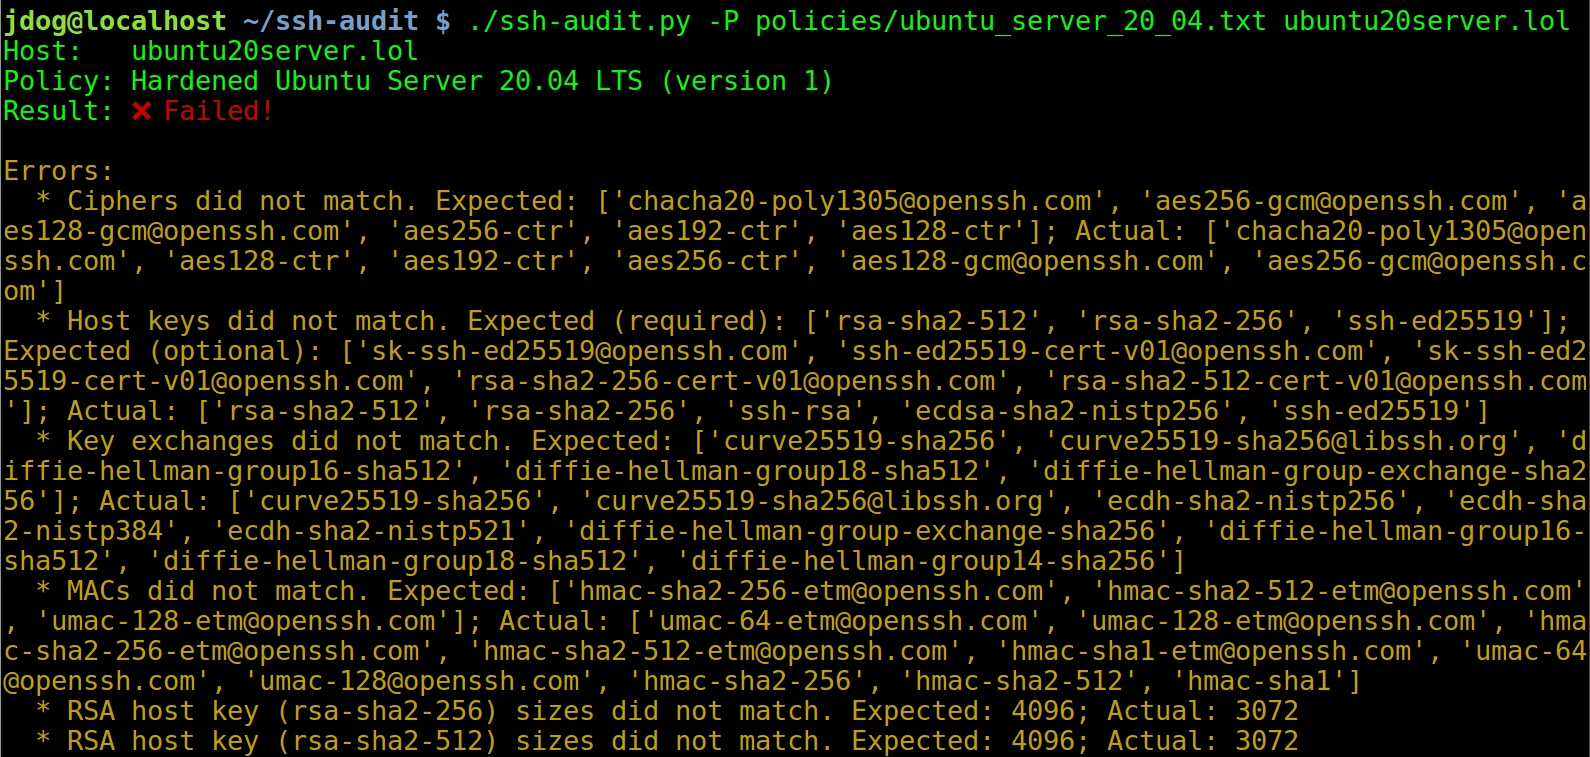 jtesta/ssh-audit
SSH server & client security auditing (banner, key exchange, encryption, mac, compression, compatibility, security, etc)
 ledksv/principal-hackthebox
Detailed walkthrough of exploiting CVE-2026-29000 in pac4j-jwt to bypass authentication, extract credentials from API settings, and escalate…
 strozfriedberg/ssh-weak-dh
Audits SSH servers for weak Diffie-Hellman key exchange groups by testing multiple client configurations, identifying Logjam-vulnerable endpoints…
 shoucheng3/apache__mina-sshd_cve-2023-35887_2-9-2
Pure Java SSH client/server library implementing SSH-2 protocol with support for multiple ciphers, key exchanges, authentication methods, SFTP, SCP,…
 libssh/libssh-mirror
C library implementing the SSH protocol for secure remote access, authentication, and encrypted communication. Includes fuzzing support via OSS-Fuzz…
 alexmullins/dsa
Analysis of CVE-2016-3959 and a Proof of Concept Attack Against a Go SSH Server.
 openssh/openssh-portable
Portable OpenSSH
 sanmilie/pkcs11sshagent
SRO PKCS11 – SSH Agent CNG est un agent Windows souverain, ultra‑léger et zéro‑dépendance qui unifie PKCS#11, SSH-agent, Pageant et CNG/Smartcard…
 jaarden/cve-2024-22894
Proof-of-concept exploit for CVE-2024-22894, demonstrating 3DES-encrypted root password extraction from Alpha Innotec/Novelan heatpump firmware,…
 cybervinner/tp-link-tl-wr820n-cve-2025-14175
Responsible disclosure write-up for CVE-2025-14175 involving weak cryptographic algorithm support in the SSH server of TP-Link TL-WR820N.