
sslscan
 rbsec/sslscan
Fast SSL/TLS scanner that discovers supported cipher suites, protocols, and vulnerabilities (Heartbleed, POODLE, CRIME) with certificate chain…
cryptographynetwork-securityvulnerability-scanners
rbsec/sslscanFast SSL/TLS scanner that discovers supported cipher suites, protocols, and vulnerabilities (Heartbleed, POODLE, CRIME) with certificate chain…
 smxlabs/lamma-beta
Vulnerability Assessment and Auditing Framework for all the Crypto Implementations.
 shopify/ssllabs.rb
Ruby client for the Qualys SSL Labs API enabling automated SSL/TLS server assessment, vulnerability detection (e.g., BEAST), and security grade…
 coroner/cryptolyzer
Multi-protocol cryptographic analyzer auditing TLS, SSL, SSH, IKE, DNSSEC, and HTTP security headers. Detects 400+ cipher suites, generates JA3/HASSH…
 nsacyber/detect-cve-2017-15361-tpm
Detects Windows and Linux systems with enabled Trusted Platform Modules (TPM) vulnerable to CVE-2017-15361. #nsacyber
 codingo/minesweeper
A Burpsuite plugin (BApp) to aid in the detection of scripts being loaded from over 23000 malicious cryptocurrency mining domains (cryptojacking).
 0sec-labs/foxguard
A fast universal code security scanner, written in Rust. Batteries included: supports 14 languages, TUI for triage, secrets, post-quantum audits,…
 nationwide-group-oss/cryptoptic
CodeQL-based scanner that inventories cryptographic function calls across repositories and GitHub organizations, producing a Cryptographic Bill of…
 getsops/sops
Simple and flexible tool for managing secrets
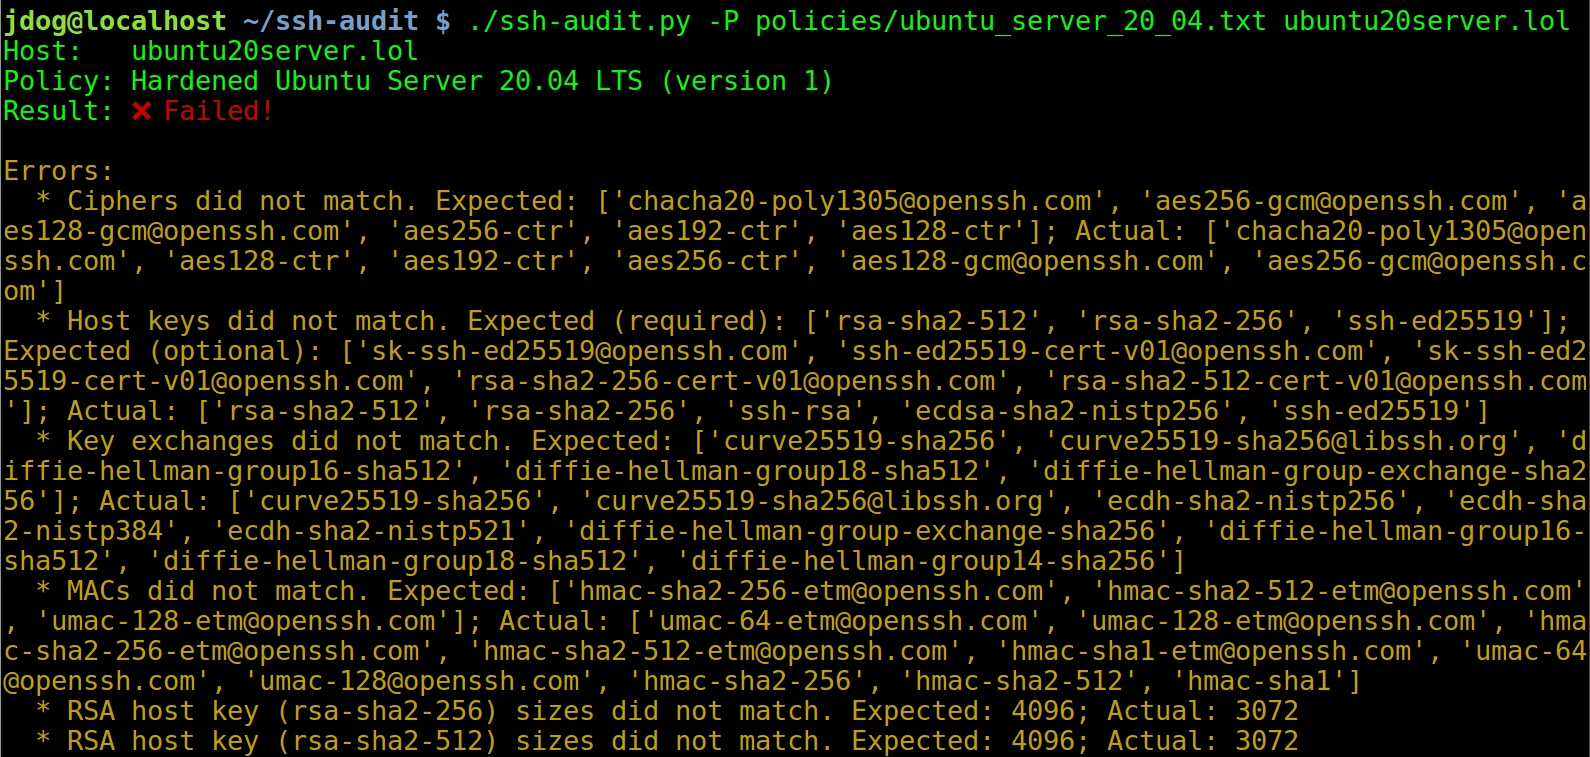 jtesta/ssh-audit
SSH server & client security auditing (banner, key exchange, encryption, mac, compression, compatibility, security, etc)
 mozilla/cipherscan
A very simple way to find out which SSL ciphersuites are supported by a target.
 dnsviz/dnsviz
Analyzes DNS delegation and DNSSEC security by probing resolvers and authoritative servers, then validating, diagnosing, and visualizing zone…
 noxxi/p5-ssl-tools
Perl scripts for SSL/TLS analysis: check protocol and cipher support, verify certificates, test OCSP, and detect Heartbleed across SMTP, HTTPS, and…
 owasp/openshield
Open source CSPM for Azure - scan for misconfigurations and quantum-unsafe cryptography, map findings to CIS/NIST/ISO27001/SOC2, and fix them with…
 nicmx/fort-validator
RPKI Relying Party and RTR server that validates BGP route origin authorizations and serves validated data to routers over the RTR protocol.
 owasp/tcasvs
OWASP Thick Client Application Security Verification Standard
 jas502n/database-spring-enc
sprint encode (plan text) get enc password
 rclone/passwordcheck
Check rclone config files for insecure passwords