
MemoryMapper
 jasondrawdy/memorymapper
Lightweight library which allows the ability to map both native and managed assemblies into memory by either using process injection of a process…
binary-analysiscryptographyexploitation+1
33
jasondrawdy/memorymapperLightweight library which allows the ability to map both native and managed assemblies into memory by either using process injection of a process…
 keepassxreboot/keepassxc
Secure offline storage of credentials with encrypted vaults, password generator, TOTP, YubiKey/OnlyKey support, browser integration, and CLI.
 kudelskisecurity/chainoffools
Proof-of-concept exploit for CVE-2020-0601 Windows CryptoAPI spoofing vulnerability, demonstrating rogue CA certificate generation using elliptic…
 ly4k/curveball
PoC for CVE-2020-0601- Windows CryptoAPI (Crypt32.dll)
 x86byte/obfusk8
Obfusk8: lightweight Obfuscation library based on C++17 / Header Only for windows binaries
 joshuakasa/van-gonography
Hide 🕵️♂️ your files of any type inside a image of your choice using steganography
 shardianlabs/ephemeralnet
A secure, decentralized P2P ephemeral network in C++. Features a custom DHT, encrypted transport, and autonomous NAT traversal using high-performance…
 7thsamurai/steganography
Simple C++ Image Steganography tool to encrypt and hide files inside images using Least-Significant-Bit encoding.
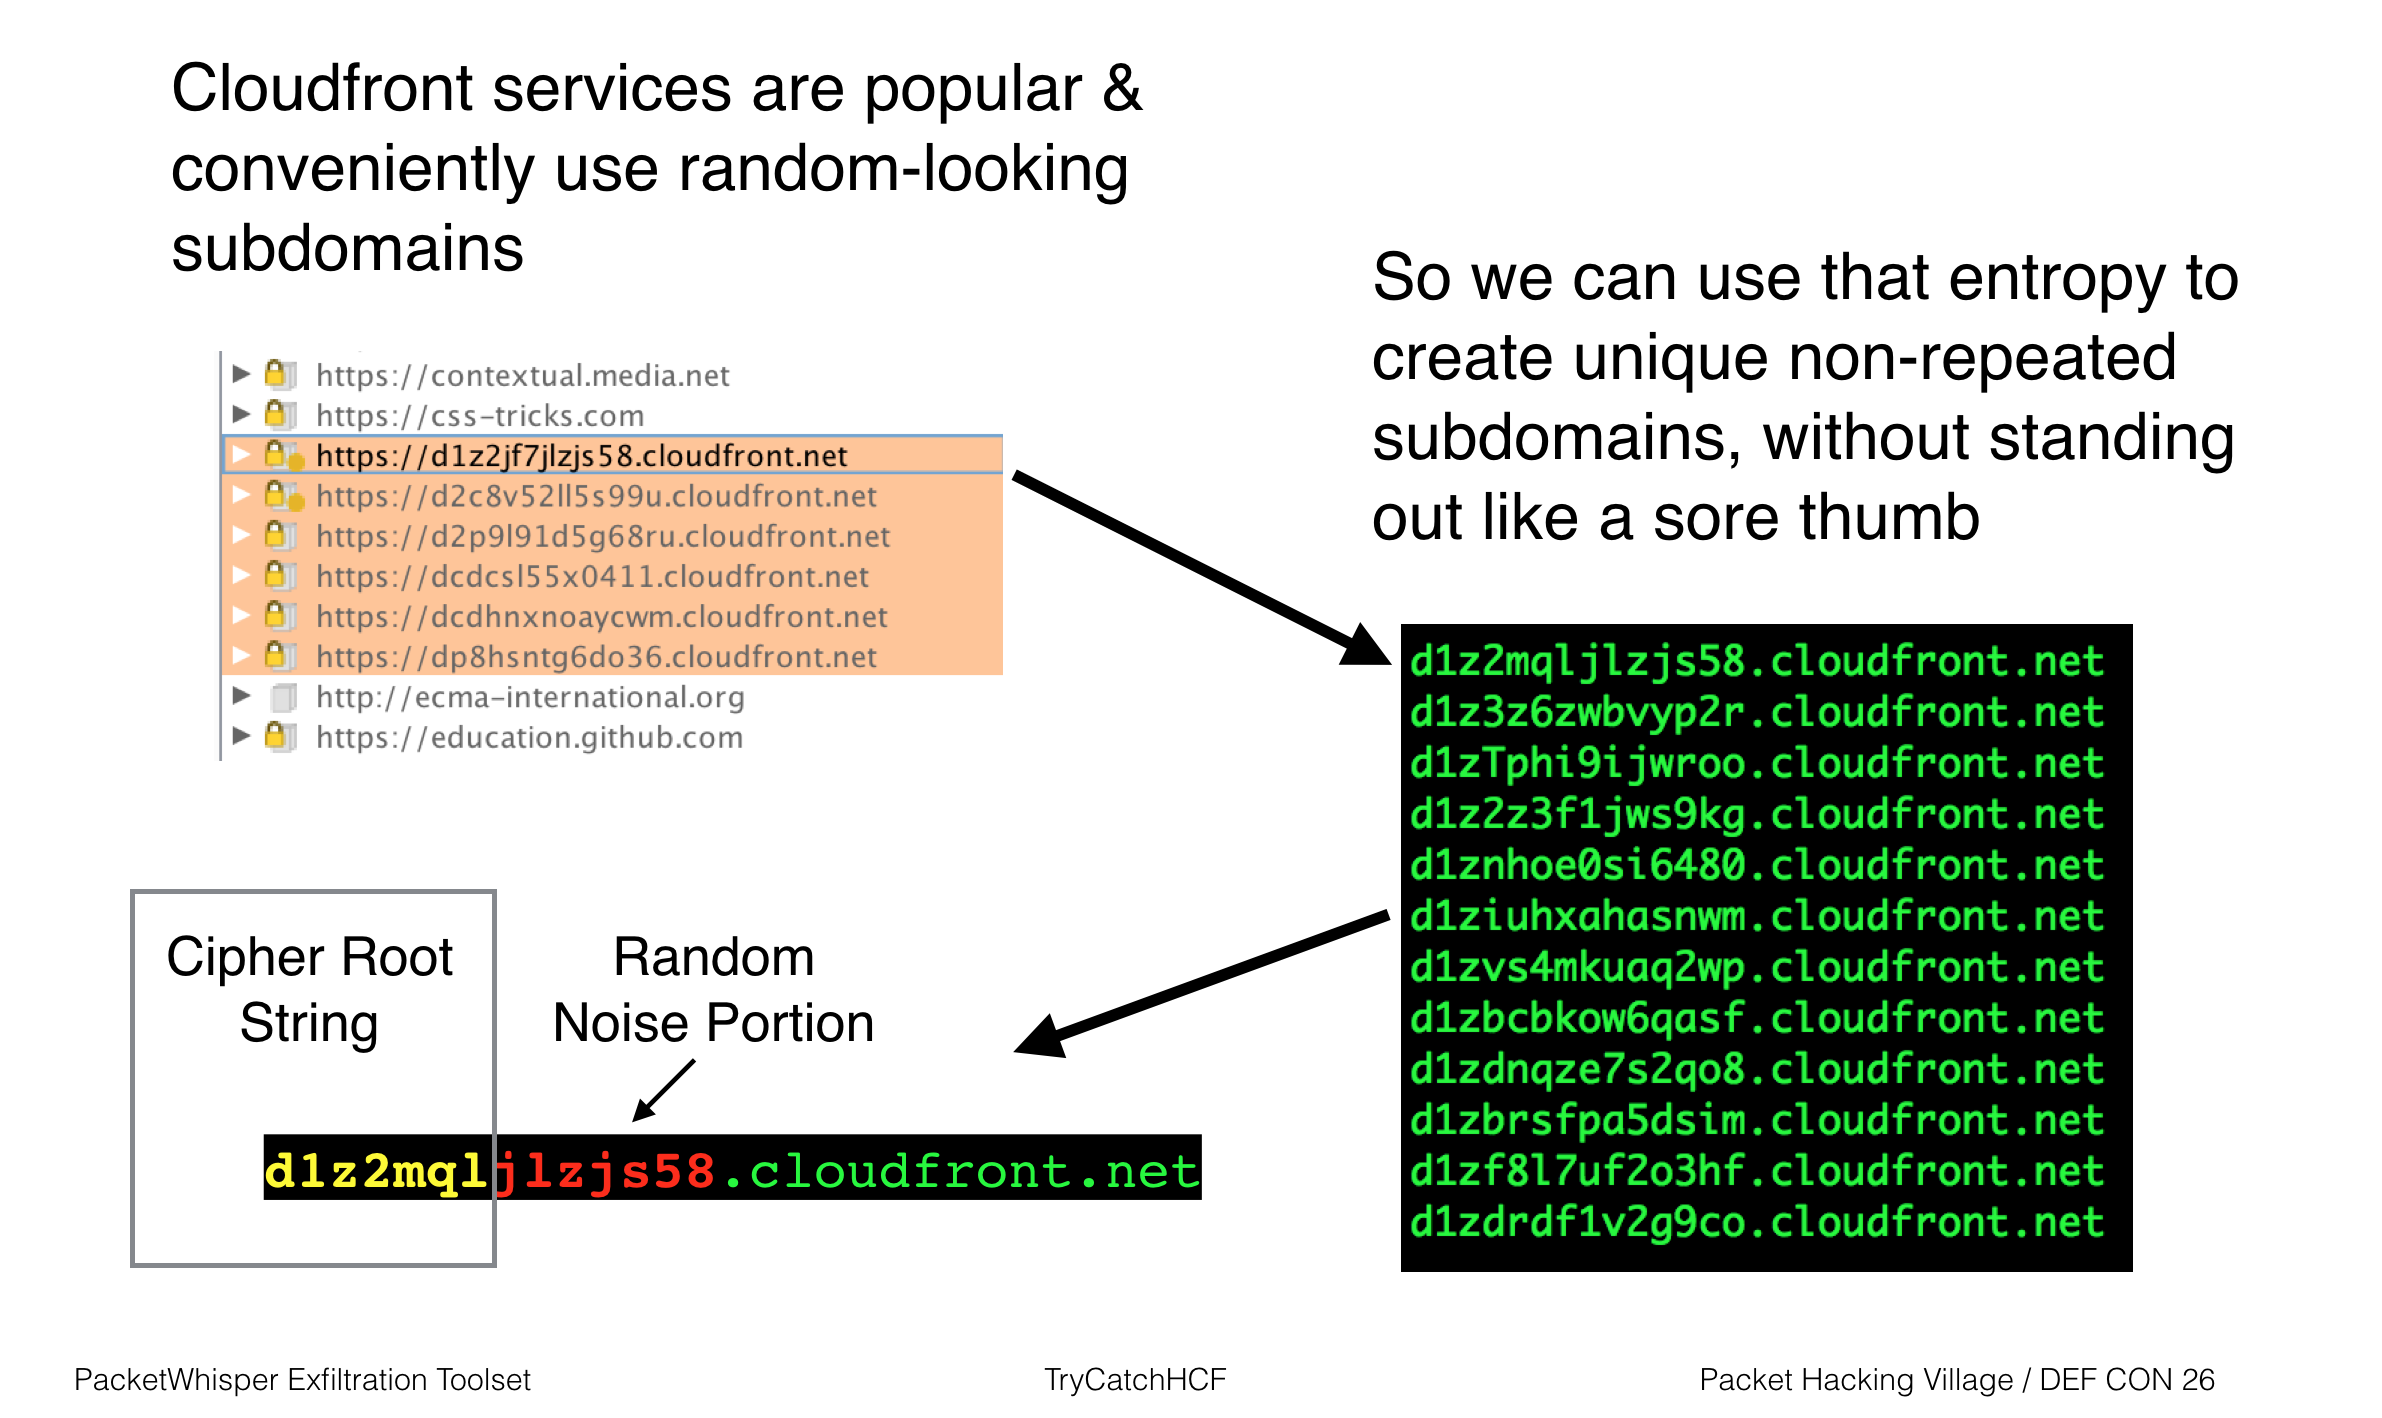 trycatchhcf/packetwhisper
PacketWhisper: Stealthily exfiltrate data and defeat attribution using DNS queries and text-based steganography. Avoid the problems associated with…
 lmatteis/peer-tweet
Decentralized feeds using BitTorrent's DHT. Idea from Arvid and The_8472 "DHT RSS feeds" http://libtorrent.org/dht_rss.html
 bedrock-safeguard/gentlemen-decryptor
First-ever decryptor for The Gentlemen ransomware — recovers encryption keys from process memory dumps using X25519 ephemeral key extraction. 35/35…
 mimi89999/webauthn_tpm_portable
Portable, hardware-backed WebAuthn credentials using TPM 2.0. Deterministic parent key derived from a master seed enables cross-device credential…
 iiictech/-cve-2020-0601-ecc---exploit
CurveBall (CVE-2020-0601) - PoC CVE-2020-0601, or commonly referred to as CurveBall, is a vulnerability in which the signature of certificates using…
 lva/infineon-cve-2017-15361
Simple PowerShell script to check whether a computer is using an Infineon TPM chip that is vulnerable to CVE-2017-15361.
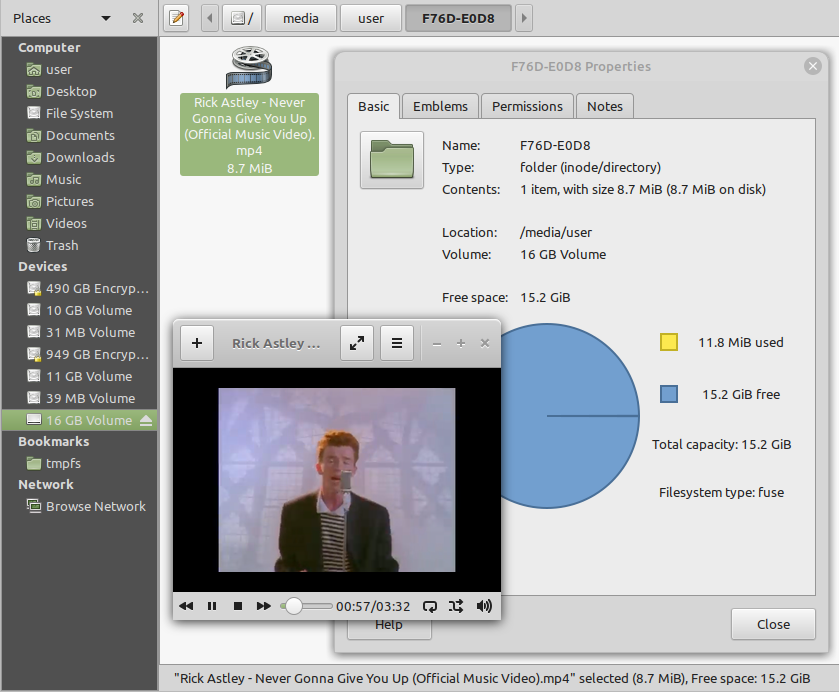 hakavlad/tird
Steganographic storage & File encryption tool
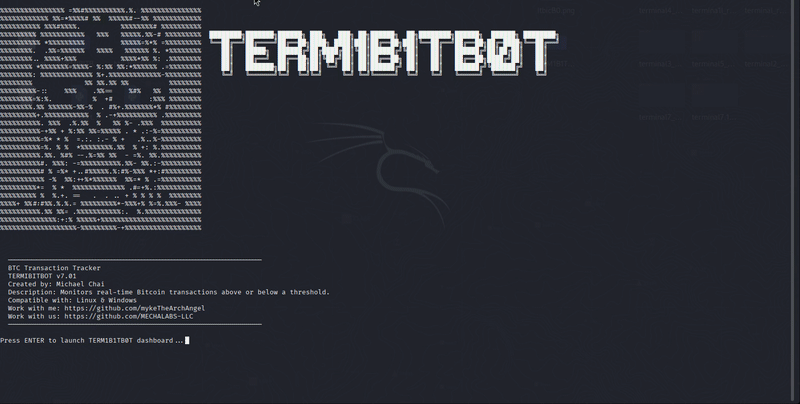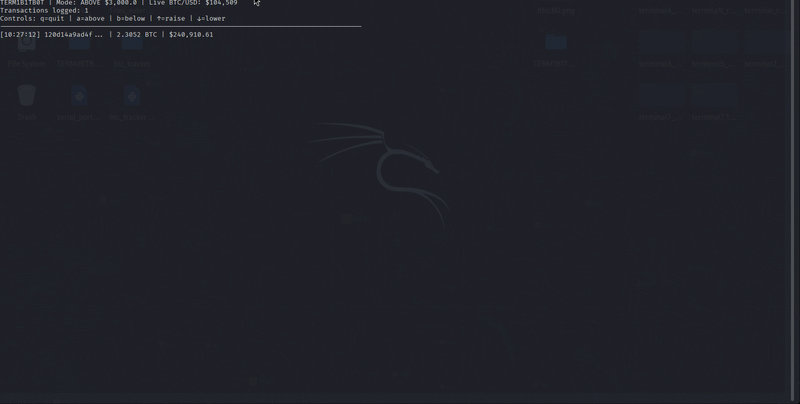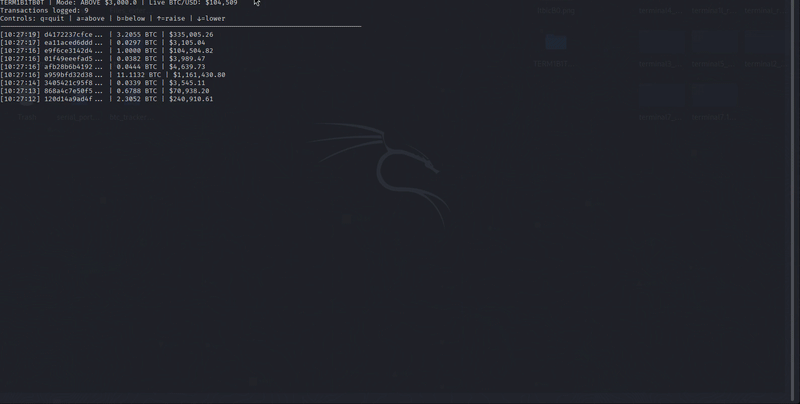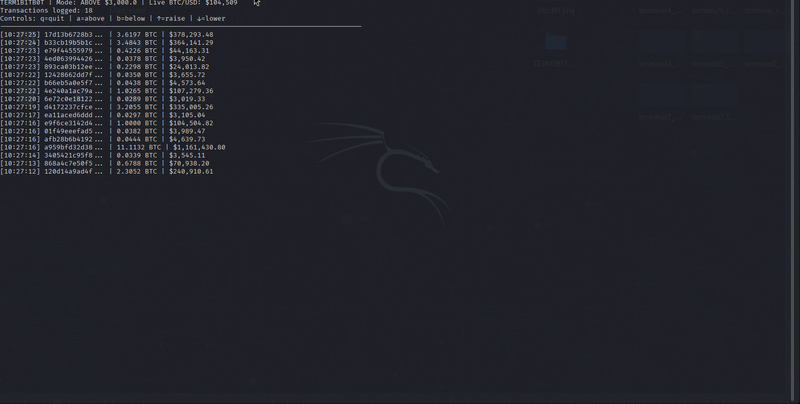 mykethearchangel/term1b1tb0t
A terminal based tool that monitors real-time Bitcoin transactions above or below a specified threshold.
 okanulkr/curveball-cve-2020-0601-poc
Proof-of-concept exploit for CVE-2020-0601 (CurveBall) demonstrating ECC certificate validation bypass to spoof trusted CA and sign arbitrary…