
TCASVS
 owasp/tcasvs
OWASP Thick Client Application Security Verification Standard
code-analysisconfiguration-auditingcryptography+5
owasp/tcasvsOWASP Thick Client Application Security Verification Standard
 strozfriedberg/padbuster
Automated script for performing Padding Oracle attacks
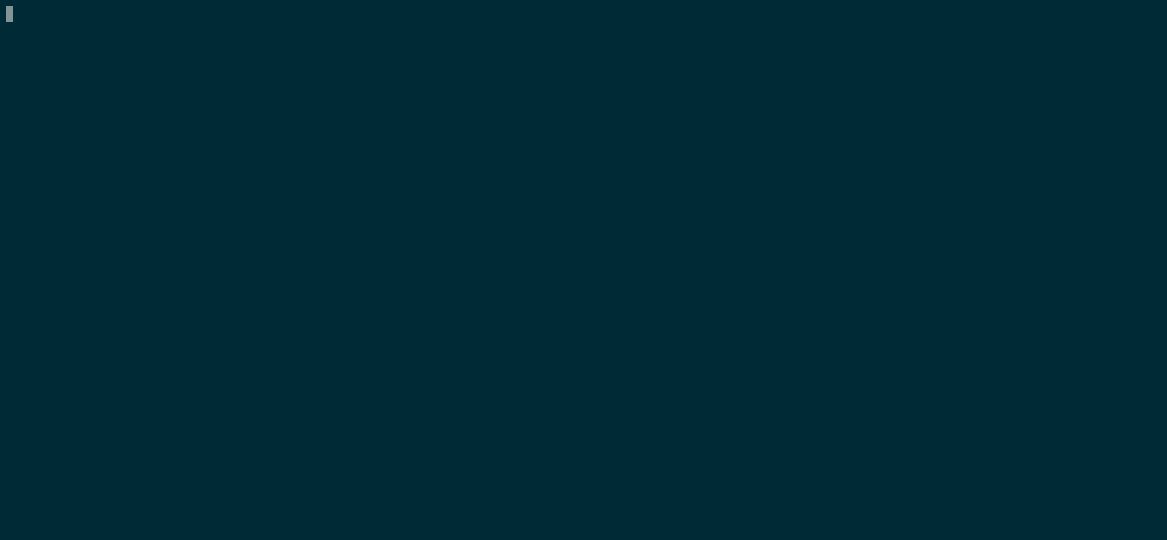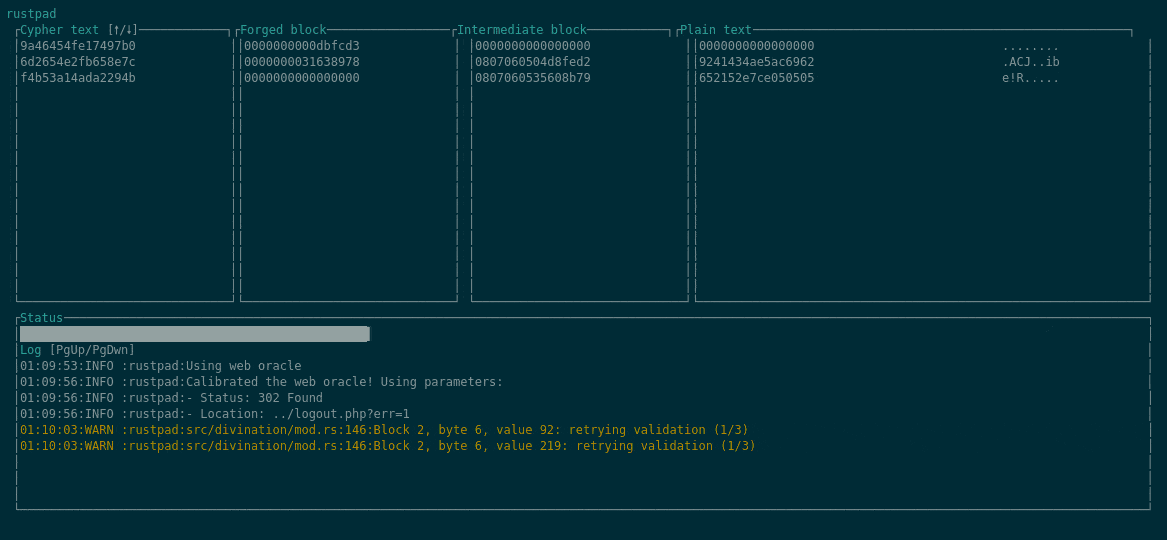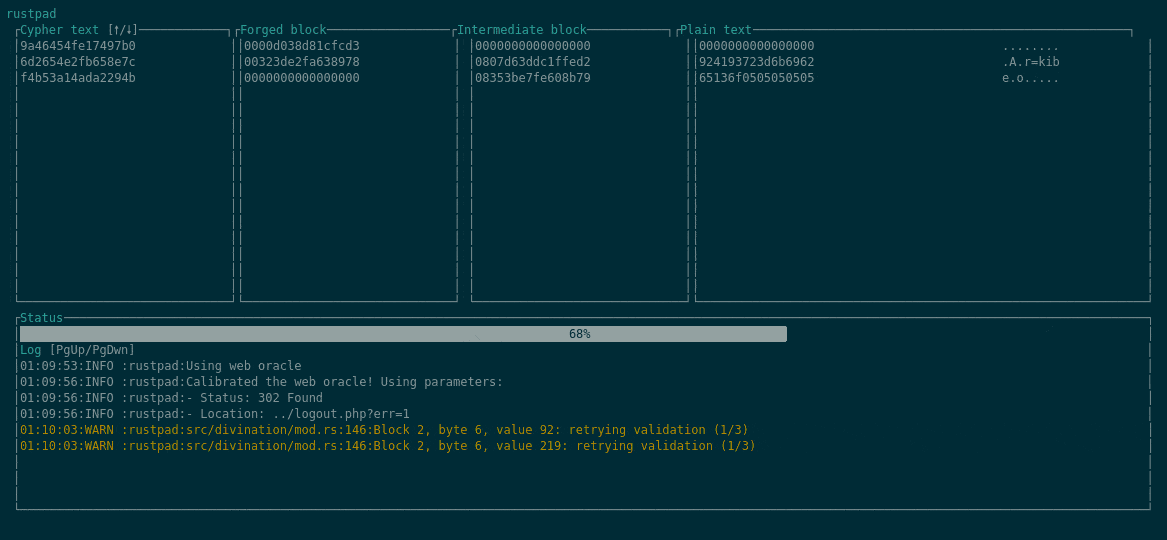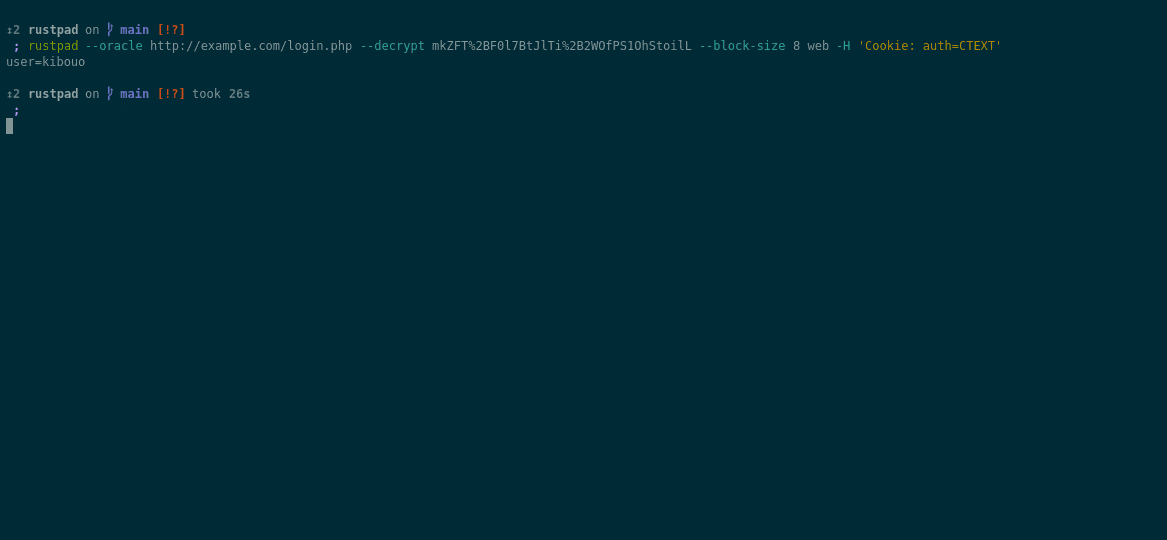 kibouo/rustpad
Multi-threaded Padding Oracle attacks against any service. Written in Rust.
 iangcarroll/cookiemonster
Decodes and unsigns vulnerable session cookies from Django, Flask, Laravel, Express, and JWT frameworks. Supports HMAC-based decoders, base64…
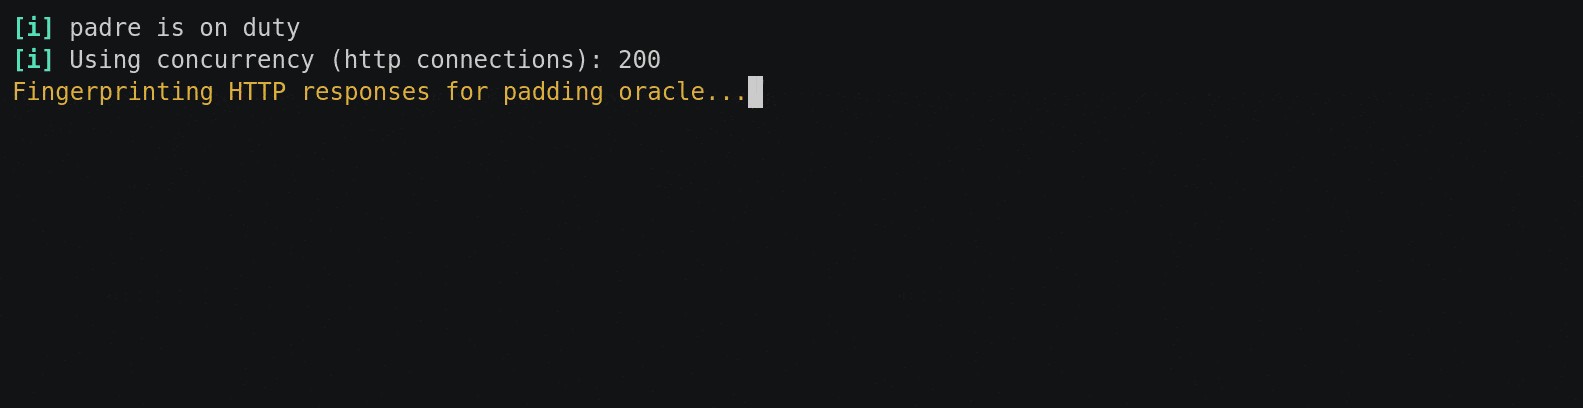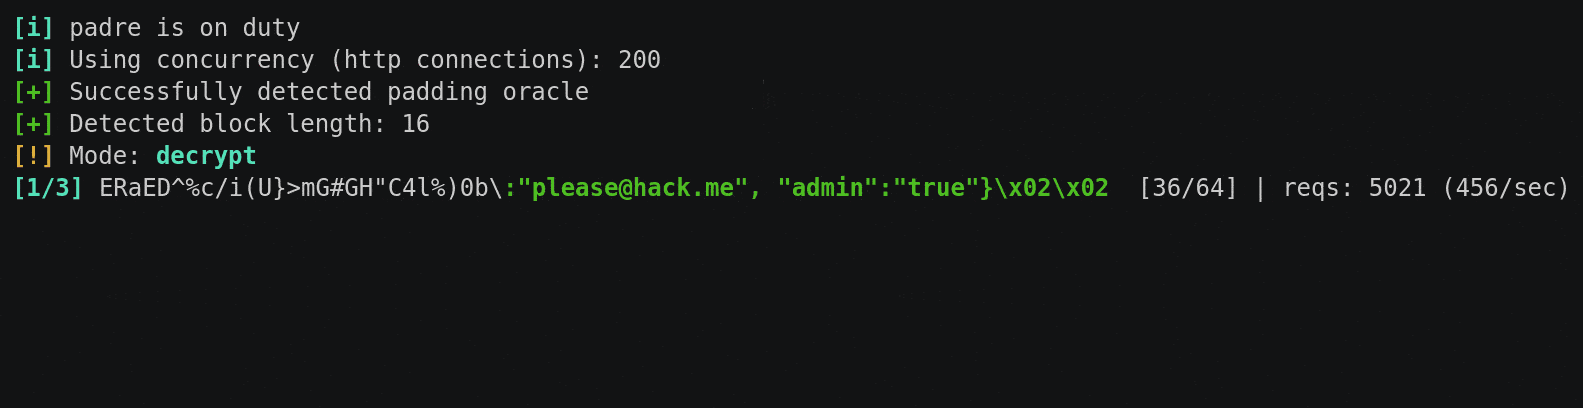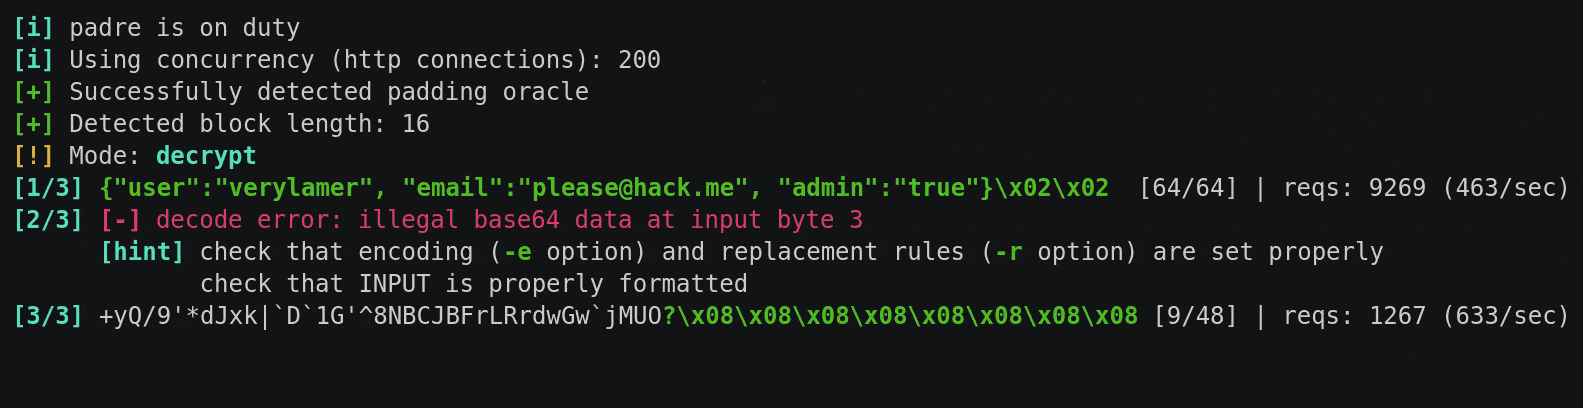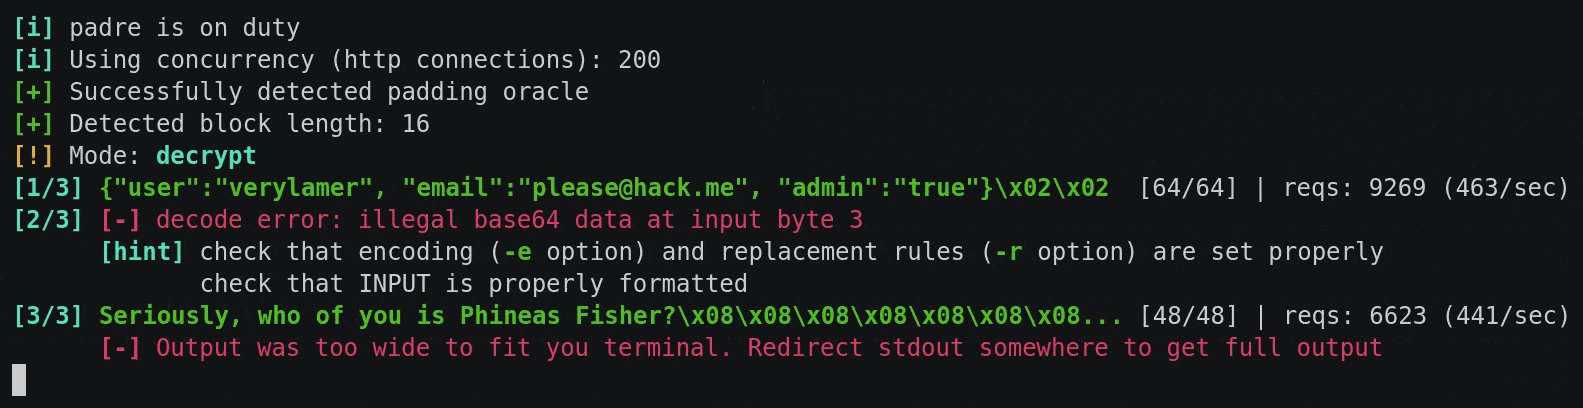 glebarez/padre
Blazing fast, advanced Padding Oracle exploit
 cagataycali/hstp
Application-layer protocol framework for trust-based, end-to-end encrypted communication across heterogeneous networks, enabling uniform service…
 3v4si0n/rs256-2-hs256
JWT Attack to change the algorithm RS256 to HS256
 helidem/cve-2020-16012-poc
Proof-of-concept for CVE-2020-16012: a side-channel attack recovering pixel data from cross-origin images using timing measurements in Chromium's…
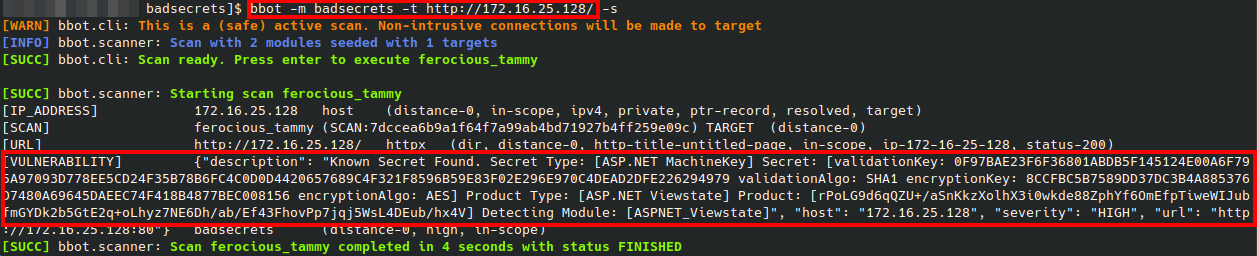 blacklanternsecurity/badsecrets
A library for detecting known secrets across many web frameworks
 irsdl/crapsecrets
A library for detecting known secrets across many web frameworks
 gogo2464/cve-2024-5124
Exploit for CVE-2024-5124 targeting ChuanhuChatGPT via TLS timing side-channel attack. Uses tlsfuzzer to perform character-by-character credential…
 shopify/ssllabs.rb
Ruby client for the Qualys SSL Labs API enabling automated SSL/TLS server assessment, vulnerability detection (e.g., BEAST), and security grade…
 testssl/testssl.sh
Testing TLS/SSL encryption anywhere on any port
 filosottile/heartbleed
A checker (site and tool) for CVE-2014-0160
 bdenneu/cve-2022-33679
One day based on https://googleprojectzero.blogspot.com/2022/10/rc4-is-still-considered-harmful.html
 c0r0n3r/dheater
Proof-of-concept denial-of-service tool that exploits the DHEat attack (CVE-2002-20001) by enforcing Diffie-Hellman key exchange against TLS and SSH…
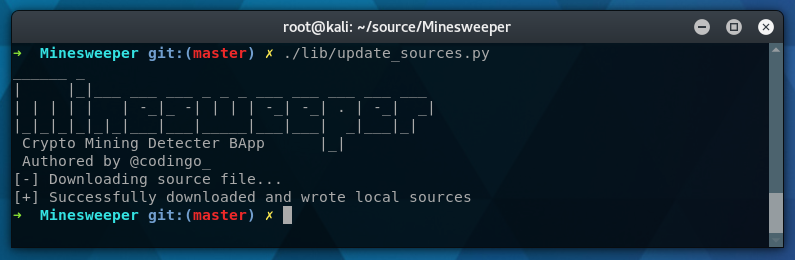 codingo/minesweeper
A Burpsuite plugin (BApp) to aid in the detection of scripts being loaded from over 23000 malicious cryptocurrency mining domains (cryptojacking).
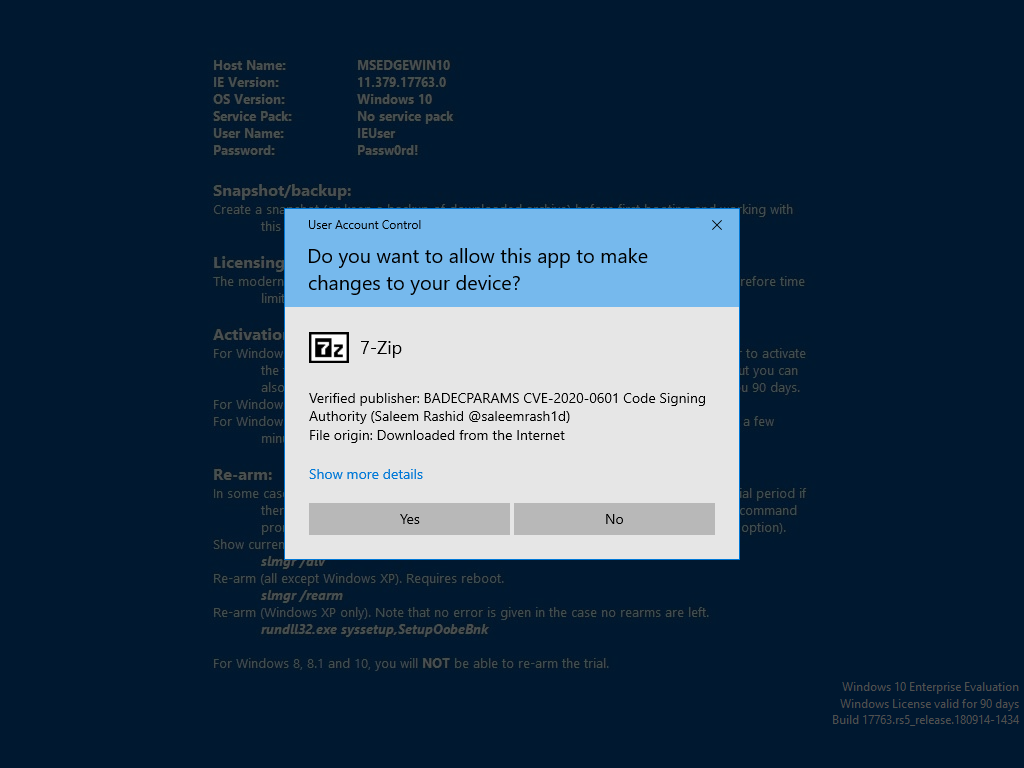 saleemrashid/badecparams
Proof of Concept for CVE-2020-0601