
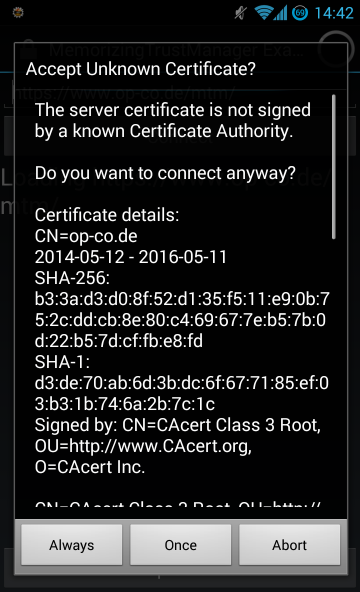
MemorizingTrustManager
 ge0rg/memorizingtrustmanager
A "plugin" for Android Java to allow asking the user about SSL certificates
android-securityauthenticationcryptography+3
181
ge0rg/memorizingtrustmanagerA "plugin" for Android Java to allow asking the user about SSL certificates
 wolfssl/wolfguard
FIPS 140-3 compliant VPN kernel module and user tool, drop-in replacement for WireGuard with AES-256-GCM, SHA2-256, and SECP256R1 cryptography for…
 c0r0n3r/dheater
Proof-of-concept denial-of-service tool that exploits the DHEat attack (CVE-2002-20001) by enforcing Diffie-Hellman key exchange against TLS and SSH…
 libssh/libssh-mirror
C library implementing the SSH protocol for secure remote access, authentication, and encrypted communication. Includes fuzzing support via OSS-Fuzz…
 foxboron/attezt
An open-source TPM device-attest-01 CA server
 einaros/heartbleed-tools
OpenSSL Heartbleed (CVE-2014-0160) vulnerability scanner, data miner and RSA key-restore tools.
 owasp/tcasvs
OWASP Thick Client Application Security Verification Standard
 b9ph0met/px-vm
Reverse engineering toolkit for PerimeterX's bytecode VM, featuring a CFG-based disassembler, 5-layer decryption pipeline, opcode table…
 kvesel/zipbrk
Zip file format fuzzer and multi-tool.
 ciscopsirt/cve-2022-20866
RSA Key Checker for CVE-2022-20866
 alperenugurlu/cve-2024-3596-detector
Detects CVE-2024-3596 in RADIUS/UDP traffic by analyzing MD5 collisions in Access-Request packets, helping administrators identify vulnerable…
 mattgsys/cve-2026-19586
Python PoC exploiting CVE-2026-19586, an unauthenticated command injection in TP-Link Omada SSL VPN that executes arbitrary commands as root via…
 umarrehmansiddiqui/cve-2026-0073
Proof-of-concept exploit for an Android adbd Wireless Debugging TLS auth bypass, using an EC/RSA key type mismatch to obtain an unauthenticated…
 jaarden/cve-2024-22894
Proof-of-concept exploit for CVE-2024-22894, demonstrating 3DES-encrypted root password extraction from Alpha Innotec/Novelan heatpump firmware,…
 gremwell/cve-2020-0601_poc
Proof-of-concept exploit for CVE-2020-0601 (Windows CryptoAPI spoofing) that generates rogue CA certificates to intercept HTTPS traffic, with…
 demining/digital-signature-forgery-attack
How CVE-2025-29774 Vulnerabilities and the SIGHASH_SINGLE Bug Threaten Multi-Signature Wallet Operational Methods with Fake RawTX