

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Sources curated into a security tool Repositories, feeds, communities and curated indexes flow through selection, classification, enrichment and translation into an illustrative tool record. ISC License Copyright (c) 2026 Lucide Icons and Contributors Permission to use, copy, modify, and/or distribute this software for any purpose with or without fee is hereby granted, provided that the above copyright notice and this permission notice appear in all copies. THE SOFTWARE IS PROVIDED "AS IS" AND THE AUTHOR DISCLAIMS ALL WARRANTIES WITH REGARD TO THIS SOFTWARE INCLUDING ALL IMPLIED WARRANTIES OF MERCHANTABILITY AND FITNESS. IN NO EVENT SHALL THE AUTHOR BE LIABLE FOR ANY SPECIAL, DIRECT, INDIRECT, OR CONSEQUENTIAL DAMAGES OR ANY DAMAGES WHATSOEVER RESULTING FROM LOSS OF USE, DATA OR PROFITS, WHETHER IN AN ACTION OF CONTRACT, NEGLIGENCE OR OTHER TORTIOUS ACTION, ARISING OUT OF OR IN CONNECTION WITH THE USE OR PERFORMANCE OF THIS SOFTWARE. --- The following Lucide icons are derived from the Feather project: airplay, alert-circle, alert-octagon, alert-triangle, aperture, arrow-down-circle, arrow-down-left, arrow-down-right, arrow-down, arrow-left-circle, arrow-left, arrow-right-circle, arrow-right, arrow-up-circle, arrow-up-left, arrow-up-right, arrow-up, at-sign, calendar, cast, check, chevron-down, chevron-left, chevron-right, chevron-up, chevrons-down, chevrons-left, chevrons-right, chevrons-up, circle, clipboard, clock, code, columns, command, compass, corner-down-left, corner-down-right, corner-left-down, corner-left-up, corner-right-down, corner-right-up, corner-up-left, corner-up-right, crosshair, database, divide-circle, divide-square, dollar-sign, download, external-link, feather, frown, hash, headphones, help-circle, info, italic, key, layout, life-buoy, link-2, link, loader, lock, log-in, log-out, maximize, meh, minimize, minimize-2, minus-circle, minus-square, minus, monitor, moon, more-horizontal, more-vertical, move, music, navigation-2, navigation, octagon, pause-circle, percent, plus-circle, plus-square, plus, power, radio, rss, search, server, share, shopping-bag, sidebar, smartphone, smile, square, table-2, tablet, target, terminal, trash-2, trash, triangle, tv, type, upload, x-circle, x-octagon, x-square, x, zoom-in, zoom-out The MIT License (MIT) (for the icons listed above) Copyright (c) 2013-present Cole Bemis Permission is hereby granted, free of charge, to any person obtaining a copy of this software and associated documentation files (the "Software"), to deal in the Software without restriction, including without limitation the rights to use, copy, modify, merge, publish, distribute, sublicense, and/or sell copies of the Software, and to permit persons to whom the Software is furnished to do so, subject to the following conditions: The above copyright notice and this permission notice shall be included in all copies or substantial portions of the Software. THE SOFTWARE IS PROVIDED "AS IS", WITHOUT WARRANTY OF ANY KIND, EXPRESS OR IMPLIED, INCLUDING BUT NOT LIMITED TO THE WARRANTIES OF MERCHANTABILITY, FITNESS FOR A PARTICULAR PURPOSE AND NONINFRINGEMENT. IN NO EVENT SHALL THE AUTHORS OR COPYRIGHT HOLDERS BE LIABLE FOR ANY CLAIM, DAMAGES OR OTHER LIABILITY, WHETHER IN AN ACTION OF CONTRACT, TORT OR OTHERWISE, ARISING FROM, OUT OF OR IN CONNECTION WITH THE SOFTWARE OR THE USE OR OTHER DEALINGS IN THE SOFTWARE.
Repositories
GitHub & GitLab
Security feeds
Blogs, RSS & Atom
Communities
Reddit, X & submissions
Curated indexes
Security lists & trends
Curate & select
Classification
Enrichment
Translation
Fictional tool and repository. The description, categories, stars, forks and views are illustrative examples, not live or verified data. Fictional tool and repository. The description, categories, stars, forks and views are illustrative examples, not live or verified data. {"fictional":true,"name":"Tool","version":"1.0.1","repository":"owner/tool","live_metrics":false,"example_metrics":{"stars":1200,"forks":128,"views":8600}}
Tool
v1.0.1 owner/tool
Discover assets and review
HTTP security headers.
Reconnaissance
Web security
1,200 stars — Fictional example1.2k 128 forks — Fictional example128 8,600 views — Fictional example8.6k

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
771 results
CVE-2020-12712 preview

CVE-2020-12712

GitHub0xvedette/cve-2020-12712

Decrypts passwords stored in SOS JobScheduler (S)FTP profiles by exploiting the use of the profile name as the 3DES encryption key, enabling recovery…

cryptographyexploitationpassword-attacks+2
6 years ago
CVE-2022-21449 preview

CVE-2022-21449

GitHubdavwwwx/cve-2022-21449

repo showcasing generating "psychic signatures for java" implemented in a nodejs environment 😅
cryptographyexploitationpayload-generation+2
3 years ago
CVE-2014-2734 preview

CVE-2014-2734

GitHubgdisneyleugers/cve-2014-2734

Proof-of-concept exploit demonstrating Ruby OpenSSL CA private key spoofing vulnerability (CVE-2014-2734) via public key manipulation before private…
cryptographyeducationexploitation+2
12 years ago
CVE-2020-16012-PoC preview

CVE-2020-16012-PoC

GitHubhelidem/cve-2020-16012-poc

Proof-of-concept for CVE-2020-16012: a side-channel attack recovering pixel data from cross-origin images using timing measurements in Chromium's…
cryptographyexploitationvulnerability-analysis+1
1 year ago
CurveBall-CVE-2020-0601-PoC preview

CurveBall-CVE-2020-0601-PoC

GitHubokanulkr/curveball-cve-2020-0601-poc

Proof-of-concept exploit for CVE-2020-0601 (CurveBall) demonstrating ECC certificate validation bypass to spoof trusted CA and sign arbitrary…
code-analysiscryptographyexploitation+3
5 years ago
details-for-CVE-2022-46505 preview

details-for-CVE-2022-46505

GitHubsmalltown123/details-for-cve-2022-46505

MatrixSSL session resume bug

binary-analysiscryptographyeducation+2
3 years ago
psychic-signatures preview

psychic-signatures

GitHubmarschall/psychic-signatures

Demos the Psychic Signatures vulnerability (CVE-2022-21449)
cryptographyeducationexploitation+2
4 years ago
CVE-2014-3570_G2.5_openssl_no_patch preview

CVE-2014-3570_G2.5_openssl_no_patch

GitHubuthrasri/cve-2014-3570_g2.5_openssl_no_patch
binary-analysiscryptographyexploitation+2
3 years ago
CVE-2022-21449-showcase preview

CVE-2022-21449-showcase

GitHubskipper7718/cve-2022-21449-showcase

Demonstrates the Java Cryptography Architecture vulnerability CVE-2022-21449, showcasing the signature verification bypass with a proof-of-concept…
cryptographyeducationexploitation+1
4 years ago
curveball-plus preview

curveball-plus

GitHubtyj956413282/curveball-plus

simulation experiment of Curveball (CVE-2020-0601) attacks under ECQV implicit certificates with Windows-like verifiers

binary-exploitationcryptographyeducation+3
3 years ago
poodle-attack-sandbox preview

poodle-attack-sandbox

GitHubgorugoo/poodle-attack-sandbox

Test code for poodle attack (CVE-2014-3566)

cryptographyeducationexploitation+3
1 year ago
demo-cve-2022-21449 preview

demo-cve-2022-21449

GitHubvolodymyr-hladkyi-symphony/demo-cve-2022-21449

Educational demo of CVE-2022-21449 Java ECDSA signature bypass using real and fake JWT tokens to illustrate the vulnerability and its impact on…
authenticationcryptographyeducation+3
1 year ago
OpenSSL_DTLS_CVE_2014_0221 preview

OpenSSL_DTLS_CVE_2014_0221

GitHubtpdlshdmlrkfmcla/openssl_dtls_cve_2014_0221

OpenSSL DTLS CVE-2014-0221 Remote Denial
cryptographyexploitationnetwork-security+2
1 year ago
bleeding-heart preview

bleeding-heart

GitHubpierceoneill/bleeding-heart

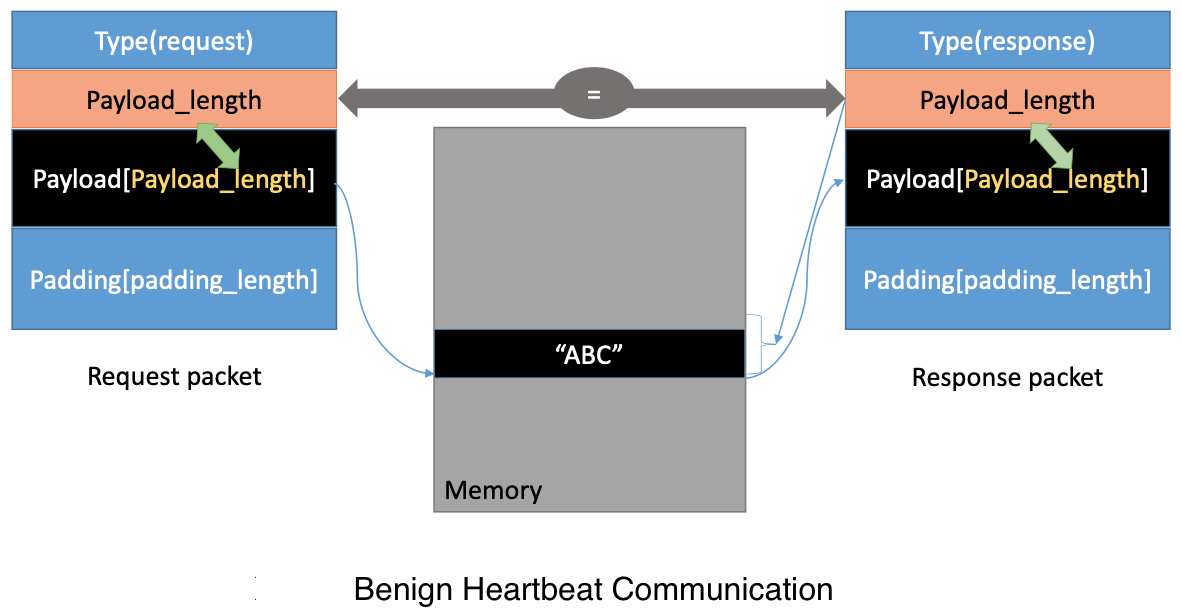
The Heartbleed bug `CVE-2014-0160` is a severe implementation flaw in the OpenSSL library, which enables attackers to steal data from the memory of…

cryptographyeducationexploitation+3
5 years ago
ROCA-attack-on-vulnerability-CVE-2017-15361 preview

ROCA-attack-on-vulnerability-CVE-2017-15361

GitHubelbarbons/roca-attack-on-vulnerability-cve-2017-15361

ROCA attack on vulnerability CVE-2017-15361
cryptographyeducationexploitation+2
3 years ago
jlangch__venice_CVE-2022-36007_1-10-16 preview

jlangch__venice_CVE-2022-36007_1-10-16

GitHubshoucheng3/jlangch__venice_cve-2022-36007_1-10-16

Sandboxed Lisp dialect for the JVM with immutable data structures, macros, and over 900 core functions. Ideal for safe scripting, automation, and…

code-analysiscryptographyeducation+2
1 year ago
CVE-2022-21449 preview

CVE-2022-21449

GitHubalexanderzinoni/cve-2022-21449

Educational Python project implementing elliptic curve cryptography (ECDSA, ECIES) and simulating exploitation of CVE-2022-21449, with visualizations…
cryptographyeducationexploitation+2
26 days ago
bouncy-castle-generative-test-poc preview

bouncy-castle-generative-test-poc

GitHubmadstap/bouncy-castle-generative-test-poc

A generative test that would've caught CVE-2020-28052

code-analysiscryptographyeducation+2
5 years ago
Previous1…40414243Next
Sources curated into a security tool Repositories, feeds, communities and curated indexes flow through selection, classification, enrichment and translation into an illustrative tool record. ISC License Copyright (c) 2026 Lucide Icons and Contributors Permission to use, copy, modify, and/or distribute this software for any purpose with or without fee is hereby granted, provided that the above copyright notice and this permission notice appear in all copies. THE SOFTWARE IS PROVIDED "AS IS" AND THE AUTHOR DISCLAIMS ALL WARRANTIES WITH REGARD TO THIS SOFTWARE INCLUDING ALL IMPLIED WARRANTIES OF MERCHANTABILITY AND FITNESS. IN NO EVENT SHALL THE AUTHOR BE LIABLE FOR ANY SPECIAL, DIRECT, INDIRECT, OR CONSEQUENTIAL DAMAGES OR ANY DAMAGES WHATSOEVER RESULTING FROM LOSS OF USE, DATA OR PROFITS, WHETHER IN AN ACTION OF CONTRACT, NEGLIGENCE OR OTHER TORTIOUS ACTION, ARISING OUT OF OR IN CONNECTION WITH THE USE OR PERFORMANCE OF THIS SOFTWARE. --- The following Lucide icons are derived from the Feather project: airplay, alert-circle, alert-octagon, alert-triangle, aperture, arrow-down-circle, arrow-down-left, arrow-down-right, arrow-down, arrow-left-circle, arrow-left, arrow-right-circle, arrow-right, arrow-up-circle, arrow-up-left, arrow-up-right, arrow-up, at-sign, calendar, cast, check, chevron-down, chevron-left, chevron-right, chevron-up, chevrons-down, chevrons-left, chevrons-right, chevrons-up, circle, clipboard, clock, code, columns, command, compass, corner-down-left, corner-down-right, corner-left-down, corner-left-up, corner-right-down, corner-right-up, corner-up-left, corner-up-right, crosshair, database, divide-circle, divide-square, dollar-sign, download, external-link, feather, frown, hash, headphones, help-circle, info, italic, key, layout, life-buoy, link-2, link, loader, lock, log-in, log-out, maximize, meh, minimize, minimize-2, minus-circle, minus-square, minus, monitor, moon, more-horizontal, more-vertical, move, music, navigation-2, navigation, octagon, pause-circle, percent, plus-circle, plus-square, plus, power, radio, rss, search, server, share, shopping-bag, sidebar, smartphone, smile, square, table-2, tablet, target, terminal, trash-2, trash, triangle, tv, type, upload, x-circle, x-octagon, x-square, x, zoom-in, zoom-out The MIT License (MIT) (for the icons listed above) Copyright (c) 2013-present Cole Bemis Permission is hereby granted, free of charge, to any person obtaining a copy of this software and associated documentation files (the "Software"), to deal in the Software without restriction, including without limitation the rights to use, copy, modify, merge, publish, distribute, sublicense, and/or sell copies of the Software, and to permit persons to whom the Software is furnished to do so, subject to the following conditions: The above copyright notice and this permission notice shall be included in all copies or substantial portions of the Software. THE SOFTWARE IS PROVIDED "AS IS", WITHOUT WARRANTY OF ANY KIND, EXPRESS OR IMPLIED, INCLUDING BUT NOT LIMITED TO THE WARRANTIES OF MERCHANTABILITY, FITNESS FOR A PARTICULAR PURPOSE AND NONINFRINGEMENT. IN NO EVENT SHALL THE AUTHORS OR COPYRIGHT HOLDERS BE LIABLE FOR ANY CLAIM, DAMAGES OR OTHER LIABILITY, WHETHER IN AN ACTION OF CONTRACT, TORT OR OTHERWISE, ARISING FROM, OUT OF OR IN CONNECTION WITH THE SOFTWARE OR THE USE OR OTHER DEALINGS IN THE SOFTWARE.
Repositories
GitHub & GitLab
Security feeds
Blogs, RSS & Atom
Communities
Social & submissions
Curated indexes
Security lists & trends
Curate & classify
Enrich & translate
Fictional tool and repository. The description, categories, stars, forks and views are illustrative examples, not live or verified data. Fictional tool and repository. The description, categories, stars, forks and views are illustrative examples, not live or verified data. {"fictional":true,"name":"Tool","version":"1.0.1","repository":"owner/tool","live_metrics":false,"example_metrics":{"stars":1200,"forks":128,"views":8600}}
Tool
owner/tool v1.0.1
Discover assets and review HTTP security headers.
Reconnaissance
Web security
1,200 stars — Fictional example1.2k 128 forks — Fictional example128 8,600 views — Fictional example8.6k