CVE-2025-23134_fixes_code

The ASN1_STRING_set() function takes an `int` length, make sure the argument is not inadvertently truncated when it is called from asn1_ex_c2i().

The ASN1_STRING_set() function takes an `int` length, make sure the argument is not inadvertently truncated when it is called from asn1_ex_c2i().

Proof-of-concept exploit for CVE-2024-22894, demonstrating 3DES-encrypted root password extraction from Alpha Innotec/Novelan heatpump firmware,…

publiccms_decrypt

Portable, hardware-backed WebAuthn credentials using TPM 2.0. Deterministic parent key derived from a master seed enables cross-device credential…

Hide valuable information where it's least expected

Public version of the Entropica repo

PoC for CVE-2025-65945 (Improper Verification of Cryptographic Signature in node-jws)

⭐️The famous XWorm RAT, version 2.1. Educational purposes only

Exploit for cve-2013-0169

Bazzite plus a TPM boot attestation layer. Work in progress: builds unverified, UKI mechanism unresolved. Spec: github.com/plunder707/attested-gaming

Palo Alto Networks PAN-OS contains an authentication bypass caused by flaws in the GlobalProtect portal and gateway, letting attackers establish…

How CVE-2025-29774 Vulnerabilities and the SIGHASH_SINGLE Bug Threaten Multi-Signature Wallet Operational Methods with Fake RawTX

Proof-of-concept local privilege escalation tool exploiting a kernel XFRM/ESP vulnerability (CVE-2026-43503) via crafted AES-CBC encrypted payloads…

Demonstrates CVE-2026-1122 Ed25519 signature bypass via low-order point injection, forging malicious IoT firmware updates with Python and C verifier…

Proof-of-concept for CVE-2026-44351, an authentication bypass in fast-jwt <6.2.4 where an empty HMAC key lets attackers forge arbitrary JWTs accepted…

ZTE SmartLife security findings leading to account takeover: 100K+ Google Play downloads and CVE-2026-86552 through CVE-2026-86555.

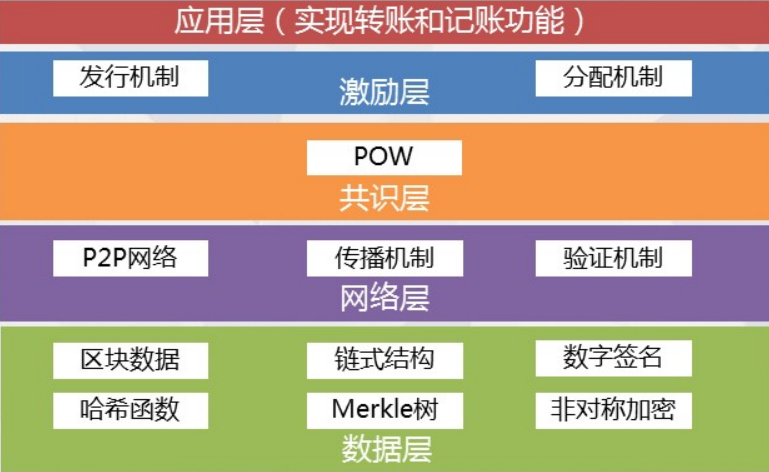
BlockChain Security Construction

Kerberos RC4 deprecation: detection, remediation and guidance (CVE-2026-20833)