CVE-2020-9289
Decrypt reversible secrets encrypted using the default hardcoded key related to CVE-2020-9289 on FortiAnalyzer/FortiManager (the only difference with…

Decrypt reversible secrets encrypted using the default hardcoded key related to CVE-2020-9289 on FortiAnalyzer/FortiManager (the only difference with…

Kerberos RC4 deprecation: detection, remediation and guidance (CVE-2026-20833)

Detects Windows and Linux systems with enabled Trusted Platform Modules (TPM) vulnerable to CVE-2017-15361. #nsacyber

A deliberately vulnerable mobile banking application designed for practicing mobile security testing. Features common vulnerabilities found in…

Java security framework providing authentication, authorization, cryptography, and session management APIs to secure any application from mobile to…

This repo describes a vulnerability affecting the QR code based pairing process of the eWeLink IoT devices (CVE-2020-12702).

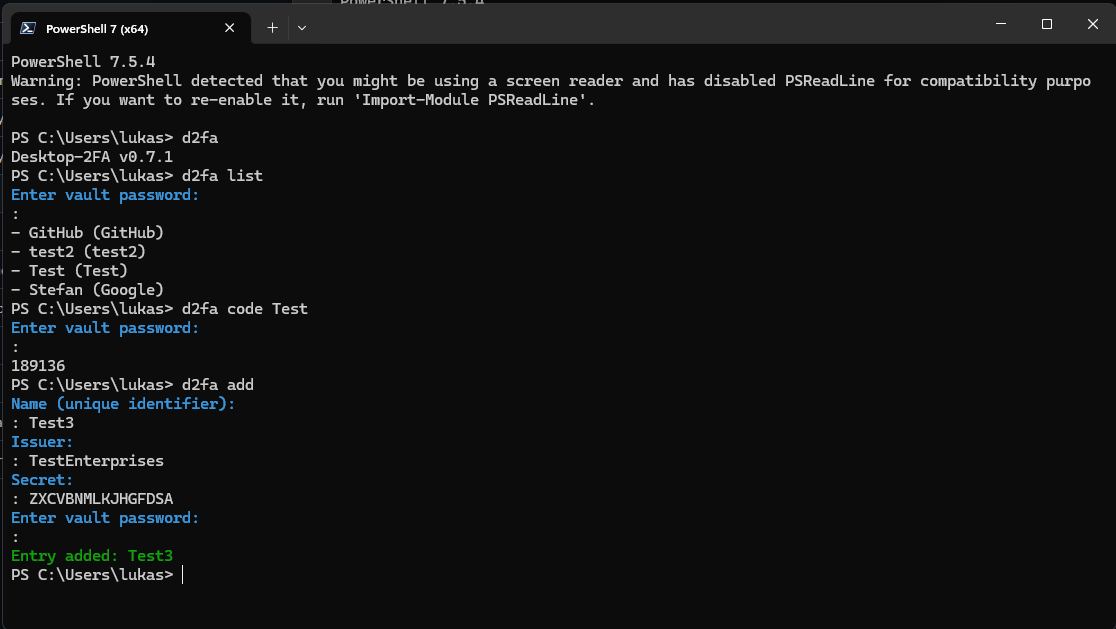
A secure offline desktop application for generating and managing TOTP 2FA codes. Features encrypted vault storage, modern cryptography (Argon2 +…

Improper Certificate Chain Validation in EagleEyes Lite Android Application

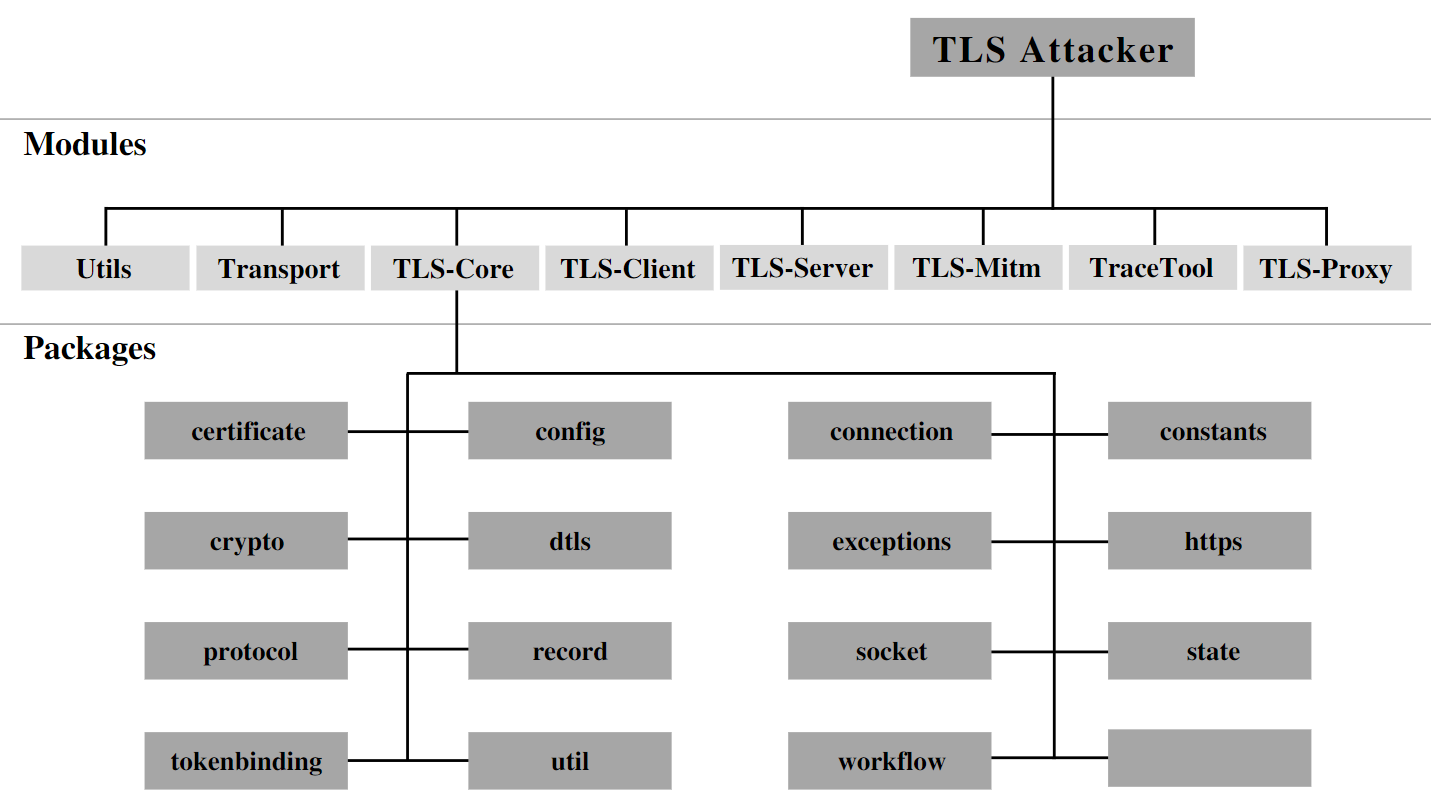
Java-based framework for systematic fuzzing and analysis of TLS libraries. Enables arbitrary protocol message crafting, modification, and testing of…