

awesome-web-hacking
 infoslack/awesome-web-hacking
Curated list of web application security resources including books, tools, cheat sheets, labs, and courses for learning penetration testing and…
cryptographyctfcurated-resources+6
7.2k
infoslack/awesome-web-hackingCurated list of web application security resources including books, tools, cheat sheets, labs, and courses for learning penetration testing and…
 secdev/scapy
Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
 nccgroup/dotnetpaddingoracle
Python Implementation of a .NET Padding Oracle Assessment Tool
 j4k0m/cve-2018-0114
Exploitation of a vulnerability in Cisco's node-jose, a JavaScript library created to manage JWT.
 azureadtrent/cve-2026-52824
Technical analysis and PoC of CVE-2026-52824: default APP_SECRET in the Kimai Docker image enabling unauthenticated login link forgery. Affects <=…
 volodymyr-hladkyi-symphony/demo-cve-2022-21449
Educational demo of CVE-2022-21449 Java ECDSA signature bypass using real and fake JWT tokens to illustrate the vulnerability and its impact on…
 murrez/cve-2026-97657
Python PoC for CVE-2026-97657: forges AES-CTR recovery tokens via XOR malleability to bypass authentication and take over WordPress accounts in…
 tori-tech/mandating-honeypots-project
This repository conducts security audits on digital identity verification systems, identifies vulnerabilities through whitepapers and technical POCs,…
 nccgroup/decoder-improved
Improved decoder for Burp Suite
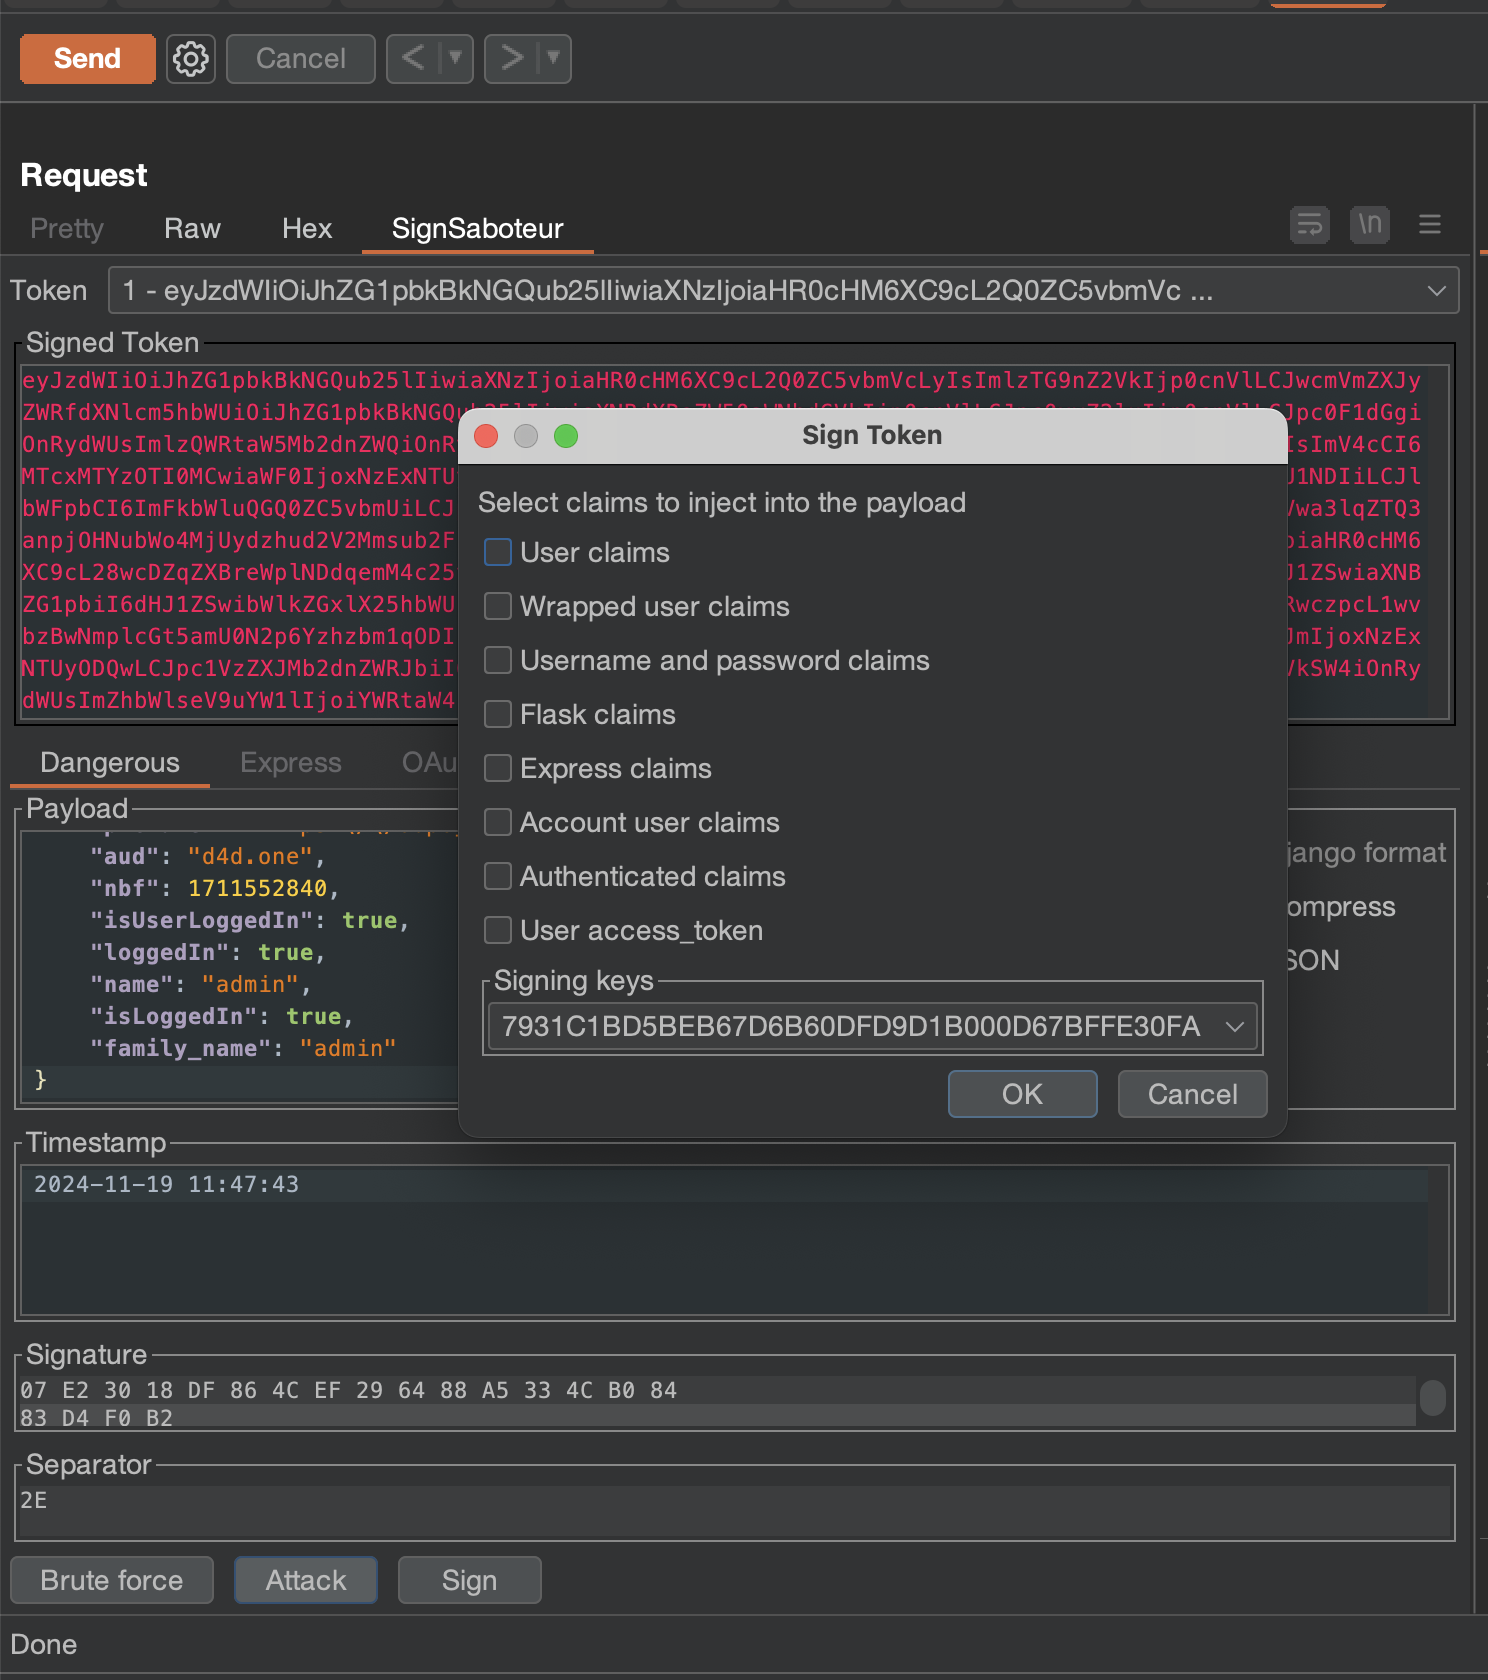 d0ge/sign-saboteur
SignSaboteur is a Burp Suite extension for editing, signing, verifying various signed web tokens
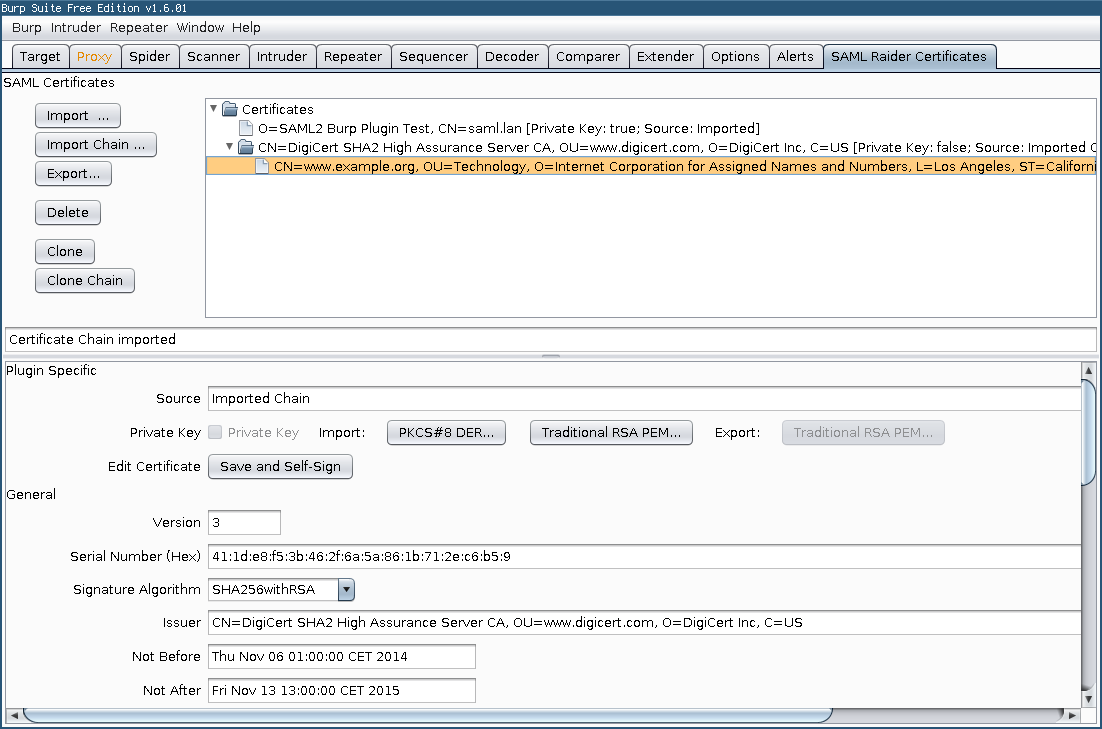 lindi2/samlraider
SAML2 Burp Extension
 kishanbagaria/padding-oracle-attacker
🔓 CLI tool and library to execute padding oracle attacks easily, with support for concurrent network requests and an elegant UI.
 bao7uo/dp_crypto
Base64-based encryption oracle exploit for CVE-2017-9248 (Telerik UI for ASP.NET AJAX dialog handler)
 blacklanternsecurity/dp_cryptomg
Another tool for exploiting CVE-2017-9248, a cryptographic weakness in Telerik UI for ASP.NET AJAX dialog handler.
 commando-x/vuln-bank-mobile
A deliberately vulnerable mobile banking application designed for practicing mobile security testing. Features common vulnerabilities found in…
 liamg/pax
:skull: :unlock: CLI tool for PKCS7 padding oracle attacks
 caveeroo/cve-2026-111497-wordpress-poc
CVE-2026-111497 RCE PoC for one pinned Docker Official Image for WordPress