

ctf-skills
 ljagiello/ctf-skills
Agent skills for solving CTF challenges - web exploitation, binary pwn, crypto, reverse engineering, forensics, OSINT, and more
binary-exploitationcryptographyctf+9
3.5k
ljagiello/ctf-skillsAgent skills for solving CTF challenges - web exploitation, binary pwn, crypto, reverse engineering, forensics, OSINT, and more
 minglink/dsh-infinite-gen-5
DeepSeek v4.1 flash 逆向工具(无限五代) 求 Star 收藏 ⭐欢迎大家提交项目的改进
 abraxas/gatex
FortinetHunter (@YogSoth0) binary cracking application. Part of CTF for FortinetHunter. ELF door: a stripped Nuitka onefile, an XOR-scrambled…
 mfthomps/labtainers
Labtainers: A Docker-based cyber lab framework
 edwardzpeng/presentations
Slides and conference talks from security research covering Windows, virtualization, web, and blockchain exploit techniques, presented at Black Hat,…
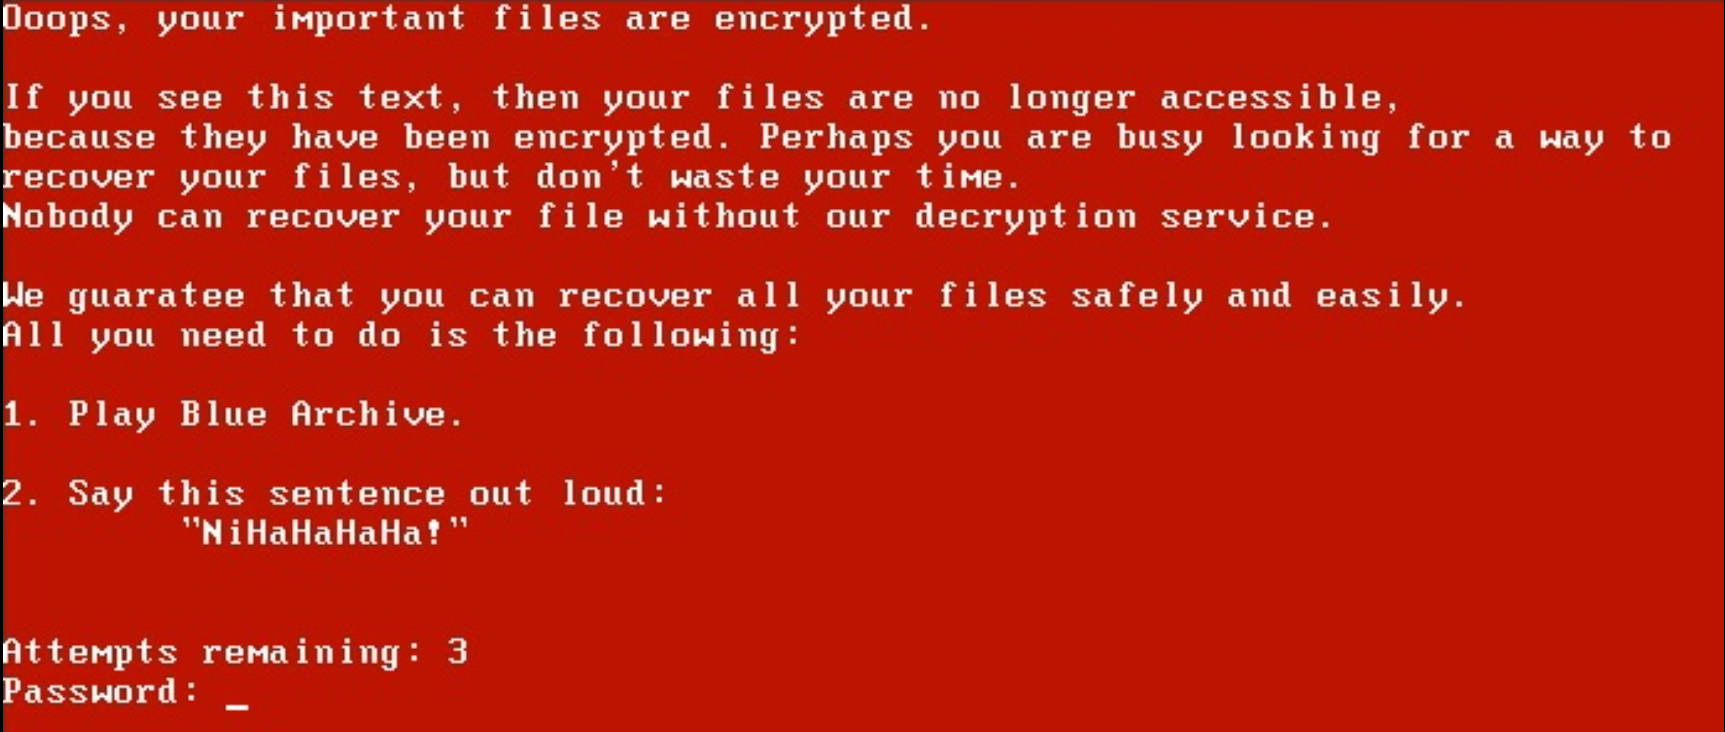 iss4cf0ng/openpetya
A Proof-of-Concept bootkit and UEFI boot application inspired by Petya ransomware, written in Assembly, C, and C++
 kha-beleh/poc-cve-2025-69420
Crash-only PoC for CVE-2025-69420 demonstrating a type-confusion vulnerability in OpenSSL's TimeStamp Response verification via malformed ESS…
 kha-beleh/poc-cve-2025-69419
Minimal proof-of-concept reproducer for CVE-2025-69419, a heap buffer overflow in OpenSSL's PKCS12_get_friendlyname() triggered by a crafted…
 winslowe/cve-2024-4309-analysis
BGT-Pentest-LAB Final Project: Xiaomi HyperOS System Updater OTA Signature Verification Bypass (CVE-2024-4309) Deep Analysis.
 gl1tch0x1/dirtyclone
Proof-of-concept local privilege escalation tool exploiting a kernel XFRM/ESP vulnerability (CVE-2026-43503) via crafted AES-CBC encrypted payloads…
 victoriacfigueiredo/heartbleed-lab
Educational laboratory for studying CVE-2014-0160 (Heartbleed) and framing inconsistencies in TLS heartbeat handling.
 x-stp/cves-2025-11187_15467_69418
OpenSSL pocs: PKCS#12 stack overflow, CMS IV overflow, OCB infoleak [partial chain]
 giancarlolelli/quantum
This repository contains the code and submission detail for the QDay prize challenge by https://www.projecteleven.com/
 metadust/cve-2025-11187
Stack buffer overflow in PKCS#12 PBMAC1 PBKDF2 keylength (OpenSSL 3.X)
 nyu-llm-ctf/ctftiny
Official repository for CTFTiny
 thegaminggallifreyan/liberationplay-cve-2025-24132-airbourne-poc
POC for CVE-2025-24132 (AirBourne). Currently just triggers the overflow and causes a crash
 guiimoraes/cve-2025-15467
Command Execution PoC for OpenSSL Stack buffer overflow CVE-2025-15467
 simoesctt/cve-2025-1234-rsa-key-validation-bypass
A flaw in a popular RSA implementation allows attackers to bypass key validation by supplying a modulus that appears valid but is actually factorable…