
fulcio
 sigstore/fulcio
Certificate authority issuing short-lived code-signing certificates tied to OpenID Connect identities, enabling verifiable software supply chain…
authentication-authorizationcryptographyidentity-access-management+1
891
sigstore/fulcioCertificate authority issuing short-lived code-signing certificates tied to OpenID Connect identities, enabling verifiable software supply chain…
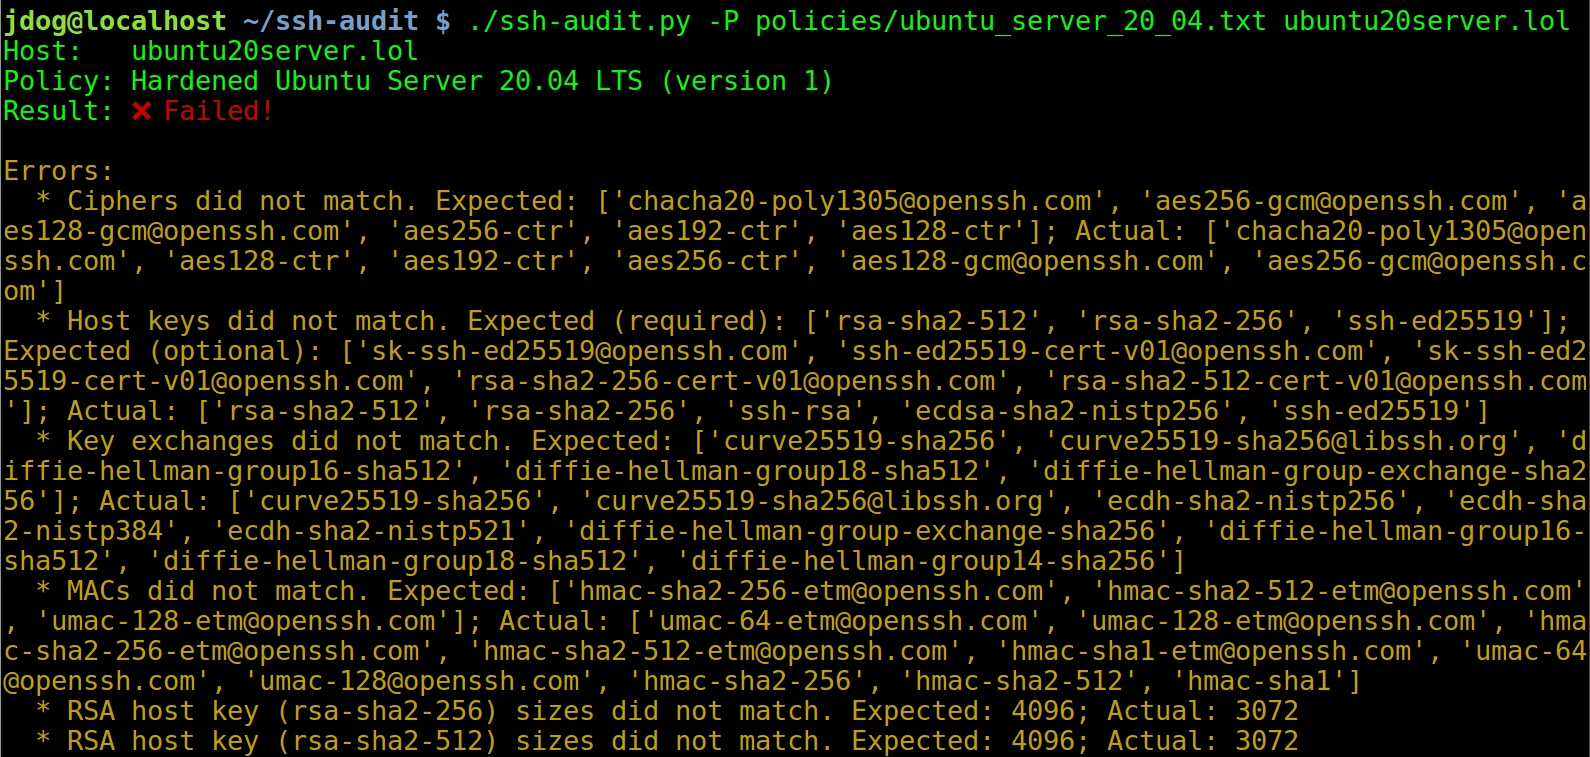 jtesta/ssh-audit
SSH server & client security auditing (banner, key exchange, encryption, mac, compression, compatibility, security, etc)
 jedisct1/libsodium
A modern, portable, easy to use crypto library.
 theupdateframework/python-tuf
Python reference implementation of The Update Framework (TUF)
 c2sp/c2sp
Community Cryptography Specification Project

 owasp/tcasvs
OWASP Thick Client Application Security Verification Standard
 quarkslab/conf-presentations
Quarkslab conference talks
 devploit/awesome-ctf-resources
A list of Capture The Flag (CTF) frameworks, libraries, resources and software for started/experienced CTF players 🚩
 nervosnetwork/ckb-vm
CKB's vm, based on open source RISC-V ISA
 in-toto/in-toto
Protects software supply chain integrity by verifying each step is performed by authorized functionaries, using signed layout and link metadata.
 msdmehdipour/meshtastic-cve-2025-52464-poc
Software-only proof of concept for CVE-2025-52464 in Meshtastic Direct Messages
 pcrosby-1990/cip-security-poc
Proof-of-concept reproducing CVE-2021-22681's hardcoded-key flaw and validating a per-device mutual TLS/CRL fix over simulated EtherNet/IP, with IEC…
 mrash/fwknop
Single Packet Authorization > Port Knocking
 awnumar/memguard
Software sandbox for storage of sensitive information in memory.
 sivaadityacoder/cve-2025-68621
Educational PoC and analysis of CVE-2025-68621, a timing attack on Trilium Notes sync login. Demonstrates HMAC hash recovery via network timing…