
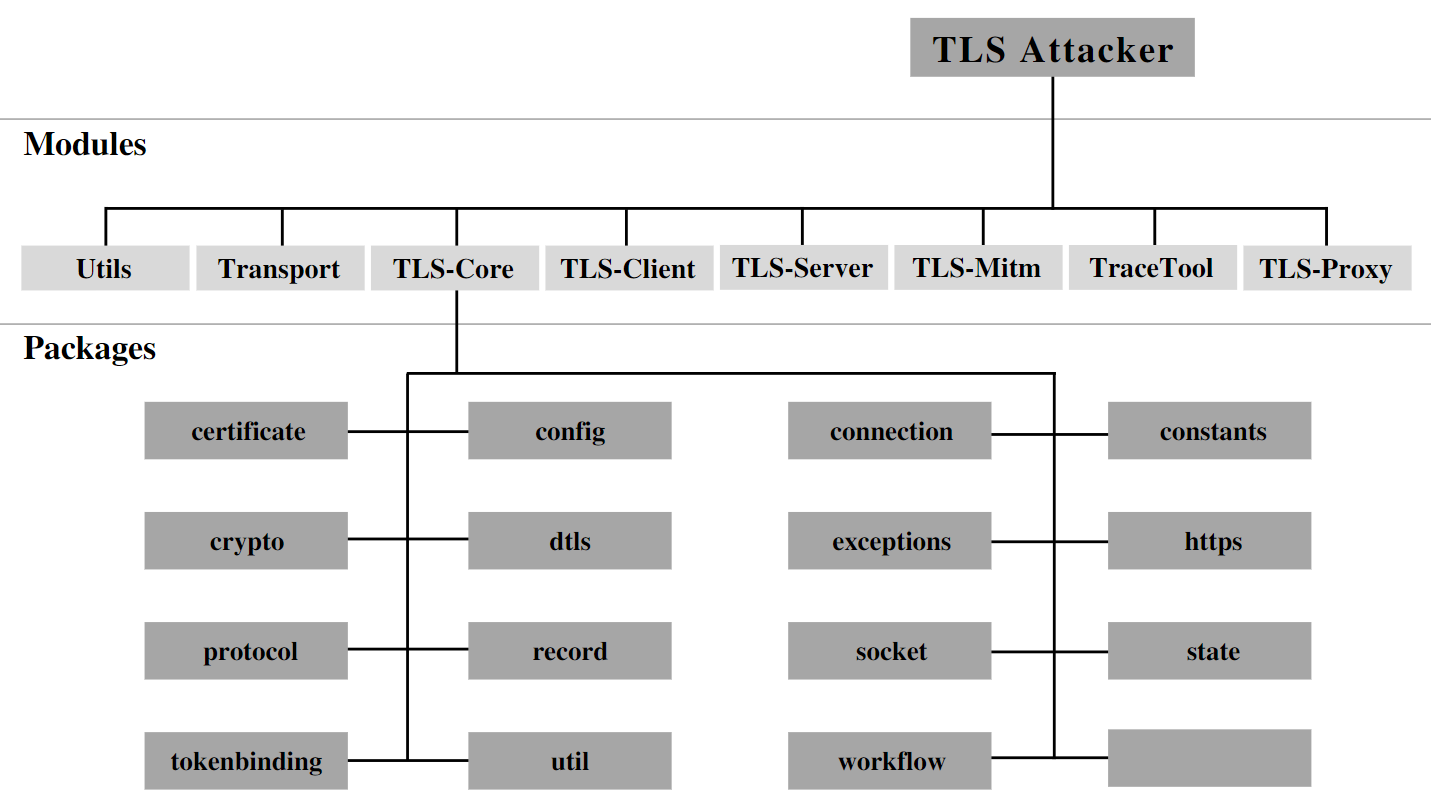
TLS-Attacker
 tls-attacker/tls-attacker
Java-based framework for systematic fuzzing and analysis of TLS libraries. Enables arbitrary protocol message crafting, modification, and testing of…
cryptographyfuzzingnetwork-security+2
880
tls-attacker/tls-attackerJava-based framework for systematic fuzzing and analysis of TLS libraries. Enables arbitrary protocol message crafting, modification, and testing of…
 coroner/cryptolyzer
Multi-protocol cryptographic analyzer auditing TLS, SSL, SSH, IKE, DNSSEC, and HTTP security headers. Detects 400+ cipher suites, generates JA3/HASSH…
 infoslack/awesome-web-hacking
Curated list of web application security resources including books, tools, cheat sheets, labs, and courses for learning penetration testing and…
 shinycolumn/cve-2025-56802
AES-CFB Key Generation and Management Vulnerability in Reolink Desktop Application
 shinycolumn/cve-2025-56801
AES-CFB IV Generation Vulnerability in Reolink Desktop Application
 gogo2464/cve-2024-5124
Exploit for CVE-2024-5124 targeting ChuanhuChatGPT via TLS timing side-channel attack. Uses tlsfuzzer to perform character-by-character credential…
 salgio/ewelink-qr-code
This repo describes a vulnerability affecting the QR code based pairing process of the eWeLink IoT devices (CVE-2020-12702).
 alex-seymour/cve-2020-10560-key-recovery
Proof-of-concept exploit that recovers the site_key for OSSN 5.3 and above, exploiting CVE-2020-10560 arbitrary file read vulnerability.
 jas502n/shiro-721
RememberMe Padding Oracle Vulnerability RCE
 redtimmy/oambuster
Multithreaded Padding Oracle Attack on Oracle OAM (CVE-2018-2879)
 nsacyber/detect-cve-2017-15361-tpm
Detects Windows and Linux systems with enabled Trusted Platform Modules (TPM) vulnerable to CVE-2017-15361. #nsacyber
 smxlabs/lamma-beta
Vulnerability Assessment and Auditing Framework for all the Crypto Implementations.