
CVE-2025-56802
 shinycolumn/cve-2025-56802
AES-CFB Key Generation and Management Vulnerability in Reolink Desktop Application
binary-analysiscryptographyeducation+3
shinycolumn/cve-2025-56802AES-CFB Key Generation and Management Vulnerability in Reolink Desktop Application
 shinycolumn/cve-2025-56801
AES-CFB IV Generation Vulnerability in Reolink Desktop Application
 signalapp/signal-desktop
A private messenger for Windows, macOS, and Linux.
 nccgroup/fips203
Pure Rust implementation of (draft) FIPS 203 Module-Lattice-based Key-Encapsulation Mechanism Standard for server, desktop, browser and embedded…
 owasp/tcasvs
OWASP Thick Client Application Security Verification Standard
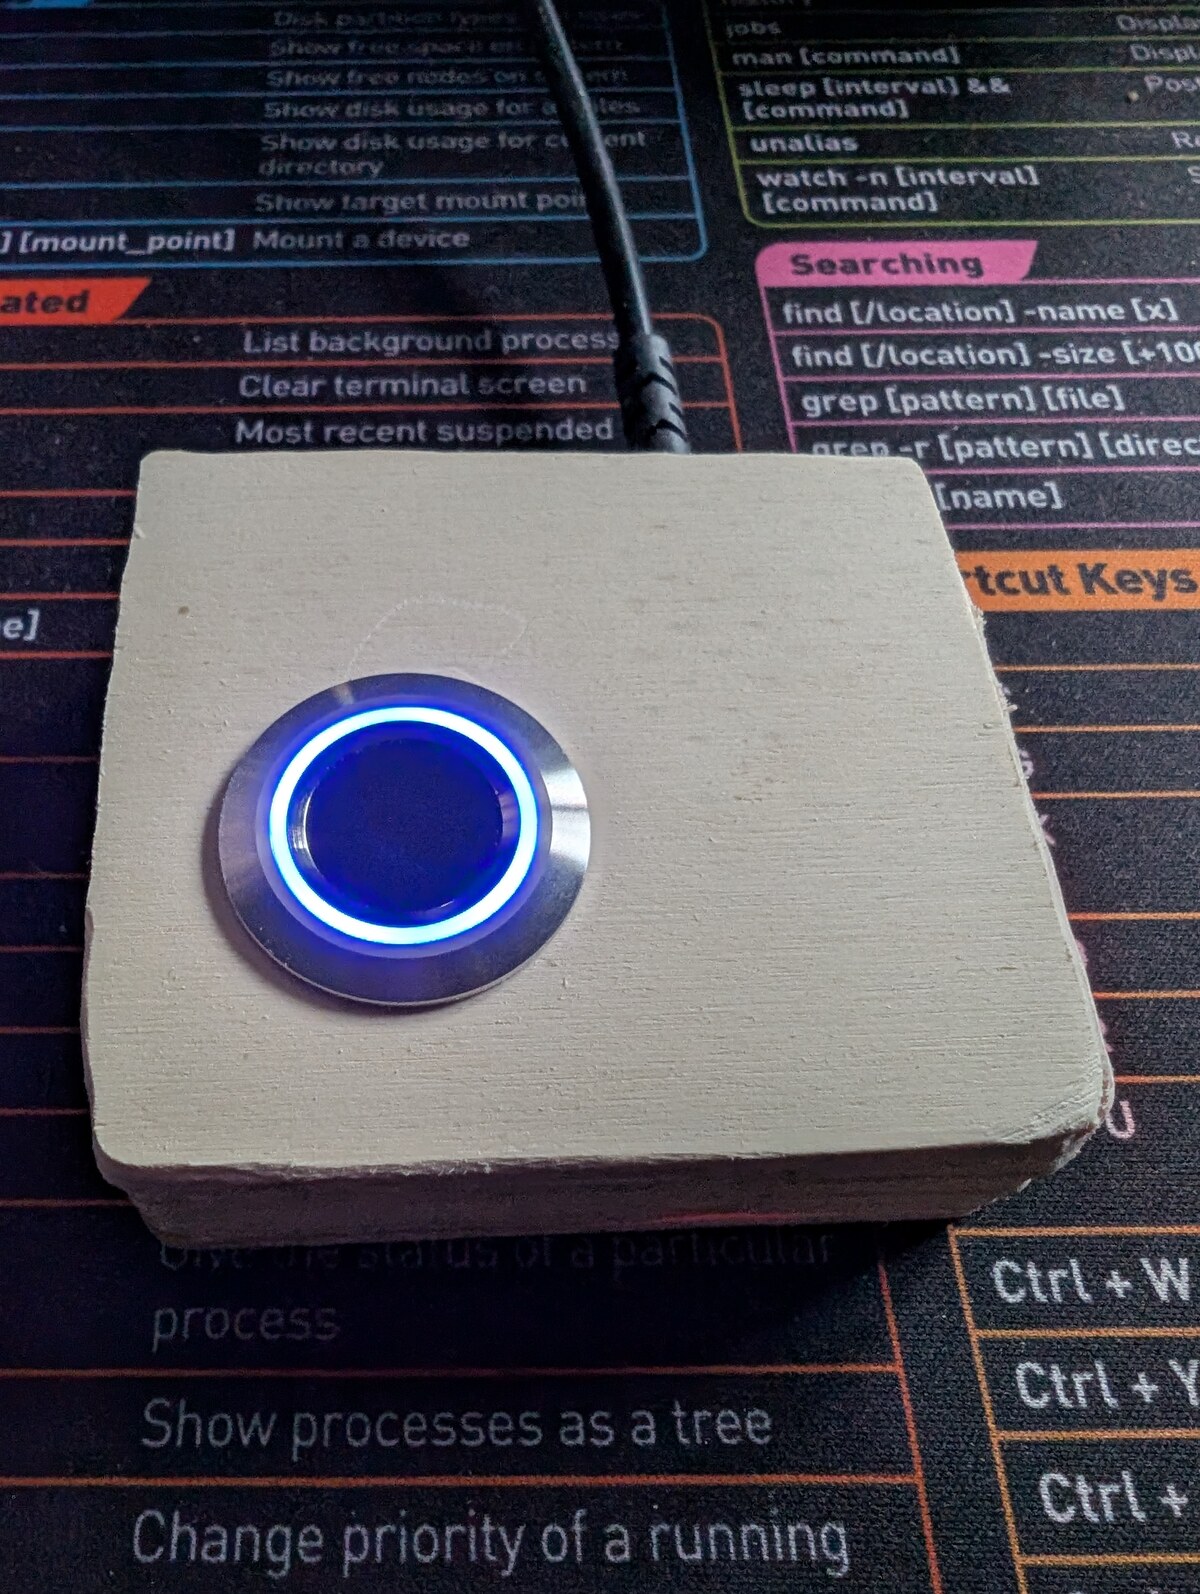 matpb/linux-fingerprint-r503
Linux desktop fingerprint login using a Grow R503 sensor + Arduino + a Rust fprintd-replacement daemon
 wolfssl/wolfssl
The wolfSSL library is a small, fast, portable implementation of TLS/SSL for embedded devices to the cloud. wolfSSL supports up to TLS 1.3 and DTLS…
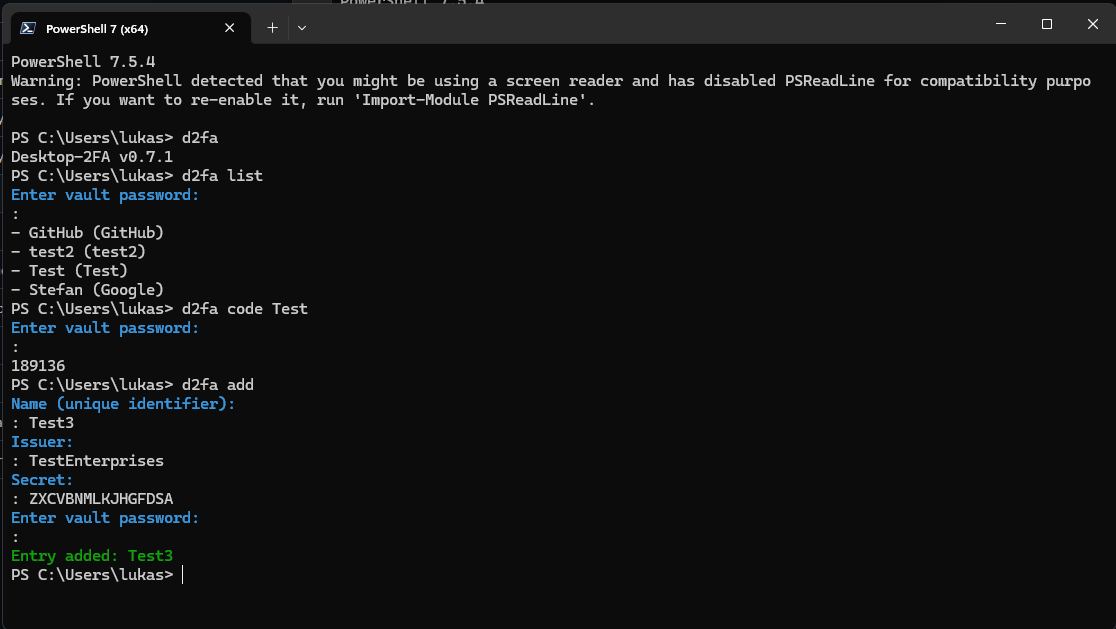 wrogistefan/desktop-2fa
A secure offline desktop application for generating and managing TOTP 2FA codes. Features encrypted vault storage, modern cryptography (Argon2 +…
 rejithregi-group/securityproject
Python Security Project that implements a file encryption and decryption tool