
CVE-2026-19586
 mattgsys/cve-2026-19586
Python PoC exploiting CVE-2026-19586, an unauthenticated command injection in TP-Link Omada SSL VPN that executes arbitrary commands as root via…
command-and-controlcryptographyembedded-systems-security+6
mattgsys/cve-2026-19586Python PoC exploiting CVE-2026-19586, an unauthenticated command injection in TP-Link Omada SSL VPN that executes arbitrary commands as root via…
 l1lf1ng3r/heartbleed-vulnerability-exploitation
hands on investigation of the heartbleed vulnerability (CVE-2014-0160).
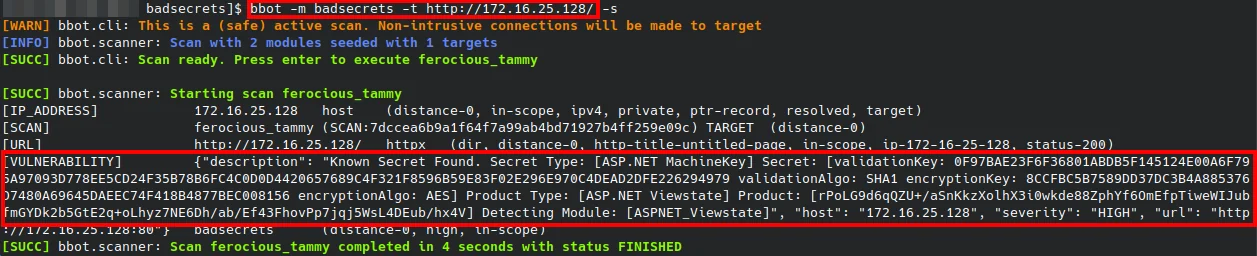 irsdl/crapsecrets
A library for detecting known secrets across many web frameworks
 tony102741/cve-2026-15469
Advisory and technical analysis of CVE-2026-15469, a hard-coded RSA-512 mesh group private key in TP-Link Deco routers, including root cause, impact,…
 hunt-benito/the-same-key-opens-every-box-cve-2026-71960-hard-coded-jwt-secret-in-cudy-wr3000-mesh-mqtt
PoC toolkit that unpacks router firmware, decrypts device secrets, forges JWT tokens, and exploits CVE-2026-71960/71961 to take over Cudy WR3000 mesh…
 google/paranoid_crypto
Paranoid's library contains implementations of checks for well known weaknesses on cryptographic artifacts.
 immune-gmbh/tpm-vuln-checker
Checks for tpm vulnerabilities
 msdmehdipour/meshtastic-cve-2025-52464-poc
Software-only proof of concept for CVE-2025-52464 in Meshtastic Direct Messages
 nccgroup/formal_np1sec
Formalizing np1sec using Tamarin and other FM (see https://github.com/equalitie/np1sec)
 itres-labs/cve-2023-3350
Exploit for cryptographic Issue vulnerability on IBERMATICA RPS [CVE-2023-3350]
 l33tdawg/aether
AI Smart Contract Security Analysis and PoC Generation Framework
 owasp/o-saft
O-Saft - OWASP SSL advanced forensic tool
 cybervinner/tp-link-tl-wr820n-cve-2025-14175
Responsible disclosure write-up for CVE-2025-14175 involving weak cryptographic algorithm support in the SSH server of TP-Link TL-WR820N.
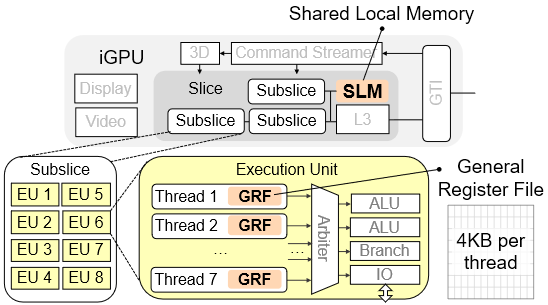 he-wenjian/igpu-leak
[CVE-2019-14615] iGPU Leak: An Information Leakage Vulnerability on Intel Integrated GPU
 lukawynants/onderzoek_cve-2024-31497-poc
Proof-of-concept exploit for CVE-2024-31497, demonstrating a specific vulnerability for security testing and validation purposes.
 filosottile/heartbleed
A checker (site and tool) for CVE-2014-0160
 salgio/ewelink-qr-code
This repo describes a vulnerability affecting the QR code based pairing process of the eWeLink IoT devices (CVE-2020-12702).
 hugobond/cve-2024-31497-poc
Proof Of Concept that exploits PuTTy CVE-2024-31497.