
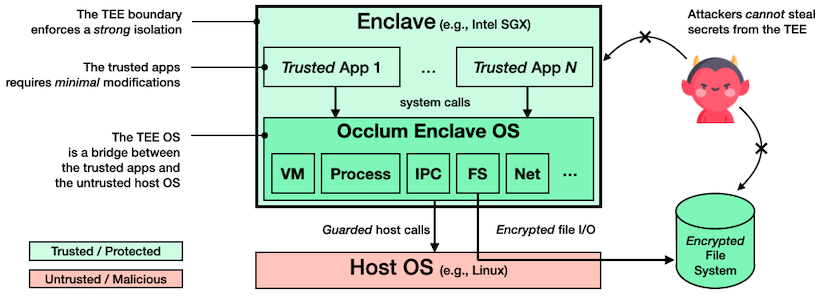
occlum
 occlum/occlum
Memory-safe, multi-process library OS for Intel SGX that runs legacy applications inside enclaves with encrypted filesystems and lightweight…
cloud-infrastructure-securitycloud-securitycryptography+5
1.5k
occlum/occlumMemory-safe, multi-process library OS for Intel SGX that runs legacy applications inside enclaves with encrypted filesystems and lightweight…
 caveeroo/cve-2026-111497-wordpress-poc
CVE-2026-111497 RCE PoC for one pinned Docker Official Image for WordPress
 izcoser/stegpy
Simple steganography program based on the LSB method.
 project-oak/oak
Meaningful control of data in distributed systems.
 tinfoilsh/cvmimage
Builds a hermetic, reproducible confidential VM image for secure inference and custom compute on AMD SEV-SNP and Intel TDX, with auditable…
 0xajstrike/emsign-trust-scan
Offline scanner for the October 2026 eMudhra/emSign CA key compromise, finds affected certificates across OS trust stores, CA bundles, Java cacerts,…
 cdxgen/cdxgen
Creates CycloneDX Bill of Materials (BOM) for your projects from source and container images. Supports many languages and package managers. Integrate…
 reloading01/certstream-server-rust
High-performance Certificate Transparency (CT) monitoring tool written in Rust. Real-time stream of newly issued SSL/TLS certificates from CT logs.…
 c8dhjp4tyv-bit/jbl-wave-buds2-firmware-research
Reverse-engineering notes and Python tooling for JBL Wave Buds 2 (BES1306) firmware: OTA container format, flash layout, BLE/GATT protocol, and…
 abraxas/sqlite-cli-go
SQLite 3.53.4 CLI - High - Local - Command injection - go and slash terminators then dot-command

 rdelasierra-uy/portfolio
Vitrina profesional: writeups de Hack The Box, informes, casos de estudio GRC (ISO 27001/27002/27005/27035, ISO 31000 + MAGERIT), scripts de…
 slowmist/knowledge-base
Curated knowledge base of blockchain security research, audit reports, guides, and translations covering smart contracts, cryptography, and AI…
 abraxas/gatex
FortinetHunter (@YogSoth0) binary cracking application. Part of CTF for FortinetHunter. ELF door: a stripped Nuitka onefile, an XOR-scrambled…
 abraxas/cve-2026-105221-gist-tls
CVE-2026-105221 - gist RubyGem - High - MITM - GitHub OAuth token theft
 rahulreddykarne/cve-2026-15911-confluent_kafka
Disabled TLS Certificate Verification for HashiCorp Vault KMS in confluent-kafka
 murrez/cve-2026-100835
Python PoC for CVE-2026-100835: audits Contrast manifests for AllowedChipIDs/AllowedPIIDs, detects versions, and probes Coordinator endpoints to…
 aramosf/cve-2026-61500
Python PoC and Docker lab for CVE-2026-61500: recovers Rejetto HFS V8 PRNG state to forge an admin session cookie and achieve RCE via server_code.
 abraxas/cve-2026-5430
Disclosure pack and Python PoC for CVE-2026-5430, a JWT algorithm-confusion flaw in WSO2 API Manager 4.5.0 enabling unauthenticated admin account…